
cve-2010-4221-lab
 diegslva/cve-2010-4221-lab
From patch to RCE: hand-built exploit for CVE-2010-4221 (ProFTPD TELNET IAC stack overflow), with the full failure-driven journey documented
binary-exploitationeducationexploitation+5
diegslva/cve-2010-4221-labFrom patch to RCE: hand-built exploit for CVE-2010-4221 (ProFTPD TELNET IAC stack overflow), with the full failure-driven journey documented
 trustedsec/social-engineer-toolkit
The Social-Engineer Toolkit (SET) repository from TrustedSec - All new versions of SET will be deployed here.
 rapid7/metasploitable3
Metasploitable3 is a VM that is built from the ground up with a large amount of security vulnerabilities.
 ambionics/phpggc
PHPGGC is a library of PHP unserialize() payloads along with a tool to generate them, from command line or programmatically.
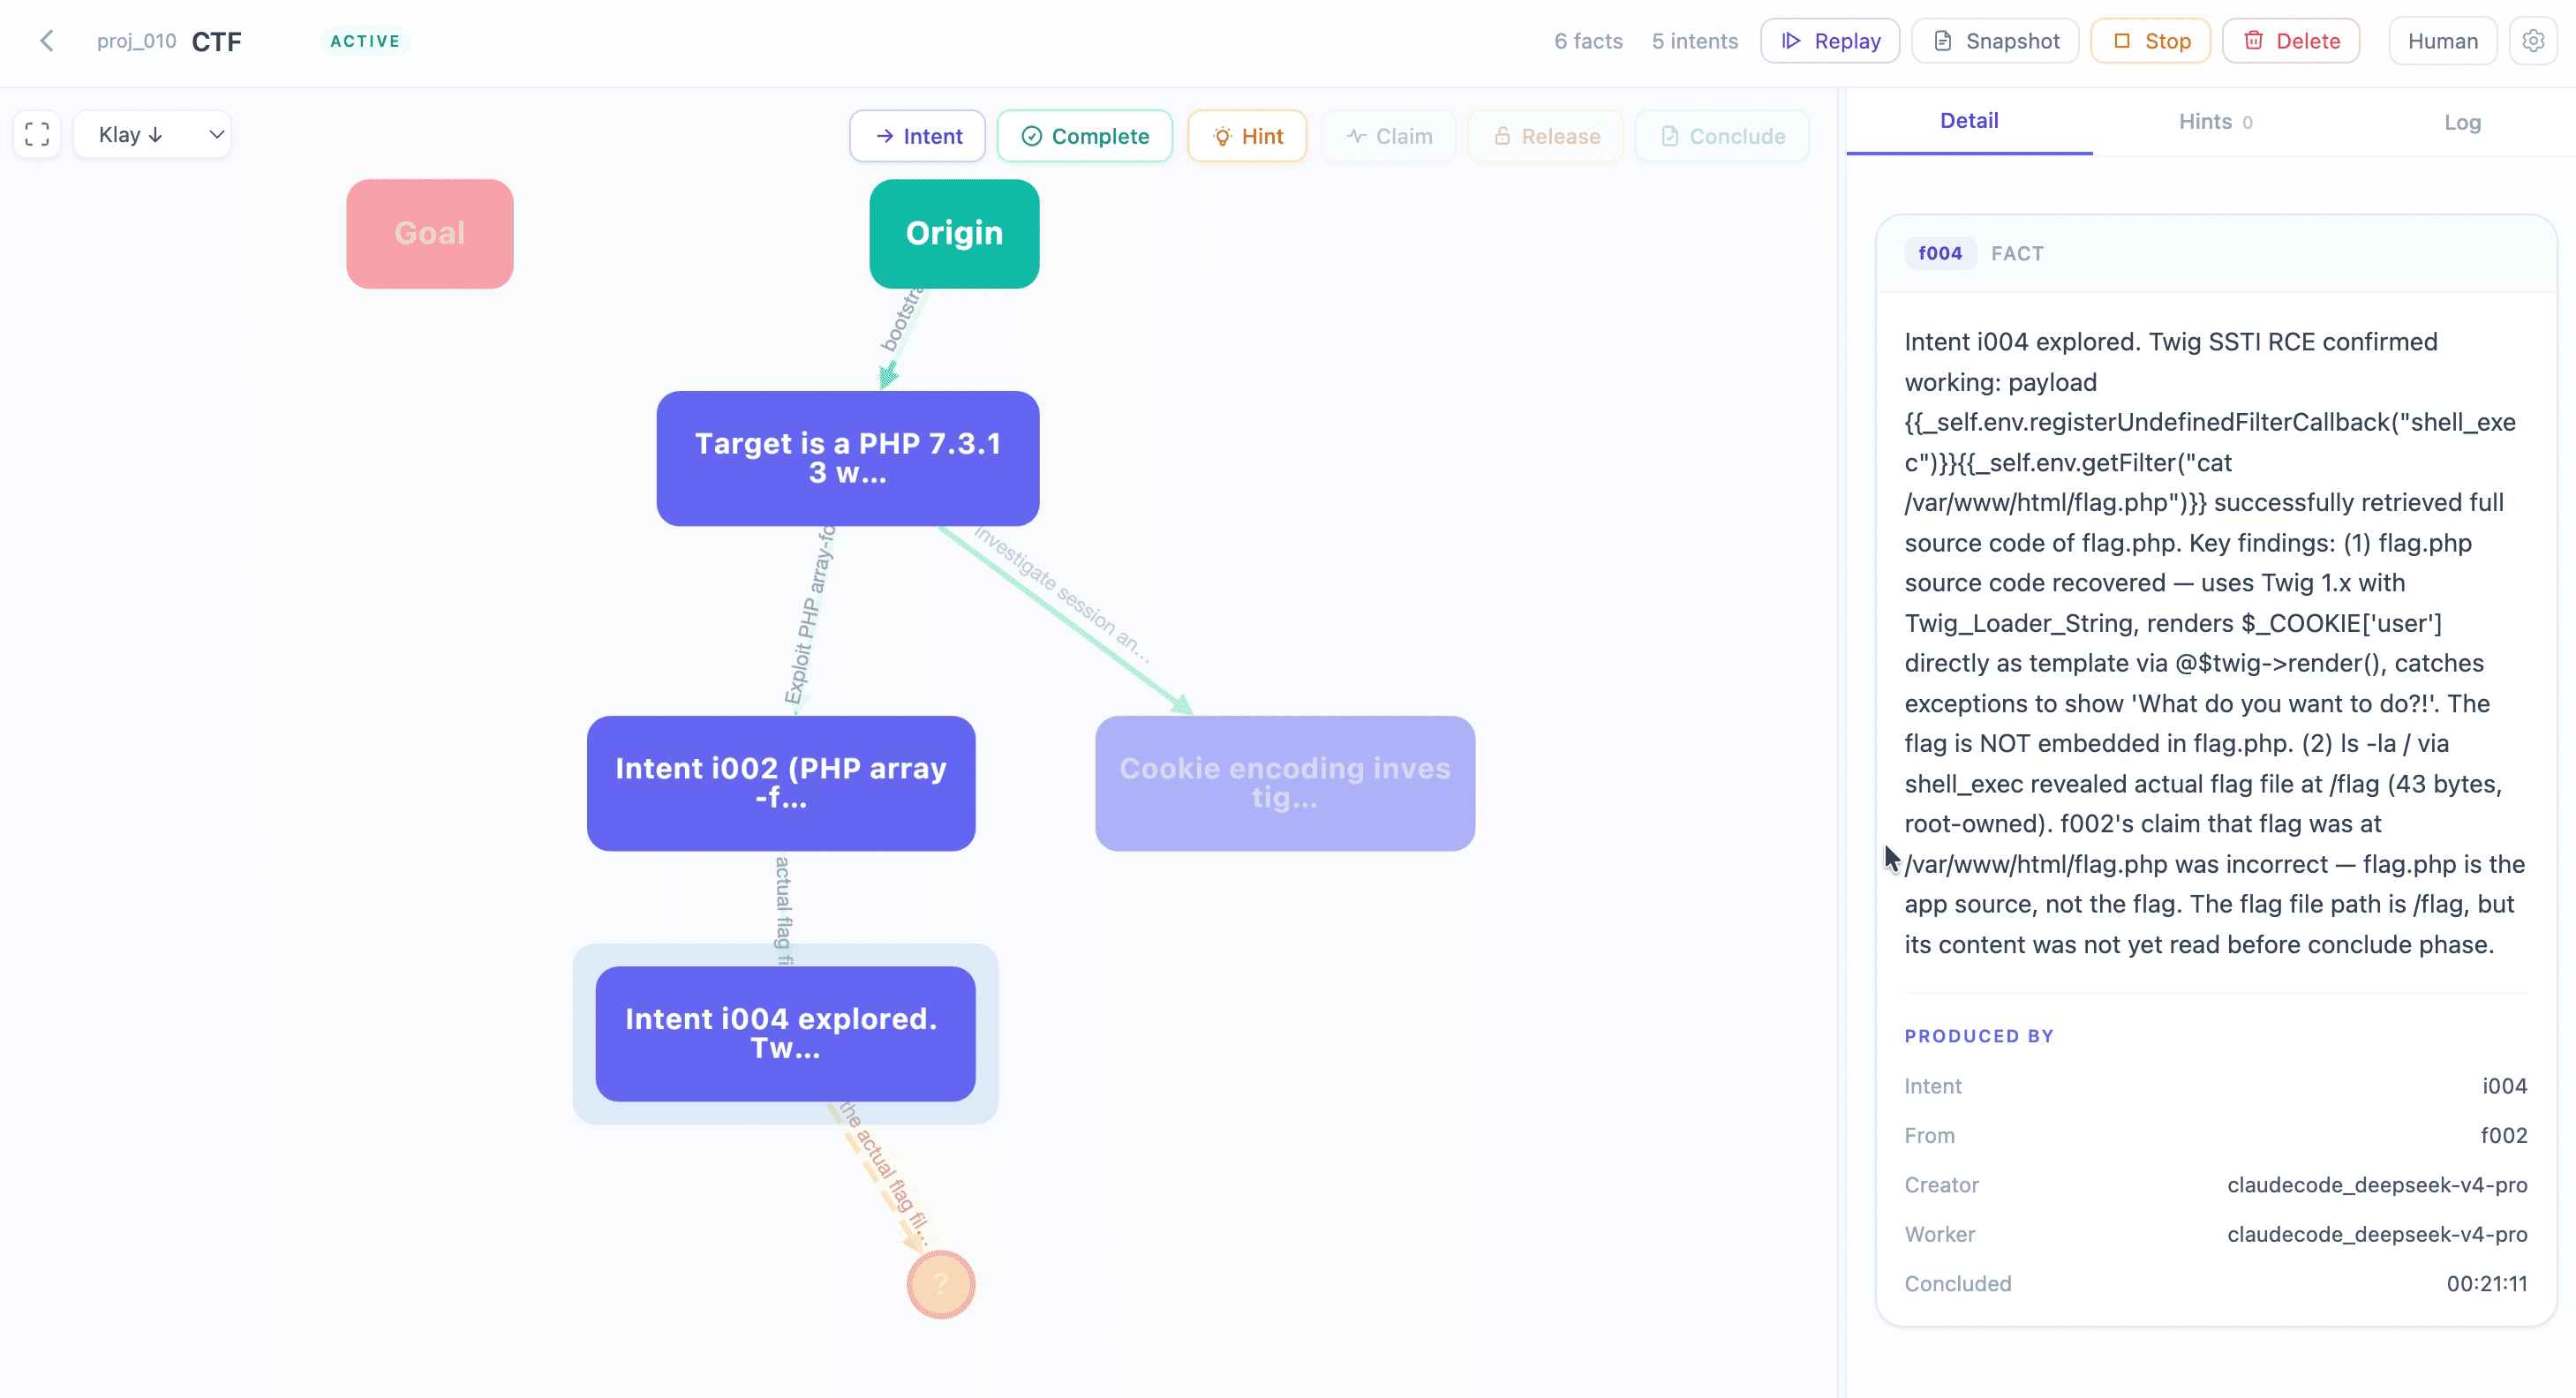 oritera/cairn
LLM-driven state-space search engine for autonomous penetration testing, CTF solving, and vulnerability research. Uses blackboard architecture with…
 0xmarcio/pocindex
Search public CVE proof-of-concept exploits from GitHub, Nuclei, ExploitDB, Metasploit and Vulhub, with CVSS, EPSS and CISA KEV context.
 vulnerscom/getsploit
Search and download public exploits from the Vulners database — online, or fully offline from a local SQLite FTS5 index.
 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.
 lsposed/lspromise
Android complete exploit chain that enables privilege escalation from a local untrusted app to root/kernel, combination of CVE-2026-49881 and…
 mgeeky/threadstackspoofer
Thread Stack Spoofing - PoC for an advanced In-Memory evasion technique allowing to better hide injected shellcode's memory allocation from scanners…
 phoenhex/files
Curated repository of exploits, proof-of-concept code, and vulnerability research presentations from the phoenhex team, focused on binary…
 seanheelan/anamnesis-release
Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…
 pnwcomputers/ultimate-cybersecurity-master-guide
This repository provides a centralized resource for operational cyber defense and offense, compiling Theory, Tools, Operating Procedures, and…
 mgeeky/stracciatella
OpSec-safe Powershell runspace from within C# (aka SharpPick) with AMSI, Constrained Language Mode and Script Block Logging disabled at startup
 naksyn/pythonmemorymodule
pure-python implementation of MemoryModule technique to load dll and unmanaged exe entirely from memory
 msd0pe-1/cve-maker
CLI tool to search CVEs and exploits from NIST, ExploitDB, and GitHub databases. Supports exploit compilation detection and lists latest critical…
 xtr4nge/fruityc2
FruityC2 is a post-exploitation (and open source) framework based on the deployment of agents on compromised machines. Agents are managed from a web…
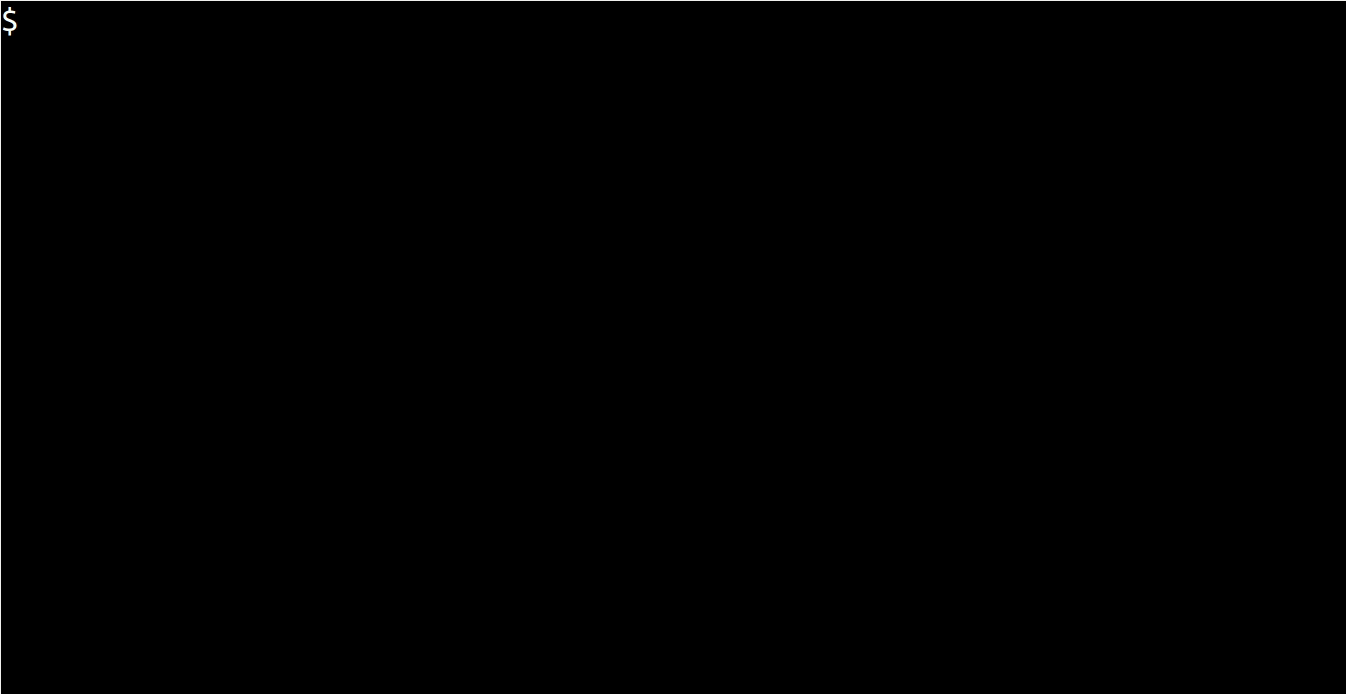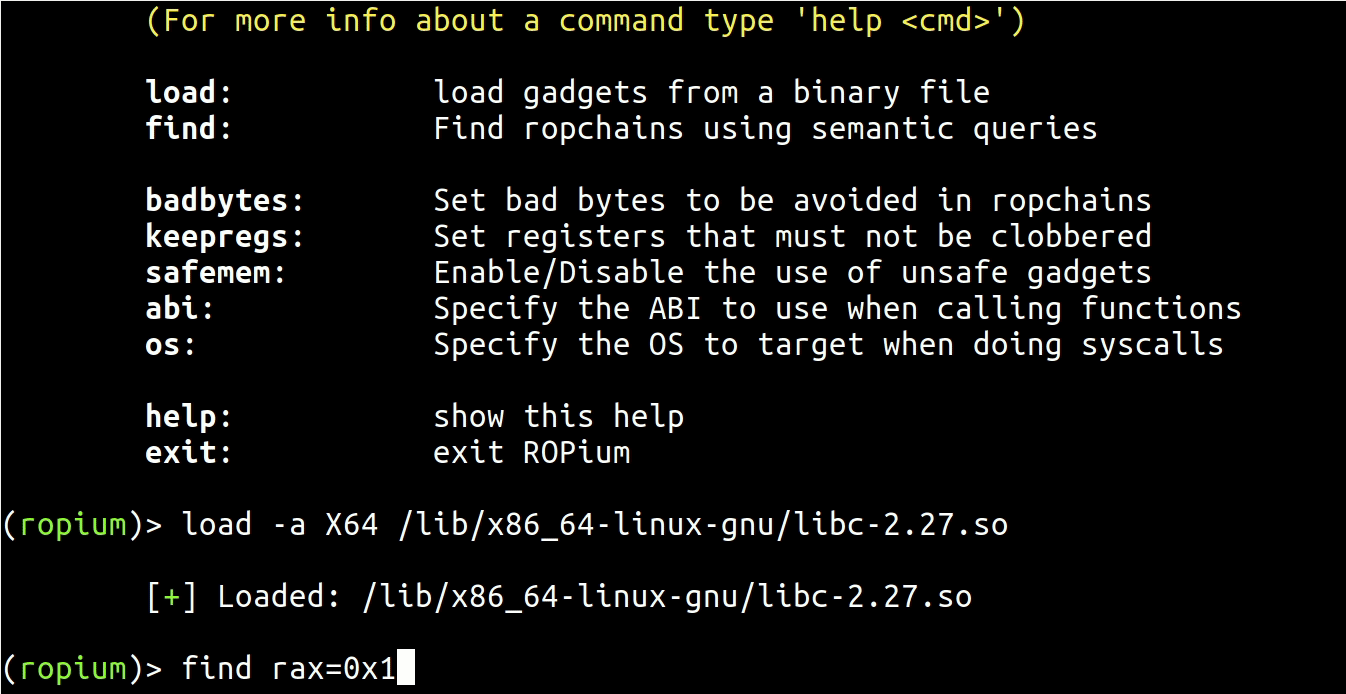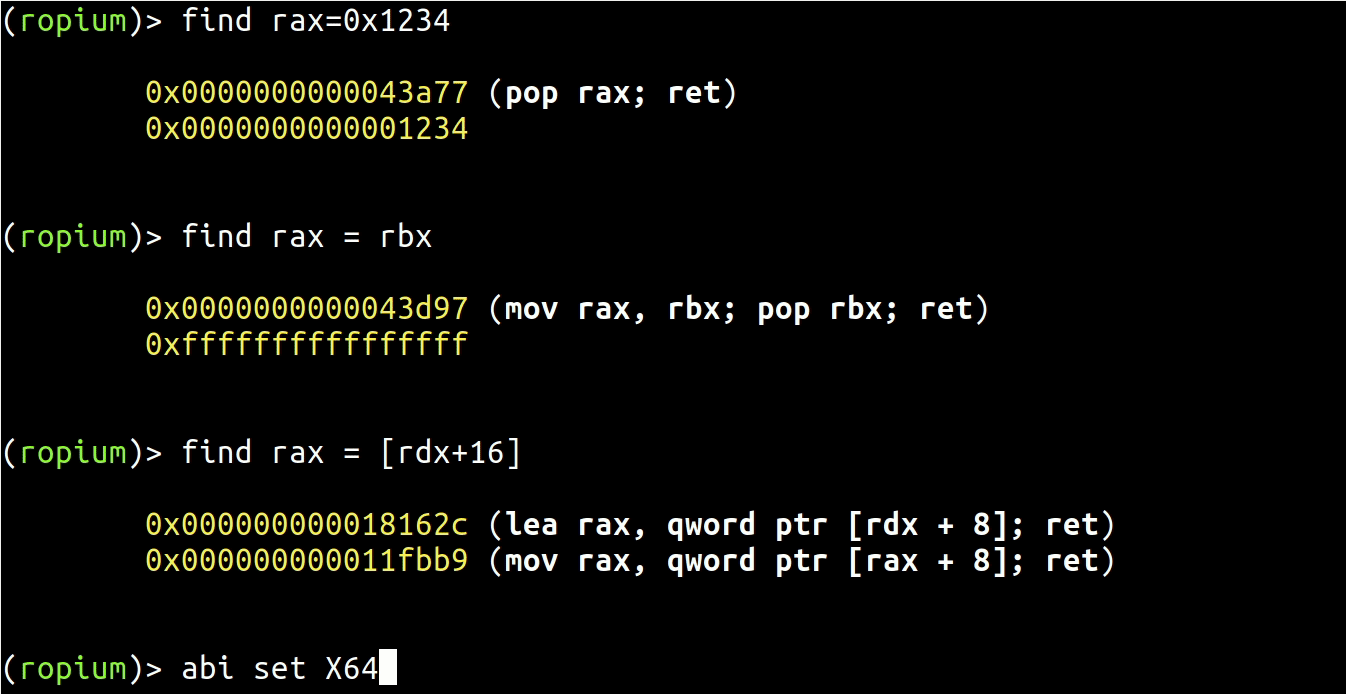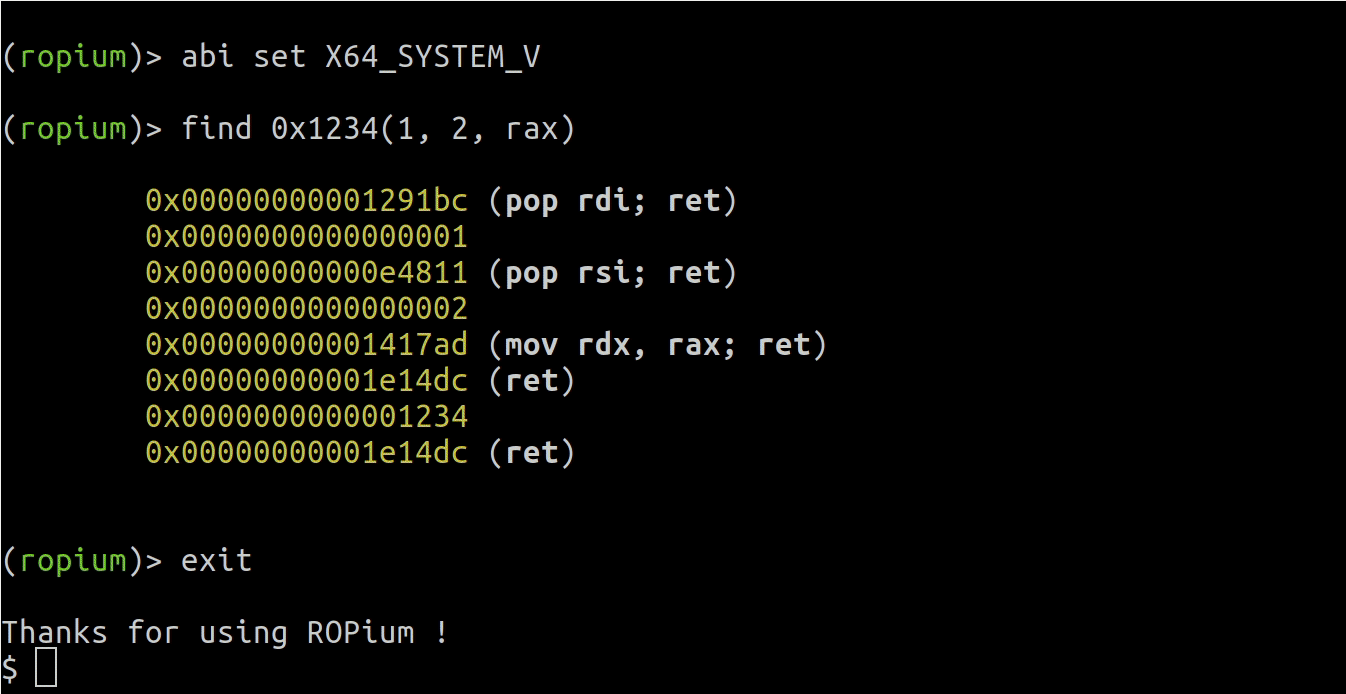 boyan-milanov/ropium
Automated ROP chain builder that extracts and analyzes gadgets from binaries using semantic queries, supporting X86/X64 architectures with a Python…