
offensive-docker
 aaaguirrep/offensive-docker
Offensive Docker is an image with the more used offensive tools to create an environment easily and quickly to launch assessment to the targets.
container-securityexploit-frameworkspassword-cracking+5
771
aaaguirrep/offensive-dockerOffensive Docker is an image with the more used offensive tools to create an environment easily and quickly to launch assessment to the targets.
 eddinos2/cve-2026-64705
Root-cause analysis and proof-of-concept for CVE-2026-64705, a macOS HFS xattr kernel heap overflow. Includes weaponized HFS+ image, patcher, parser,…
 nu11secur1ty/kali-linux-docker
kali-linux-docker
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 charmve/pystegosploit
PoC - Exploit Delivery via Steganography and Polyglots, CVE-2014-0282
 metarget/metarget
Metarget is a framework providing automatic constructions of vulnerable infrastructures.
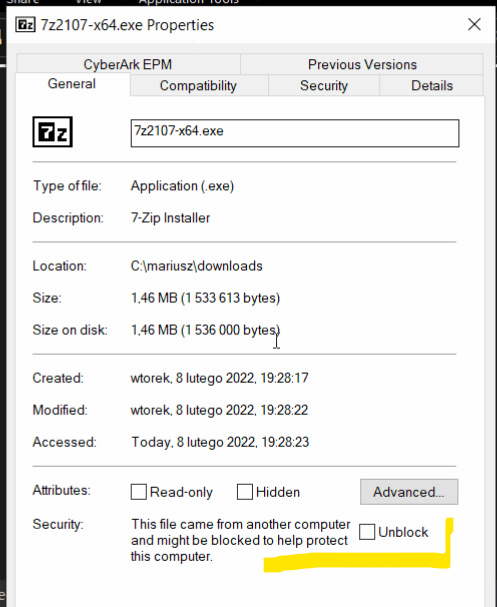 mgeeky/packmypayload
A PoC that packages payloads into output containers to evade Mark-of-the-Web flag & demonstrate risks associated with container file formats.…
 khast3x/redcloud
Automated Red Team Infrastructure deployement using Docker
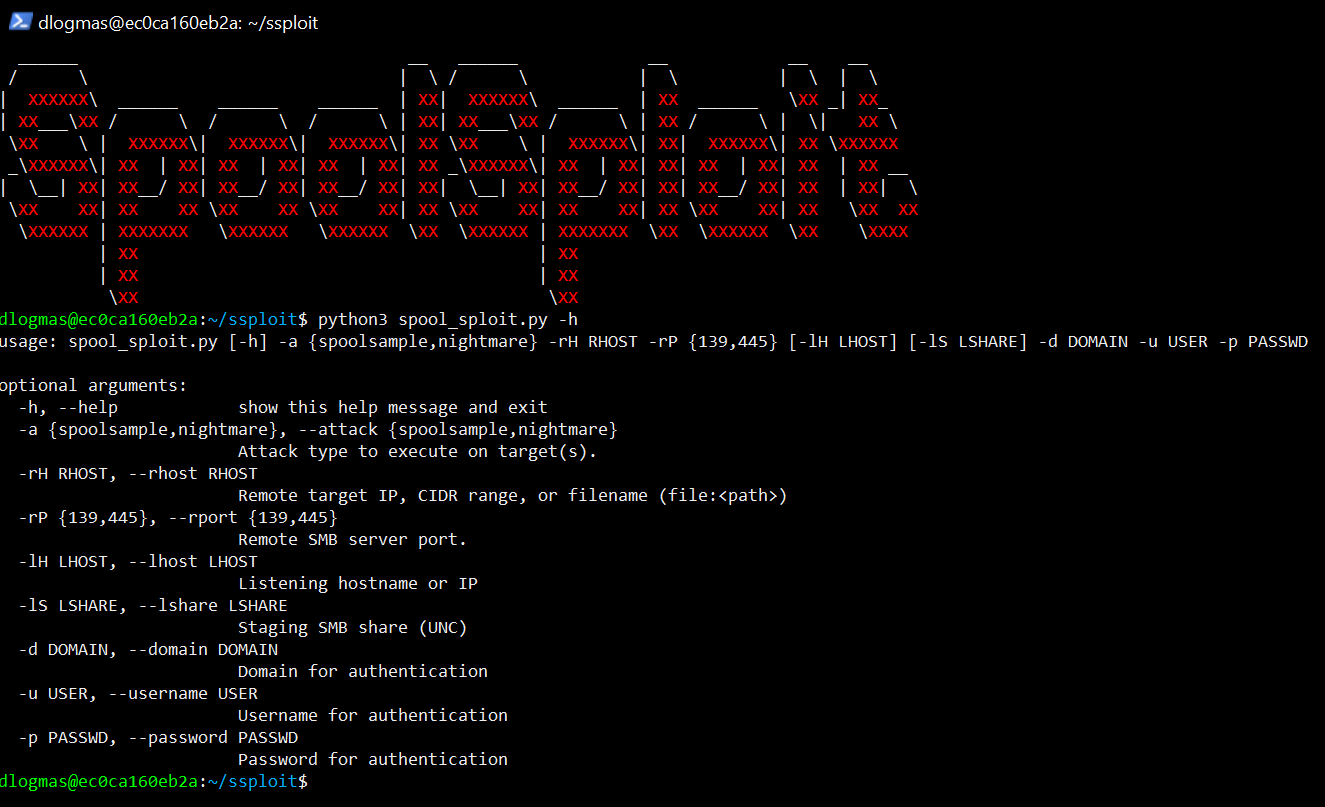 beetlechunks/spoolsploit
A collection of Windows print spooler exploits containerized with other utilities for practical exploitation.
 shadowabi/cve-2026-31431-copyfail-universal-lpe
CVE-2026-31431 Copy Fail — Universal LPE exploit. Dynamic ELF offset + full-binary overwrite, Python 2/3 compatible with ctypes splice fallback
 mauroeldritch/gevaudan
Exploit for Red Hat / GlusterFS CVE-2018-1088 & CVE-2018-1112, featured @ DEFCON 26, Las Vegas!
 m4xsec/my-exploits
Metasploit modules, Python PoCs and throwaway Docker labs for four platform CVEs: Keycloak (CVE-2026-18963), Apache NiFi (CVE-2026-39816), HashiCorp…
 lglznl/klaios
KLAIOS is a hybrid security environment that merges Kali Linux’s offensive toolkit with hardened, VPN-bunker-style isolation—enhanced by modern AI…
 jlk/exploit-cve-2017-6090
Containerized exploitable PhpCollab
 cgv-dev/metasploit-module-tfm
Module written in Ruby with the objective of exploiting vulnerabilities CVE-2023-2728 and CVE-2024-3177, both related to the secret mount policy in a…