
android_autorooter
 scs-labrat/android_autorooter
Exfiltrate sensitive user data from apps on Android 12 and 13 using CVE-2024-0044 vulnerability remotely
android-securitydata-exfiltrationexploitation+5
76
scs-labrat/android_autorooterExfiltrate sensitive user data from apps on Android 12 and 13 using CVE-2024-0044 vulnerability remotely
 lsposed/lspromise
Android complete exploit chain that enables privilege escalation from a local untrusted app to root/kernel, combination of CVE-2026-49881 and…
 gushmazuko/metasploit_in_termux
Install and run Metasploit Framework 6 on Android via Termux with automated setup, payload generation (msfvenom), and full msfconsole access for…
 perongh/badepoll-selinux-disabler
Use CVE-2026-43074 to disable SELinux on Android (Linux 6.6/6.12)
 hegaz0y/-bul
EDSEC_BKIF is a keystroke injection tool for Android, Linux, and iOS. With the help of CVE-2023-45866, it grants users unprecedented control over…
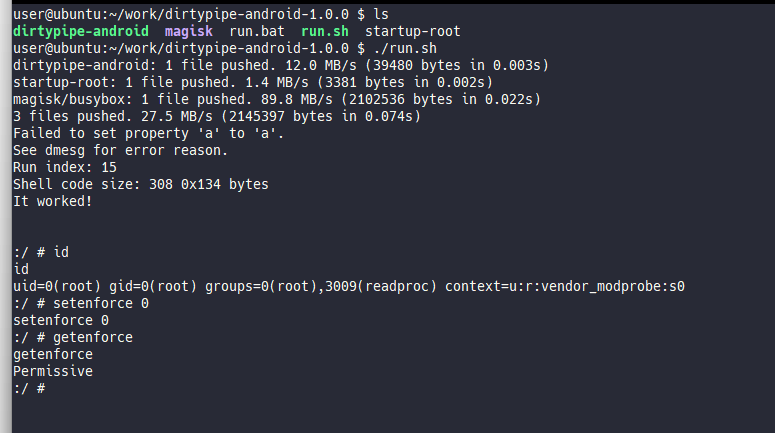 polygraphene/dirtypipe-android
Dirty Pipe root exploit for Android (Pixel 6)
 timwr/cve-2019-2215
Android kernel privilege escalation exploit for CVE-2019-2215, providing a proof-of-concept to achieve root access via a use-after-free vulnerability…
 josephshenton/triple_fetch-kernel-creds
Attempt to steal kernelcredentials from launchd + task_t pointer (Based on: CVE-2017-7047)
 nettitude/scrounger
Mobile application testing toolkit
 jingmatrix/pixel-ksu-root
CVE research and exploits to help gaining roots for Pixel devices
 r0rt1z2/ghostlock
Kernel root exploit (CVE-2026-43499) for some Amazon devices
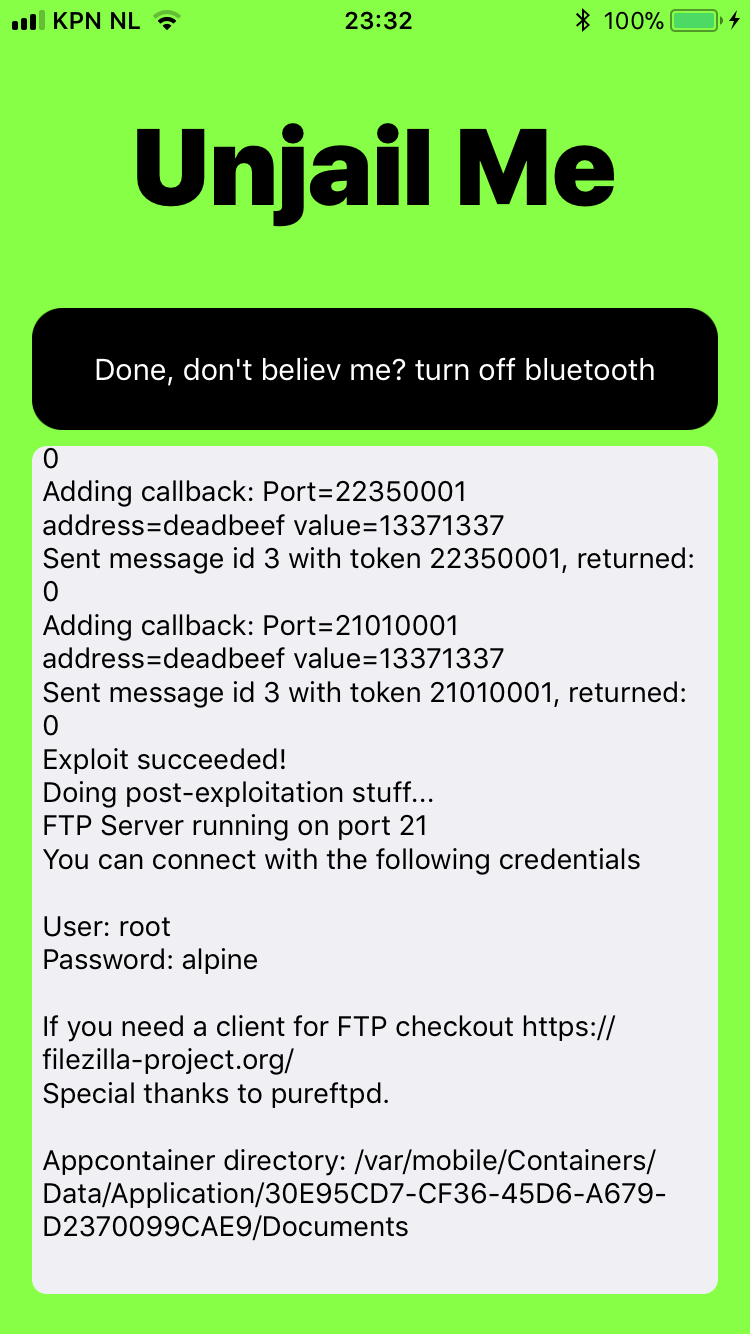 mtjailed/unjailme
A sandbox escape based on the proof-of-concept (CVE-2018-4087) by Rani Idan (Zimperium)
 diabl0w/cve-2022-22057_sm-f926u
Qualcomm kgsl driver exploit (CVE-2022-22057) for Samsung Galaxy devices achieving arbitrary kernel memory read/write, SELinux bypass, and temporary…
 llccd/temproot-huawei
CVE-2019-2215 poc for Huawei hardened kernel
 dorlow/hazel-cve-2026-43499
Firmware-specific temporary root exploit for Toshiba/Amazon Fire TV (hazel) using CVE-2026-43499. Implements ARM32 futex-PI UAF, kernel address leak,…