
Offensive-lab-2
 mafiosohack/offensive-lab-2
Penetration test walkthrough on a vulnerable Ubuntu VM. Exploited the ProFTPD 1.3.3c backdoor (CVE-2010-4221) to gain root access and capture the…
ctfeducationexploitation+8
mafiosohack/offensive-lab-2Penetration test walkthrough on a vulnerable Ubuntu VM. Exploited the ProFTPD 1.3.3c backdoor (CVE-2010-4221) to gain root access and capture the…
 tgies/copy-fail-c
Cross-platform C port of the Copy Fail Linux LPE (CVE-2026-31431). Disclosed 2026-04-29 by Theori / Xint.
 aramosf/cve-2026-64468
Unprivileged proof-of-concept and x86_64 local privilege escalation for a Linux kernel Binder use-after-free (CVE-2026-64468), with KASAN lab and…
 franklinf25/cve-2026-31431
Analyzes CVE-2026-31431, a Linux kernel AF_ALG AEAD vulnerability, providing a safe detector, in-lab LPE exploit, and QEMU-based A/B kernel lab for…
 erdemozgen/copy-fail-cve-2026-31431
Go port of the Copy Fail PoC for CVE-2026-31431, a Linux kernel authencesn flaw enabling a 4-byte write into page cache via AF_ALG and splice.…
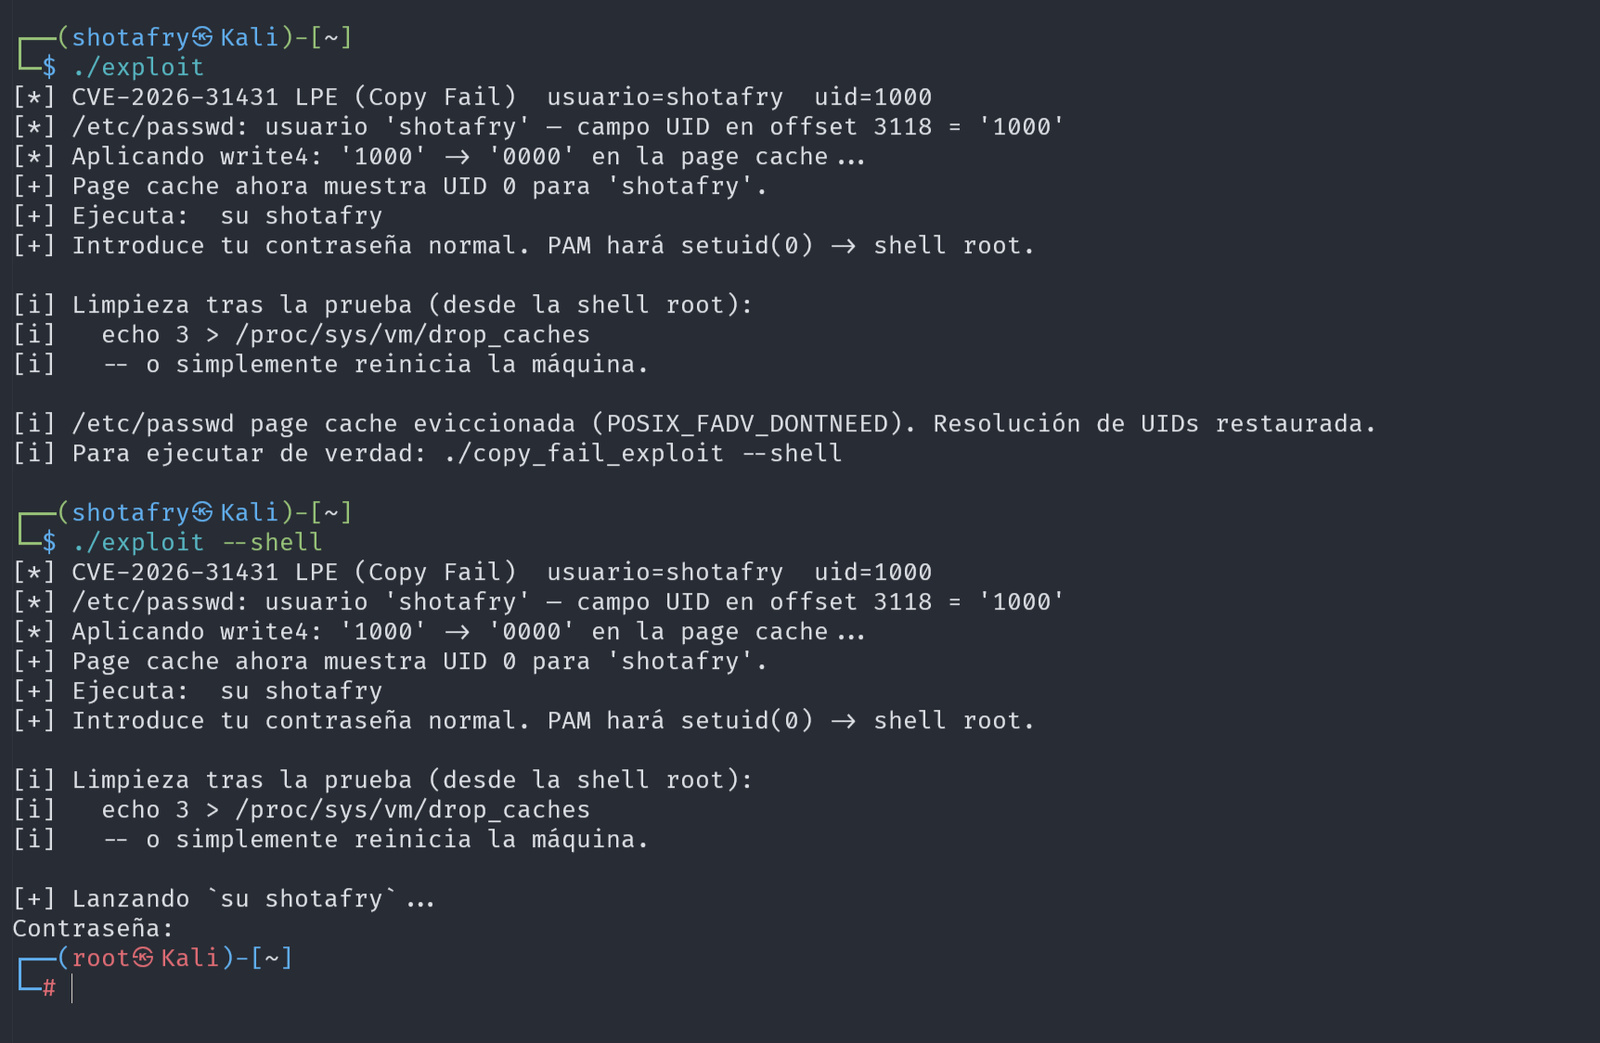 shotafry/copyfail-exploits-cve-2026-31431
Multi-language educational exploit implementations for CVE-2026-31431, a Linux kernel local privilege escalation via the algif_aead module, with a…
 rvzsec/cve-2026-31431
PoC exploits for CVE-2026-31431, a Linux kernel LPE via authencesn page cache write, providing unprivileged user to root escalation on most distros…
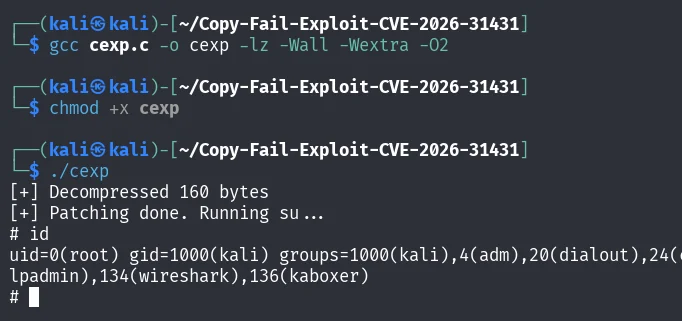 beatbeast007/linux-copyfail-c-version-cve-2026-31431
Clean C implementation of the Copy Fail Linux local privilege escalation exploit (CVE-2026-31431). Uses AF_ALG and splice to overwrite page cache of…
 luotian2/cve-2026-31431
Exploit for CVE-2026-31431, a Linux kernel authencesn bug enabling local privilege escalation and container escape via a 4-byte page cache write.
 kongqbin/cve-2016-5195
Educational implementation of the Dirty COW (CVE-2016-5195) privilege escalation exploit, including race condition payload and SUID-based root shell…
 ak777177/dirty-frag-analysis
Dirty Frag (CVE-2026-43284/43500) - Linux Kernel LPE Deep Technical Analysis by Bomb
 boos4721/copyfail-rs
Rust exploit for CVE-2026-31431, a Linux kernel page-cache write primitive via AF_ALG splice, enabling privilege escalation to root through…
 xn0kkx/cve-2026-31431_copyfail_linuxkernel_lpe
Educational rewrite of the Copy Fail PoC (CVE-2026-31431) — Linux kernel LPE via algif_aead in-place crypto + splice() page-cache write
 3jee/copy-fail-go
Go port of the CVE-2026-31431 (copy-fail) Linux kernel privilege escalation PoC, with automatic SUID binary enumeration and interactive target…
 adityasingh108/cve-2026-31431-metasploit-exploit
Automated Metasploit post-exploitation module for CVE-2026-31431 ("Copy Fail"). Weaponizes a deterministic logic flaw in the Linux kernel AF_ALG…
 rayferrufino/make-and-break
Built a custom Virtual Machine, running Ubuntu 18.04.1 and Webmin 1.810. Using CVE-2019-15107 to exploit a backdoor in the Linux machine
 armircetaj/tetragon-dirtyfrag
Blocking the DirtyFrag Linux LPE chain (CVE-2026-43284 / CVE-2026-43500) at runtime with a Cilium Tetragon TracingPolicy
 themursalin/cve-2026-31431
Python exploit for CVE-2026-31431, a Linux kernel LPE via AF_ALG null pointer dereference leading to heap OOB write and credential overwrite.…