
copy_fail
 spensercai/copy_fail
Rust exploit PoC for Linux kernel LPE CVE-2026-31431 (AF_ALG page-cache write) plus eBPF runtime defense blocking AF_ALG socket creation via LSM or…
binary-exploitationdefensive-toolsexploitation+4
3
spensercai/copy_failRust exploit PoC for Linux kernel LPE CVE-2026-31431 (AF_ALG page-cache write) plus eBPF runtime defense blocking AF_ALG socket creation via LSM or…
 v4bel/januscape
KVM/x86 guest-to-host escape exploit (CVE-2026-53359) leveraging a use-after-free in shadow MMU emulation. Includes PoC for triggering host kernel…
 bin4ry/unipwn
BLE exploit framework for Unitree robots: command injection via hardcoded AES keys enables remote takeover, payload injection, and wormable…
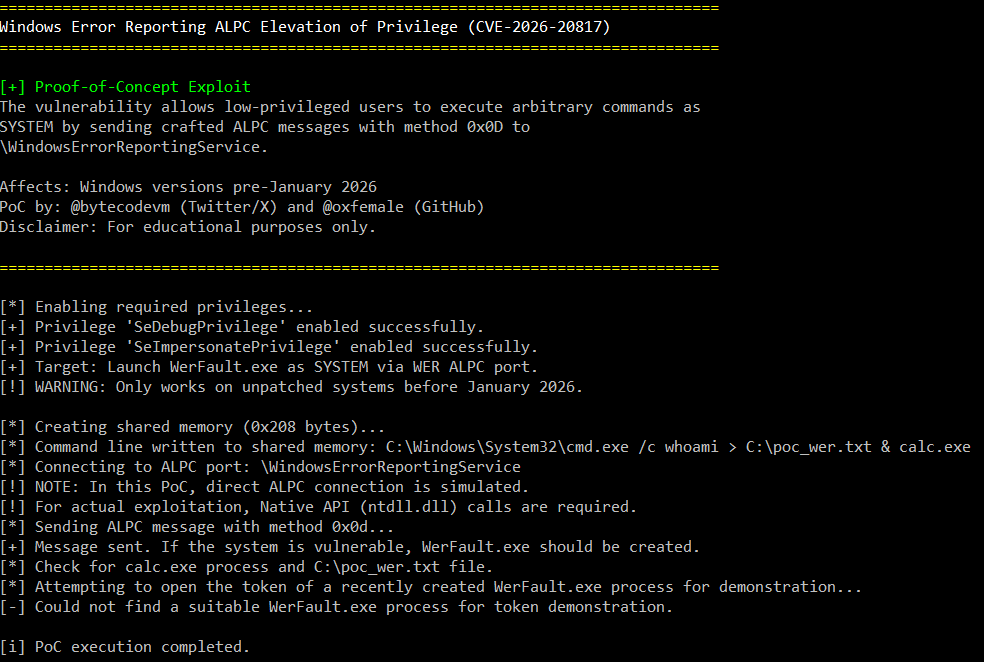 oxfemale/cve-2026-20817
Proof-of-concept exploit for CVE-2026-20817, a local privilege escalation in Windows Error Reporting (WER) via ALPC, allowing low-privileged users to…
 mebeim/cve-2021-4034
Proof-of-concept exploit for CVE-2021-4034, a local privilege escalation in polkit's pkexec, demonstrating exploitation with simple C helpers and a…
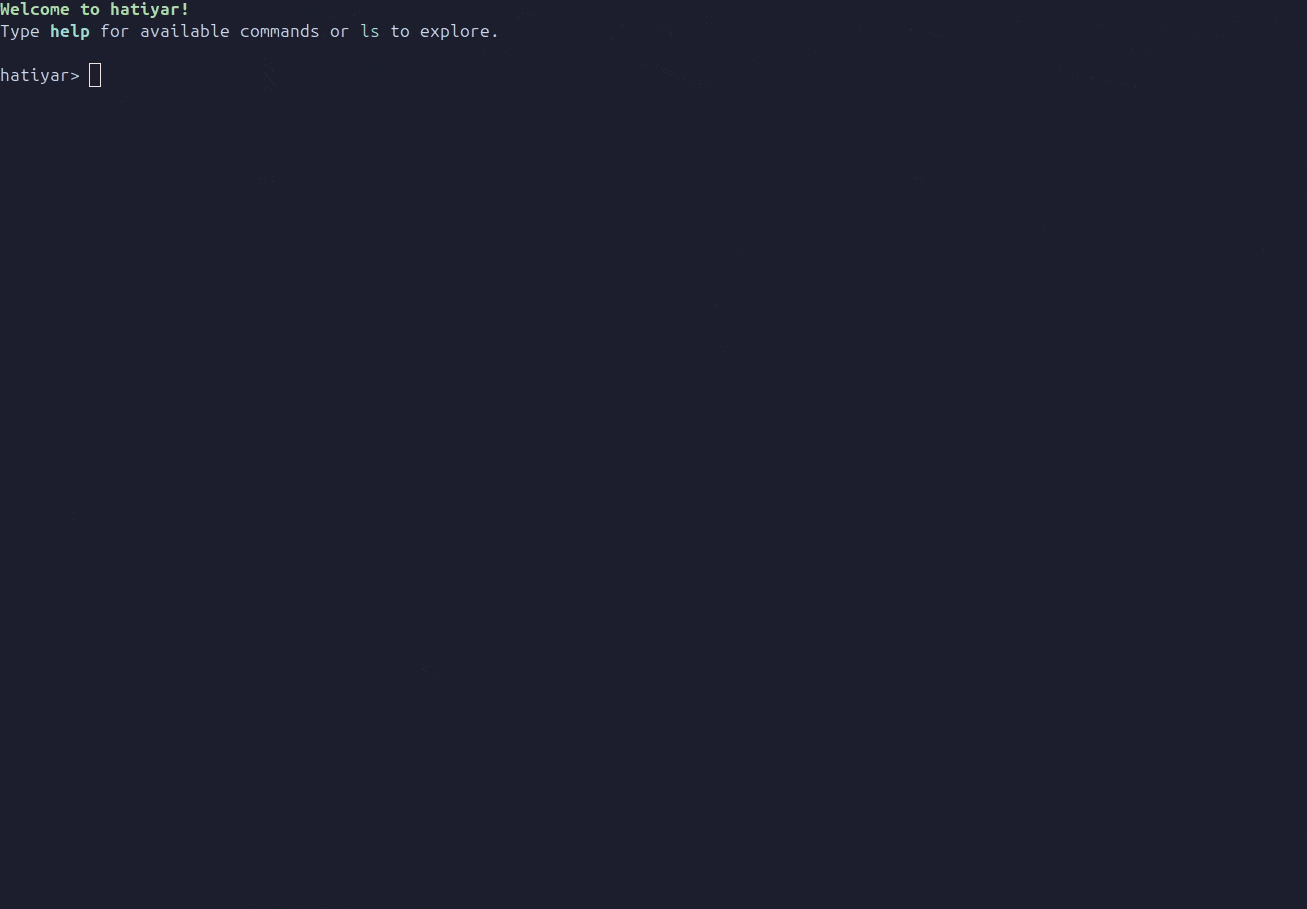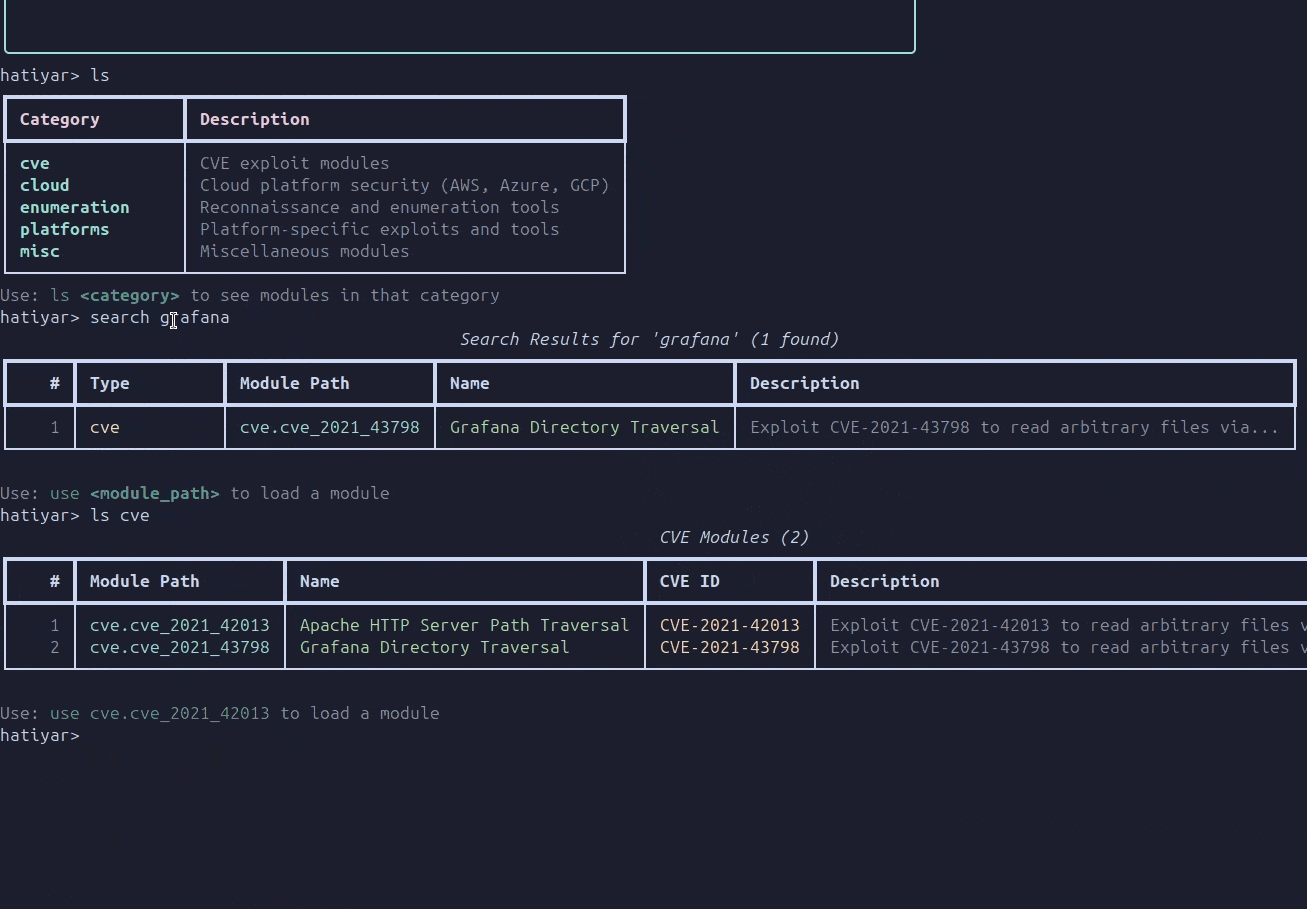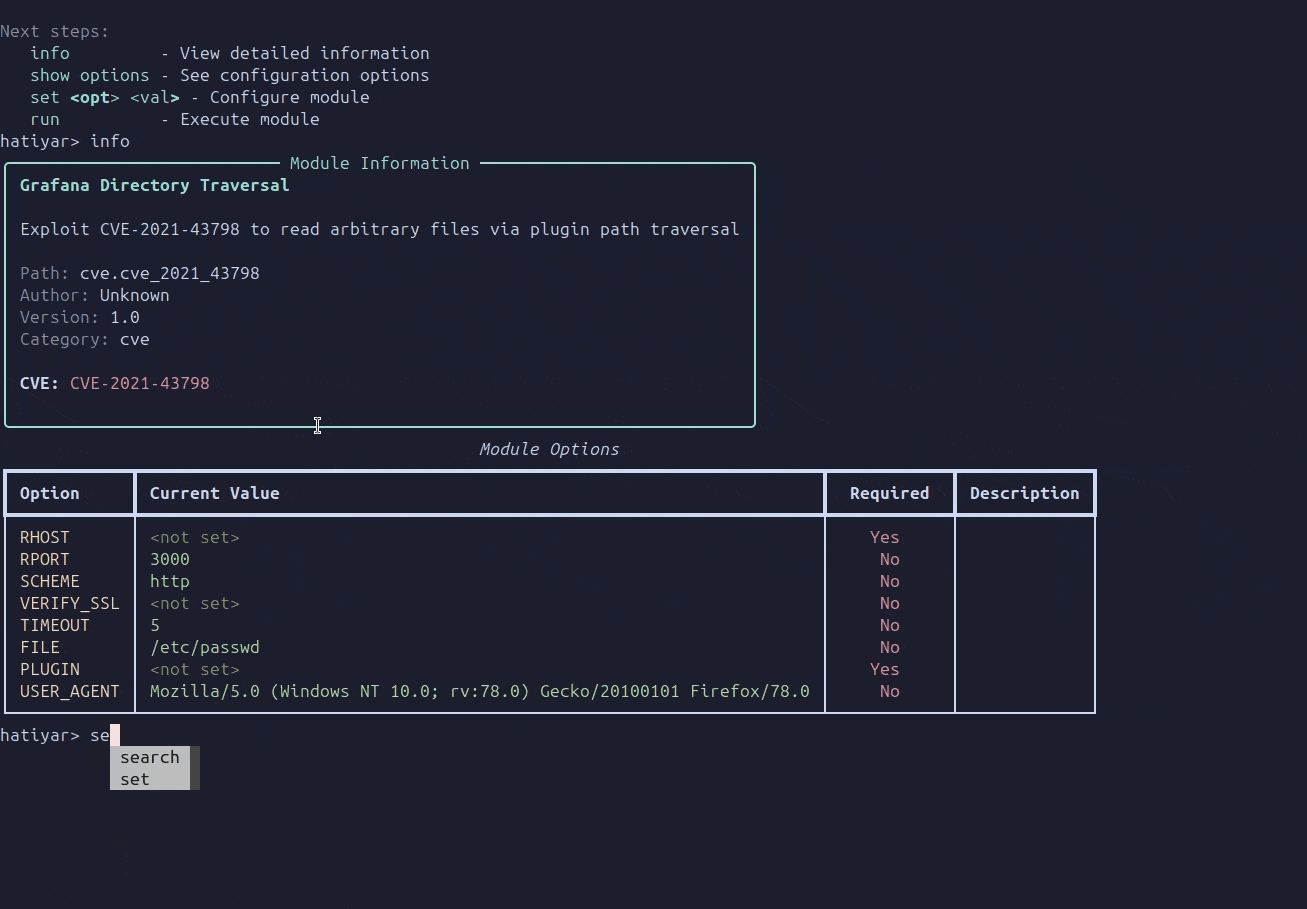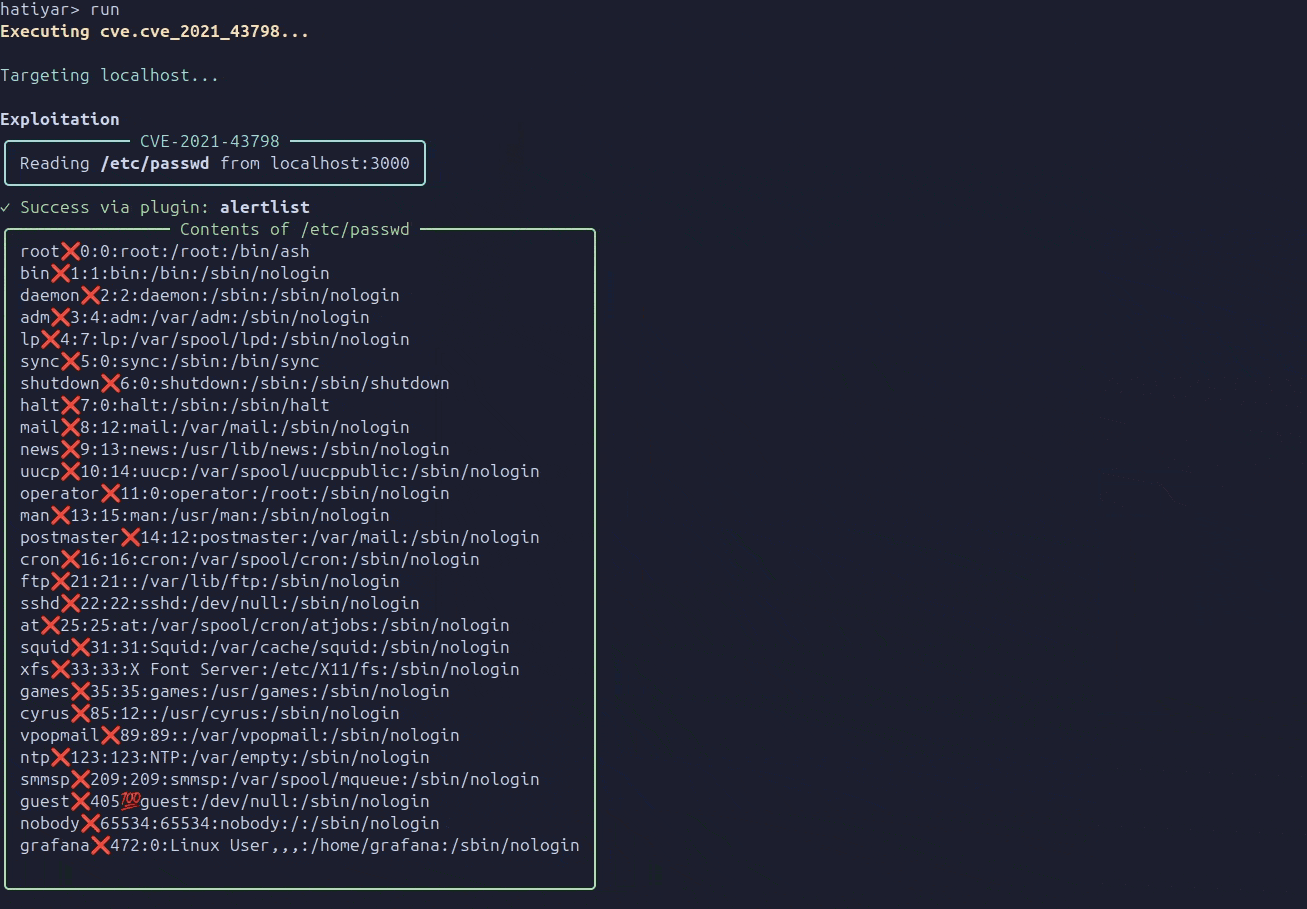 ajutamangdev/hatiyar
Modular penetration testing framework with a Metasploit-like interactive shell, pre-built CVE exploit modules, and cloud/network reconnaissance…
 rbowes-r7/unrar-cve-2022-30333-poc
Proof-of-concept exploit for CVE-2022-30333 path traversal in unRAR, generating malicious .rar files to plant payloads at arbitrary locations.…
 zeop-cybersec/apache_normalize_path
Metasploit-Framework modules (scanner and exploit) for the CVE-2021-41773 and CVE-2021-42013 (Path Traversal in Apache 2.4.49/2.4.50)
 0dayninja/cve-2021-24155.rb
WordPress Backup Guard Authenticated Remote Code Execution Exploit
 hackspeak/cve-2026-62735
Local privilege escalation exploit for Windows HTTP.sys integer overflow (CVE-2026-62735), demonstrating crash and full SYSTEM shell via nonpaged…
 yakumwamba/poc-cve-2021-4034
Proof-of-concept exploit for CVE-2021-4034 (PwnKit), a local privilege escalation in polkit's pkexec, verified on Debian 10 and CentOS 7.
 adityabhatt3010/cve-2026-31431
Local privilege escalation exploit for CVE-2026-31431, abusing AF_ALG AEAD socket handling to achieve root shell access on vulnerable Linux kernels.
 diegslva/cve-2015-3306-lab
Reproducible Docker lab + raw-socket exploit for CVE-2015-3306 (ProFTPD mod_copy pre-auth arbitrary file copy) — a patch-diffing learning exercise
 victorns69/cve-2024-12381
Exploit for Chrome V8 type confusion (CVE-2024-12381) with JSPI sandbox bypass, delivering RCE via a Flask server that fingerprints browsers and…
 astounds/copy-fail-cve-2026-31431
Local privilege escalation exploit for CVE-2026-31431, a Linux kernel AF_ALG + splice page-cache overwrite. Includes PoC, BPFtrace detection script,…
 ryan2929/cve-2026-43284-
Local privilege escalation exploit for Linux kernel CVE-2026-43284 (Dirty Flag), providing root access on vulnerable systems.
 cleozi/copy_grail
Elegant C++ exploit for CVE-2026-31431 (Copy Fail) using AF_ALG authenticated encryption + splice(2) to overwrite setuid binary memory