
brutus
 exbotanical/brutus
extensible exploitation framework shipped on a modular multi-tasking architecture
educationexploit-frameworksnetwork-security+6
exbotanical/brutusextensible exploitation framework shipped on a modular multi-tasking architecture
 tayontech/scope
AI agent set for cloud security purple teaming, runs inside Claude Code, Gemini CLI, and Codex.
 elevenpaths/siemframework
Modular Python3 attack framework for automating exploitation of SIEM platforms (Splunk, Graylog, OSSIM, QRadar, McAfee) via credential theft, payload…

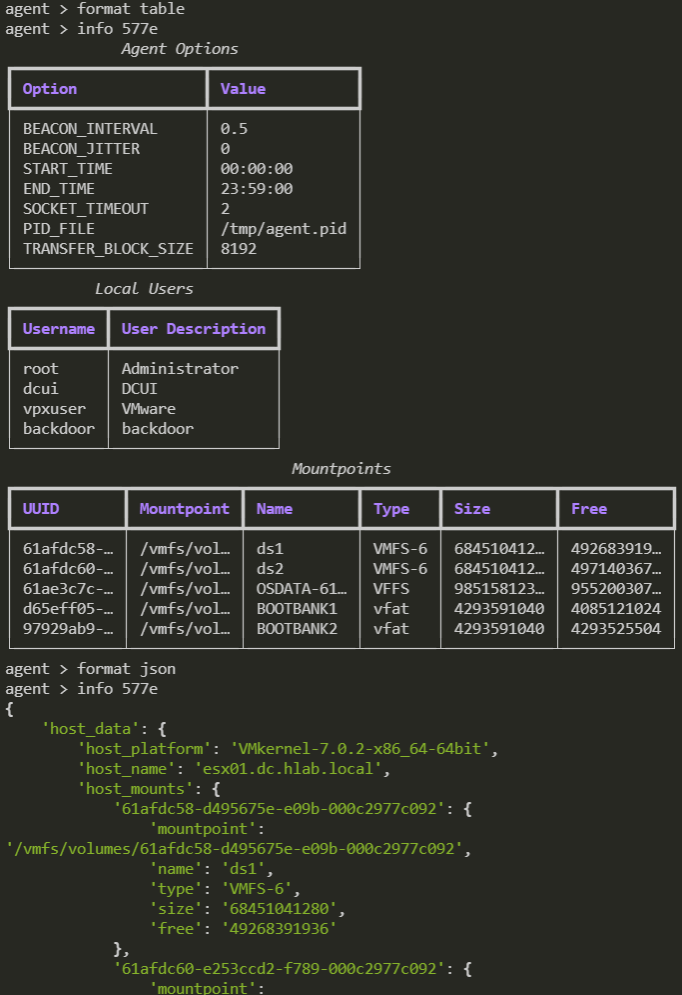 psmths/reave
WIP Post-exploitation framework tailored for hypervisors.
 cisc0-gif/kitt
Python-Based Pentesting Framework
 denizparlak/blackhat-arsenal-tools
Black Hat Arsenal Tools Official Account
 owasp/redteamtoolkit
The WASM Based Security Toolkit for the Web First Paradigm
 01rabbit/pakuri-thon
PAKURI-THON is a tool that supports pentesters with various pentesting tools and C4 server (command & control and chat & communication server).…
 ajutamangdev/hatiyar
Modular penetration testing framework with a Metasploit-like interactive shell, pre-built CVE exploit modules, and cloud/network reconnaissance…
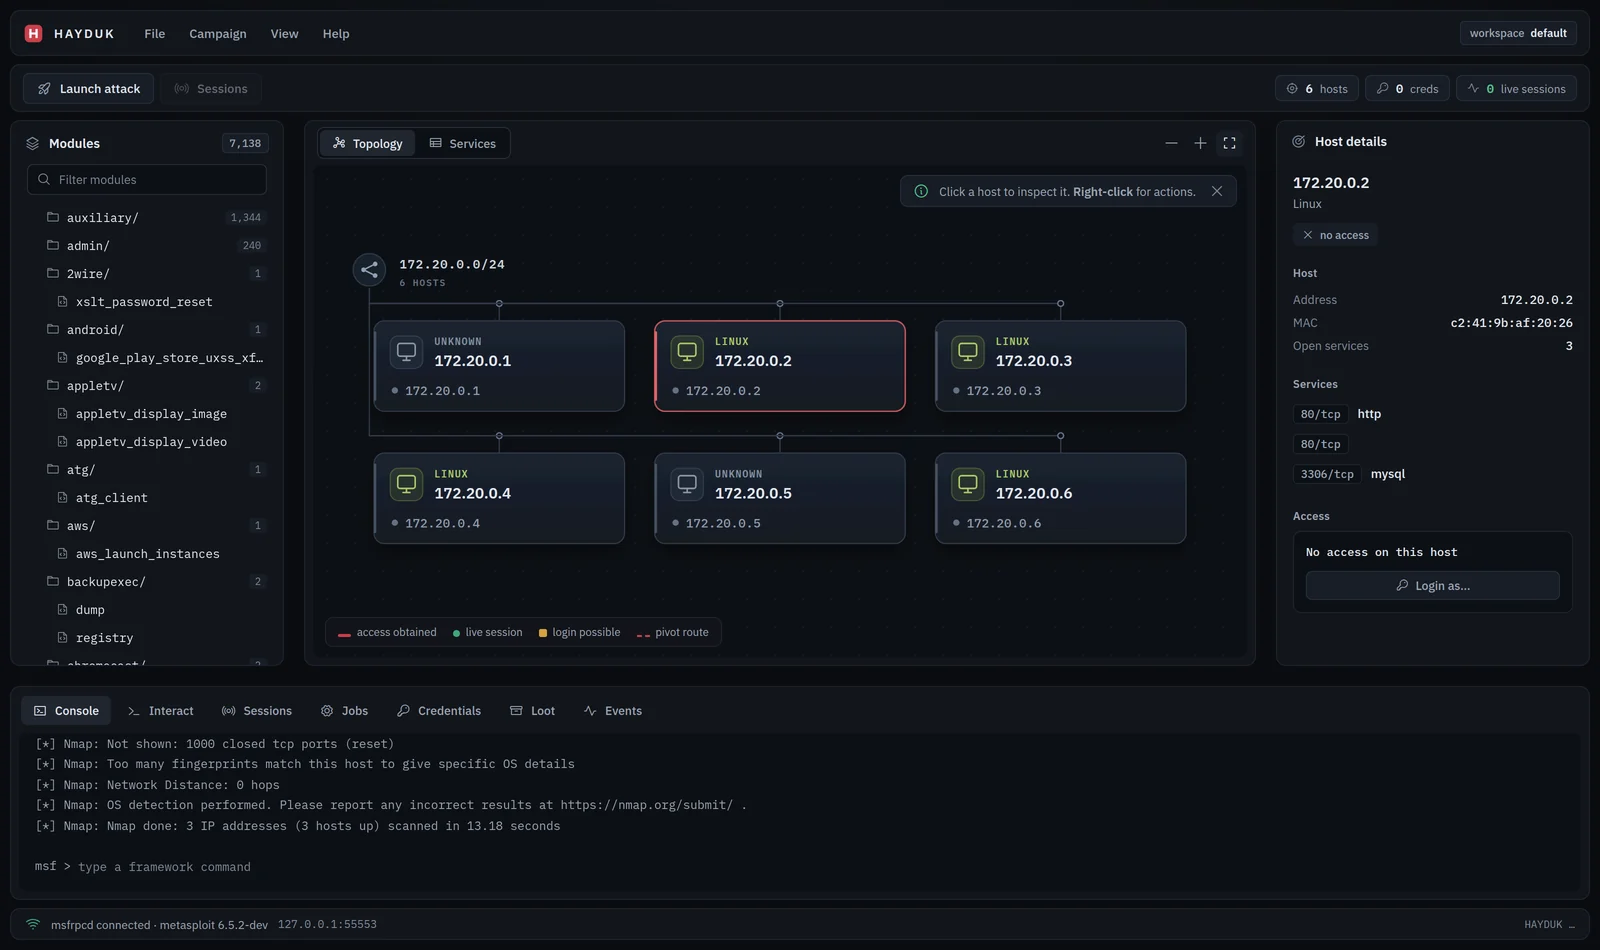 jolovicdev/hayduk
Graphical attack management console for Metasploit: the lineage of Armitage as a single Go binary with a browser UI. Live network topology, campaign…
 leviticus-triage/chromsploit-framework
Advanced AI-Powered Exploitation Framework | CVE-2025-4664 & CVE-2025-2783 & CVE-2025-2857 & CVE-2025-30397 |
 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
 taroballzchen/cve-2021-44228-log4jvulnscanner-metasploit
open detection and scanning tool for discovering and fuzzing for Log4J RCE CVE-2021-44228 vulnerability
 murataydemir/cve-2020-17519
[CVE-2020-17519] Apache Flink RESTful API Arbitrary File Read
 zeop-cybersec/citrix_adc_netscaler_lfi
This Metasploit-Framework module can be use to help companies to check the last Citrix vulnerability CVE-2020-8193, CVE-2020-8195 and CVE-2020-8196…
 ransomwares/there-is-a-cve
Pentesting tool integrating Shodan for IP reconnaissance and CVE identification, with Metasploit and Exploit-DB integration for automated exploit…