
ThisSeemsWrong
 michalbednarski/thisseemswrong
Writeup and exploit for CVE-2024-49746: Android's Parcel::continueWrite closing File Descriptors that are later used
android-securitybinary-exploitationexploit-frameworks+3
47
michalbednarski/thisseemswrongWriteup and exploit for CVE-2024-49746: Android's Parcel::continueWrite closing File Descriptors that are later used
 1n3/attacksurfacemanagement
Discover the attack surface and prioritize risks with our continuous Attack Surface Management (ASM) platform - Sn1per Professional #pentest #redteam…
 xtiankisutsa/twiga
A tool that enumerates Android devices for information useful in understanding its internals and for exploit development. It supports android 4.2 to…
 mateusverass/ngixshell
nginx CVE scanner + RCE exploit framework (CVE-2026-42945 + 16 others)
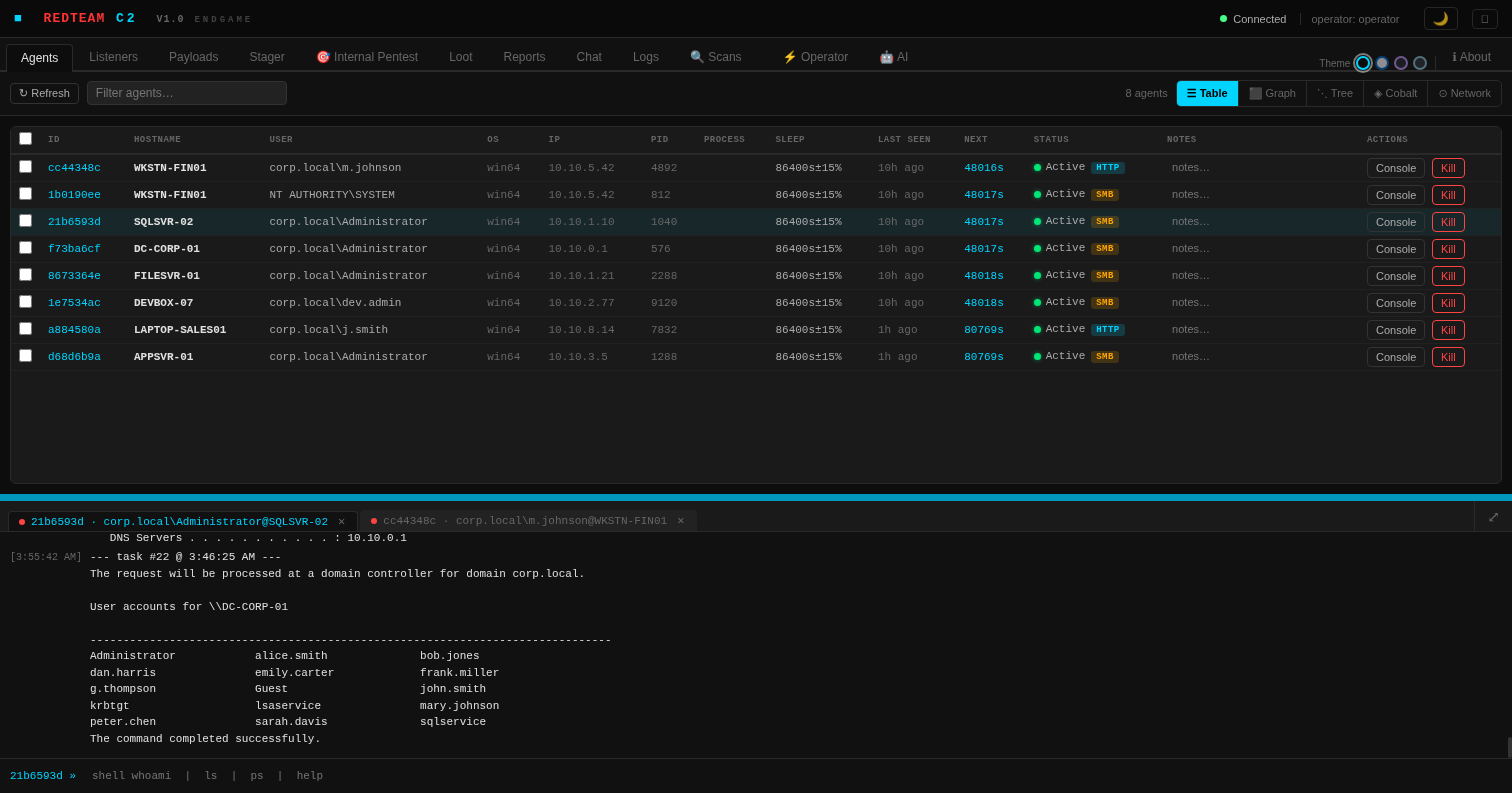 endgamec2framework/endgame
ENDGAME C2 FRAMEWORK — AI-powered command and control for professional red team operations
 karollooool/cve-2026-50416-writeup-and-poc
CVE-2026-50416: Windows 11 KASLR bypass
 exbotanical/brutus
extensible exploitation framework shipped on a modular multi-tasking architecture
 tayontech/scope
AI agent set for cloud security purple teaming, runs inside Claude Code, Gemini CLI, and Codex.
 elevenpaths/siemframework
Modular Python3 attack framework for automating exploitation of SIEM platforms (Splunk, Graylog, OSSIM, QRadar, McAfee) via credential theft, payload…
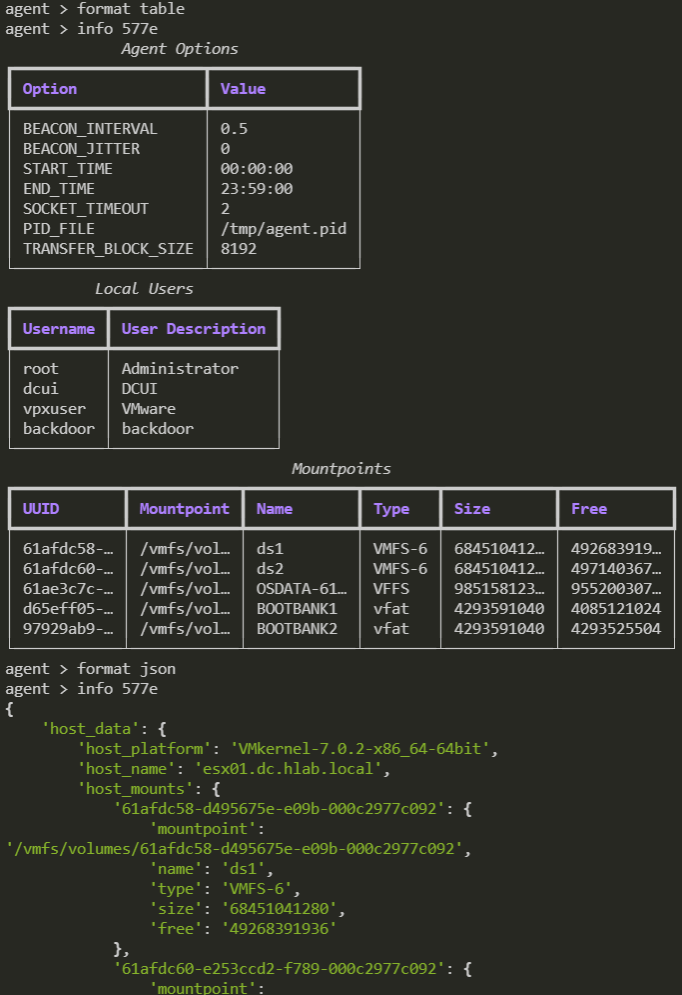 psmths/reave
WIP Post-exploitation framework tailored for hypervisors.
 cisc0-gif/kitt
Python-Based Pentesting Framework
 owasp/redteamtoolkit
The WASM Based Security Toolkit for the Web First Paradigm
 denizparlak/blackhat-arsenal-tools
Black Hat Arsenal Tools Official Account
 01rabbit/pakuri-thon
PAKURI-THON is a tool that supports pentesters with various pentesting tools and C4 server (command & control and chat & communication server).…
 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
 ajutamangdev/hatiyar
Modular penetration testing framework with a Metasploit-like interactive shell, pre-built CVE exploit modules, and cloud/network reconnaissance…
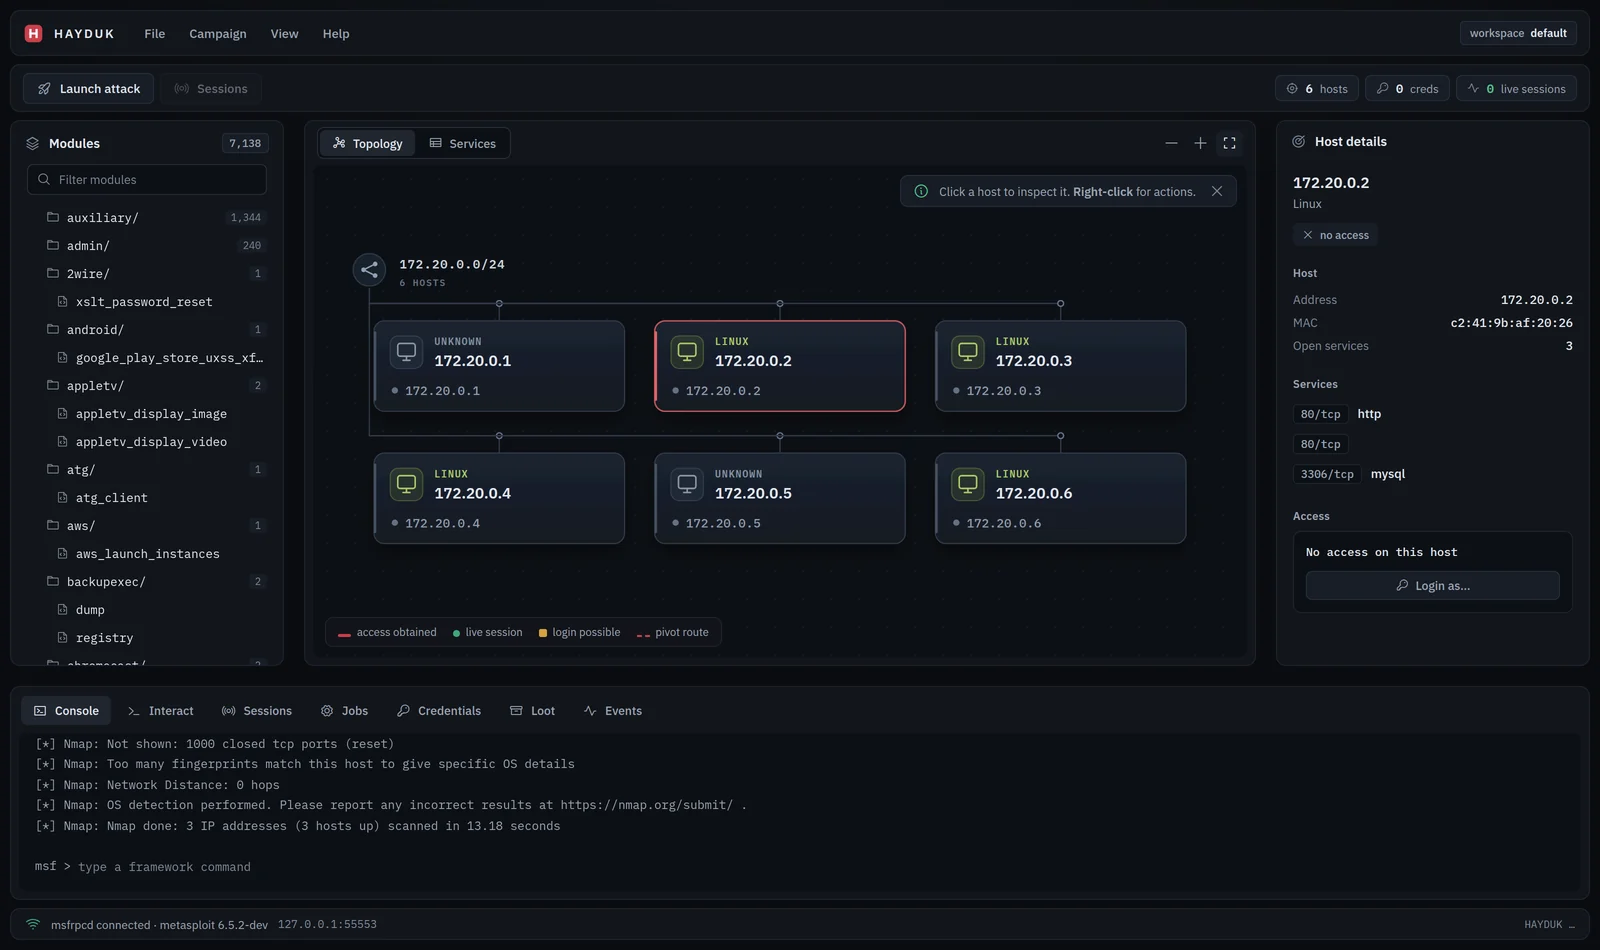 jolovicdev/hayduk
Graphical attack management console for Metasploit: the lineage of Armitage as a single Go binary with a browser UI. Live network topology, campaign…