
MalleableC2Profiles
 bluscreenofjeff/malleablec2profiles
Malleable C2 profiles for Cobalt Strike
command-and-controlexploit-frameworksnetwork-security+3
77
bluscreenofjeff/malleablec2profilesMalleable C2 profiles for Cobalt Strike
 codextf2/customc2channeltemplate
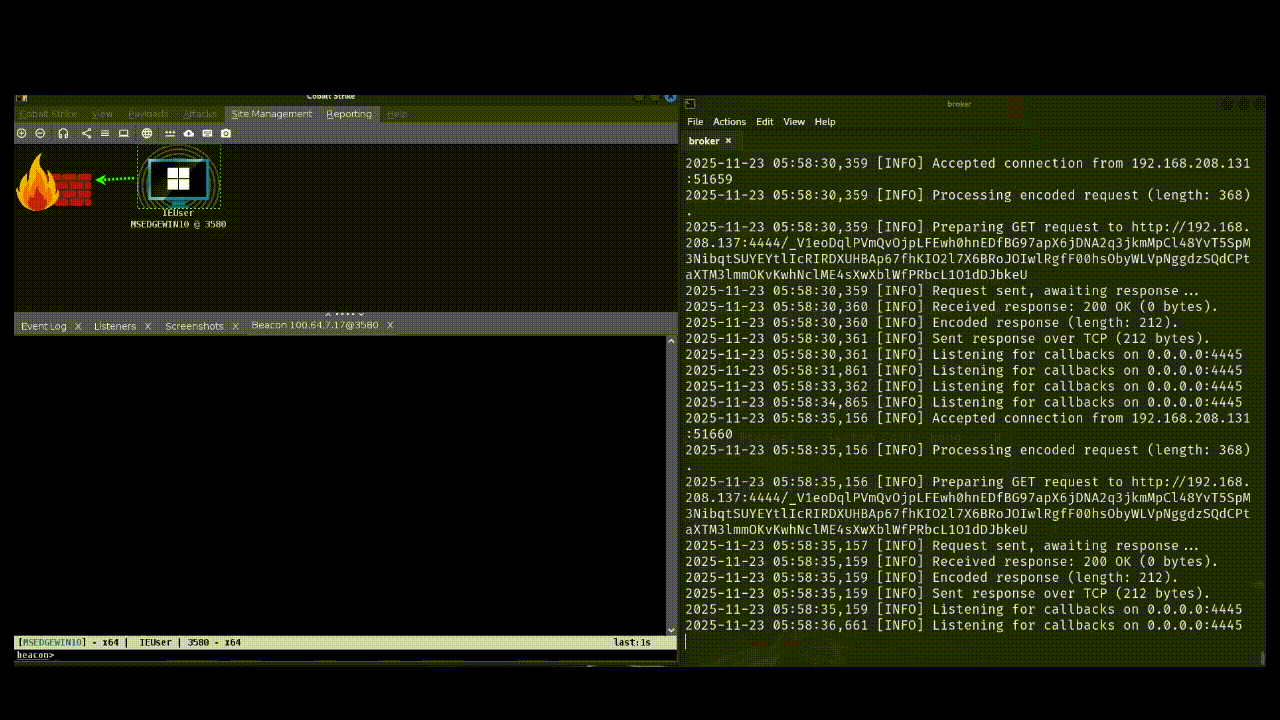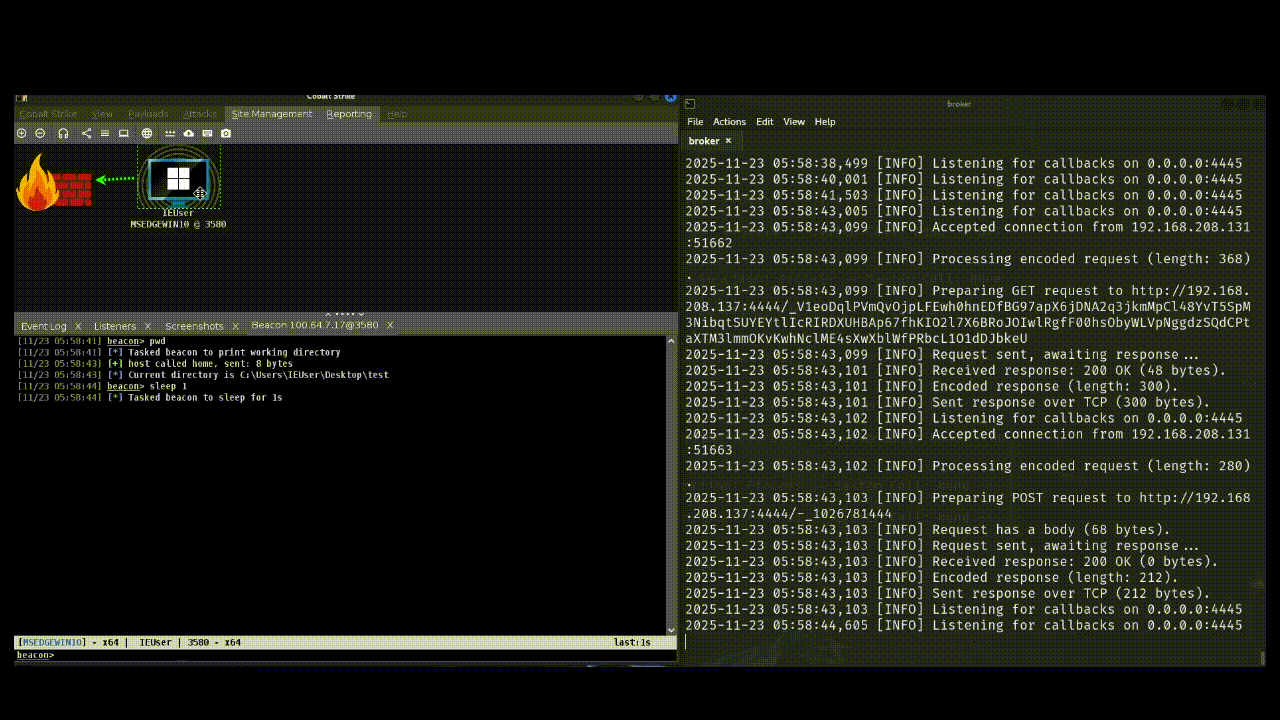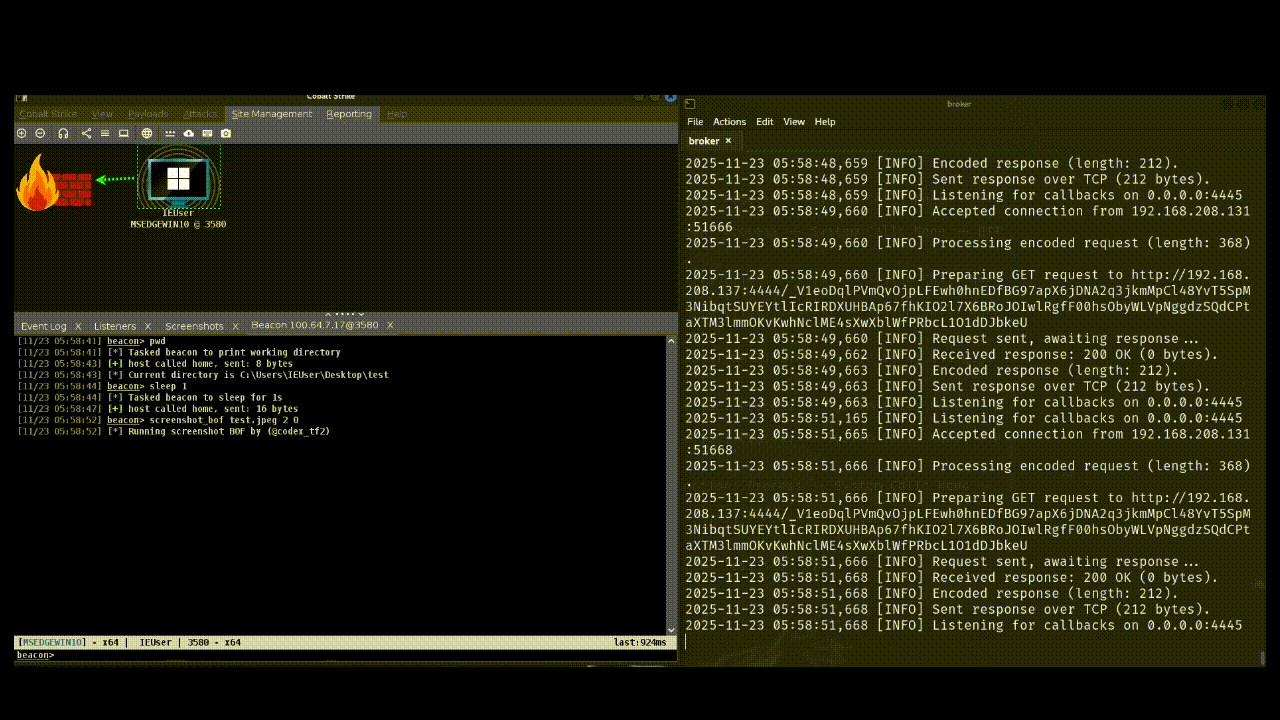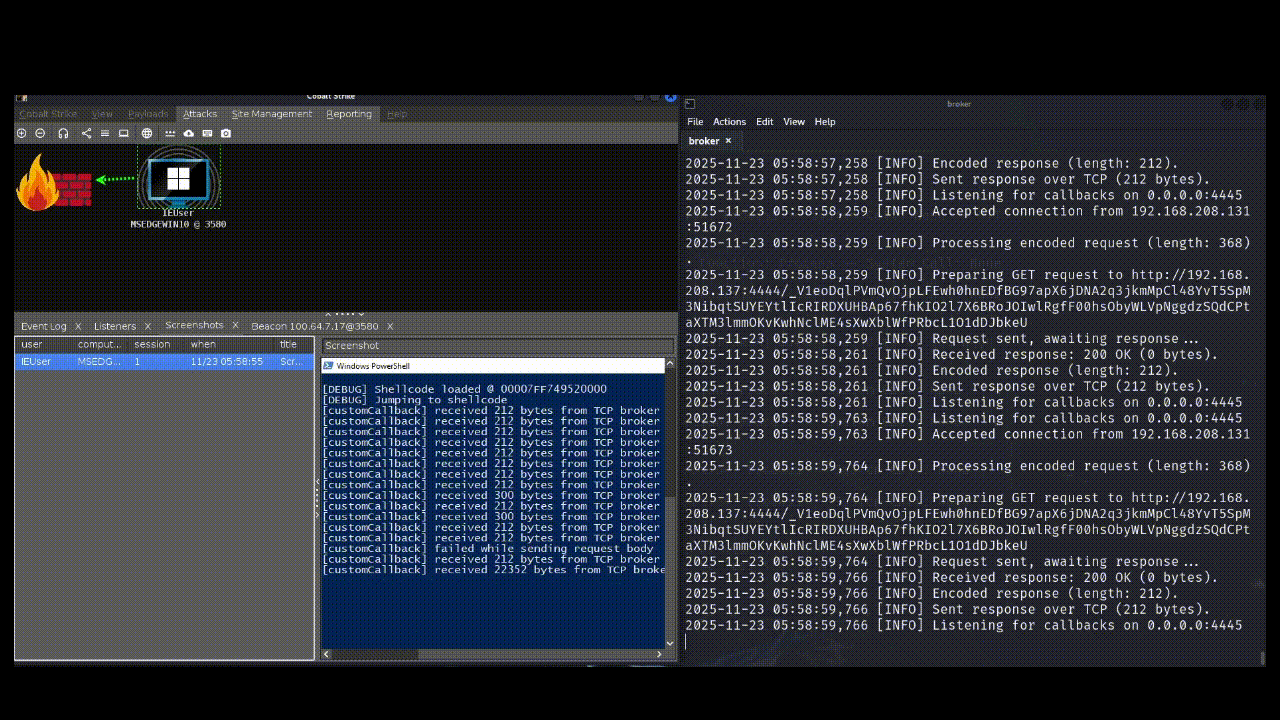
template for developing custom C2 channels for Cobalt Strike using IAT hooks applied by a reflective loader.
 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
 cedowens/mythic-macro-generator
Python3 script to generate a macro to launch a Mythic payload. Author: Cedric Owens
 averagesecurityguy/c2
A simple, extensible C&C beaconing system.
 n0qword/mythic_ornn
LLM-driven generator for Mythic Agents, Payload-Type and C2 Profiles.
 huynambka/cve-2026-26114-poc
Proof-of-concept exploit for CVE-2026-26114, a remote code execution vulnerability in Microsoft SharePoint, with a Python PoC and Metasploit module…
 degenerat3/meteor
A cross-platform C2/teamserver supporting multiple transport protocols, written in Go.
 alexlinov/miniplasma-runner
CVE-2020-17103 adapted for C2 with split-binary SYSTEM callback
 xzajyjs/cve-2022-39197-poc
CVE-2022-39197(CobaltStrike XSS <=4.7) POC
 qmadev/crabloader
Rust-based User-Defined Reflective Loader for Cobalt Strike payloads. Avoids RWX memory pages for OPSEC safety. Includes an extractor tool for loader…
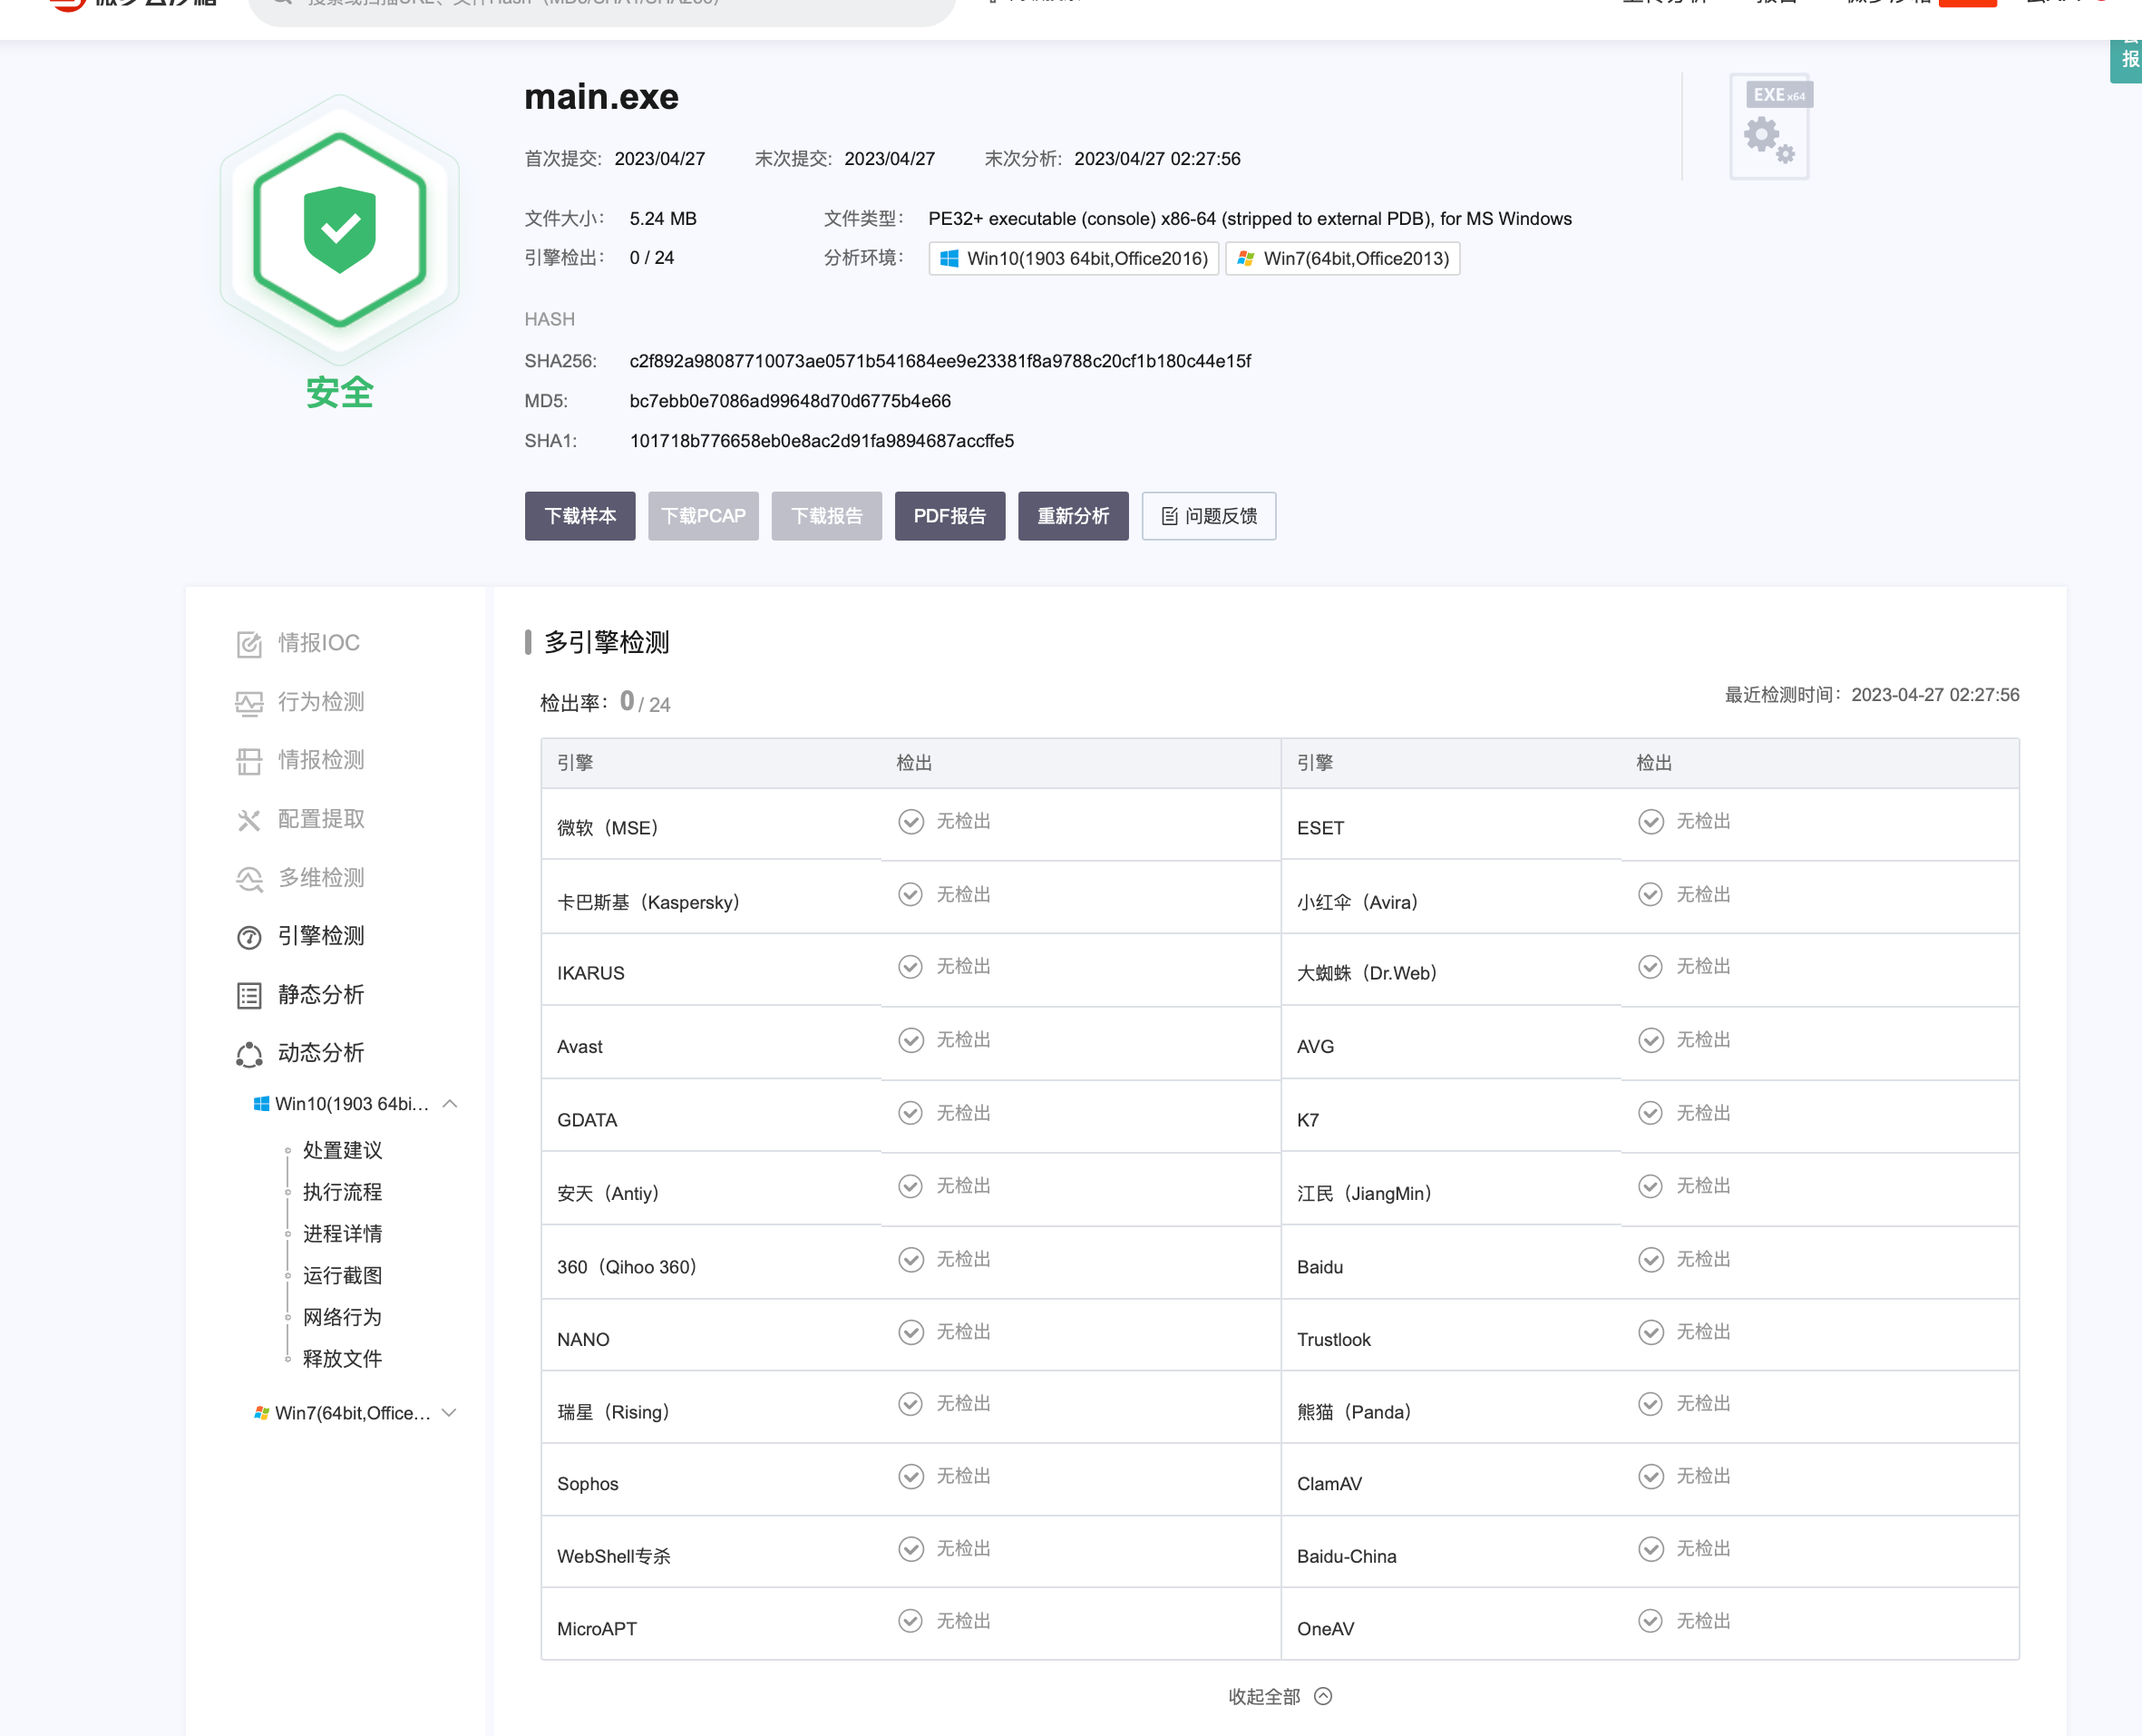 xiao-zhu-zhu/pig_cs4.4
Cobalt Strike 4.4 猪猪版 去暗桩 去流量特征 beacon仿造真实API服务 修补CVE-2022-39197补丁
 attackercan/wp2shell-poc2
CVE-2026-63030
 lovechoudoufu/about_cobaltstrike4.5_cdf
cobaltstrike4.5版本破解、去除checksum8特征、bypass BeaconEye、修复错误路径泄漏stage、增加totp双因子验证、修复CVE-2022-39197等
 hluwa/cobaltstrike_swing_xss2rce
Exploit for CVE-2022-39197, a cross-site scripting vulnerability in Cobalt Strike's Swing GUI that enables remote code execution on team servers.
 epsilonpointori/ikev2-poc
IKEv2, ikeext.dll, CVE-2026-33824, double free, heap grooming, ROP, SKF fragmentation, Windows exploit, anti-debug, obfuscation, API hooking,…

 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
 coolman6942o/-exploit-cve-2023-36025
Windows SmartScreen Security Feature Bypass Vulnerability