
CVE-2019-0708
 frostsaberx/cve-2019-0708
CVE-2019-0708 With Metasploit-Framework Exploit
exploitationexploit-frameworkspenetration-testing+3
4
frostsaberx/cve-2019-0708CVE-2019-0708 With Metasploit-Framework Exploit
 yakumwamba/poc-cve-2021-4034
Proof-of-concept exploit for CVE-2021-4034 (PwnKit), a local privilege escalation in polkit's pkexec, verified on Debian 10 and CentOS 7.
 mauricelambert/cve-2021-31166
CVE-2021-31166: exploitation with Powershell, Python, Ruby, NMAP and Metasploit.
 whokilleddb/cve-2021-4034
Local privilege escalation exploit for CVE-2021-4034 (PwnKit) targeting polkit's pkexec, providing root shell access on vulnerable Linux systems.
 black-army-security/blackarmy-framework
Modular Python-based penetration testing framework for automated security assessments, exploitation, and red team operations. Includes modules for…
 sneakynachos/cve-2026-4692-trust-me-im-in-rdm
Proof-of-concept exploit for Firefox BrowsingContext authorization bypass (CVE-2026-4692), demonstrating forged IPC messages to set InRDMPane and…
 tiagob0b/cve-2021-22005
Metasploit module for CVE-2021-22005 VMware vCenter arbitrary file upload vulnerability with proof-of-concept and remote code execution exploit.
 randomrobbiebf/wordpress-php-object-helper
Know a plugin has a php object exploit but need to find which lib to use?
 n1shant-sinha/cve-2017-0199
Exploit toolkit CVE-2017-0199 - v2.0 is a handy python script which provides a quick and effective way to exploit Microsoft RTF RCE. It could…
 0rioncollector/exploit-chain-cve-2025-6018-6019
Exploit Chain of CVE-2025-6018 to CVE-2025-6019
 ang3ll/cve-2025-66177
CVE-2025-66177 Metasploit exploit for Hikvision NVR firmware v4.72 and v4.83
 thejoyofhacking/berdav-cve-2021-4034
Exploit for CVE-2021-4034 (PwnKit) that provides a root shell via polkit pkexec. Includes a dry-run mode to test vulnerability and a one-liner script…
 callrbx/pkexec-lpe-poc
Proof-of-concept exploit for CVE-2021-4034, a local privilege escalation in pkexec, allowing arbitrary payload execution with root privileges.
 neseos-corp/cve-2026-50657
Exploit code for CVE-2026-50657 targeting Nese Vista through Nese 11 (BETA). Includes patch details and affected OS versions for security testing and…
 izxci/cve-2026-49083
Python exploit for CVE-2026-49083 targeting privilege escalation in the LatePoint Calendar Booking WordPress plugin. Provides automated exploitation…
 ljp-tw/cve-2021-4034
Exploit for CVE-2021-4034, a local privilege escalation in pkexec, providing proof-of-concept code and a detailed writeup.
 ccievoice2009/cve-2024-49112
Exploit for CVE-2024-49112, a critical Windows LDAP RCE vulnerability, triggering a crash via crafted Netlogon and LDAP interactions.
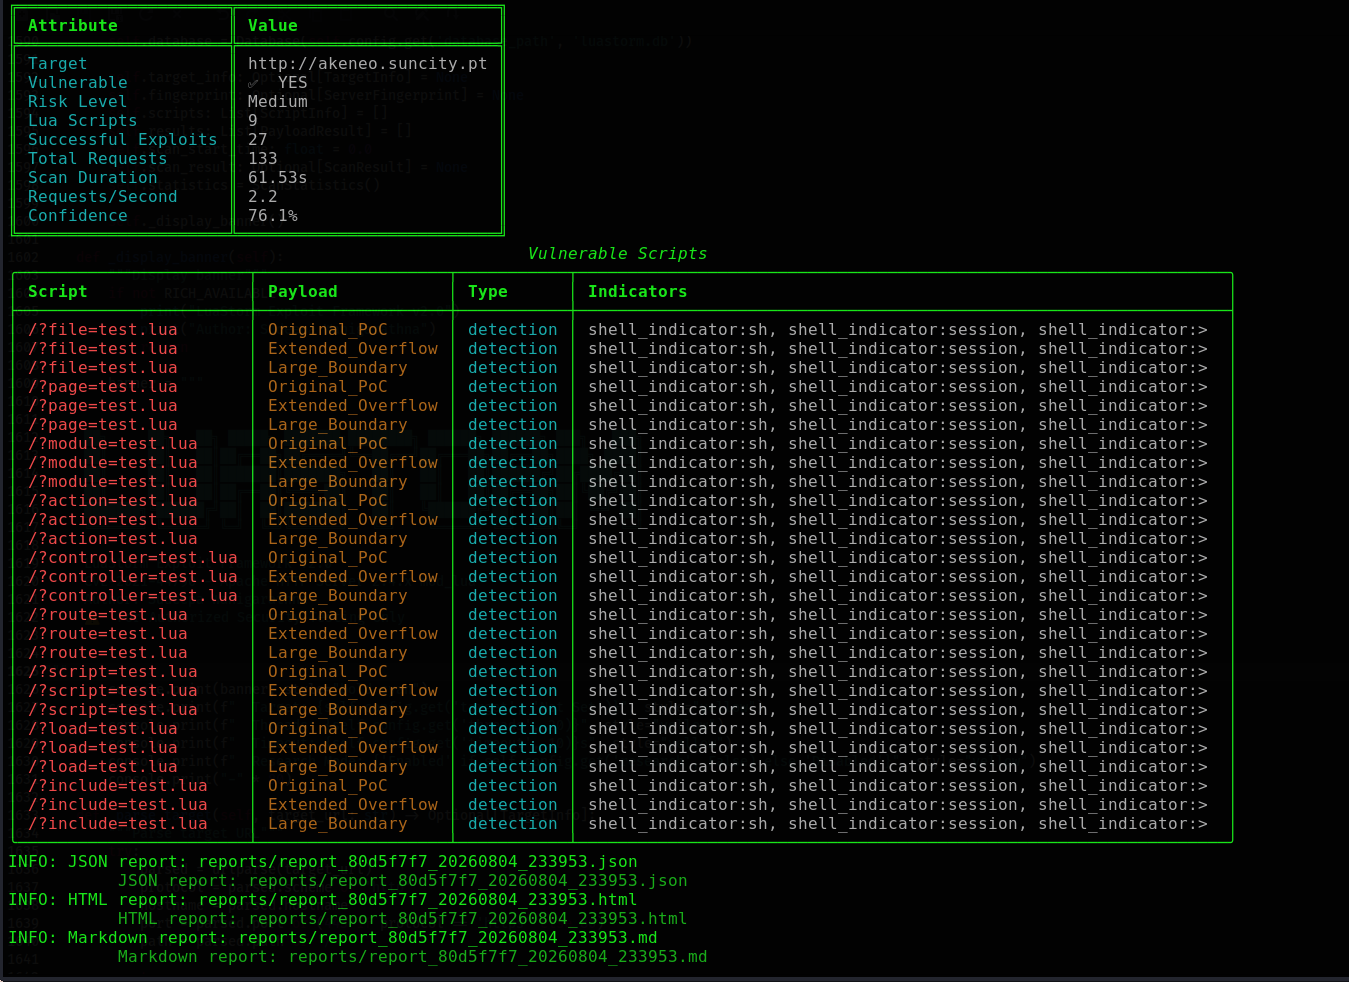 cerberusmrxi/apache-lua-buffer-overflow-exploit-cve-2021-44790
Apache HTTP Server 2.4.x mod_lua Buffer Overflow (CVE-2021-44790) - Advanced exploitation framework with fingerprinting, multi-stage scanning, plugin…