
Redcloud
 khast3x/redcloud
Automated Red Team Infrastructure deployement using Docker
container-securityexploit-frameworkspenetration-testing-frameworks+1
1.3k4 years ago
khast3x/redcloudAutomated Red Team Infrastructure deployement using Docker
 funnywolf/pystinger
Bypass firewall for traffic forwarding using webshell
 pablosnt/rekono
Offensive security platform that automates attack surface discovery and vulnerability management

 mgeeky/threadstackspoofer
Thread Stack Spoofing - PoC for an advanced In-Memory evasion technique allowing to better hide injected shellcode's memory allocation from scanners…
 vulncheck-oss/go-exploit
Go-based exploit development framework with built-in phases for target verification, version scanning, exploitation, and C2. Supports multiple…
 reverseclabs/wepwnise
WePWNise generates architecture independent VBA code to be used in Office documents or templates and automates bypassing application control and…
 0xthirteen/movekit
Cobalt Strike kit for Lateral Movement
 sgxgsx/bluetoolkit
Modular Bluetooth Classic (BR/EDR) vulnerability testing framework with reconnaissance, exploit modules for 43 public attacks/CVEs, and structured…
 kyleavery/aceldr
Cobalt Strike UDRL for memory scanner evasion.
 mythicagents/thanatos
Mythic C2 agent targeting Linux and Windows hosts written in Rust
 hatriot/clusterd
application server attack toolkit
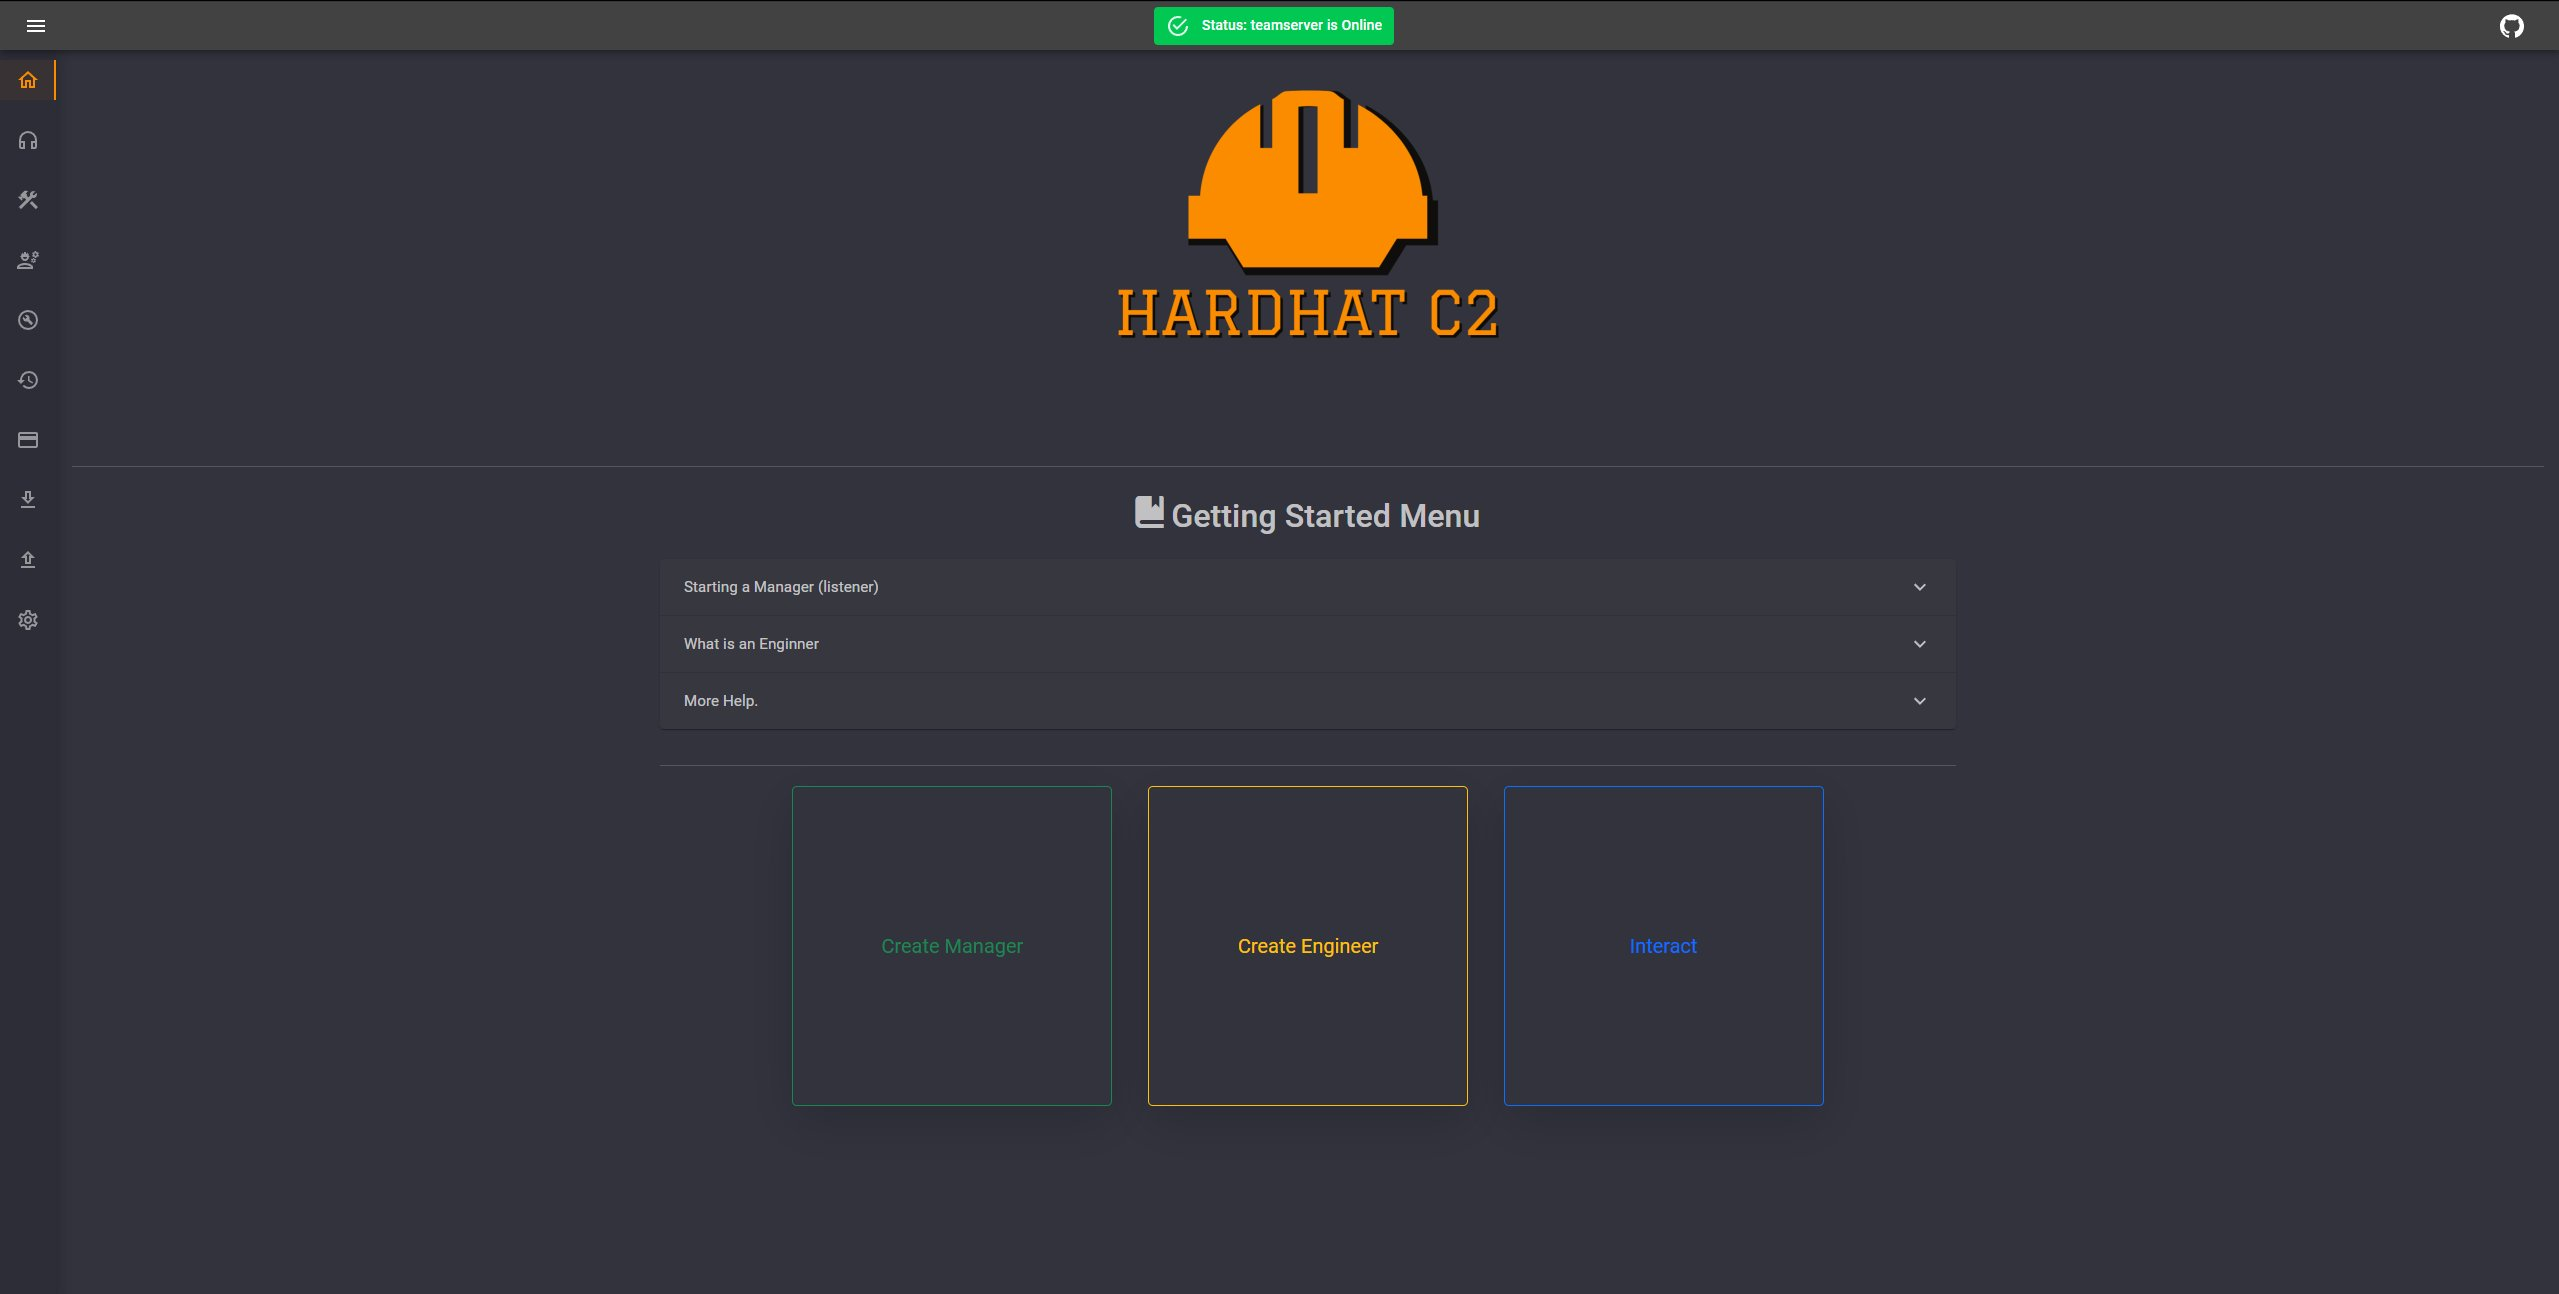 dragoqcc/cruciblec2
A C# Command & Control framework
 rvn0xsy/cooolis-ms
Cooolis-ms是一个包含了Metasploit Payload Loader、Cobalt Strike External C2 Loader、Reflective DLL injection的代码执行工具,它的定位在于能够在静态查杀上规避一些我们将要执行且含有特征的代码,帮助红队人员更方便快…
 qax-a-team/cobaltstrike-toolset
Aggressor Script, Kits, Malleable C2 Profiles, External C2 and so on
 fozavci/viproy-voipkit
VIPROY - VoIP Pen-Test Kit for Metasploit Framework
 allfro/sploitego
Maltego Penetration Testing Transforms
 aaaguirrep/offensive-docker
Offensive Docker is an image with the more used offensive tools to create an environment easily and quickly to launch assessment to the targets.