
ThreadStackSpoofer
Thread Stack Spoofing - PoC for an advanced In-Memory evasion technique allowing to better hide injected shellcode's memory allocation from scanners…

Thread Stack Spoofing - PoC for an advanced In-Memory evasion technique allowing to better hide injected shellcode's memory allocation from scanners…

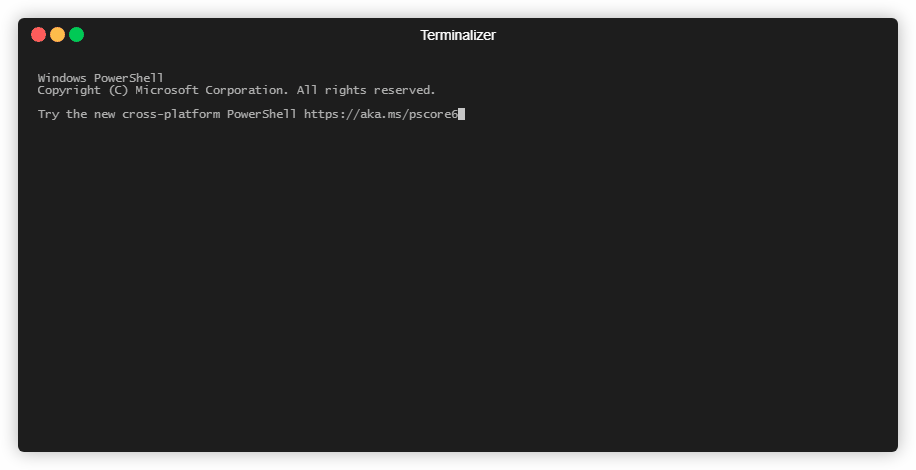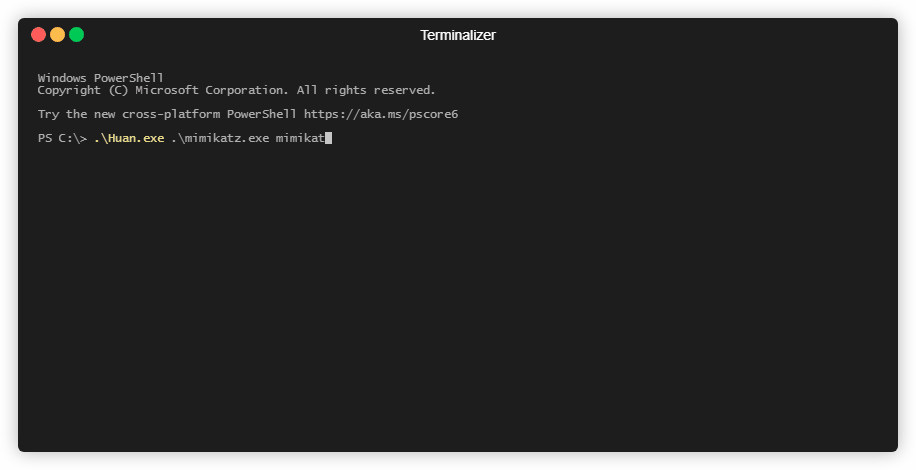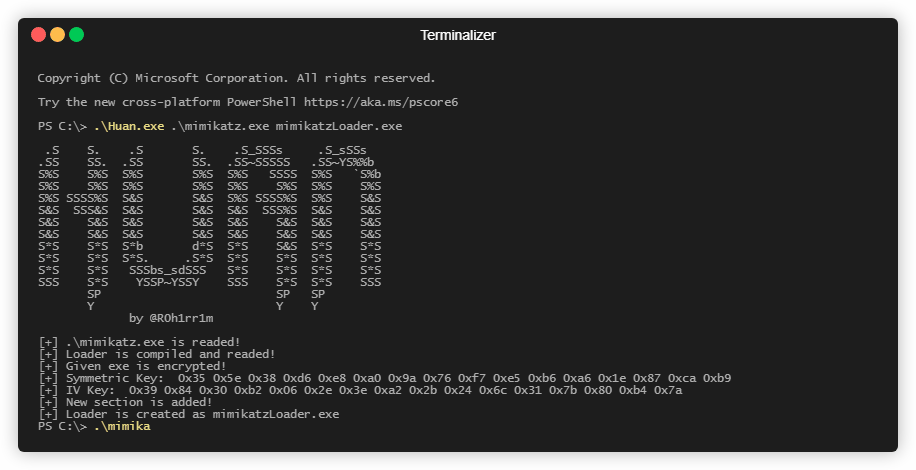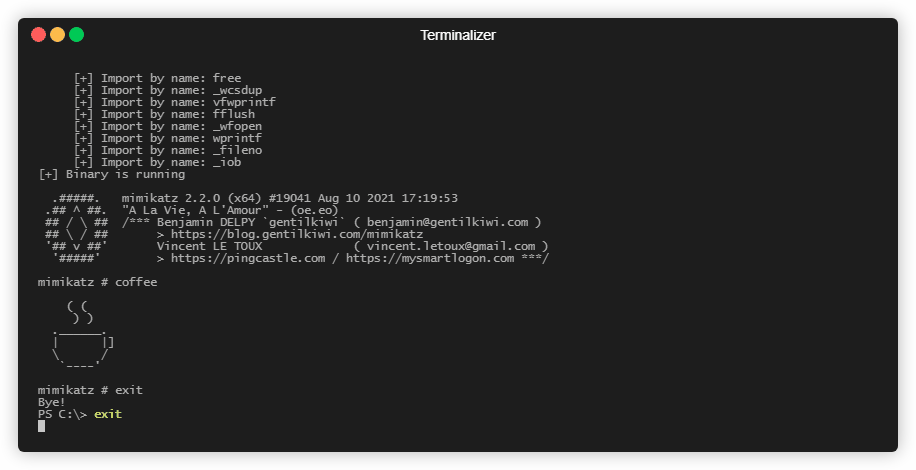
Encrypted PE Loader Generator

Maltego Penetration Testing Transforms

Powershell C2 Server and Implants

WePWNise generates architecture independent VBA code to be used in Office documents or templates and automates bypassing application control and…

Cobalt Strike BOF - Bypass AMSI in a remote process with code injection.

ROP-based sleep obfuscation to evade memory scanners

Automated penetration testing tool using Cyber Attack Techniques Scoring (CATS) to select and execute optimal attack scenarios via Metasploit, Nmap,…

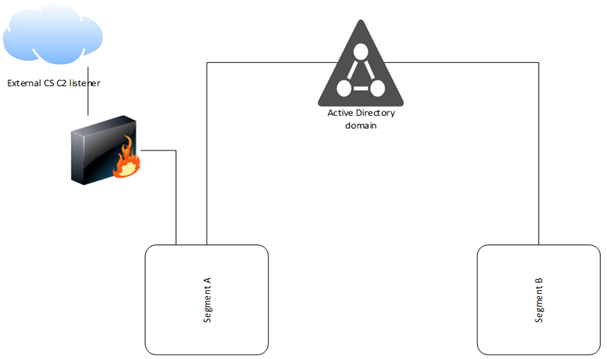
C2 tool routing Cobalt Strike beacon data over LDAP user attributes for stealthy command-and-control in segmented networks.

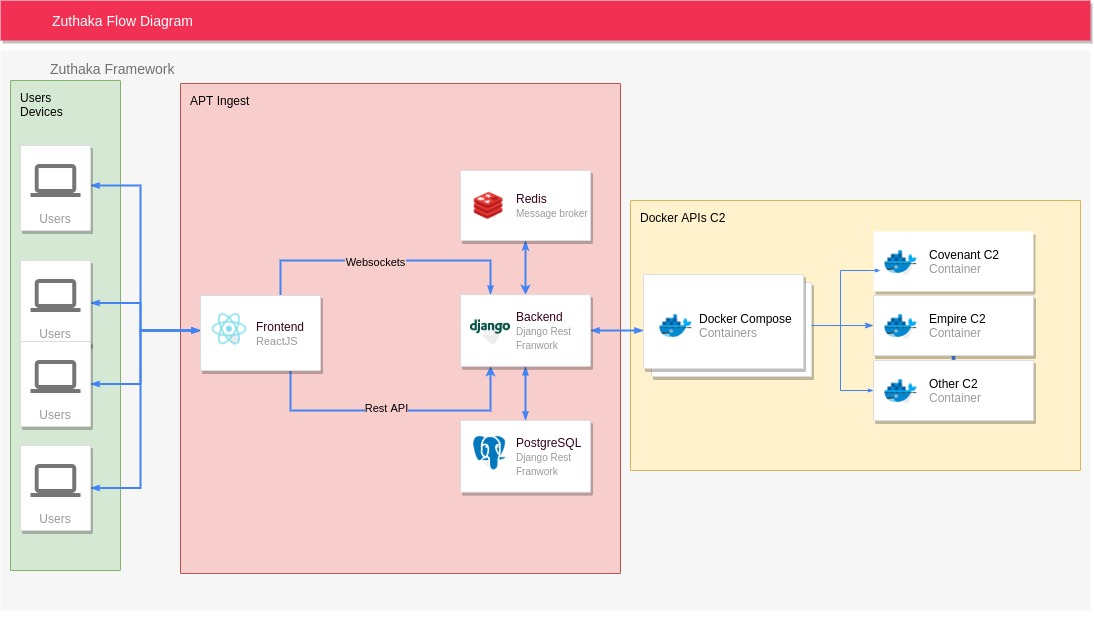
Open-source C2 integration framework providing a unified web interface for managing multiple command-and-control instances, listeners, agents, and…

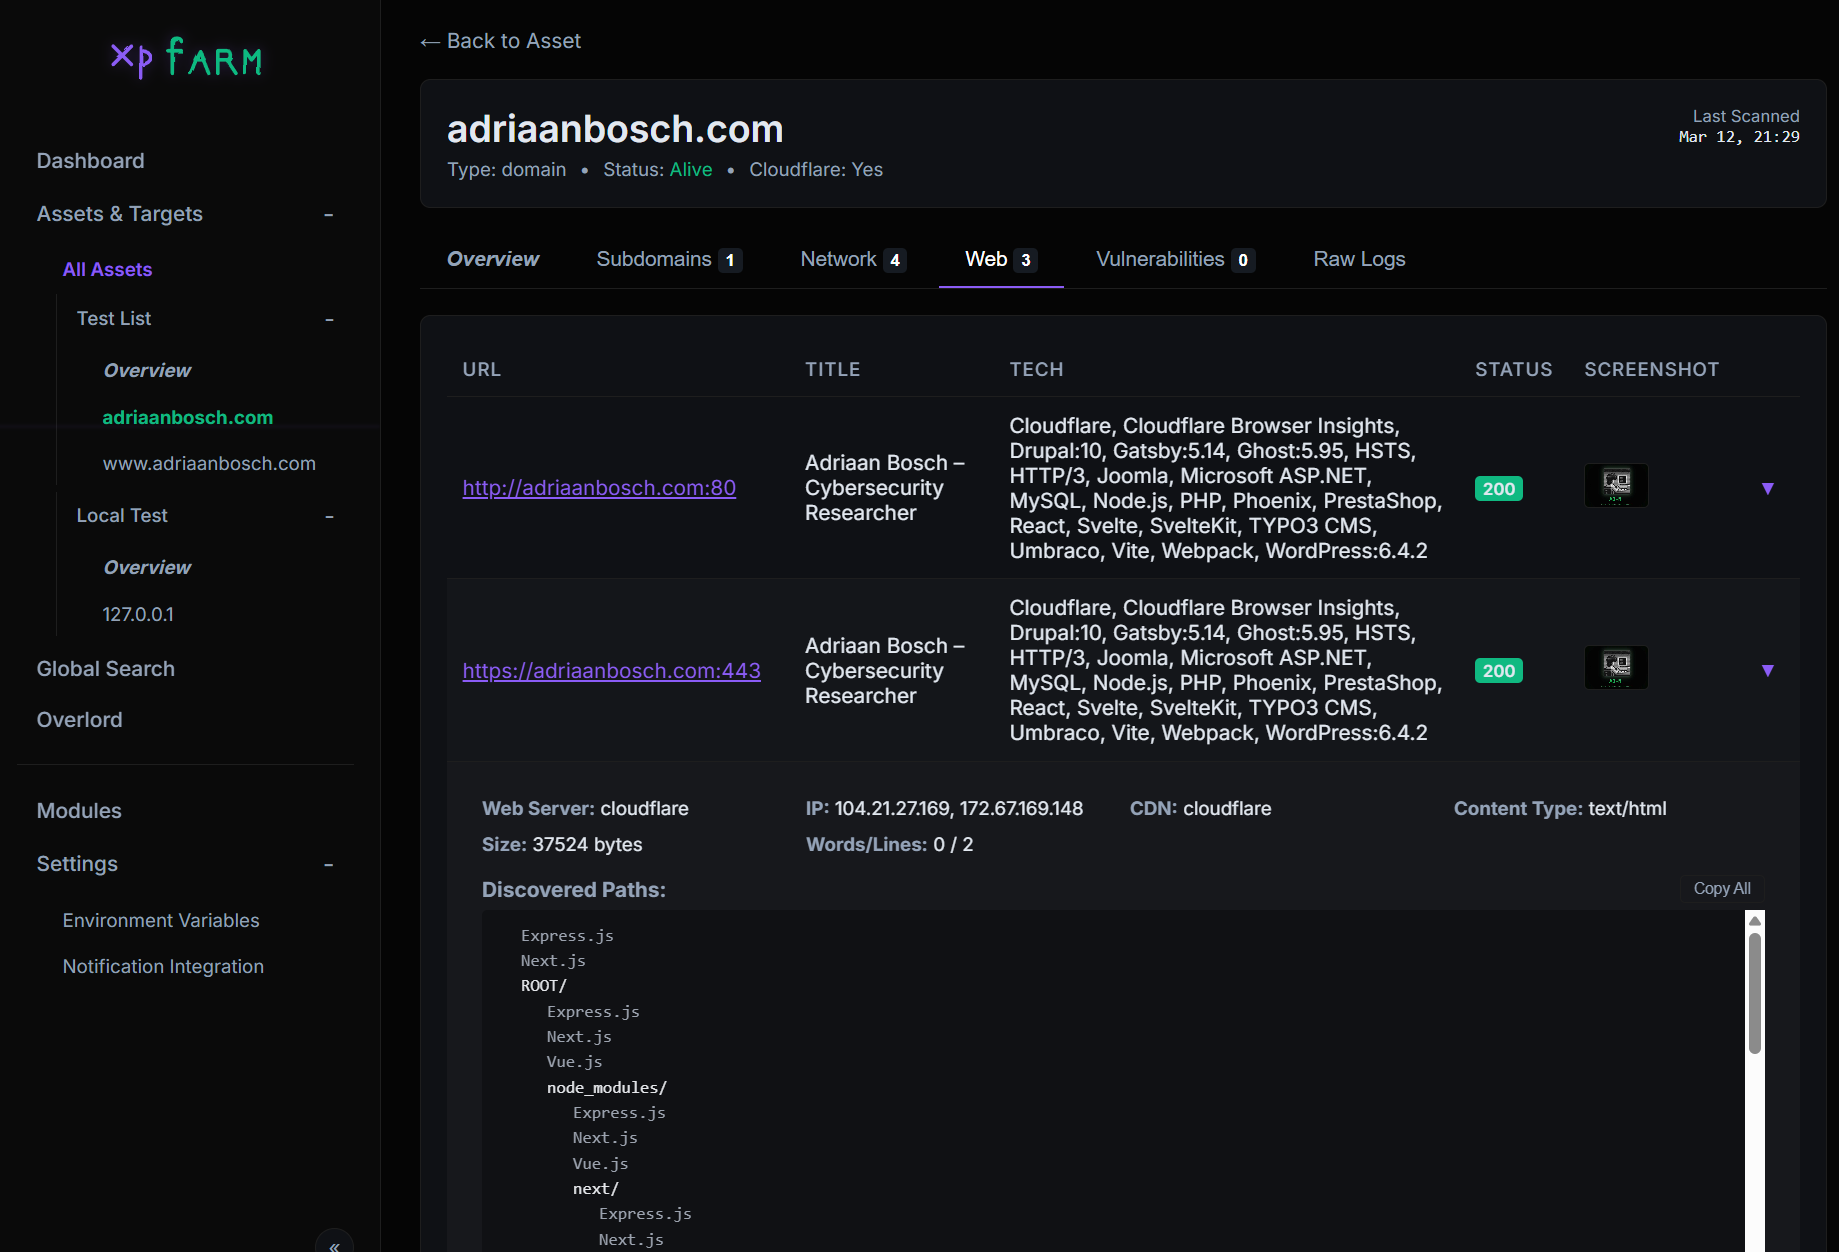
Automated bug bounty & recon framework — wraps Subfinder, Naabu, Httpx, Nuclei, Nmap, CVEMap, Gowitness, Katana & more behind a unified web UI

Forth-based compiler deployed as position-independent x86_64 shellcode, providing a remote code execution agent with interactive REPL over TCP, HTTP,…

Exploit for CVE-2023-0179, a stack buffer overflow in the Linux nftables subsystem, enabling unprivileged local privilege escalation to root via…

ARTi-C2 is a post-exploitation framework used to execute Atomic Red Team test cases with rapid payload deployment and execution capabilities via…

Mogwai Java Management Extensions (JMX) Exploitation Toolkit

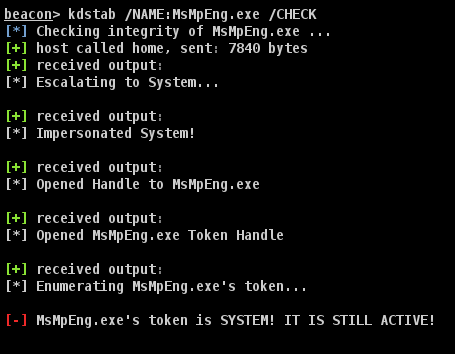
BOF combination of KillDefender and Backstab

PowerSploit - A PowerShell Post-Exploitation Framework

Curated collection of cybersecurity learning resources, CTF writeups, research papers, and practical labs for hands-on skill development across web…