

Tentacle
 orleven/tentacle
Tentacle is a POC vulnerability verification and exploit framework. It supports free extension of exploits and uses POC scripts. It supports calls to…
exploit-frameworksinformation-gatheringpenetration-testing+2
374
orleven/tentacleTentacle is a POC vulnerability verification and exploit framework. It supports free extension of exploits and uses POC scripts. It supports calls to…
 0ca/boxpwnr
A modular framework for benchmarking LLMs and agentic strategies on security challenges across HackTheBox, TryHackMe, PortSwigger Labs, Cybench,…
 gl4ssesbo1/nebula
Nebula is a cloud C2 Framework, which at the moment offers reconnaissance, enumeration, exploitation, post exploitation on AWS, but still working to…
 mazen160/shennina
Automating Host Exploitation with AI
 jack-new-project/zeebsploit
Modular exploitation framework for penetration testing, featuring automated payload generation, reconnaissance modules, and post-exploitation…
 jiangsir404/poc-s
POC-T强化版本 POC-S , 用于红蓝对抗中快速验证Web应用漏洞, 对功能进行强化以及脚本进行分类添加,自带dnslog等, 平台补充来自vulhub靶机及其他开源项目的高可用POC
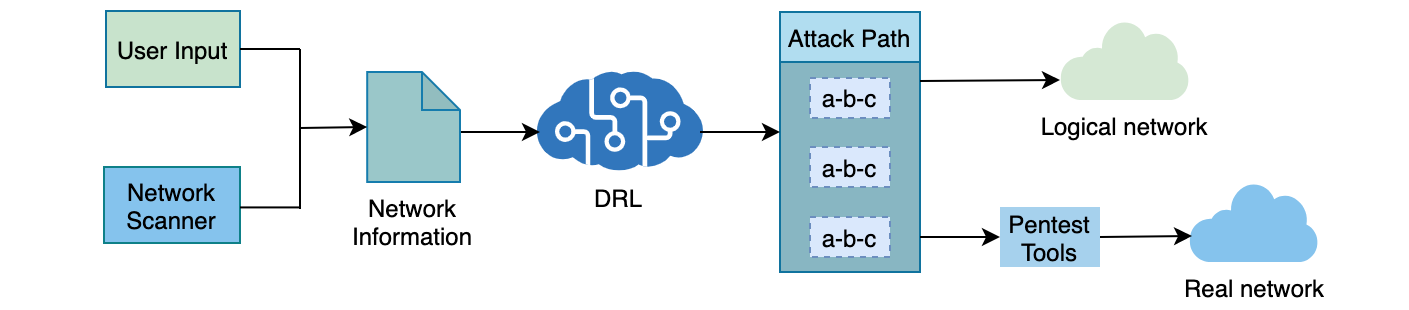 crond-jaist/autopentest-drl
AutoPentest-DRL: Automated Penetration Testing Using Deep Reinforcement Learning
 msd0pe-1/cve-maker
CLI tool to search CVEs and exploits from NIST, ExploitDB, and GitHub databases. Supports exploit compilation detection and lists latest critical…
 cleanunicorn/theo
Ethereum recon and exploitation tool.
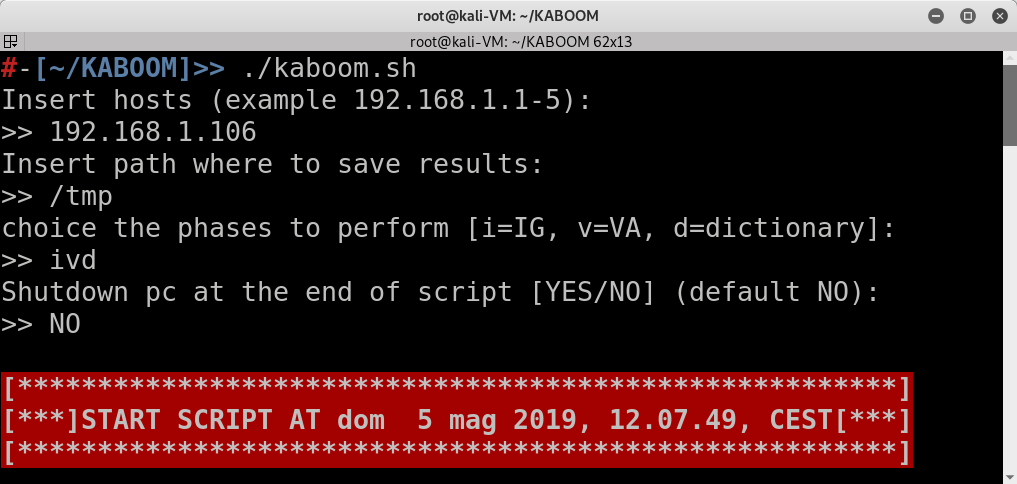 leviathan36/kaboom
A tool to automate penetration tests
 stevenaldinger/decker
Declarative penetration testing orchestration framework
 dviros/excalibur
Excalibur is an Eternalblue exploit payload based "Powershell" for the Bashbunny project.
 ruped24/killchain
A unified console to perform the "kill chain" stages of attacks.
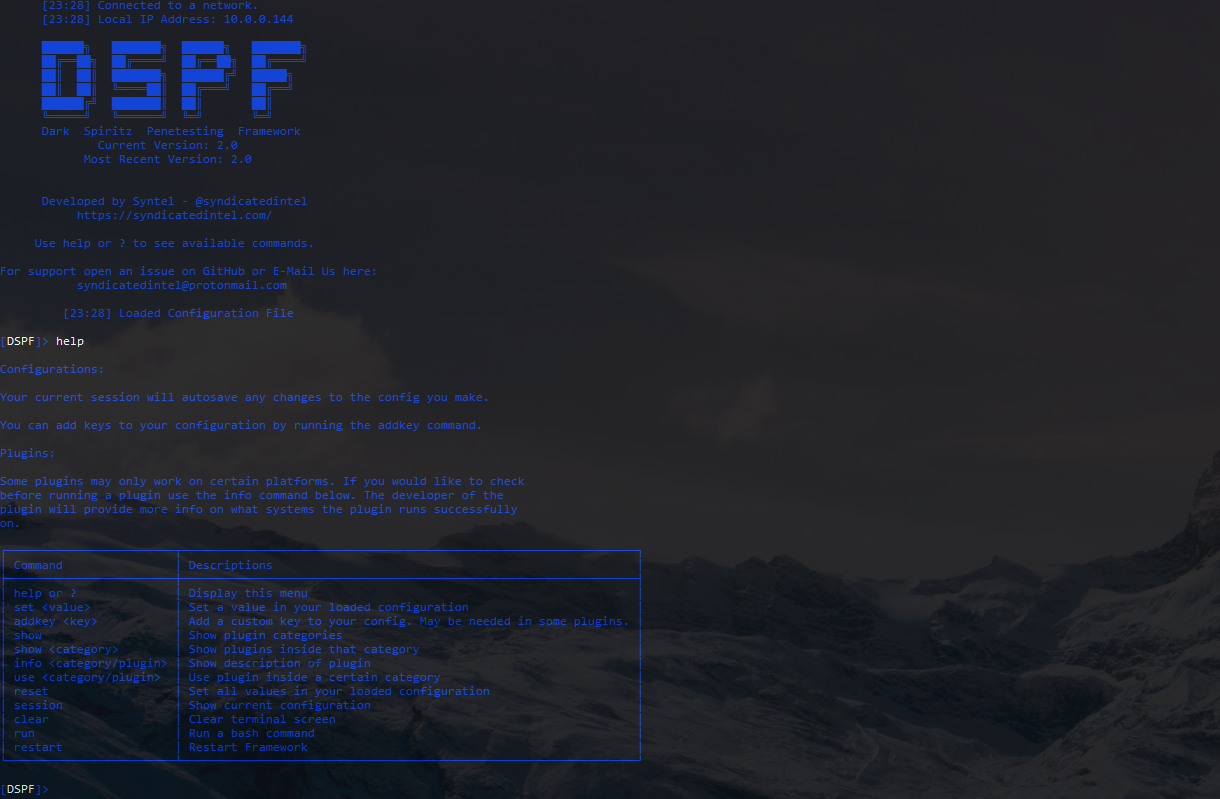 m4cs/darkspiritz
🌔 Official Repository for DarkSpiritz Penetration Framework | Written in Python 🐍
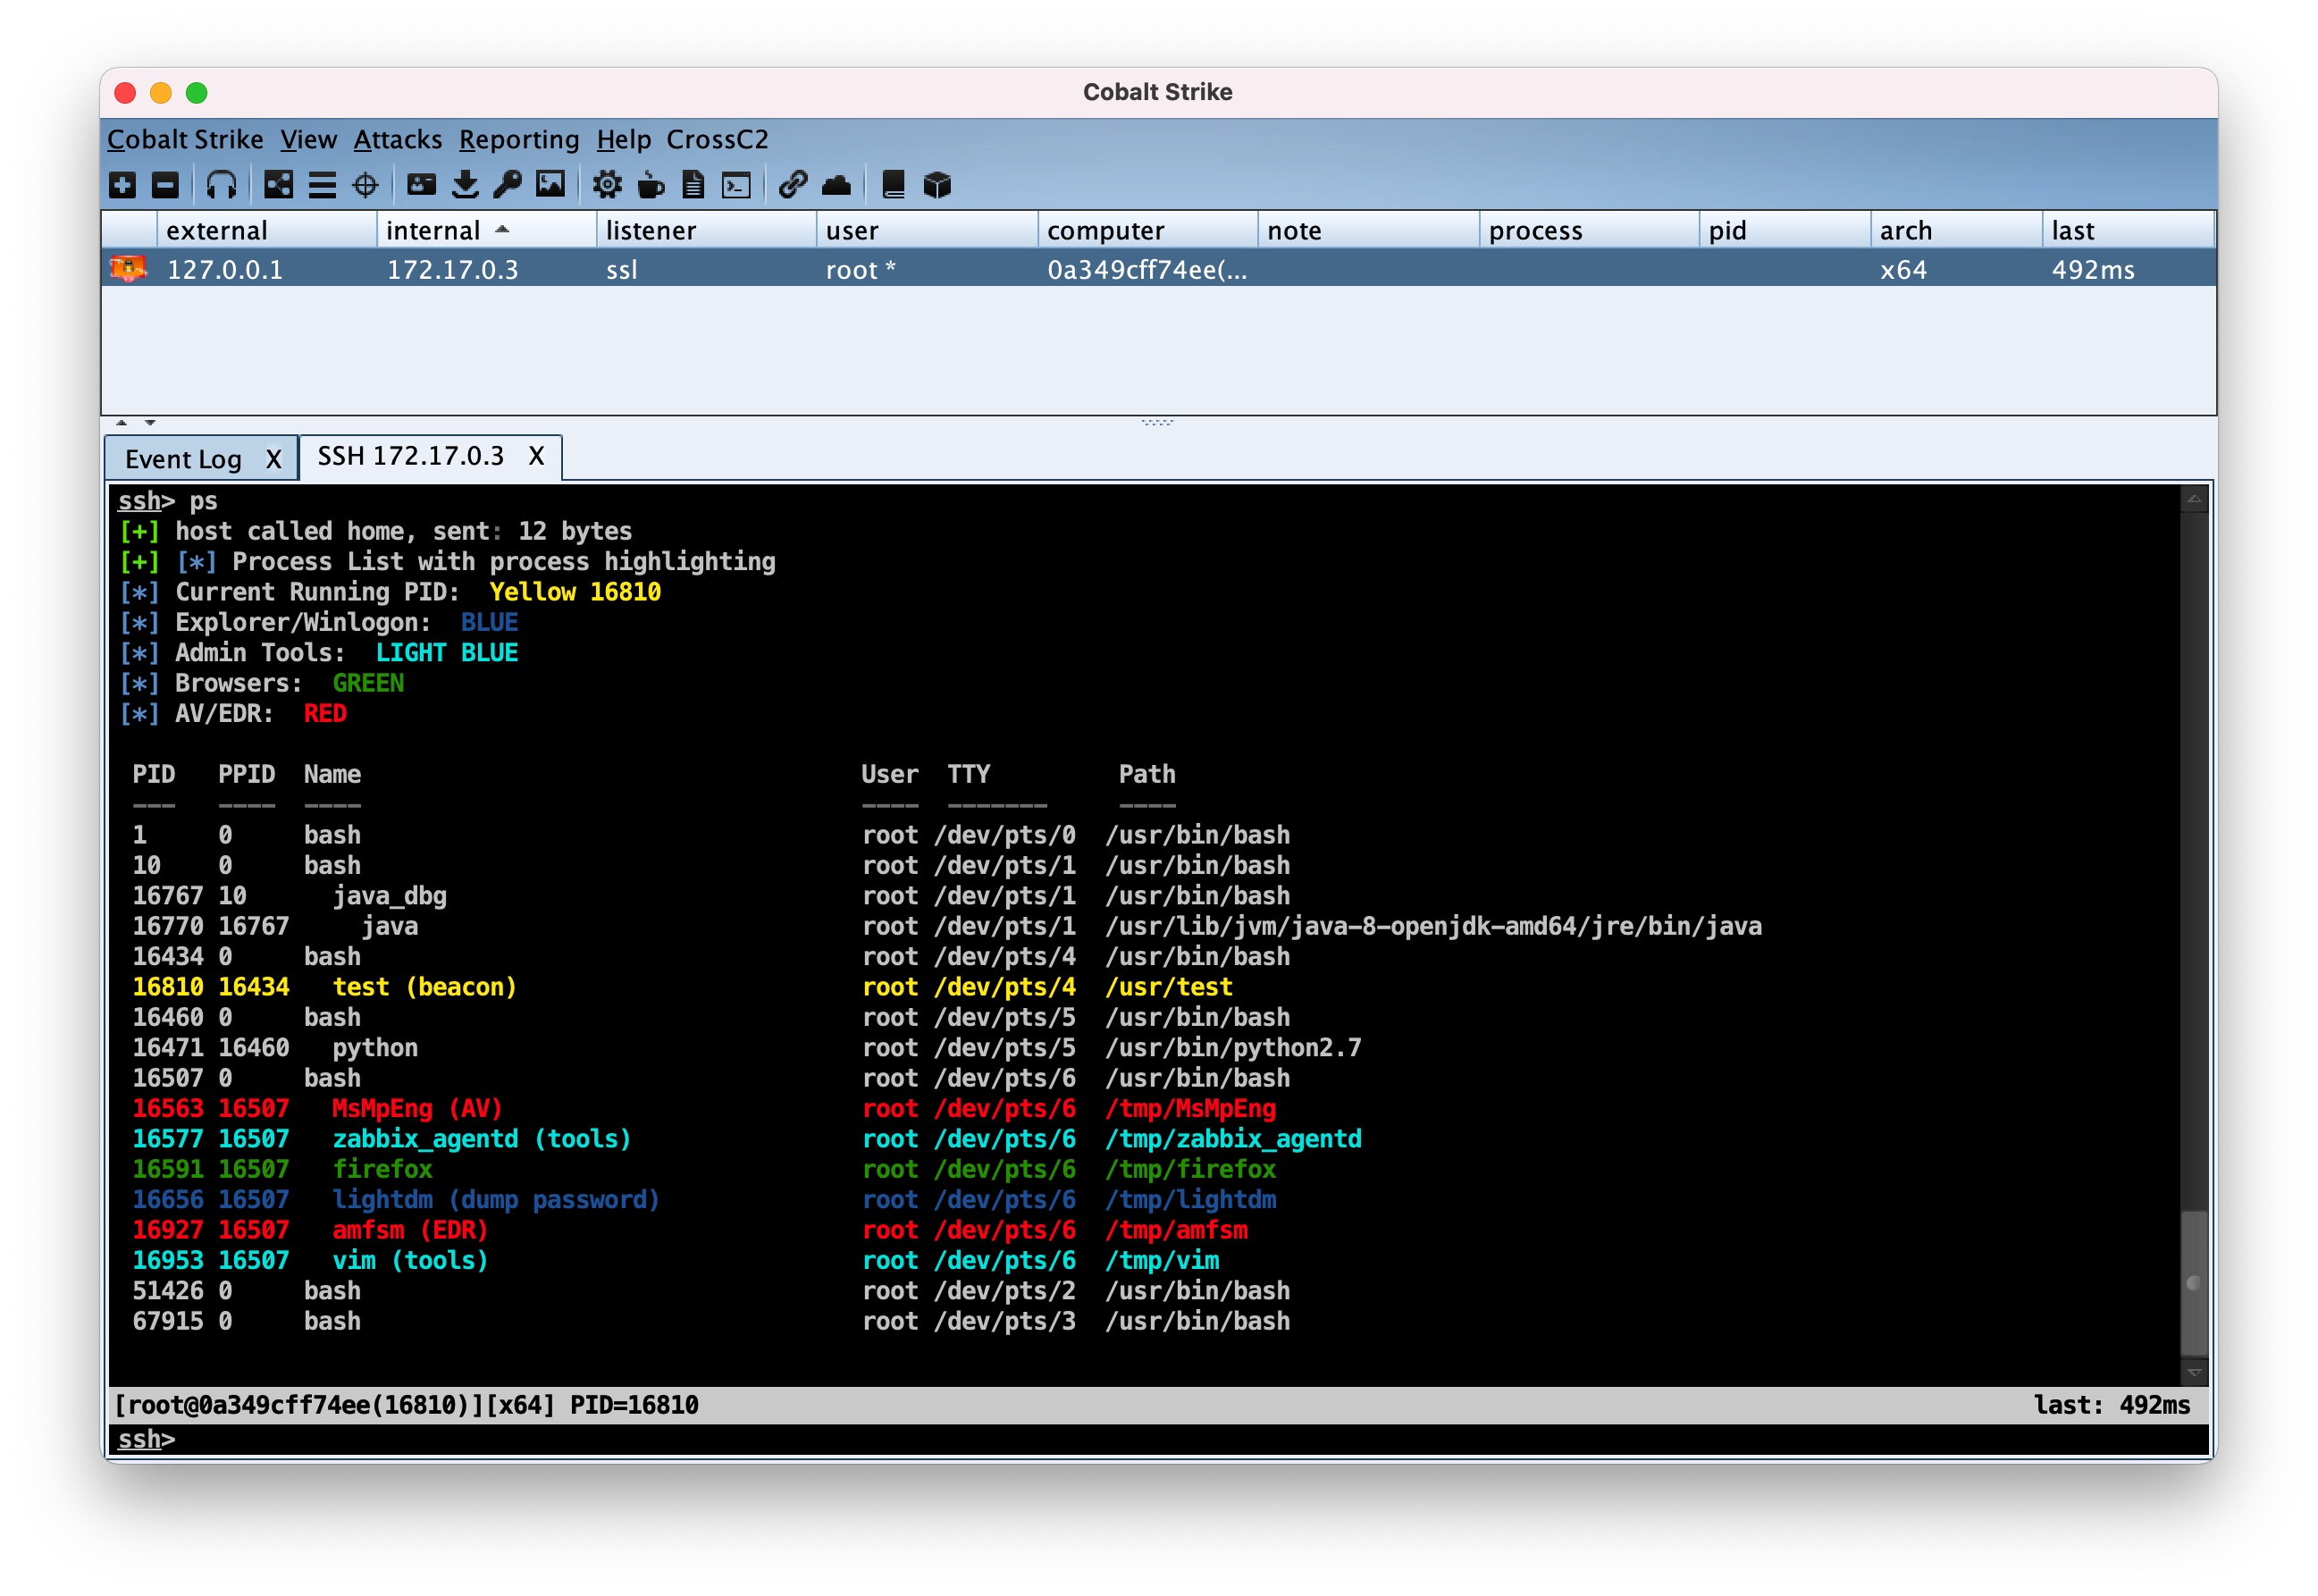 crossc2/crossc2kit
CrossC2 developed based on the Cobalt Strike framework can be used for other cross-platform system control. CrossC2Kit provides some interfaces for…
 enelg52/kittystager
KittyStager is a simple stage 0 C2. It is made of a web server to host the shellcode and an implant, called kitten. The purpose of this project is to…
 luemmelsec/apex
Azure Post Exploitation Framework
 nvisosecurity/pycobalthound
pyCobaltHound is an Aggressor script extension for Cobalt Strike which aims to provide a deep integration between Cobalt Strike and Bloodhound.