
CVE-2021-27877-PoC
 yashswarup12/cve-2021-27877-poc
A modified version of the Rapid7 Metasploit module for CVE-2021-27877 that supports direct command execution for reliable vulnerability validation.…
educationexploitationexploit-frameworks+3
yashswarup12/cve-2021-27877-pocA modified version of the Rapid7 Metasploit module for CVE-2021-27877 that supports direct command execution for reliable vulnerability validation.…
 361way/cve-2026-31431
Exploit for CVE-2026-31431 that escalates privileges to root, with a detection mode and C implementation for portability.
 ash1996x/cve-2025-50154-aggressor-script
Cobalt Strike Aggressor script that weaponizes LNK and Library-MS files to trigger SMB NTLMv2 hash disclosure, including CVE-2025-24054 bypass, for…
 kaleth4/cve-2026-31431
Exploit and detector for a Linux kernel local privilege escalation (CVE-2026-31431) that corrupts page cache to gain root, with mitigation guidance.
 b1gn0se/pwnkit_cve-2021-4034
Self-contained exploit for CVE-2021-4034 (PwnKit) that escalates privileges to root on vulnerable Linux systems via pkexec, with support for…
 vulncheck-oss/external-c2-experiments
Go external C2 module for go-exploit that catches reverse SSH shells, providing a server listener and payload client for integrating custom C2…
 fulucky0-yuri/cve-2026-31431-pocc
C implementation of a proof-of-concept for CVE-2026-31431, a Linux kernel AF_ALG page cache poisoning vulnerability that enables local privilege…
 edu0x01/hack-tools
Project that brings together several pentest tools
 0xn7y/cve-2026-31431
Logic bug in the kernel's authencesn cryptographic template that escalate privilege
 wongwaituck/cve-2021-4034
Proof-of-concept exploit for CVE-2021-4034 (PwnKit) that escalates privileges to root on vulnerable Linux systems.
 v-rzh/cve-2021-4034
Root exploit for CVE-2021-4034 (PwnKit) that abuses pkexec's out-of-bounds write to escalate privileges to root on Linux systems.
 joaoaugustom/wordpress_backup_migration-rce_unauthenticated
This exploit is based on CVE-2023-6553 and was built upon the original exploit by Chocapik, it was added that a direct reverse shell can be obtained.
 simoesctt/ctt-exchange-rce-v1.0---microsoft-exchange-exploit-cvss-10.0-critical-cve-2021-26855-cve-2021-27065
CTT-enhanced version of the Microsoft Exchange Server SSRF to RCE exploit (ProxyShell/ProxyLogon), another CVSS 10.0 critical vulnerability that…
 lglznl/klaios
KLAIOS is a hybrid security environment that merges Kali Linux’s offensive toolkit with hardened, VPN-bunker-style isolation—enhanced by modern AI…
 rakhithjk/cve-2021-4034-new
Exploit for CVE-2021-4034 (polkit pkexec) that provides a root shell. Includes build instructions and references the original advisory.
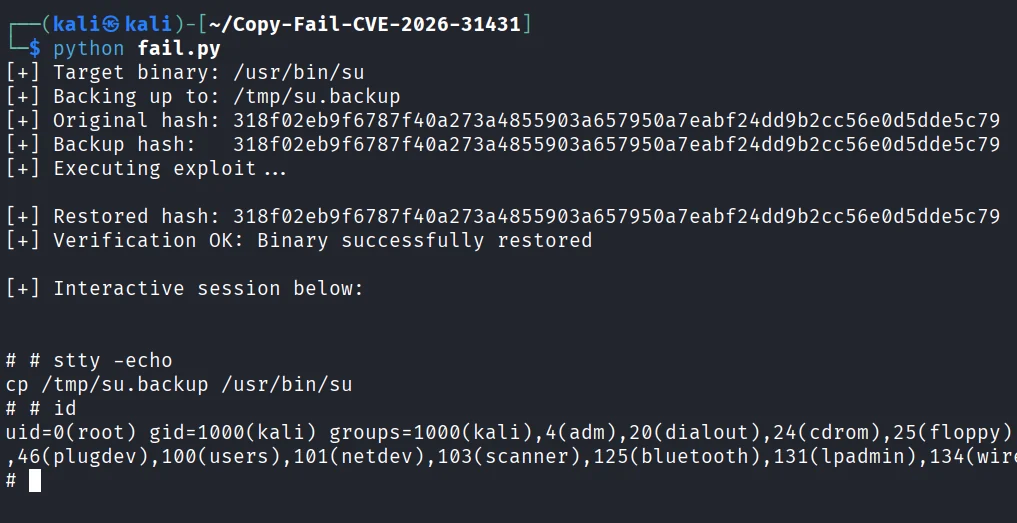 mohamedkarrab/copy-fail-cve-2026-31431
Proof-of-concept exploit for Linux kernel CVE-2026-31431 (Copy Fail) that abuses AF_ALG to corrupt setuid-root binaries in page cache, achieving…
 hectorgie/cve-2020-1472
Proof-of-concept exploit for CVE-2020-1472 (ZeroLogon) that changes the domain controller's machine account password, enabling DCSync and full domain…
 abdurahmon3236/-cve-2024-31211
Metasploit module that exploits a WordPress unserialization vulnerability (CVE-2024-31211) in WP_HTML_Token to achieve remote code execution.