
 poliva/root-zte-open
exploit for CVE-2012-4220 working on zte-open
 ma4the/omae-wa-cheese-da
CVE-2025-21479 PoC for ZFlip5 with Knox in the way!(˶˃ ᵕ ˂˶)
 xiaohj233/ghostlock-x200-app
vivo X200 设备端一键 root App(Shizuku 授权 shell 域执行,CVE-2026-43499)
 diabl0w/cve-2022-22057_sm-f926u
Qualcomm kgsl driver exploit (CVE-2022-22057) for Samsung Galaxy devices achieving arbitrary kernel memory read/write, SELinux bypass, and temporary…
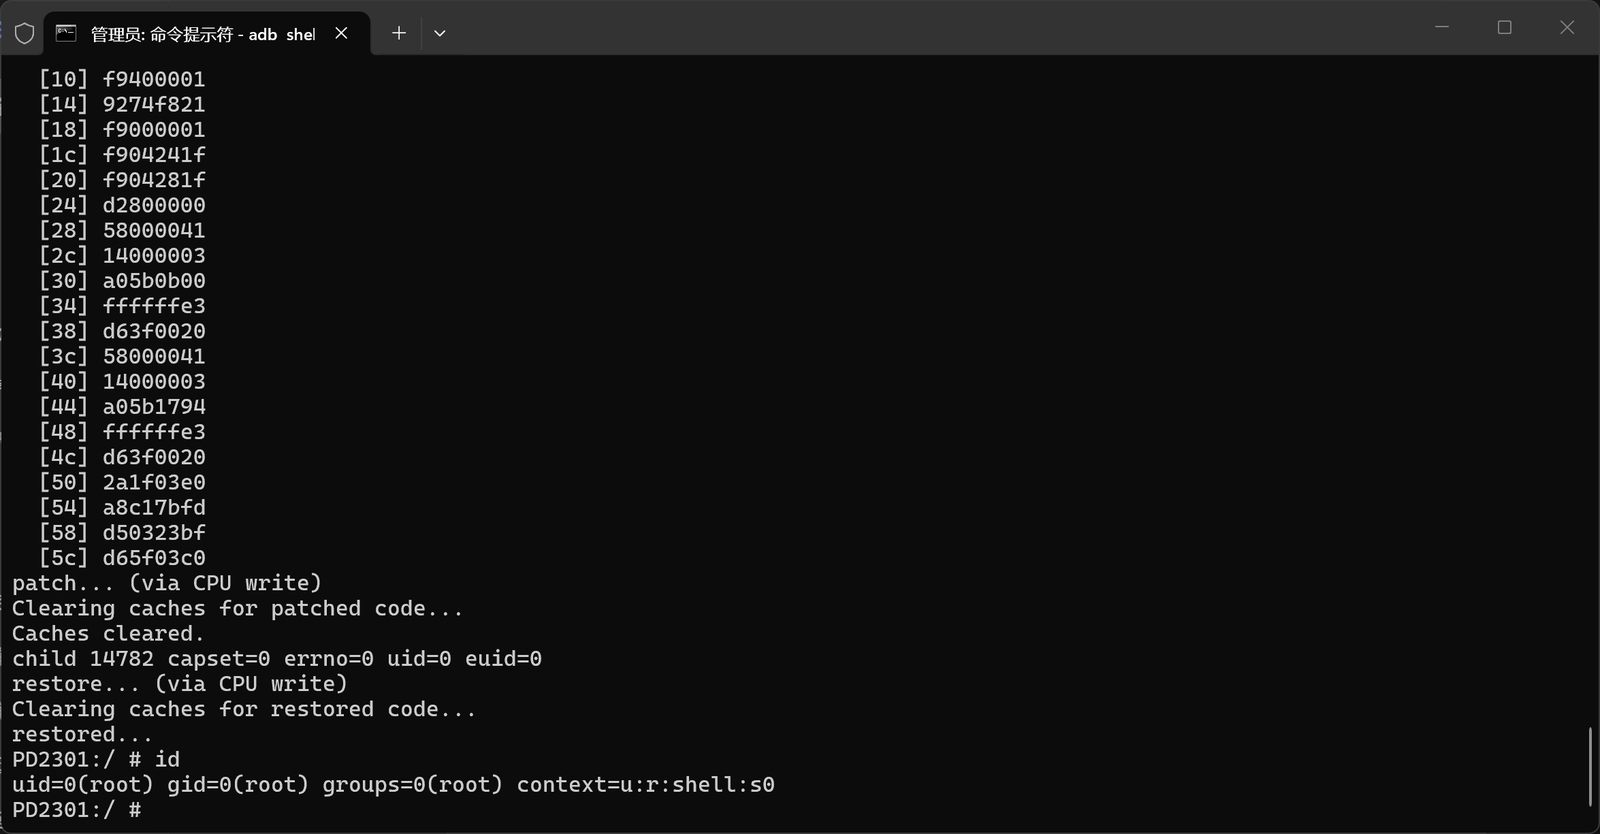 qingizi7/cve-2025-21479_iqooneo8
Local root exploit for CVE-2025-21479 (Adreno KGSL) on iQOO Neo8 (SM8475) - physical memory r/w, disables SELinux, spawns root shell
 become-illusory/cve-2026-64560-a16
CVE-2026-64560 toolkit: Go single-binary toolchain + realme RMX5010 (A16, SM8750) target port
 llccd/temproot-huawei
CVE-2019-2215 poc for Huawei hardened kernel
 ireshchaminda1/android-privilege-escalation-remote-access-vulnerability-cve-2015-1805
AndroRAT is a capability that can be used to inject a root exploit as a silent installation to perform a malicious task on the device. This AndroRAT…
 newazbenalam/root-my-galaxy-payloads
Device-specific CVE-2026-43499 root payloads and KernelSU artifacts for Samsung Galaxy models, with firmware profiles, exploit source, and a support…
 begitdj/cve-2019-2215-markw
Exploit for CVE-2019-2215 to gain temporary root on Xiaomi MIUI devices, enabling bootloader unlock and system modifications.
 dorlow/hazel-cve-2026-43499
Firmware-specific temporary root exploit for Toshiba/Amazon Fire TV (hazel) using CVE-2026-43499. Implements ARM32 futex-PI UAF, kernel address leak,…
 abdgalaxy36-code/rmgp-complete-handoff
Complete RMGP (CVE-2026-43499) workspace + experiment-state handoff for SM-A376B/A376BXXU1AZB7
 everyoneexe/root-s24-e1s
Galaxy S24 SM-S921B S921BXXSDCZB2 RAM-only KernelSU Next + Root S24 app
 cxyofficial/k50g-pocof4gt-cve-2026-43499-poc
Local privilege escalation exploit for Redmi K50G/POCO F4 GT using CVE-2026-43499 (futex UAF) to gain temporary root and load KernelSU without…
 sgswzglwlx/vivo-root-build
Builds a root exploit for vivo/iQOO devices targeting CVE-2026-43499, leveraging kernel techniques like KASLR bypass and CFI manipulation to achieve…
 last-emo-boy/rikune
MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…
 aflplusplus/libafl
Advanced Fuzzing Library - Slot your Fuzzer together in Rust! Scales across cores and machines. For Windows, Android, MacOS, Linux, no_std, ...