

Archived
RedWarden
 mgeeky/redwarden
Cobalt Strike C2 Reverse proxy that fends off Blue Teams, AVs, EDRs, scanners through packet inspection and malleable profile correlation
command-and-controlexploit-frameworksids-ips-evasion+8
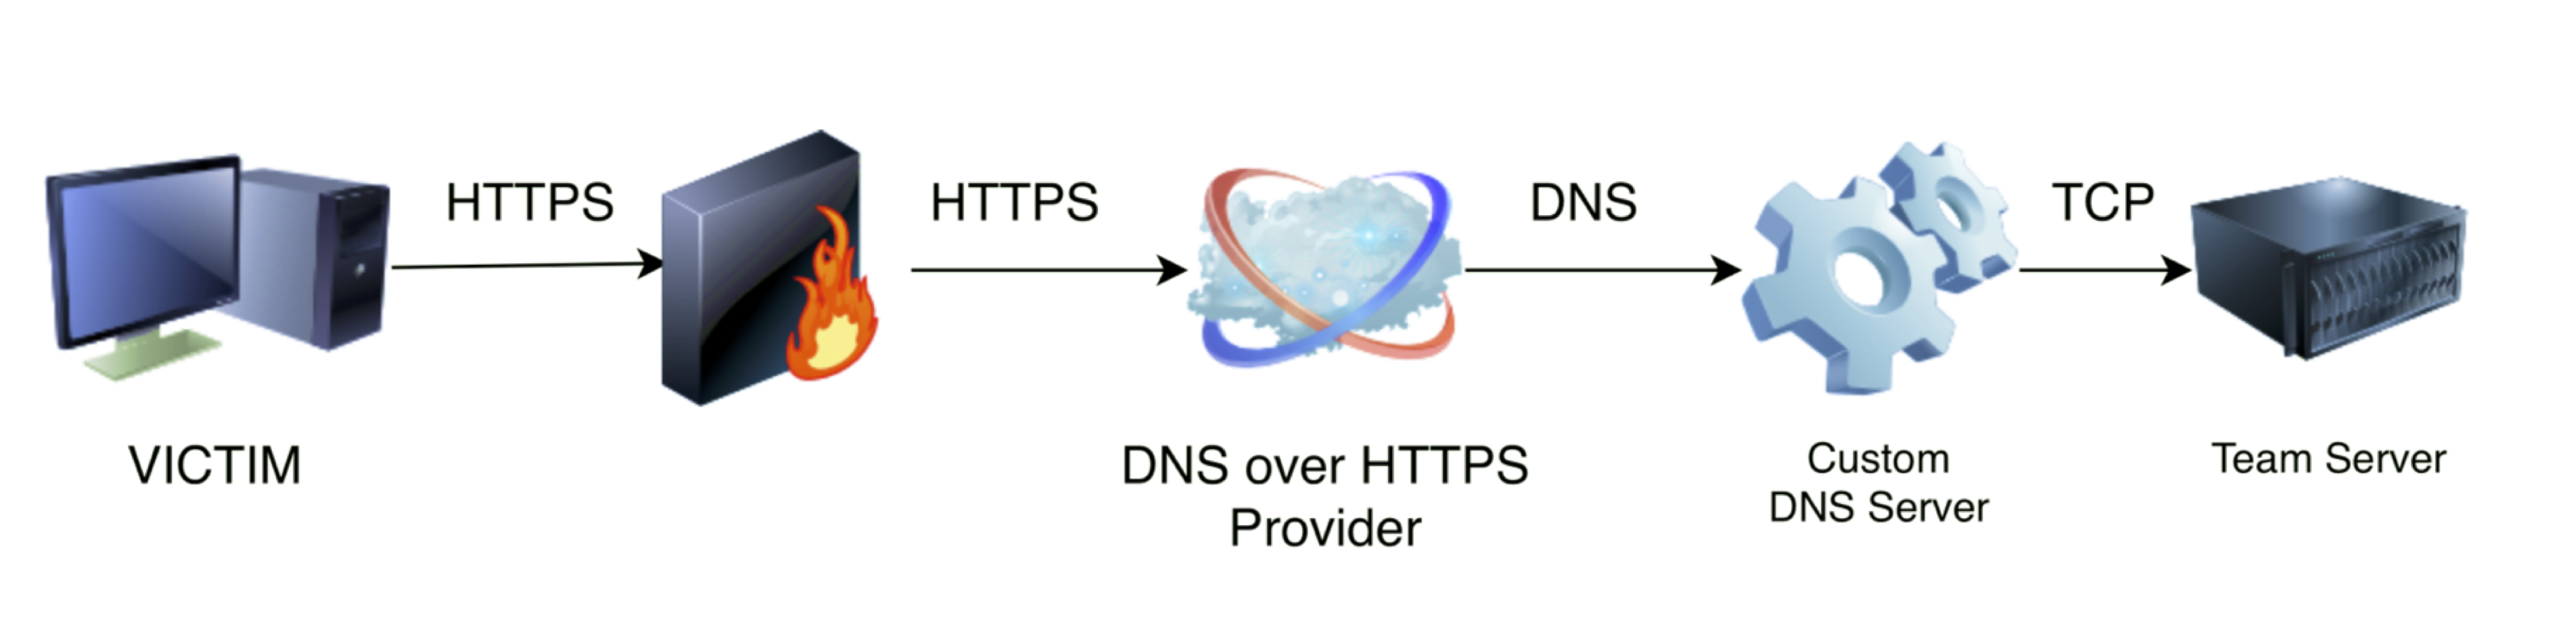 spiderlabs/dohc2
DoHC2 allows the ExternalC2 library from Ryan Hanson (https://github.com/ryhanson/ExternalC2) to be leveraged for command and control (C2) via DNS…
 vulncheck-oss/external-c2-experiments
Go external C2 module for go-exploit that catches reverse SSH shells, providing a server listener and payload client for integrating custom C2…
 wavestone-cdt/abaddon
Red team operations management platform automating infrastructure deployment, C2 setup, phishing campaigns, and reconnaissance with integrated tool…
 bats3c/shad0w
A post exploitation framework designed to operate covertly on heavily monitored environments
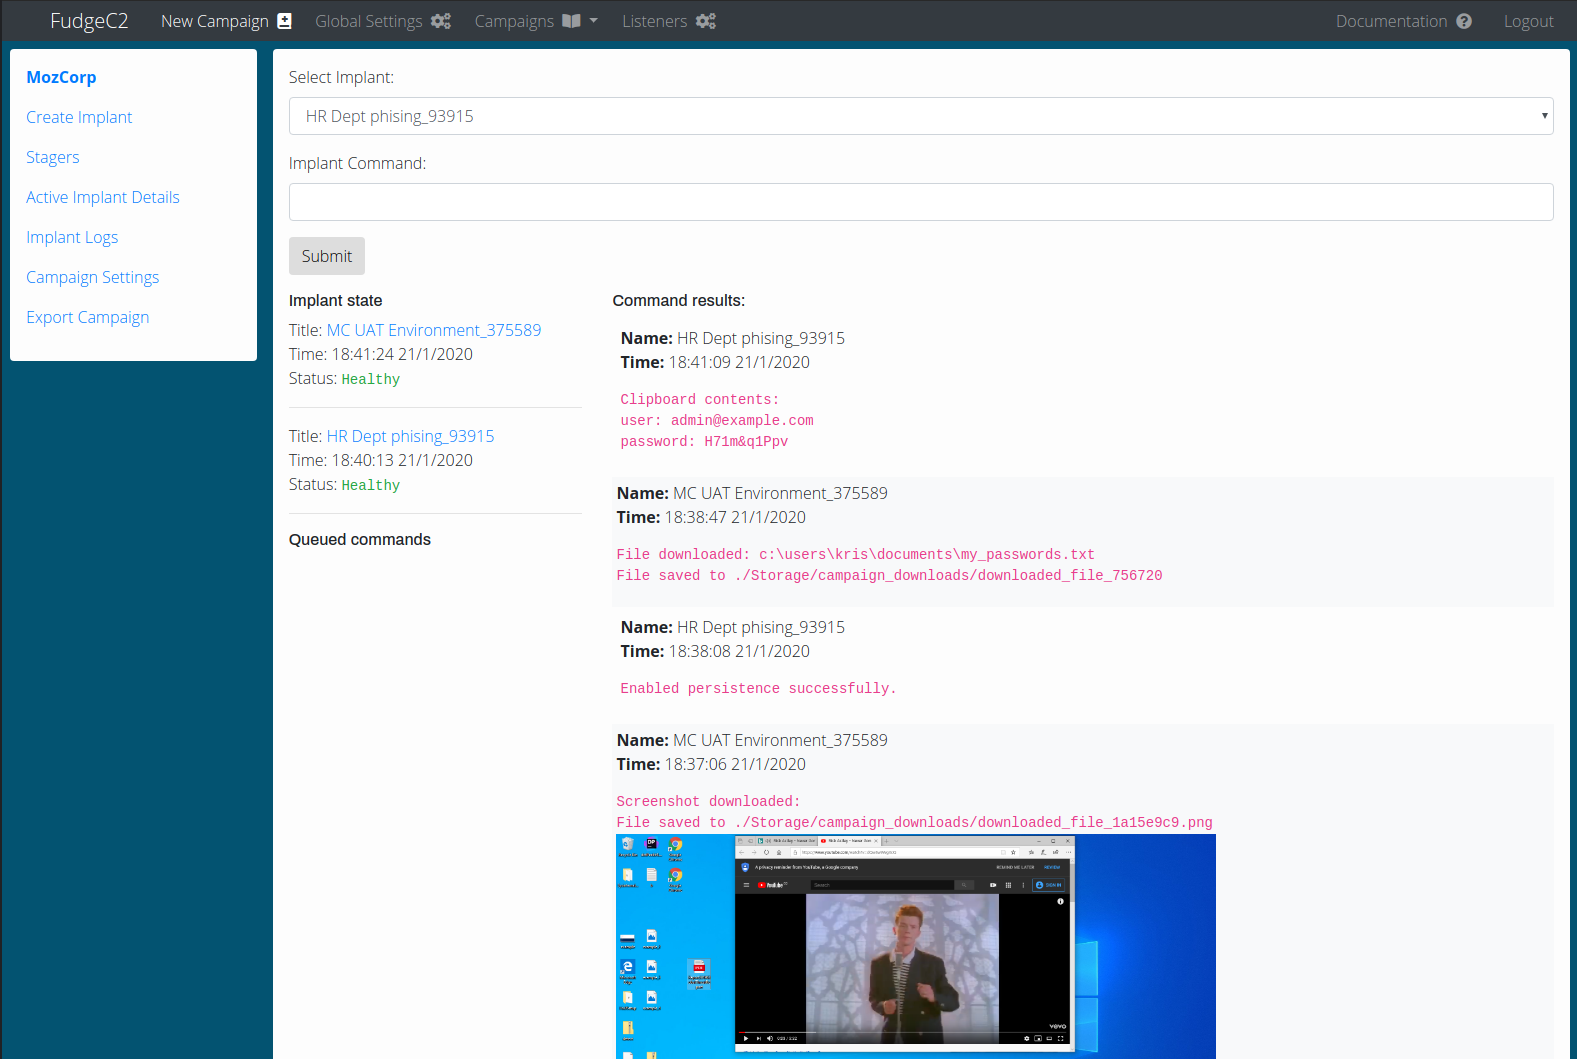 ziconius/fudgec2
FudgeC2 - a command and control framework designed for team collaboration and post-exploitation activities.
 project-prismatica/prismatica
Responsive Command and Control System
 professionallyevil/c4
Cyberdelia, a Collection of Command and Control frameworks
 phoenixc2/phoenixc2
Command & Control-Framework created for collaboration in python3
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 dragoqcc/cruciblec2
A C# Command & Control framework
 1135/1135-cobaltstrike-toolkit
about CobaltStrike
 licitrasimone/crystalsliver
Crystal Palace Evasion kit for Sliver
 outflanknl/wdtoggle
A Beacon Object File (BOF) for Cobalt Strike which uses direct system calls to enable WDigest credential caching.
 bishopfox/sliver
Adversary Emulation Framework
 ne0nd0g/merlin
Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
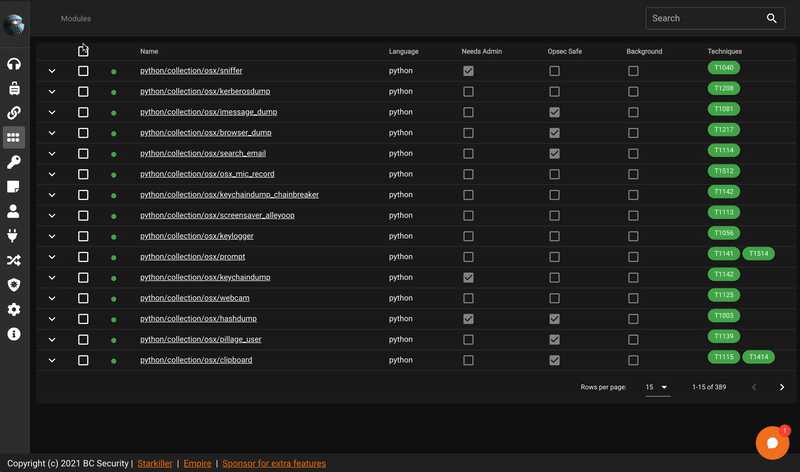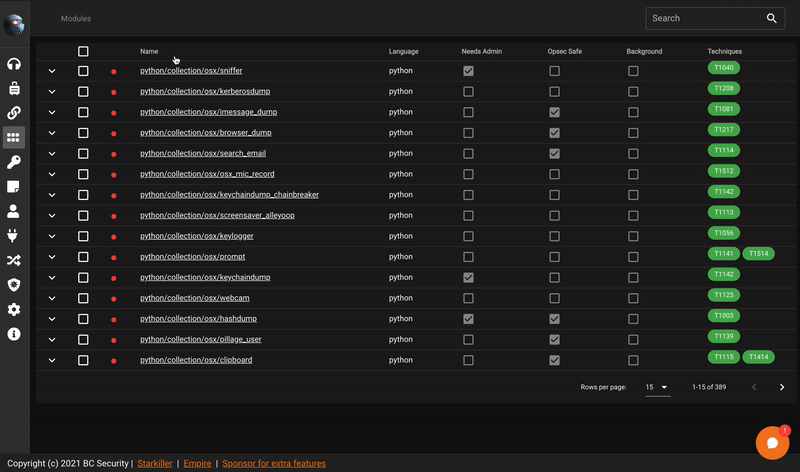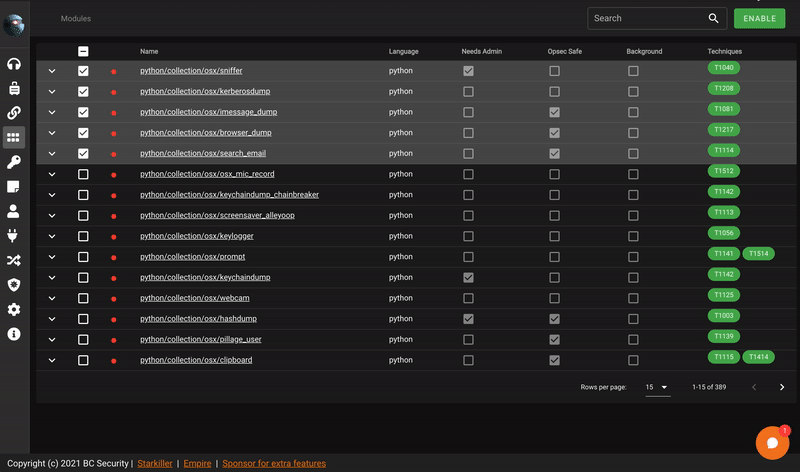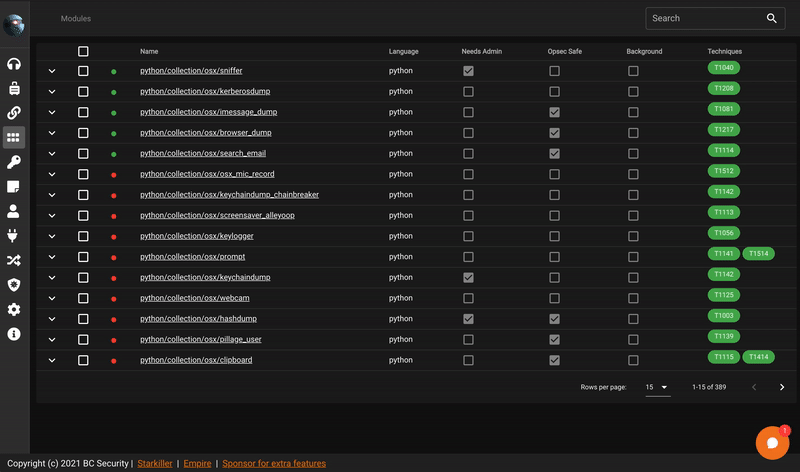 bc-security/starkiller
Starkiller is a Frontend for PowerShell Empire.