
exchange_proxylogon
 mekhalleh/exchange_proxylogon
Module pack for #ProxyLogon (part. of my contribute for Metasploit-Framework) [CVE-2021-26855 && CVE-2021-27065]
exploit-frameworkspayload-developmentpenetration-testing-frameworks+2
mekhalleh/exchange_proxylogonModule pack for #ProxyLogon (part. of my contribute for Metasploit-Framework) [CVE-2021-26855 && CVE-2021-27065]
 tiagob0b/cve-2021-22005
Metasploit module for CVE-2021-22005 VMware vCenter arbitrary file upload vulnerability with proof-of-concept and remote code execution exploit.
 j4ck3lsyn-gen2/cve-2026-58457
PoC tools for CVE-2026-58457: Unauthenticated OS Command Injection leading to remote root on Shenzhen Aitemi M300 Wi-Fi Repeater (MT02). Includes…
 abdurahmon3236/cve-2024-38472
Metasploit module that exploits Apache HTTP Server SSRF (CVE-2024-38472) on Windows to reach internal services and achieve remote code execution.
 0x00-0x00/cve-2015-3224
Modification of Metasploit module for RCE in Ruby-On-Rails Console CVE-2015-3224
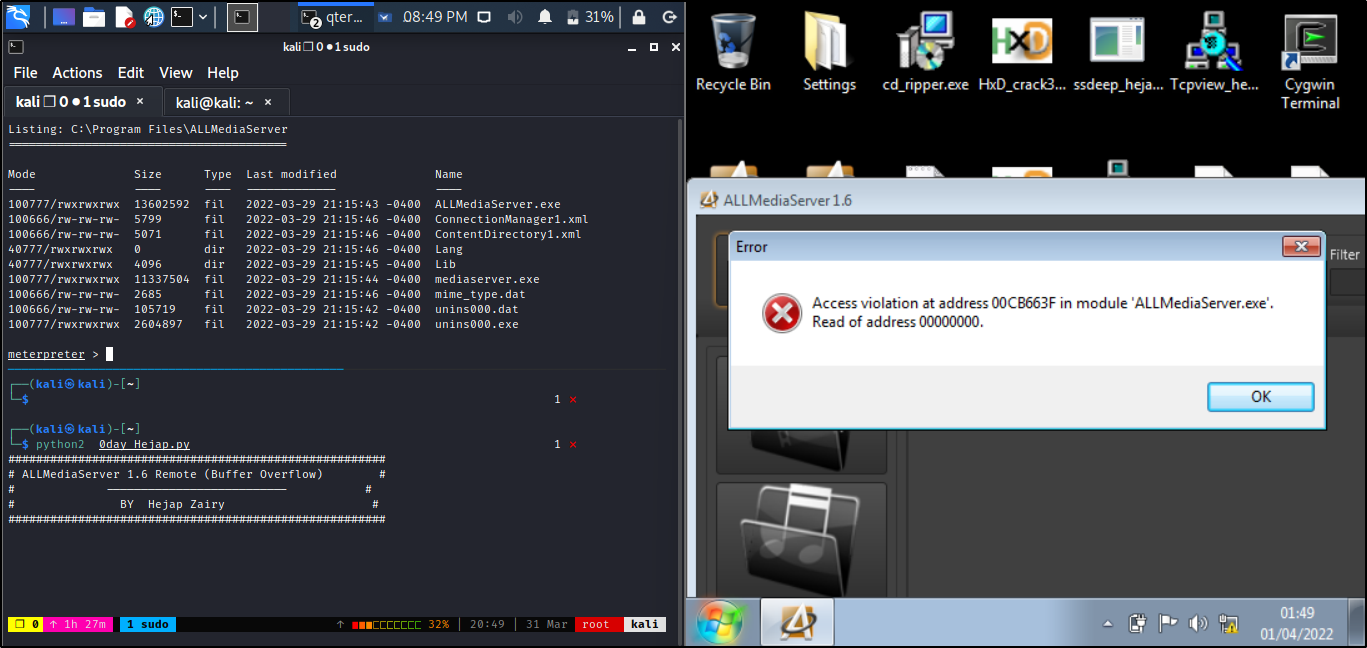 matrix07ksa/allmediaserver-1.6-buffer-overflow
Remote buffer overflow exploit with SEH overwrite for ALLMediaServer 1.6, provided as a Metasploit module targeting CVE-2022-28381.
 b0fh/cve-2018-4878
Metasploit module for CVE-2018-4878
 soham23/firefox-rce-nssmil
Educational standalone JavaScript implementation of the public exploit for CVE-2016-9079 (Firefox Use-After-Free), adapted from the original…
 divinepwner/terramaster-tos-cve-2020-15568
Repository for CVE-2020-15568 Metasploit module
 xfox64x/cve-2016-5640
Crestron AirMedia AM-100 RCE (CVE-2016-5640) Metasploit Module
 adityasingh108/cve-2026-31431-metasploit-exploit
Automated Metasploit post-exploitation module for CVE-2026-31431 ("Copy Fail"). Weaponizes a deterministic logic flaw in the Linux kernel AF_ALG…
 ide0x90/cve-2016-1555
Metasploit module exploiting unauthenticated command injection in multiple Netgear router models to achieve remote code execution with root…
 dsfau/wordpress-cve-2018-6389
Metasploit module for WordPress DOS load-scripts.php CVE-2018-638
 julixsalas/cve-2020-0796
Metasploit Auxiliary module for scanning and detecting CVE-2020-0796 (SMBGhost) vulnerability in Windows SMBv3 implementations.
 bootstrapbool/msf-cve-2024-46987
Metasploit module to exploit CVE-2024-46987 - an authenticated path traversal vulnerability in Camaleon CMS versions 2.8.0 through 2.8.2 and 2.9.0
 starxsky/cve-2026-31431
Provides attack source code and sniffing tools for CVE-2026-31431, a kernel vulnerability, along with mitigation instructions including disabling the…
 fsn4k3/dahua-dvr-metasploit
Improved Metasploit module for CVE-2013-6117 (Dahua DVR authentication bypass)
 mrowkoob/cve-2023-33538-msf
CVE-2023-33538 - TP-Link Command Injection Ruby module for Metasploit Framework