Malleable-C2-Randomizer

A script to randomize Cobalt Strike Malleable C2 profiles and reduce the chances of flagging signature-based detection controls

A script to randomize Cobalt Strike Malleable C2 profiles and reduce the chances of flagging signature-based detection controls

Tentacle is a POC vulnerability verification and exploit framework. It supports free extension of exploits and uses POC scripts. It supports calls to…

A collection of exploits for different VoIP products.

Red Team engagement platform with the goal of unifying offensive tools behind a simple UI

A unified console to perform the "kill chain" stages of attacks.

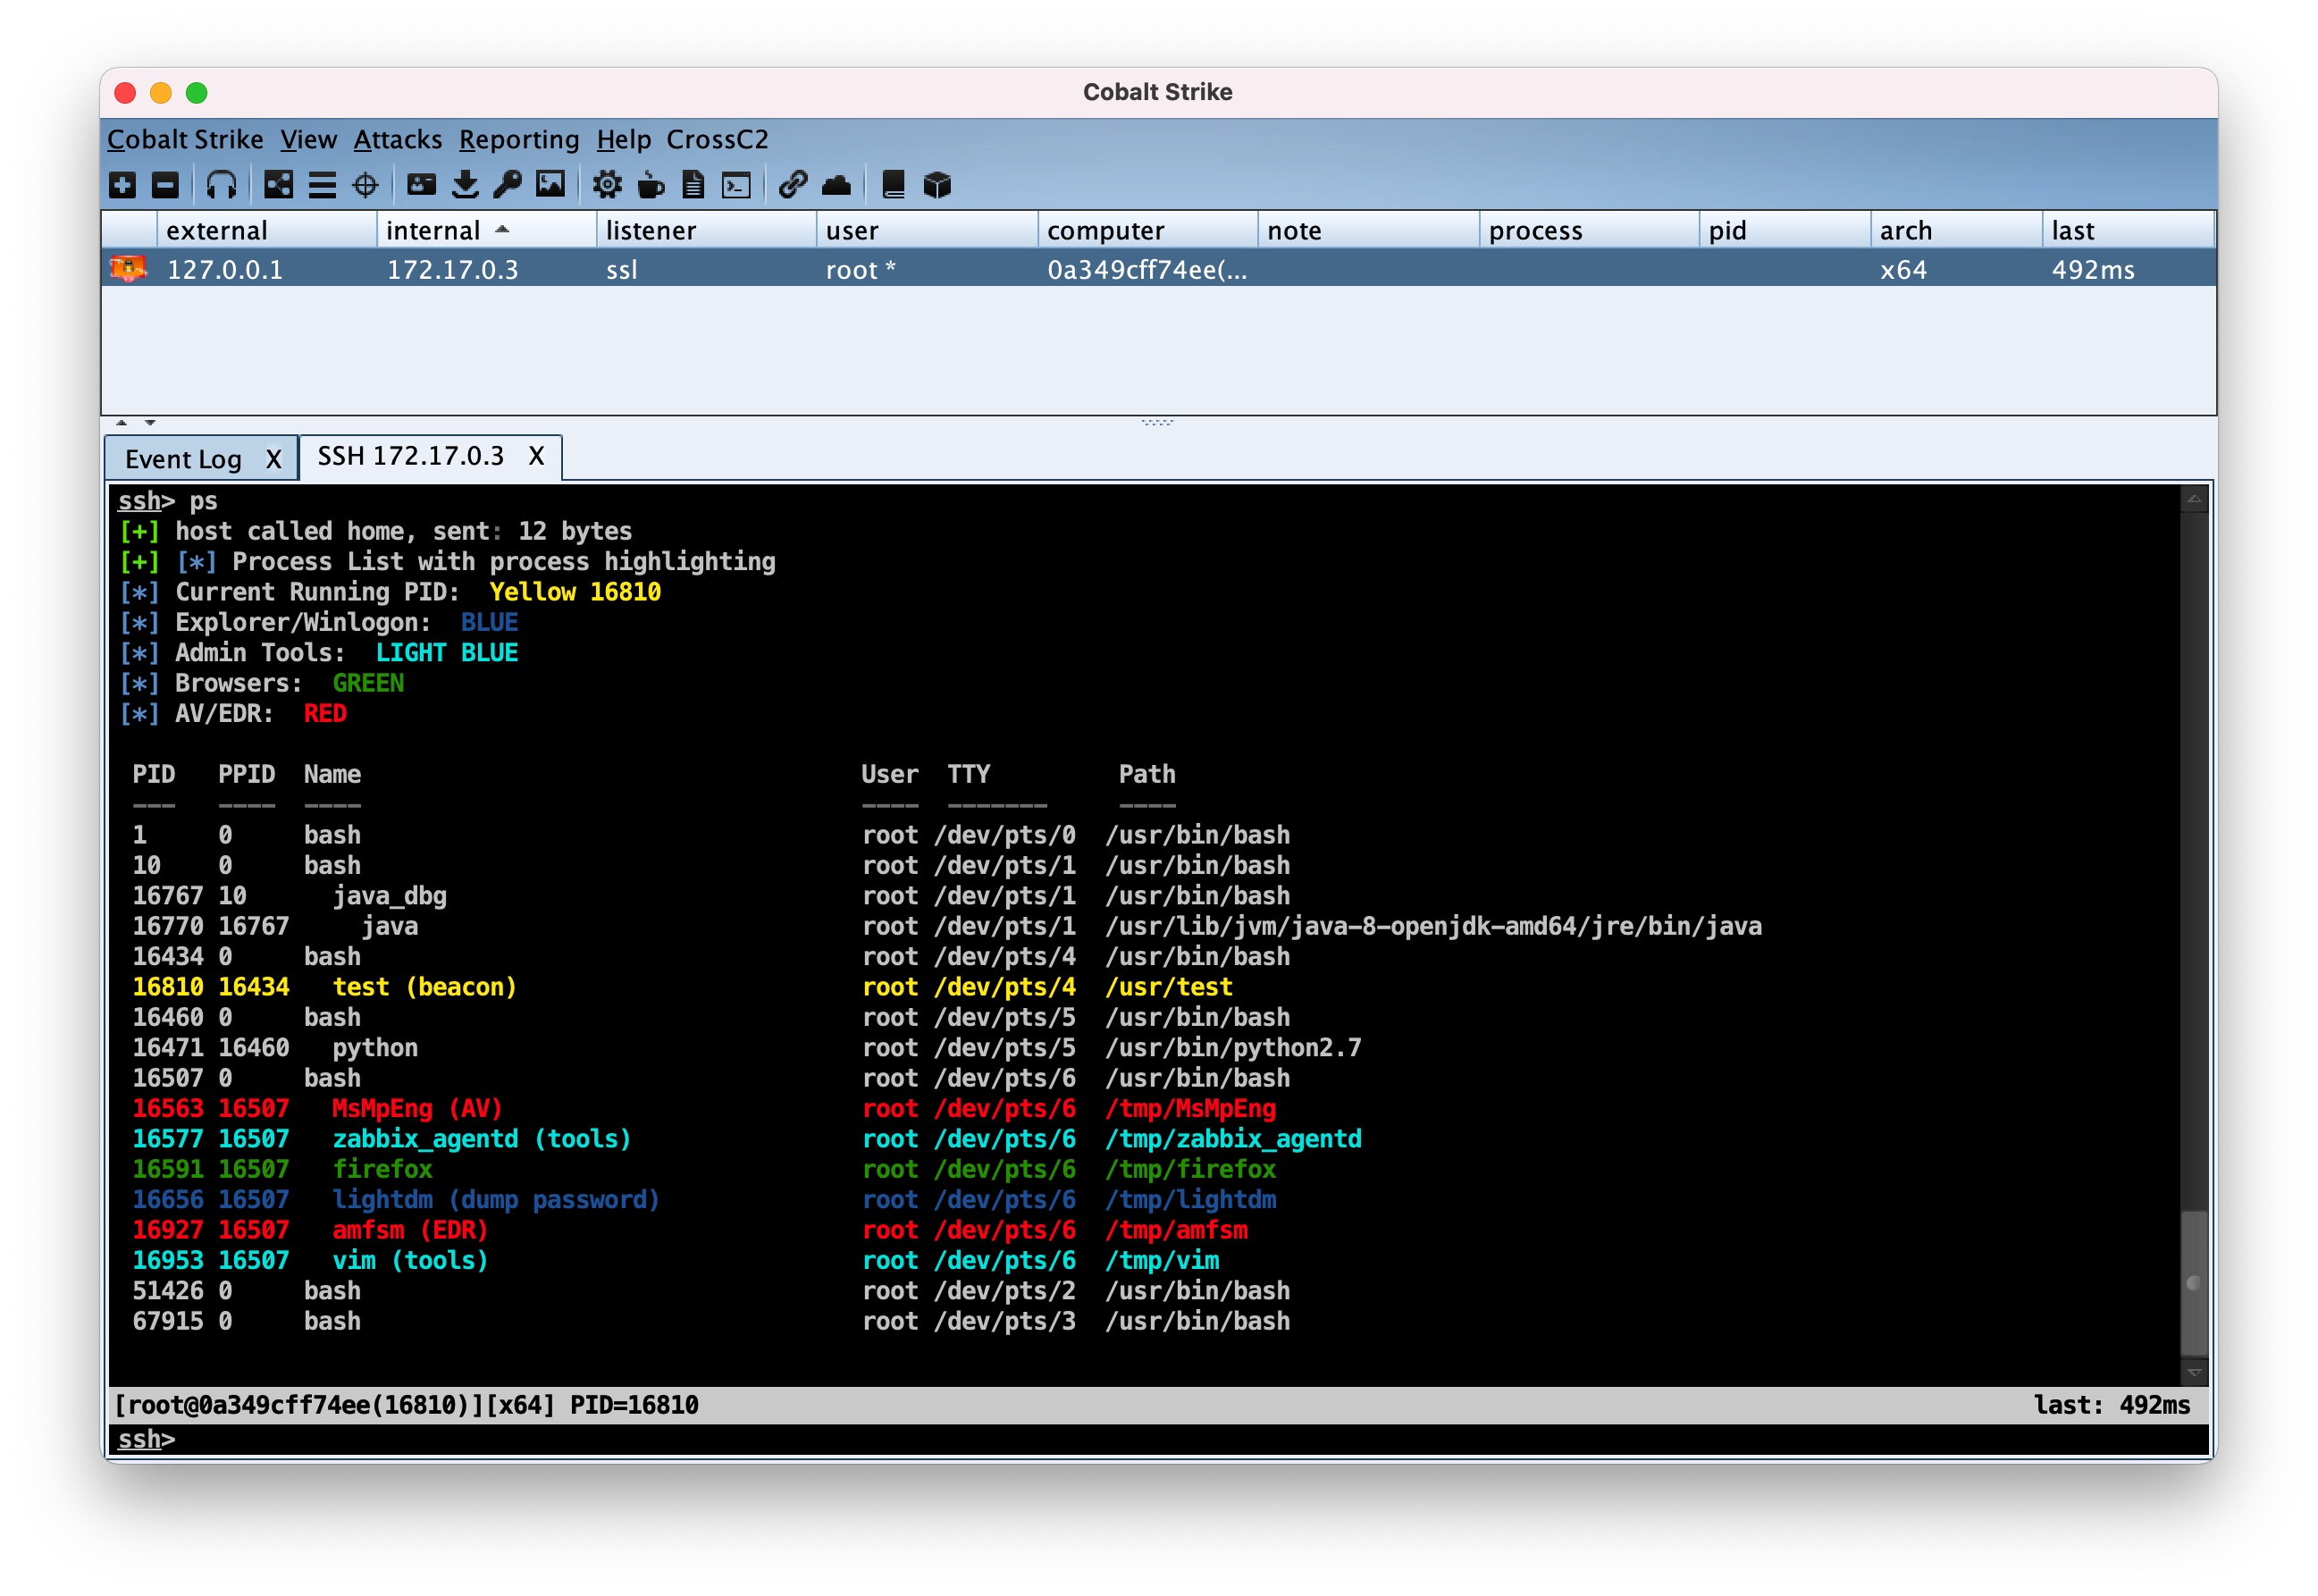
CrossC2 developed based on the Cobalt Strike framework can be used for other cross-platform system control. CrossC2Kit provides some interfaces for…

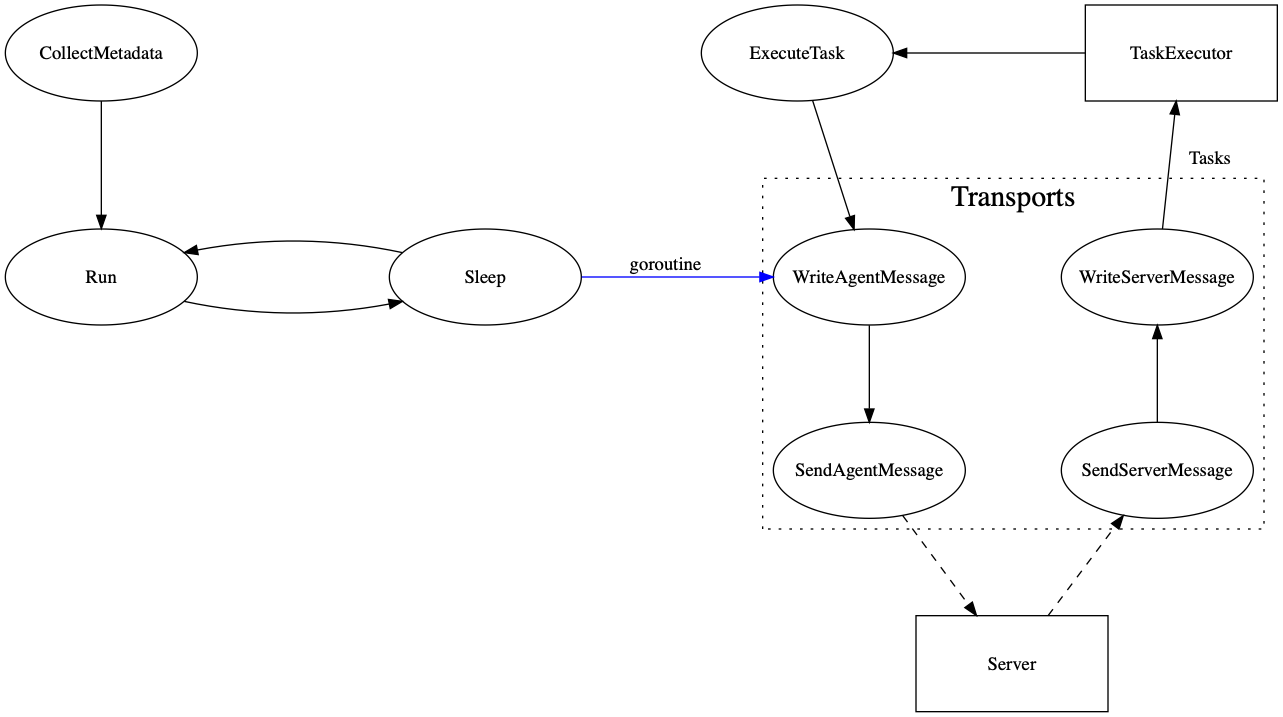
KittyStager is a simple stage 0 C2. It is made of a web server to host the shellcode and an implant, called kitten. The purpose of this project is to…

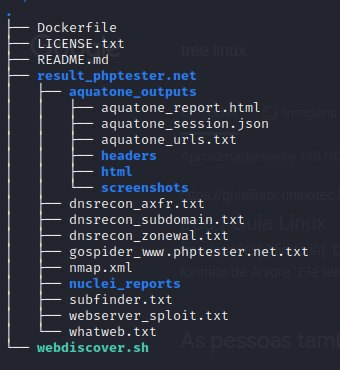
The purpose of this script is to automate the web enumeration process and search for exploits

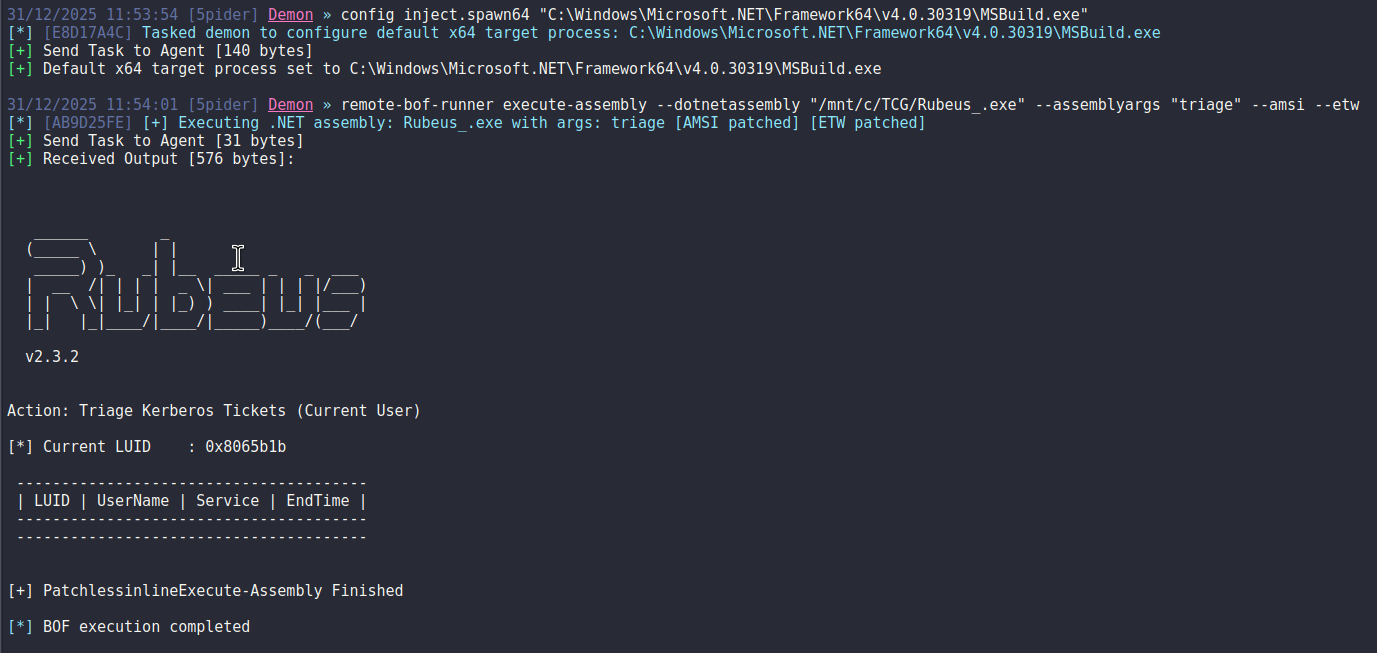
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.

Modular Python3 attack framework for automating exploitation of SIEM platforms (Splunk, Graylog, OSSIM, QRadar, McAfee) via credential theft, payload…

Proof of Concept for EFSRPC Arbitrary File Upload (CVE-2021-43893)

PAKURI-THON is a tool that supports pentesters with various pentesting tools and C4 server (command & control and chat & communication server).…

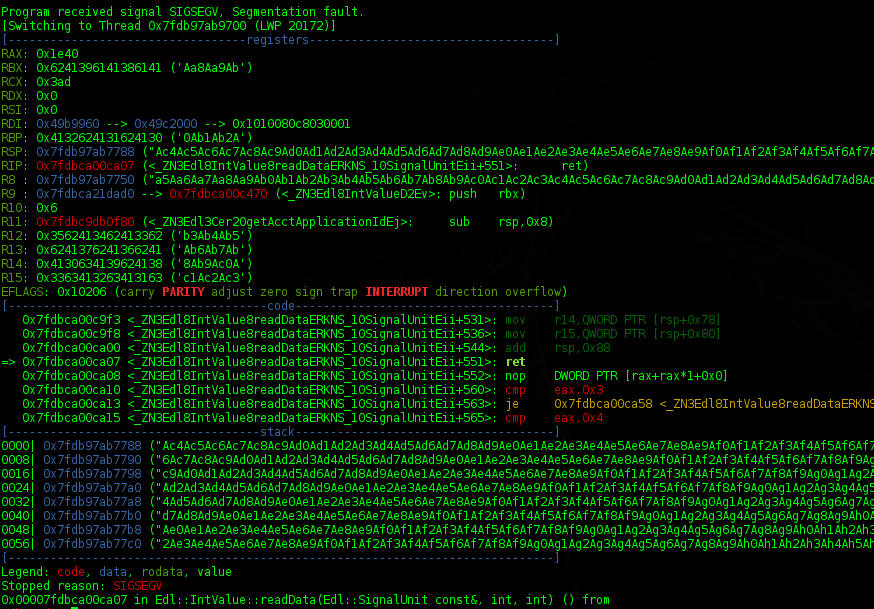
Writeup of the Oracle DSR stack buffer overflow vulnerability (DRA) CVE-2014-6598

ISAF aims to be a framework that provides the necessary tools for the correct security audit of industrial (OT) environments.

Educational penetration testing lab report documenting exploitation of vsftpd 2.3.4 backdoor (CVE-2011-2523) on Metasploitable 2 using Metasploit,…

The FortiGate SSL-VPN pot of gold. CVE-2024-21762 and CVE-2023-27997. 79 working exploit clients. 53 hardware SKUs. 55 FortiOS builds.

A remote Denial of Service (DoS) exploit for PX4 Autopilot versions ≤1.17.0-rc2 via a stack‑based buffer overflow in the MavlinkLogHandler.

Penetration testing assessment of a vulnerable IIS 6.0 WebDAV server, demonstrating reconnaissance, enumeration, exploitation (CVE-2017-7269), and…