
CVE-2021-4034
 ayrx/cve-2021-4034
Exploit for CVE-2021-4034 (PwnKit) that leverages a race condition in pkexec to escalate privileges to root on Linux systems.
binary-exploitationexploitationexploit-frameworks+2
ayrx/cve-2021-4034Exploit for CVE-2021-4034 (PwnKit) that leverages a race condition in pkexec to escalate privileges to root on Linux systems.
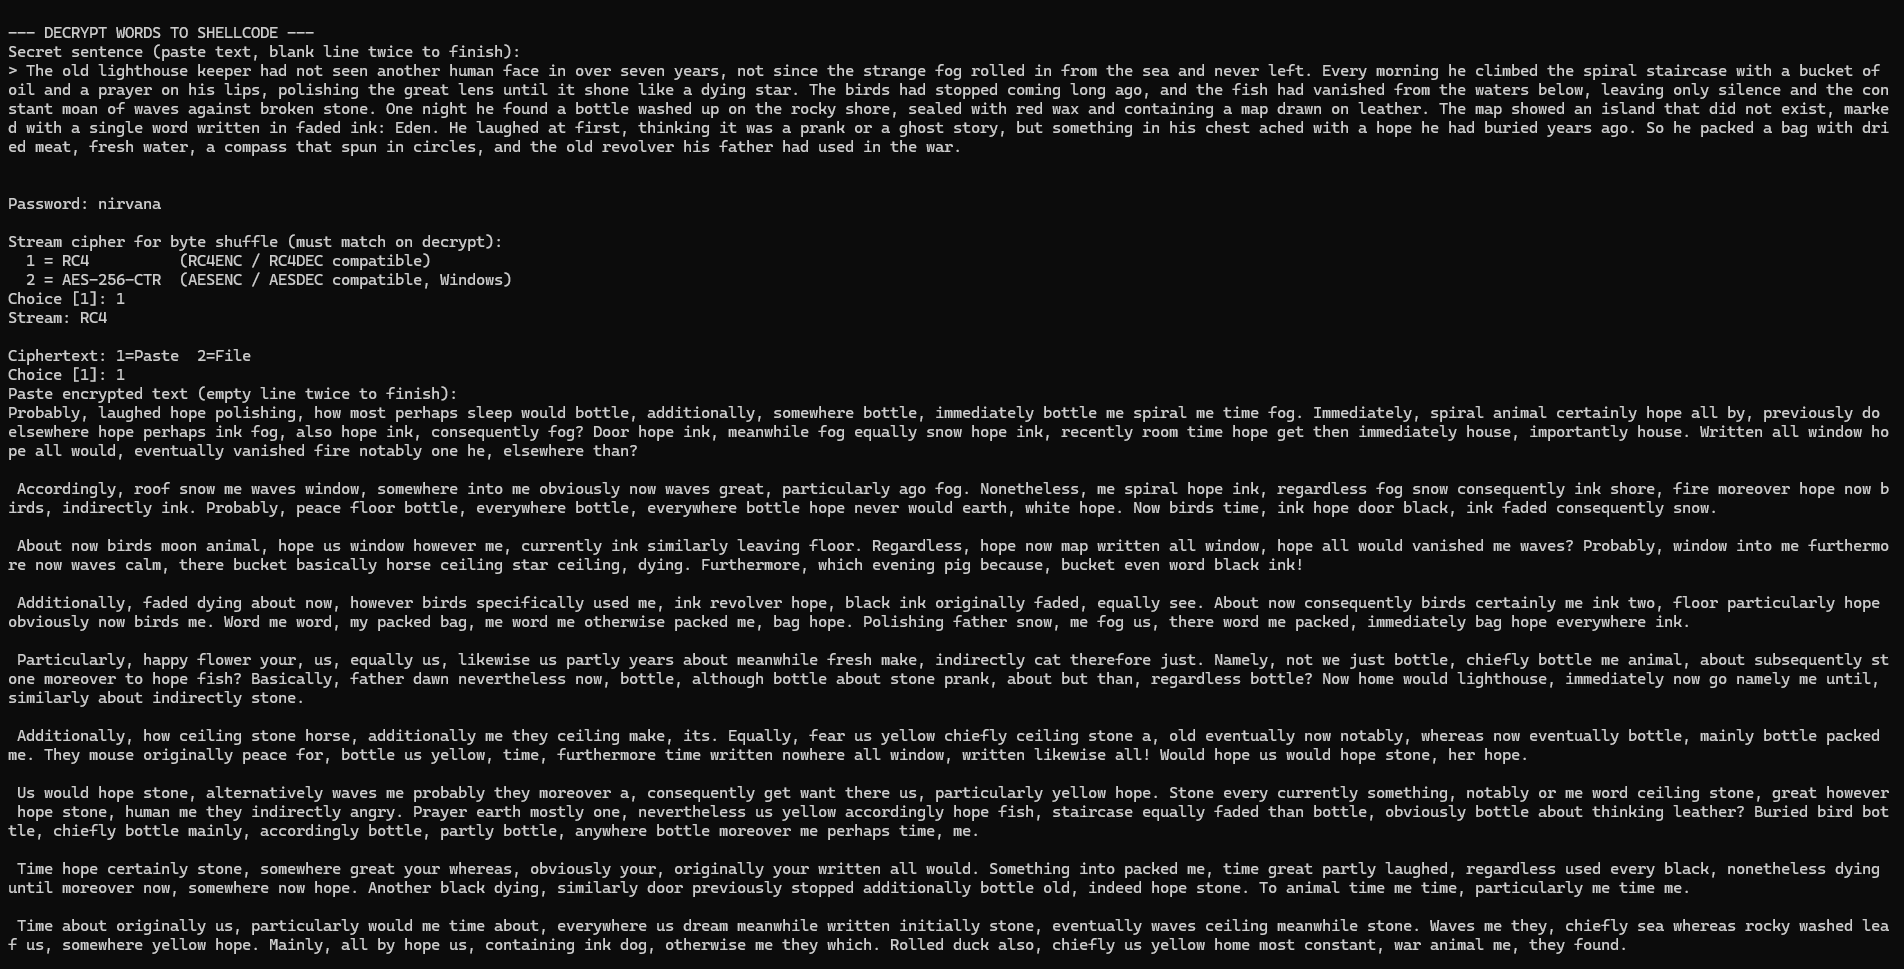 nirvanaon/now
NØW is a word-based shellcode encoding and obfuscation tool that transforms raw shellcode bytes into natural-looking English prose.
 calfcrusher/maccaronic2
A proof-of-concept Command & Control framework that utilizes the powerful AsyncSSH Python library which provides an asynchronous client and server…
 michalbednarski/thisseemswrong
Writeup and exploit for CVE-2024-49746: Android's Parcel::continueWrite closing File Descriptors that are later used
 lorentzenman/payday
Payload generator that uses Metasploit and Veil. Takes IP address as input and calls Veil. Use msfvenom to create payloads and writes resource…
 kuwaitist/astral_projection
Cobalt Strike UDRL that performs advanced module stomping using VEH to intercept calls, unmap modules during sleep, and remap fresh modules to evade…
 xtiankisutsa/twiga
A tool that enumerates Android devices for information useful in understanding its internals and for exploit development. It supports android 4.2 to…
 estamelgg/cve-2021-4034-nogcc
Standalone exploit for CVE-2021-4034 (polkit pkexec) that runs without gcc or cmake, providing interactive shell or one-liner command execution on…
 blacksnufkin/cheshire
Adaptix C2 service plugin that drives LitterBox payload analysis from the operator UI.
 kyle41111/ai-file
A listener profile for the Mythic C2 framework that utilizes AI vendors file API's
 danaepp/pwncat_pwnkit
pwncat module that automatically exploits CVE-2021-4034 (pwnkit)
 01rabbit/pakuri-thon
PAKURI-THON is a tool that supports pentesters with various pentesting tools and C4 server (command & control and chat & communication server).…
 bounteous17/libenom
CLI wrapper for MSFvenom that streamlines payload creation with profile management, automated listener generation, and organized output for…
 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
 c3c/cve-2021-4034
Precompiled multi-architecture exploit for CVE-2021-4034 (pkexec LPE) that drops a shared object to gain root privileges, with build scripts for…
 hluwa/cobaltstrike_swing_xss2rce
Exploit for CVE-2022-39197, a cross-site scripting vulnerability in Cobalt Strike's Swing GUI that enables remote code execution on team servers.
 davidcarliez/mythic_telegram_profile
Mythic C2 profile that tunnels Athena and Apollo agent traffic through Telegram bot-to-bot messages, bridging encrypted payloads to Mythic via its…
 neo-neo6/cve-2025-65018-heap-buffer-overflow-in-libpng-ps4-ps5-
Proof-of-concept exploit for a heap buffer overflow in libpng on PS4/PS5. Generates a malicious PNG that triggers the vulnerability when opened in…