CVE-2026-31431-Copy-Fail

Proof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation vulnerability, allowing unprivileged users to gain root access.

Proof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation vulnerability, allowing unprivileged users to gain root access.

Rust PoC for a Linux kernel local privilege escalation vulnerability, exploiting the Crypto API and splice to overwrite page cache and modify…

Proof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation vulnerability in the algif_aead module, enabling unprivileged…

Proof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation via splice() and crafted socket options, enabling arbitrary…

Educational analysis of CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG AEAD in-place operation, including technical root cause,…

Linux kernel exploit implementations targeting CVE-2008-0600, CVE-2008-0900, and CVE-2008-4210, providing proof-of-concept code for privilege…

An adapted version of the copy fail exploit to use parameters instead of dropping you into a root shell

Proof-of-concept exploit for CVE-2016-0728, a Linux kernel vulnerability enabling local privilege escalation via keyctl subsystem.

CVE-2026-31431 — Local Privilege Escalation via Linux Kernel Page Cache Corruption

Copy Fail (CVE-2026-31431) LPE exploit. A clean, multi-arch Python reimplementation targeting the Linux kernel AF_ALG page cache vulnerability.

Linux algif_aead page-cache write to root - Local Privilege Escalation Exploit

Exploit for CVE-2023-0179, a stack buffer overflow in the Linux nftables subsystem, enabling unprivileged local privilege escalation to root via…

Unprivileged proof-of-concept and x86_64 local privilege escalation for a Linux kernel Binder use-after-free (CVE-2026-64468), with KASAN lab and…

Bash script exploiting CVE-2021-4034 (Pwnkit) for local privilege escalation on vulnerable Linux systems. Copy-paste execution for quick testing.

GhostLock AAK Launcher - CVE-2026-43499 Linux kernel rtmutex stack UAF local privilege escalation trigger (GPLv3)

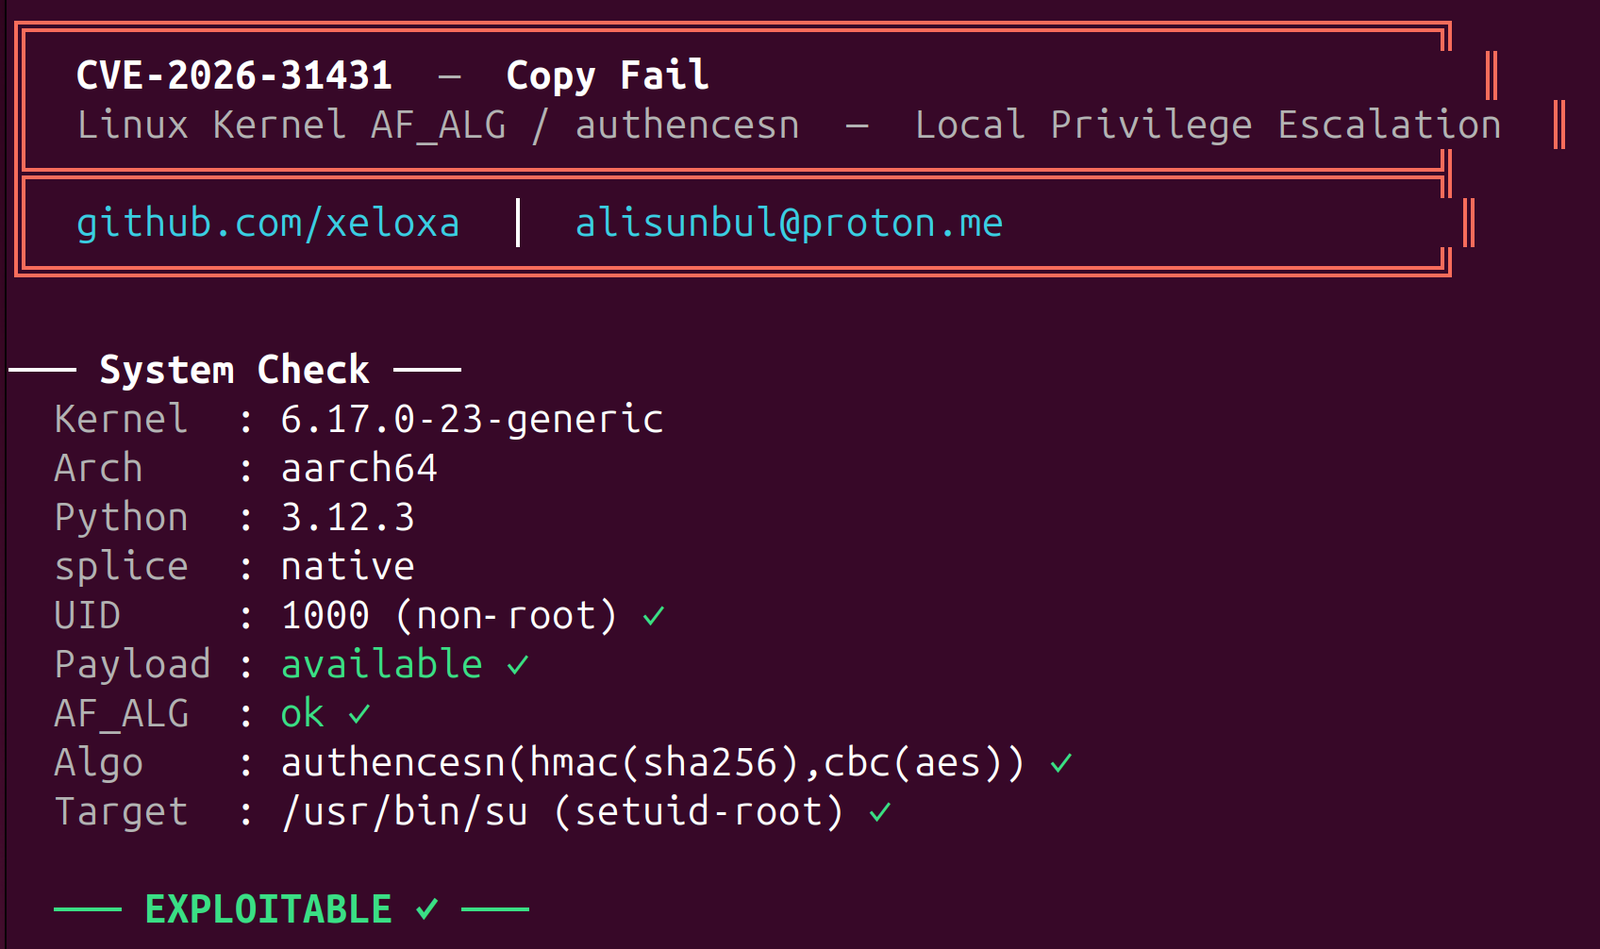
Local privilege escalation exploit for Linux kernel CVE-2026-31431, abusing AF_ALG and splice to patch /usr/bin/su and gain root.

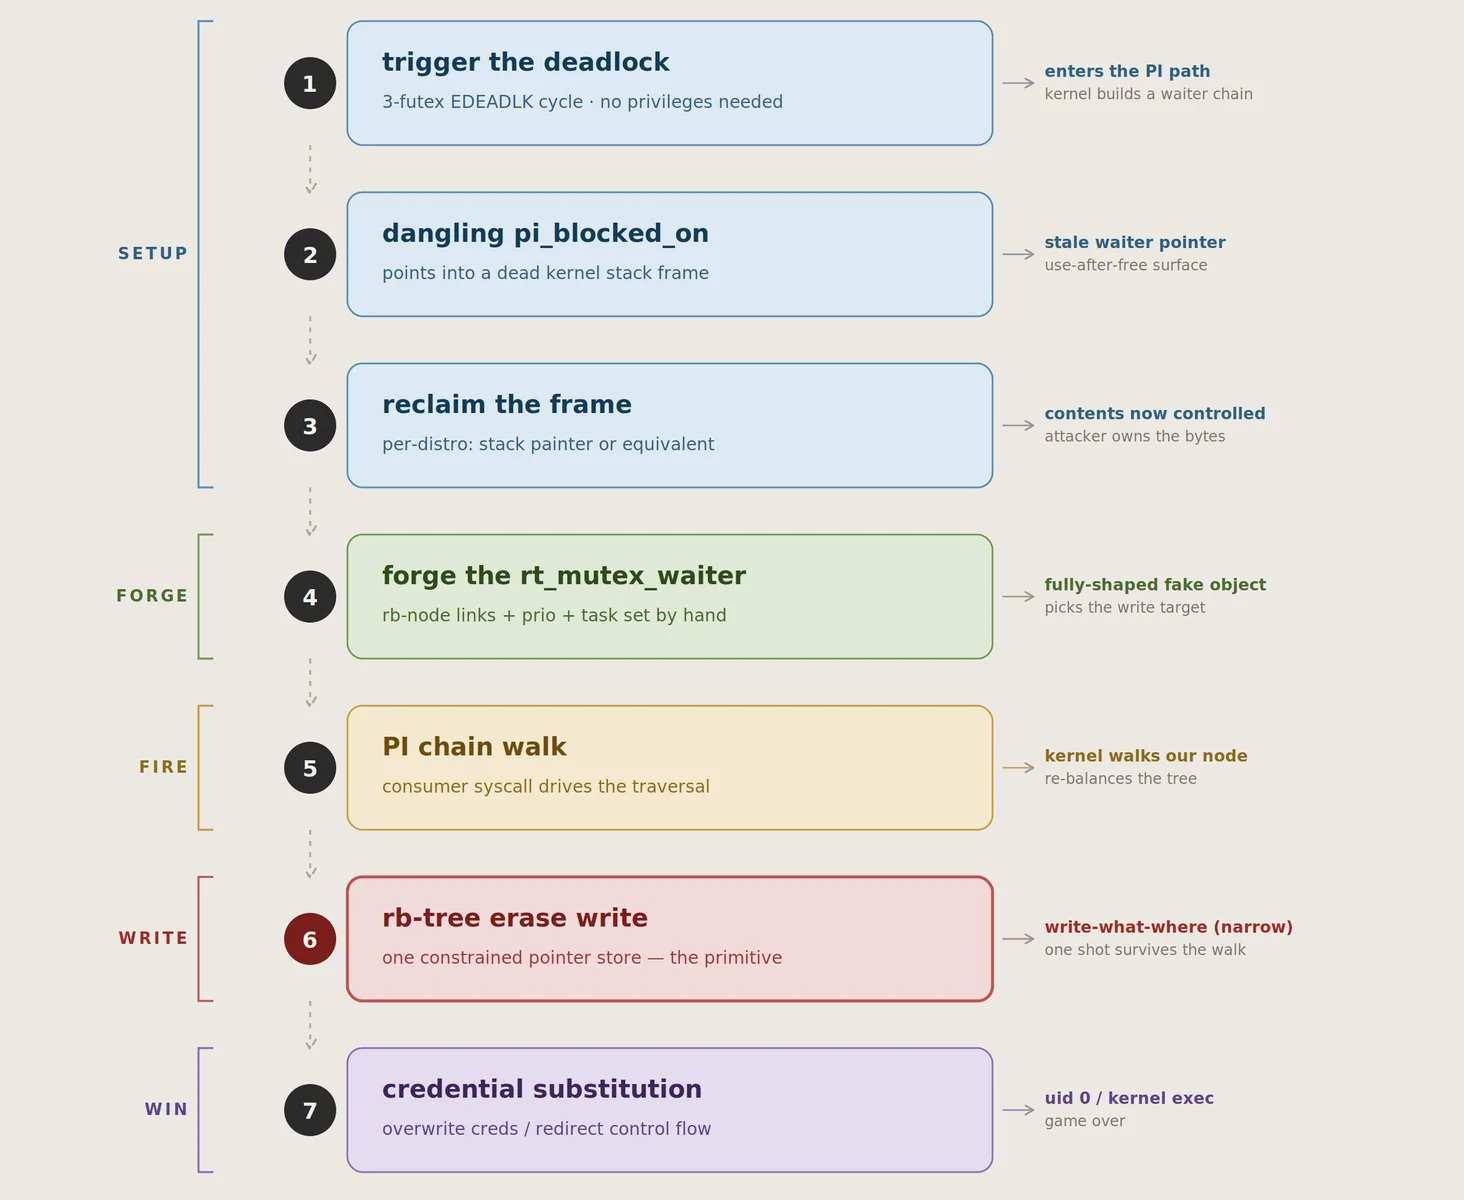
Weaponized proof-of-concept for CVE-2026-43499 (GhostLock), a Linux kernel rtmutex bug enabling local privilege escalation. Includes per-distribution…

Exploit for CVE-2026-31431, a Linux kernel authencesn bug enabling local privilege escalation and container escape via a 4-byte page cache write.