Android-Privilege-Escalation-Remote-Access-Vulnerability-CVE-2015-1805

AndroRAT is a capability that can be used to inject a root exploit as a silent installation to perform a malicious task on the device. This AndroRAT…

AndroRAT is a capability that can be used to inject a root exploit as a silent installation to perform a malicious task on the device. This AndroRAT…

Local privilege escalation exploit for CVE-2021-1675 (PrintNightmare) that installs a malicious DLL to gain SYSTEM access on vulnerable Windows…

Metasploit module that exploits a WordPress unserialization vulnerability (CVE-2024-31211) in WP_HTML_Token to achieve remote code execution.


Local privilege escalation exploit for Windows Ancillary Function Driver (afd.sys) targeting CVE-2023-21768, with post-exploitation cleanup code.…

Exploit for CVE-2022-39197, a cross-site scripting vulnerability in Cobalt Strike's Swing GUI that enables remote code execution on team servers.

Full-chain exploit for Android Chromium combining CVE-2026-11057 info leak and CVE-2026-5281 use-after-free to achieve vtable hijack and arbitrary…

Python implementation of the EternalBlue exploit (CVE-2017-0144) targeting SMBv1 vulnerability for remote code execution on Windows systems.

Gain privileges:system -> root,as a part of https://github.com/retme7/CVE-2014-7911_poc

Ghidra is a software reverse engineering (SRE) framework

GhostLock CVE-2026-43499 port for Galaxy Z Fold 8 (h8q)

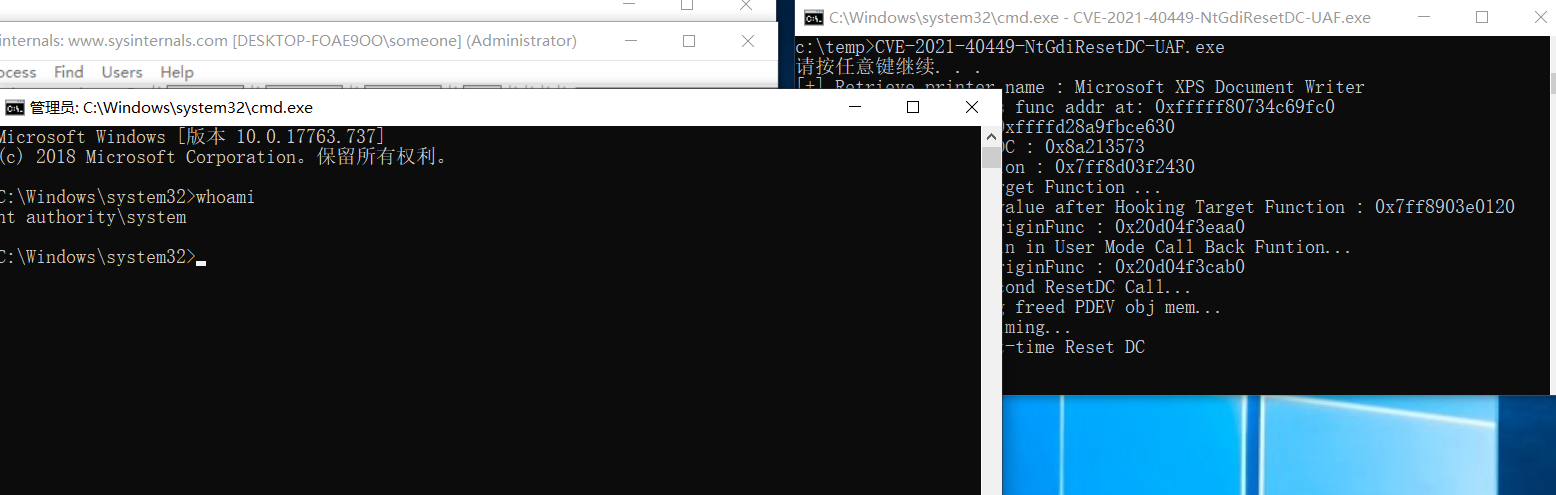
Proof-of-concept exploit for CVE-2021-40449, a Windows kernel use-after-free in NtGdiResetDC, demonstrating privilege escalation via user-space…

Fix for undefined method each in Metasploit’s bailiwicked_domain.rb (CVE-2008-1447 DNS cache poisoning module)

Local privilege escalation exploit for Android kernel vulnerability CVE-2020-0041, with portability across devices and kernel versions.

Tool to look for several security related Android application vulnerabilities

CVE-2019-2215 poc for Huawei hardened kernel

Win32k elevation of privilege exploit for CVE-2015-1701, providing proof-of-concept code for kernel-mode privilege escalation on vulnerable Windows…

A Remote Code Execution (RCE) exploit for Huawei HG532d based on CVE-2017-17215 vulnerability. Modded from original PoC code from exploit-db.com