
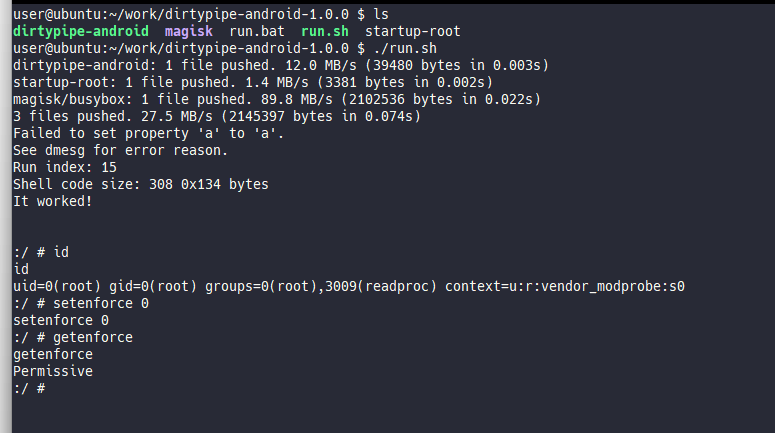
DirtyPipe-Android
 polygraphene/dirtypipe-android
Dirty Pipe root exploit for Android (Pixel 6)
android-securitybinary-exploitationexploitation+5
855
polygraphene/dirtypipe-androidDirty Pipe root exploit for Android (Pixel 6)
 sslab-gatech/avpass
Tool for leaking and bypassing Android malware detection system
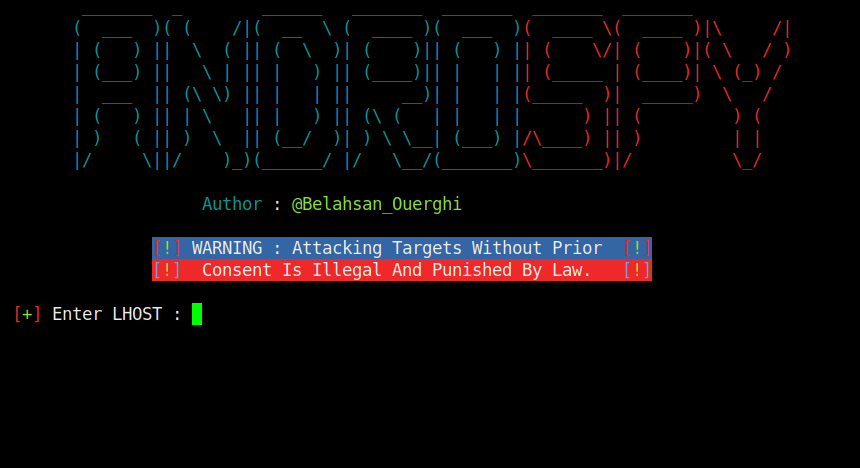 cyb0r9/androspy
Automated Android backdoor generator with crypter, IP poisoning, and Metasploit payload integration for penetration testing and red team operations.
 retme7/cve-2014-7911_poc
Local root exploit for Nexus5 Android 4.4.4(KTU84P)
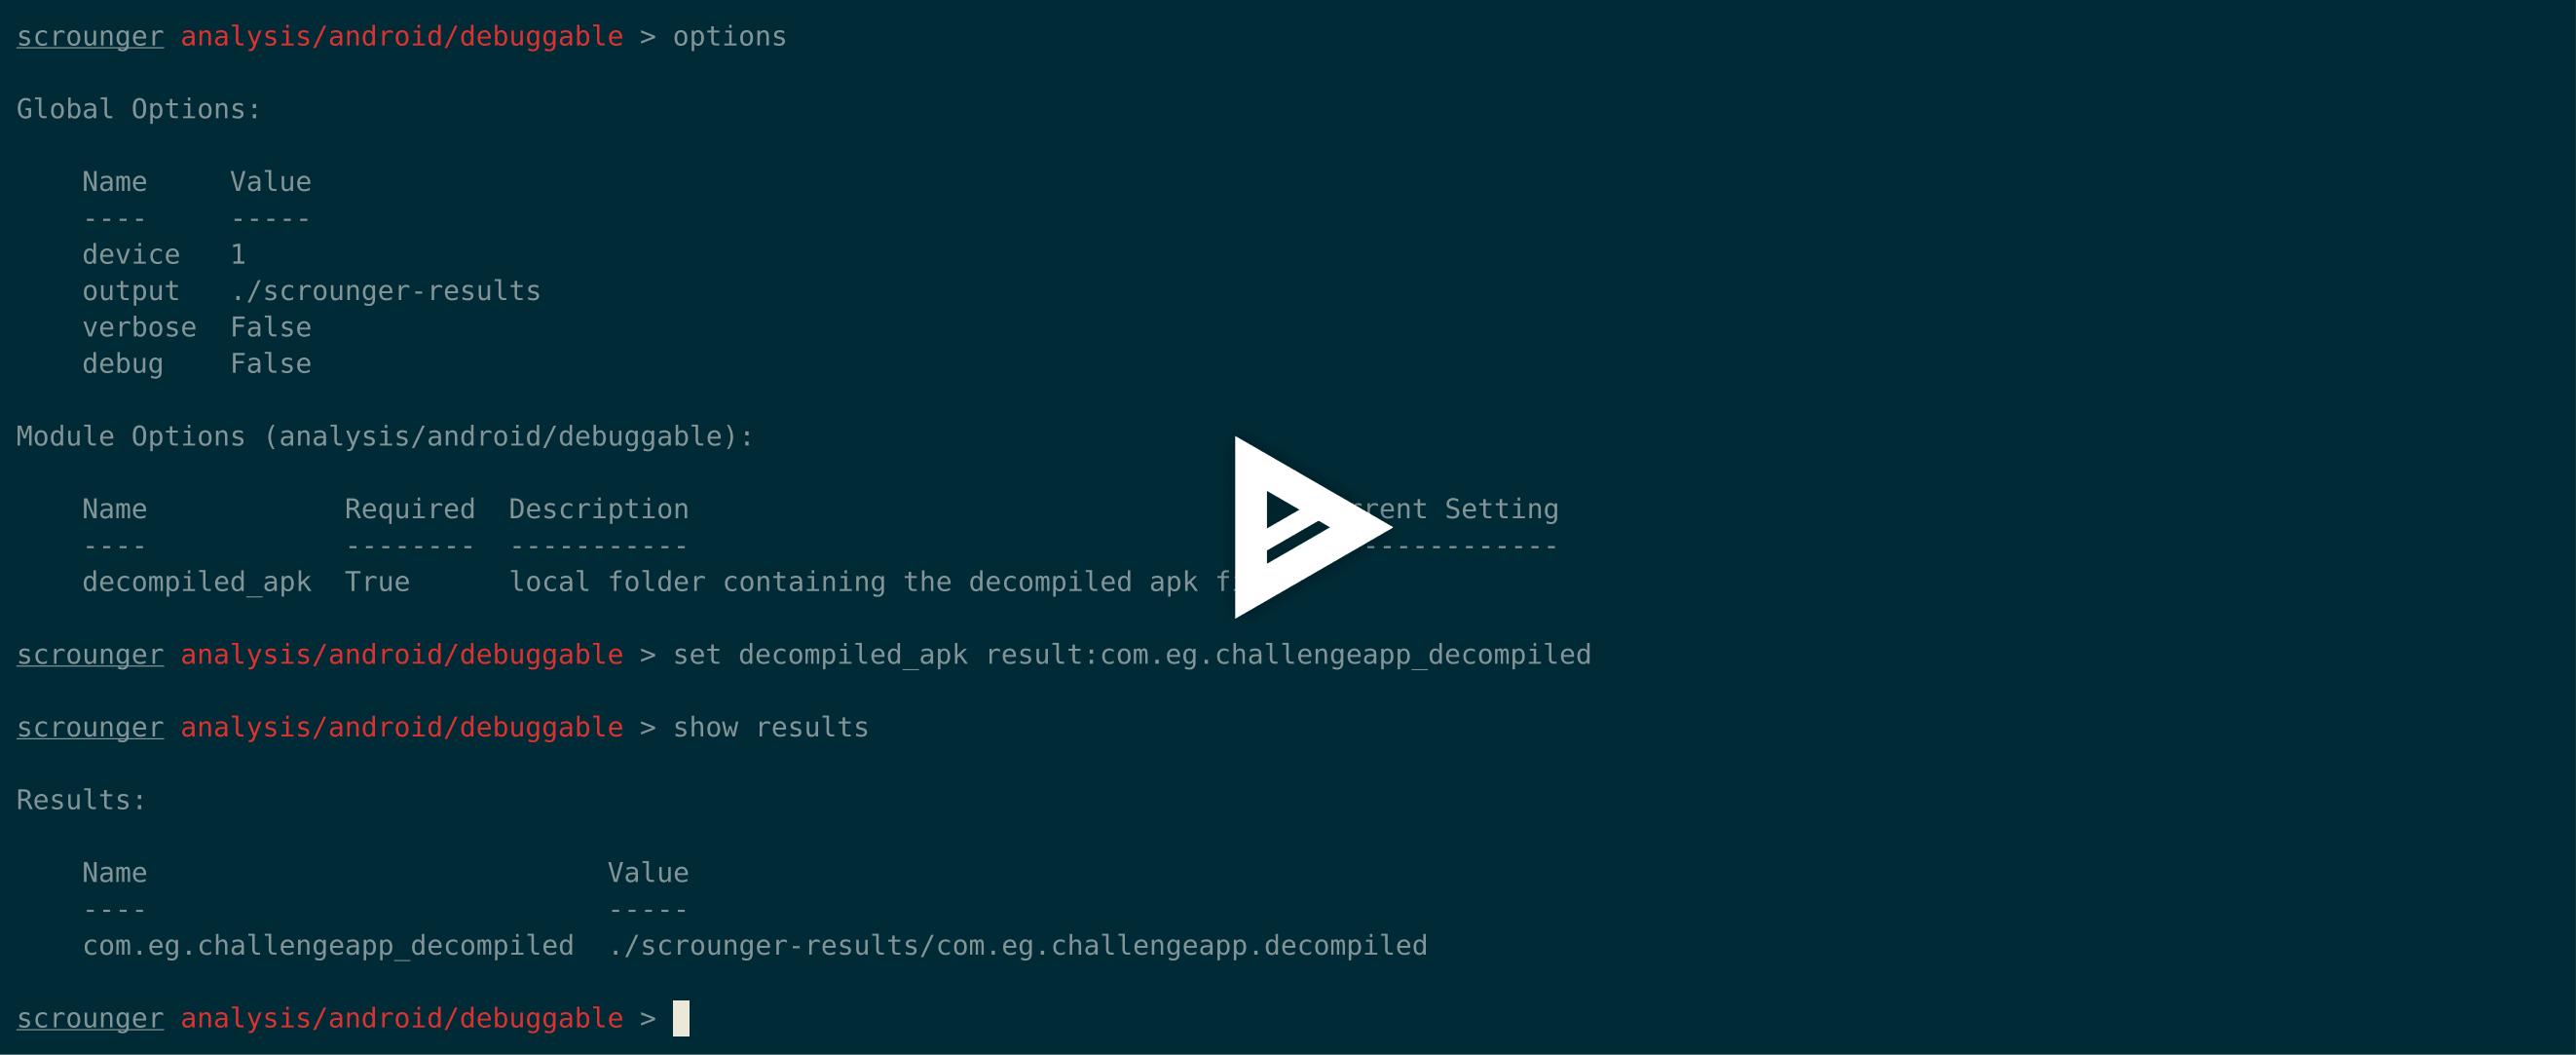 nettitude/scrounger
Mobile application testing toolkit
 pubglite55/oppo-ghostlock
OPPO Find N2 GhostLock (CVE-2026-43499) exploit adaptation
 retme7/cve-2014-4322_poc
Gain privileges:system -> root,as a part of https://github.com/retme7/CVE-2014-7911_poc
 viralsecuritygroup/knoxout
A PoC of KNOXout (CVE-2016-6584) - bypassing Samsung KNOX protections and root Samsung Galaxy S6 Android Device.
 jingmatrix/pixel-ksu-root
CVE research and exploits to help gaining roots for Pixel devices
 timwr/cve-2019-2215
Android kernel privilege escalation exploit for CVE-2019-2215, providing a proof-of-concept to achieve root access via a use-after-free vulnerability…
 r0rt1z2/ghostlock
Kernel root exploit (CVE-2026-43499) for some Amazon devices
 scs-labrat/android_autorooter
Exfiltrate sensitive user data from apps on Android 12 and 13 using CVE-2024-0044 vulnerability remotely
 michalbednarski/thisseemswrong
Writeup and exploit for CVE-2024-49746: Android's Parcel::continueWrite closing File Descriptors that are later used
 j4nn/cve-2020-0041
Local privilege escalation exploit for Android kernel vulnerability CVE-2020-0041, with portability across devices and kernel versions.
 xtiankisutsa/twiga
A tool that enumerates Android devices for information useful in understanding its internals and for exploit development. It supports android 4.2 to…
 quyicheng03-boop/xiaomi15-dada-cve-2026-64560
Device-bound CVE-2026-64560 adaptation for Xiaomi 15 dada OS4.0.0.8
 zenyxx-xd/rootmyvivo
One-click root for vivo/iQOO devices on locked bootloader | CVE-2026-43499 + KernelSU
 dimitrifourny/cve-2019-2215
Android privilege escalation via an use-after-free in binder.c