
venom
 r00t-3xp10it/venom
venom - C2 shellcode generator/compiler/handler
command-and-controlexploit-frameworkspayload-development+5
r00t-3xp10it/venomvenom - C2 shellcode generator/compiler/handler
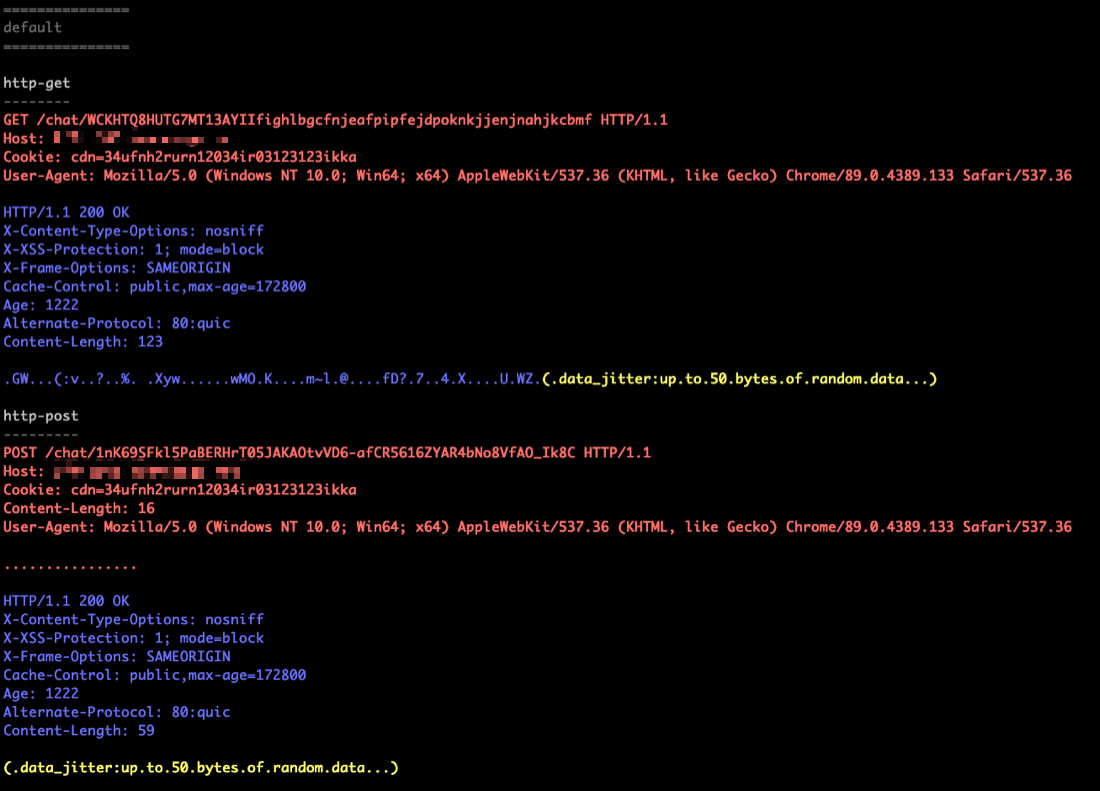 tylous/sourcepoint
Polymorphic C2 profile generator for Cobalt Strike that automates creation of evasive beacon configurations with randomized options for HTTP, DNS,…
 outflanknl/c2-tool-collection
A collection of tools which integrate with Cobalt Strike (and possibly other C2 frameworks) through BOF and reflective DLL loading techniques.
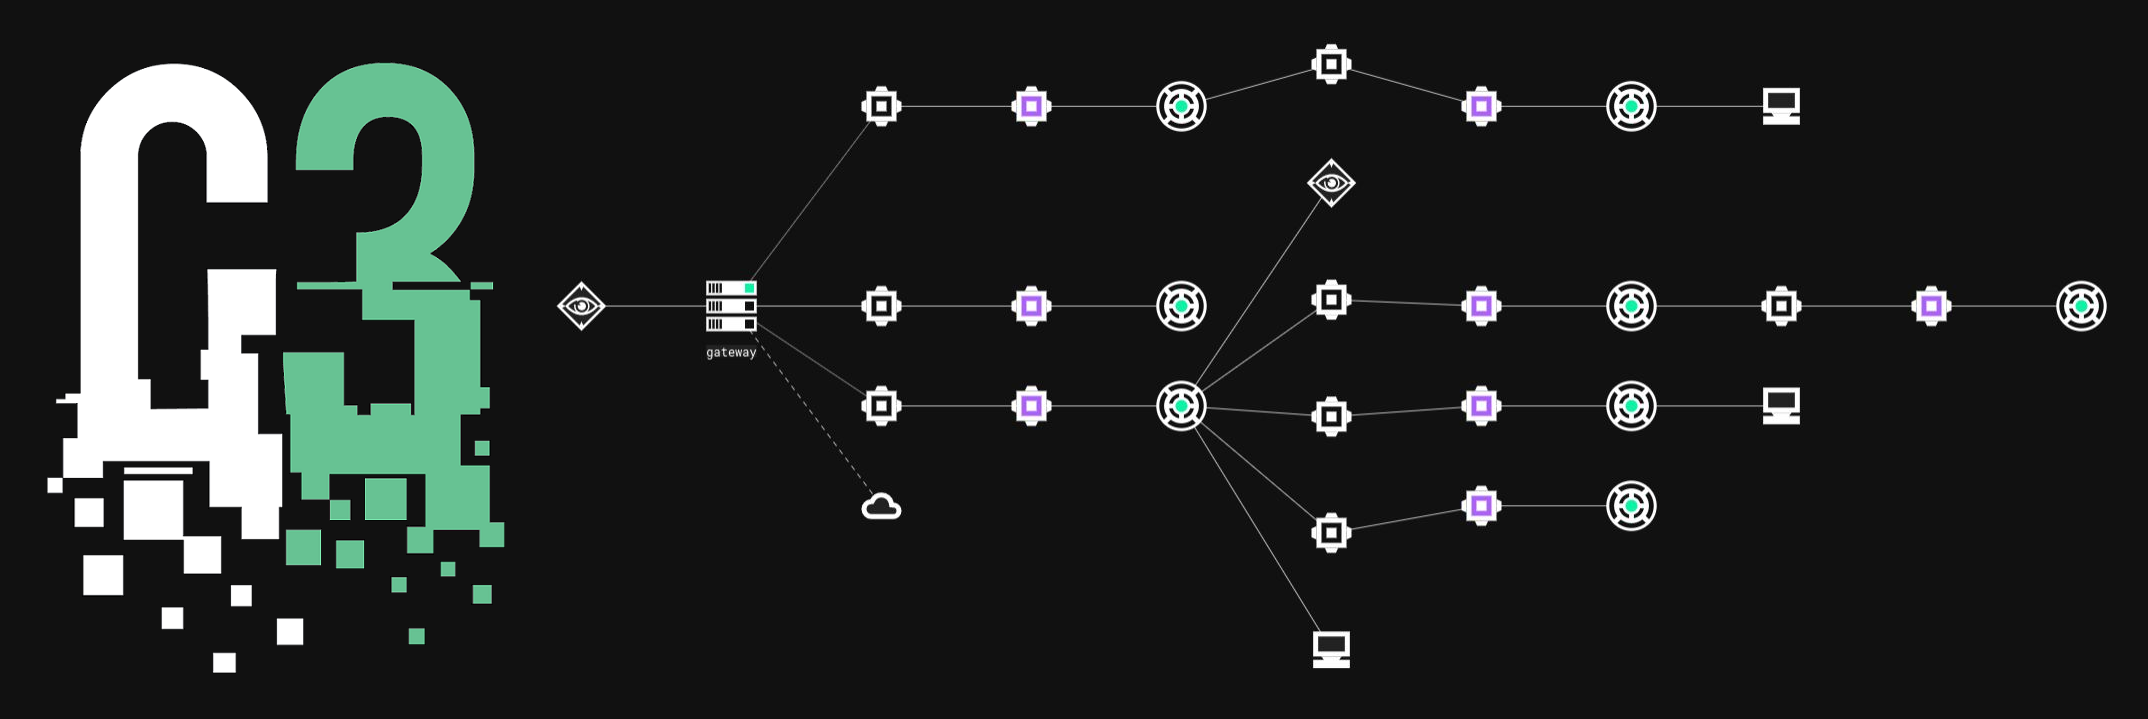 reverseclabs/c3
Custom Command and Control (C3). A framework for rapid prototyping of custom C2 channels, while still providing integration with existing offensive…
 xx0hcd/malleable-c2-profiles
Cobalt Strike - Malleable C2 Profiles. A collection of profiles used in different projects using Cobalt Strike https://www.cobaltstrike.com/.
 vulncheck-oss/go-exploit
Go-based exploit development framework with built-in phases for target verification, version scanning, exploitation, and C2. Supports multiple…
 mythicagents/thanatos
Mythic C2 agent targeting Linux and Windows hosts written in Rust
 rvn0xsy/cooolis-ms
Cooolis-ms是一个包含了Metasploit Payload Loader、Cobalt Strike External C2 Loader、Reflective DLL injection的代码执行工具,它的定位在于能够在静态查杀上规避一些我们将要执行且含有特征的代码,帮助红队人员更方便快…
 qax-a-team/cobaltstrike-toolset
Aggressor Script, Kits, Malleable C2 Profiles, External C2 and so on
 grisuno/lazyown
Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
 nettitude/poshc2_old
Powershell C2 Server and Implants
 bluscreenofjeff/malleable-c2-randomizer
A script to randomize Cobalt Strike Malleable C2 profiles and reduce the chances of flagging signature-based detection controls
 mythicagents/medusa
Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…
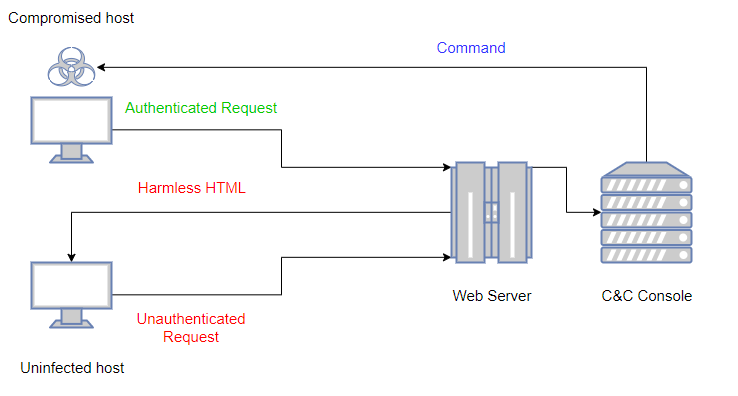 kudaes/lolbits
** DISCONTINUED ** C2 framework that uses Background Intelligent Transfer Service (BITS) as communication protocol and Direct Syscalls + Dinvoke for…
 gr1mmie/atlasc2
C# C2 Framework centered around Stage 1 operations
 und3rf10w/external_c2_framework
Python api for usage with cobalt strike's External C2 specification
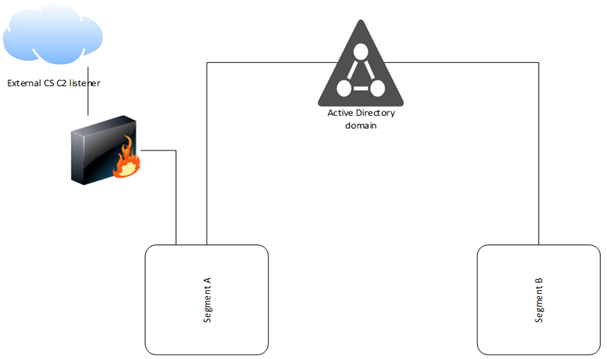 fox-it/ldapfragger
C2 tool routing Cobalt Strike beacon data over LDAP user attributes for stealthy command-and-control in segmented networks.