Polkit-pkexec-exploit-for-Linux

Exploit for CVE-2021-4034, a local privilege escalation vulnerability in polkit's pkexec, allowing unprivileged users to gain root on Linux systems.

Exploit for CVE-2021-4034, a local privilege escalation vulnerability in polkit's pkexec, allowing unprivileged users to gain root on Linux systems.

Development of an exploit for privilege escalation in Windows systems ( NT / 2k / XP / 2K3 / VISTA / 2k8 / 7 ) using the vulnerability CVE-2010-0232

Win32k elevation of privilege exploit for CVE-2015-1701, providing proof-of-concept code for kernel-mode privilege escalation on vulnerable Windows…

WiFiRanger 7.0.8rc3 Incorrect Access Control - Privilege Escalation

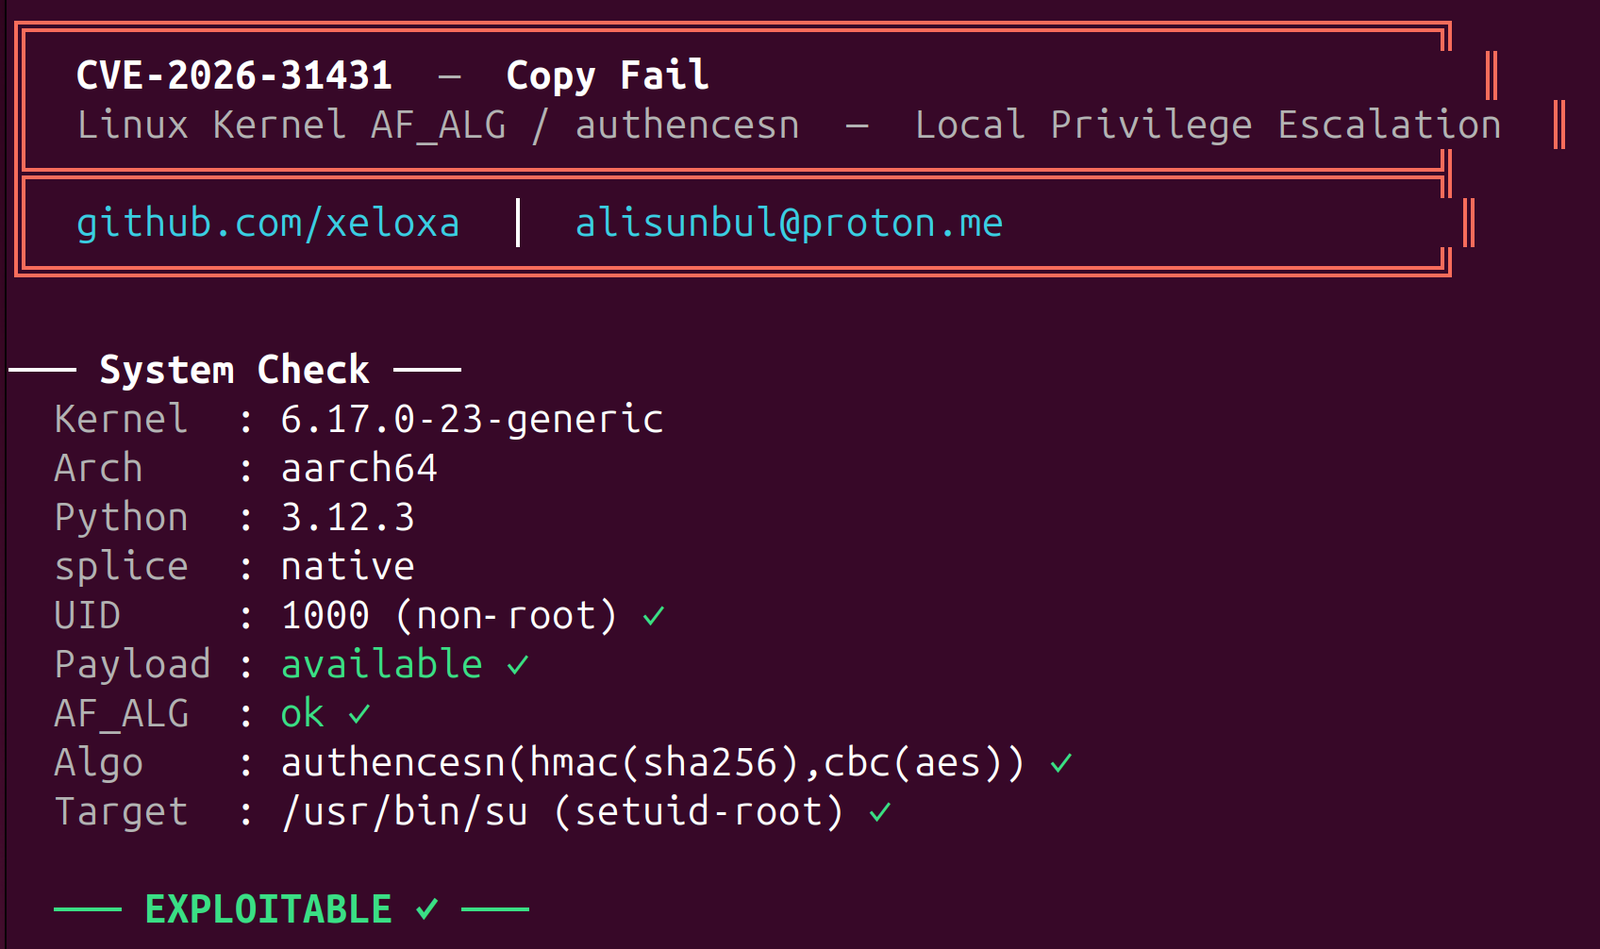
Copy Fail (CVE-2026-31431) LPE exploit. A clean, multi-arch Python reimplementation targeting the Linux kernel AF_ALG page cache vulnerability.

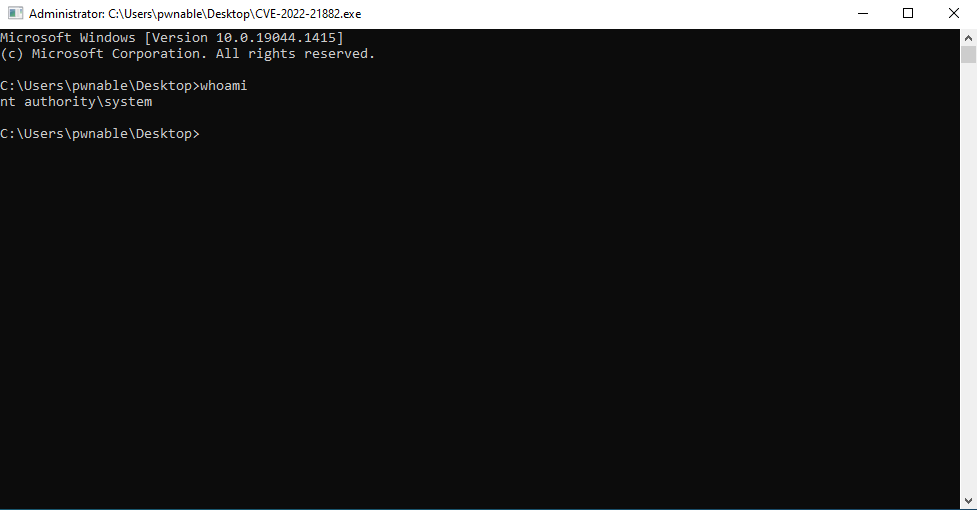
Win32k elevation of privilege exploit for CVE-2022-21882, providing a proof-of-concept implementation targeting Windows kernel vulnerabilities.

linux-kernel-exploits Linux平台提权漏洞集合

CVE-2026-31431 Copy Fail — Universal LPE exploit. Dynamic ELF offset + full-binary overwrite, Python 2/3 compatible with ctypes splice fallback

Proof of Concept for EFSRPC Arbitrary File Upload (CVE-2021-43893)

CVE-2026-31431 (Copy Fail) PoC - Linux kernel page cache corruption via authencesn AF_ALG + splice()

Copy Fail exploit (CVE-2026-31431) but in Rust.

CVE-2026-57851

Rust exploit PoC for Linux kernel LPE CVE-2026-31431 (AF_ALG page-cache write) plus eBPF runtime defense blocking AF_ALG socket creation via LSM or…

PoC shell exploit for CVE-2026-31431 (copy_fail) — Linux LPE via AF_ALG + splice page-cache overwrite. Single-shot, no race condition, kernel…

Exploit Chain of CVE-2025-6018 to CVE-2025-6019

Exploit for CVE-2021-4034 (PwnKit) that provides a root shell via polkit pkexec. Includes a dry-run mode to test vulnerability and a one-liner script…

Educational rewrite of the Copy Fail PoC (CVE-2026-31431) — Linux kernel LPE via algif_aead in-place crypto + splice() page-cache write

Blocking the DirtyFrag Linux LPE chain (CVE-2026-43284 / CVE-2026-43500) at runtime with a Cilium Tetragon TracingPolicy