
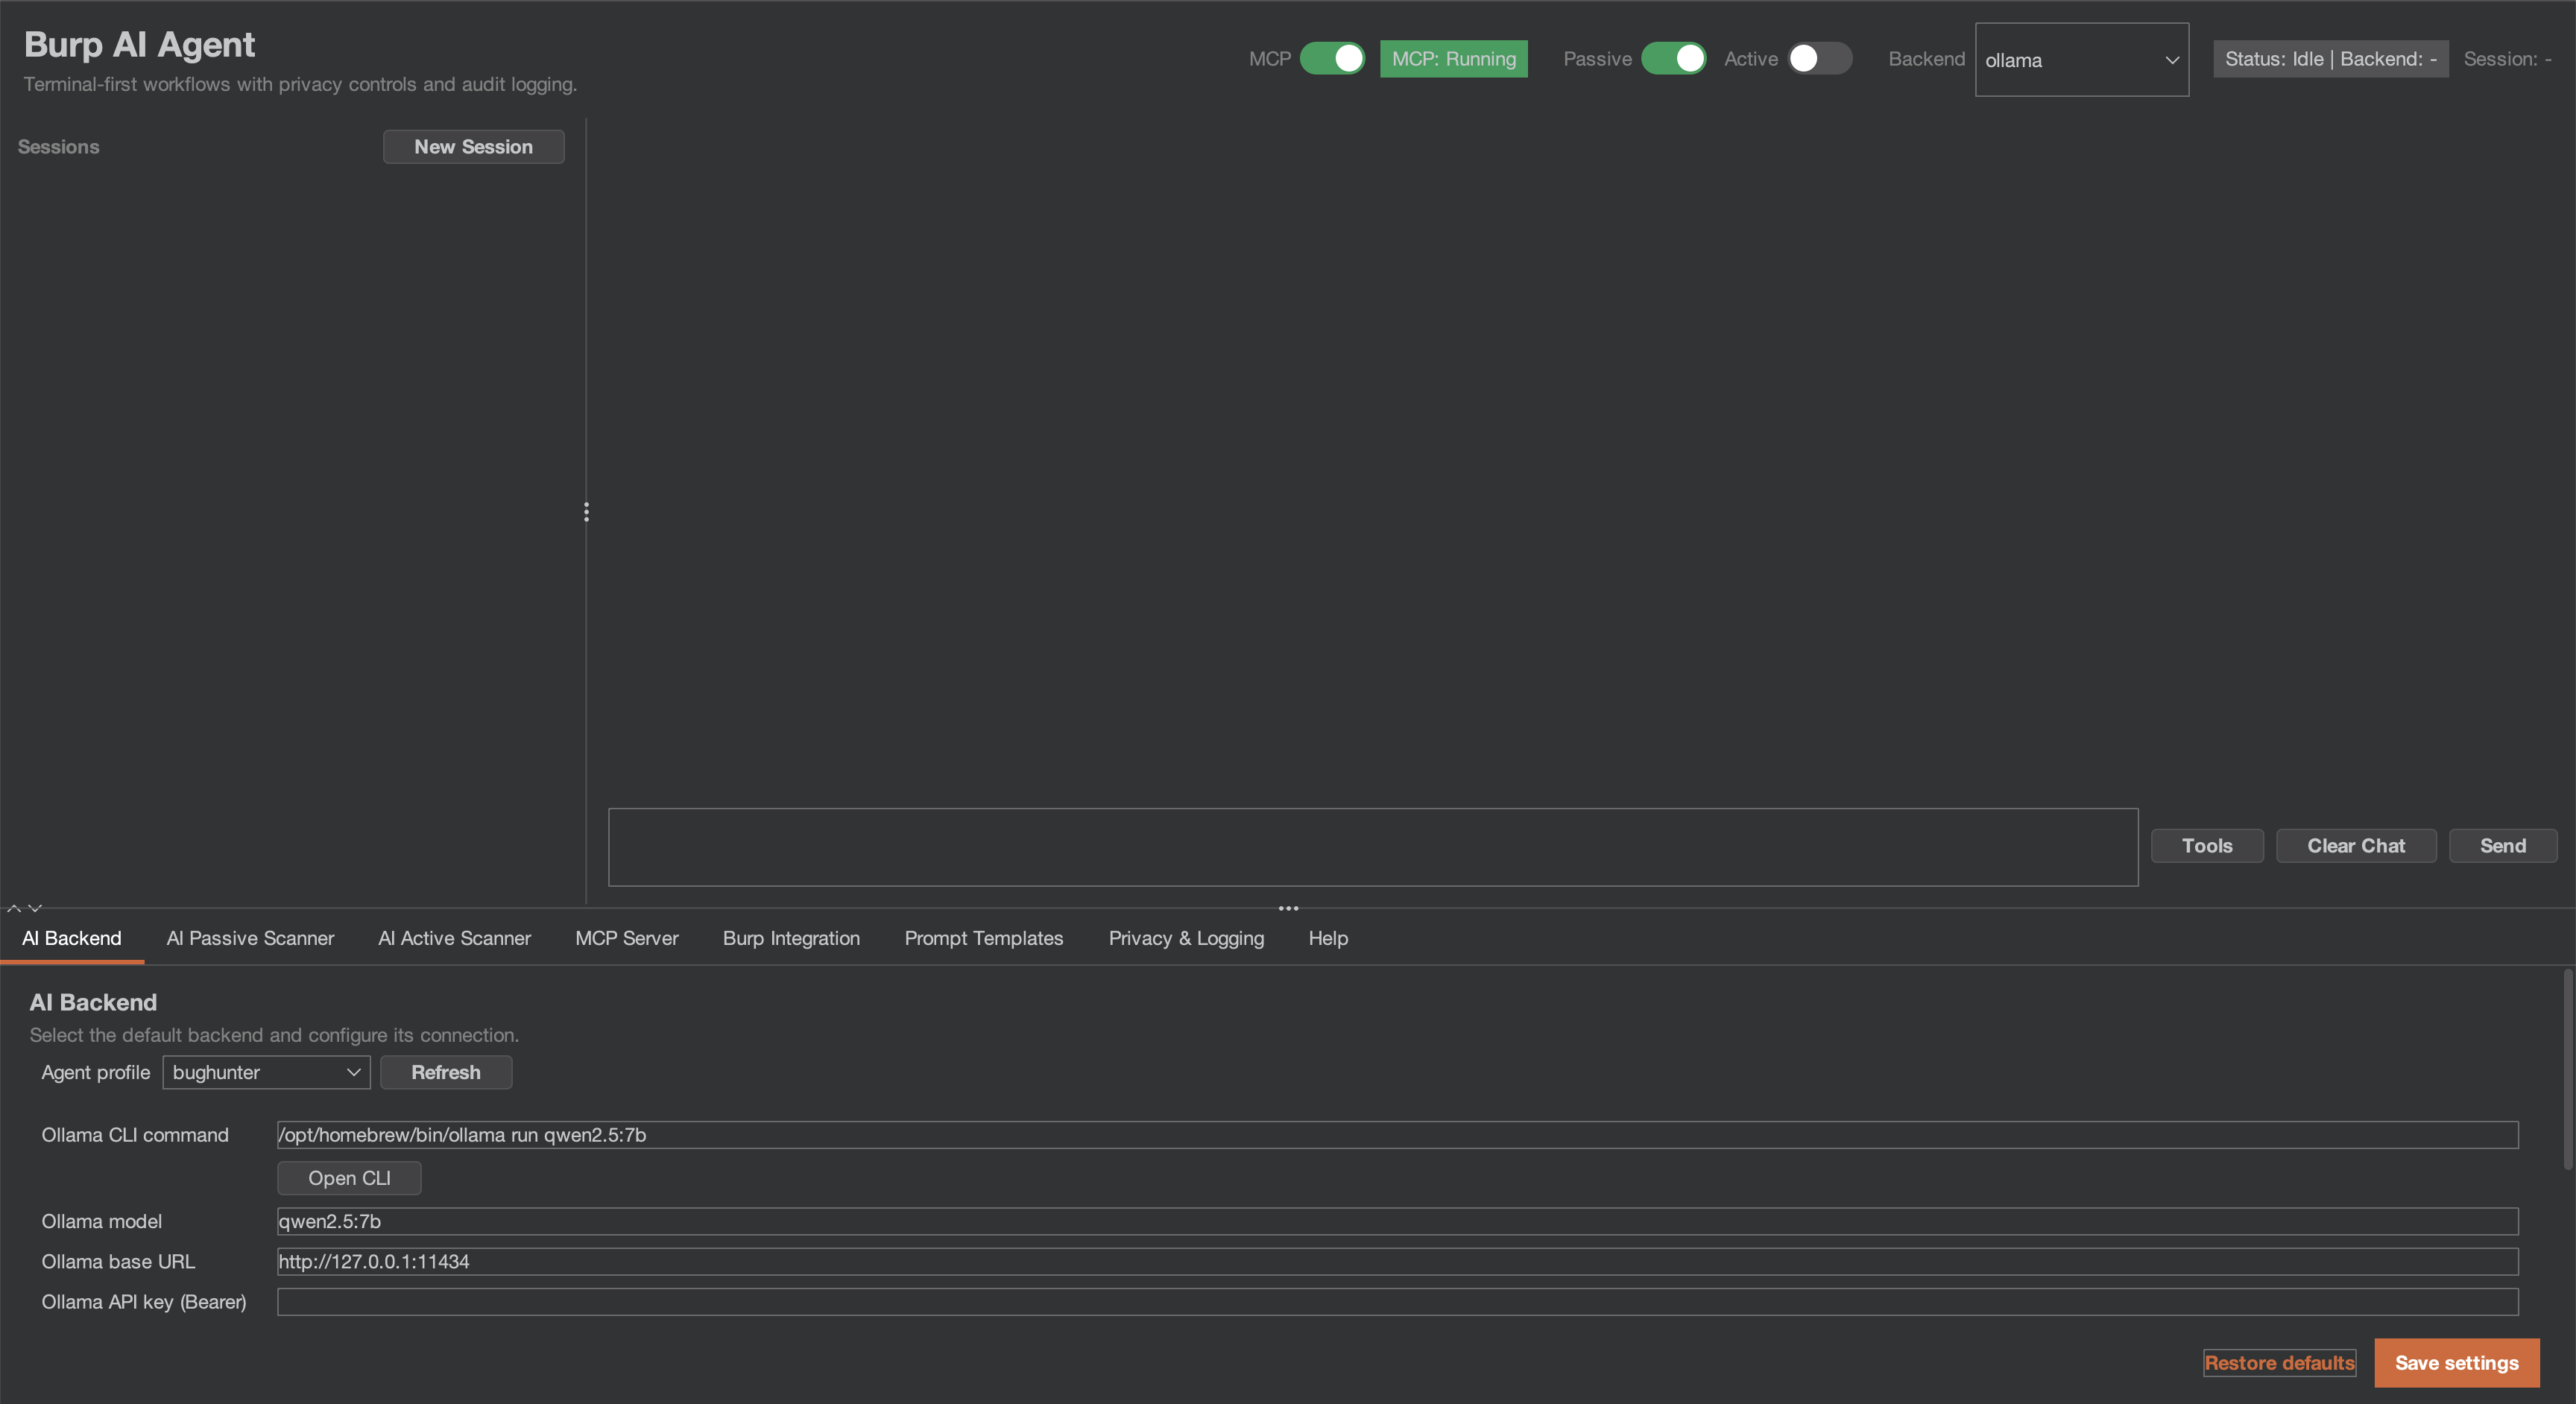
burp-ai-agent
 six2dez/burp-ai-agent
Burp Suite extension that adds built-in MCP tooling, AI-assisted analysis, privacy controls, passive and active scanning and more
ai-securityapi-security-testingexploit-frameworks+4
1.4k
six2dez/burp-ai-agentBurp Suite extension that adds built-in MCP tooling, AI-assisted analysis, privacy controls, passive and active scanning and more
 nu11secur1ty/sqlmap-nu11secur1ty
Professional extension of sqlmap project
 eddinos2/cve-2026-64747
Root-cause analysis and reachability PoC for CVE-2026-64747, a buffer overflow in the AppleAVE2 kernel extension. Includes reversed IOKit wire…
 eddinos2/cve-2026-64705
Root-cause analysis and proof-of-concept for CVE-2026-64705, a macOS HFS xattr kernel heap overflow. Includes weaponized HFS+ image, patcher, parser,…
 shinthink/pbck-exploit
📤 Mass exploitation framework for CVE-2026-56290 — Page Builder CK Joomla unauthenticated file upload to RCE
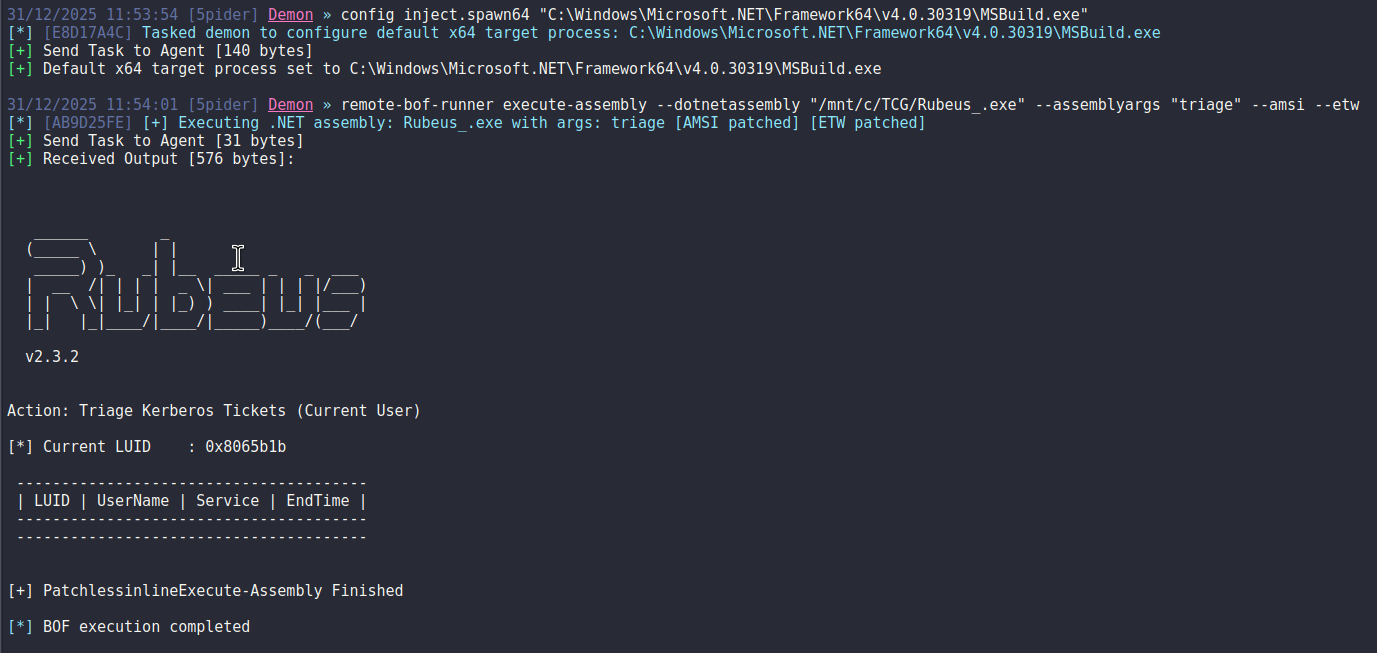 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
 sho-luv/react2shell
CVE-2025-55182 security test kit: CLI scanner + Chrome extension + Nuclei templates + Docker lab.
 orleven/tentacle
Tentacle is a POC vulnerability verification and exploit framework. It supports free extension of exploits and uses POC scripts. It supports calls to…
 und3rf10w/external_c2_framework
Python api for usage with cobalt strike's External C2 specification
 nvisosecurity/pycobalthound
pyCobaltHound is an Aggressor script extension for Cobalt Strike which aims to provide a deep integration between Cobalt Strike and Bloodhound.
 sec-consult/aggrokatz
Aggrokatz is an aggressor plugin extension for Cobalt Strike which enables pypykatz to interface with the beacons remotely and allows it to parse…
 xorrior/apfell-chrome-extension-c2server
Apfell C2 Server for the Google Chrome Extension Payload
 0xthirteen/staykit
Cobalt Strike extension for post-exploitation persistence using SharpStay .NET assembly. Provides GUI-driven persistence via Registry keys, Scheduled…
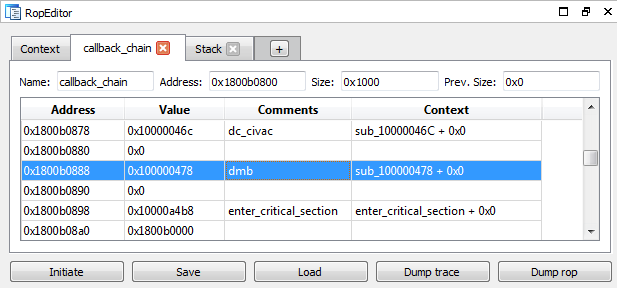 dsecurity/crauemu
crauEmu is an uEmu extension for developing and analyzing payloads for code-reuse attacks