
pixel-ksu-root
 jingmatrix/pixel-ksu-root
CVE research and exploits to help gaining roots for Pixel devices
android-securityexploitationexploit-frameworks+6
43
jingmatrix/pixel-ksu-rootCVE research and exploits to help gaining roots for Pixel devices
 oopnv70-lab/ghostlock-aak-apk
GhostLock AAK Launcher - CVE-2026-43499 Linux kernel rtmutex stack UAF local privilege escalation trigger (GPLv3)
 dorlow/hazel-cve-2026-43499
Firmware-specific temporary root exploit for Toshiba/Amazon Fire TV (hazel) using CVE-2026-43499. Implements ARM32 futex-PI UAF, kernel address leak,…
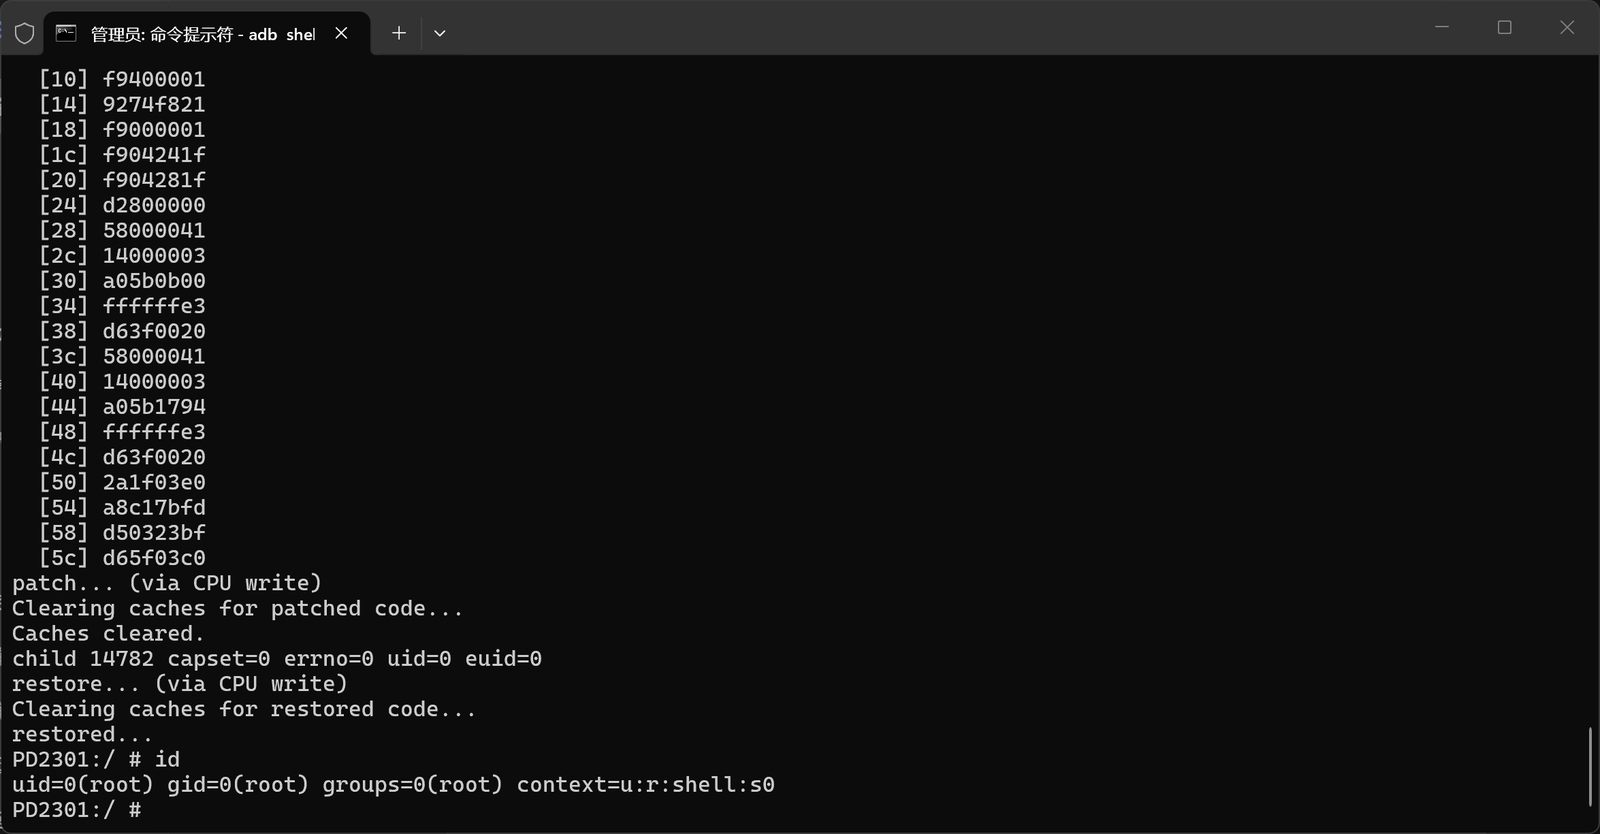 qingizi7/cve-2025-21479_iqooneo8
Local root exploit for CVE-2025-21479 (Adreno KGSL) on iQOO Neo8 (SM8475) - physical memory r/w, disables SELinux, spawns root shell
 xiaohj233/ghostlock-x200-app
vivo X200 设备端一键 root App(Shizuku 授权 shell 域执行,CVE-2026-43499)
 joaoaugustom/wordpress_backup_migration-rce_unauthenticated
This exploit is based on CVE-2023-6553 and was built upon the original exploit by Chocapik, it was added that a direct reverse shell can be obtained.
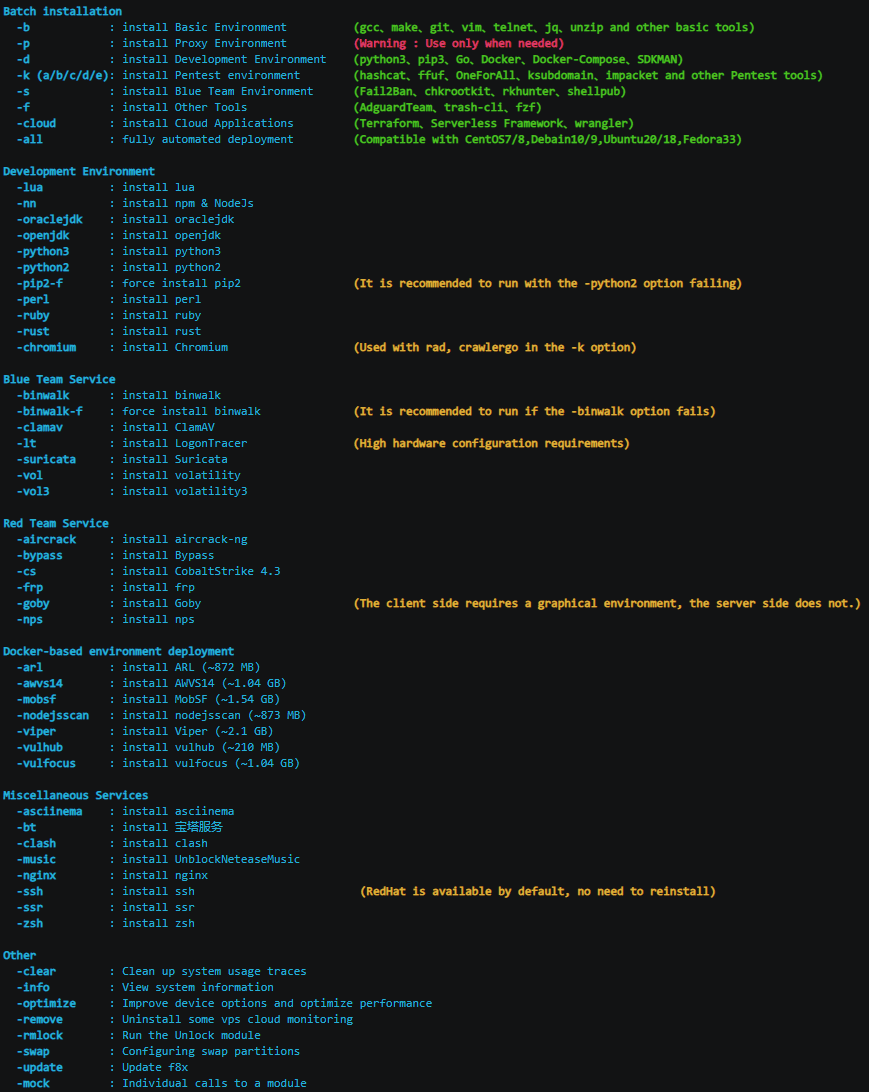 ffffffff0x/f8x
红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool
 abdullah50i/internal-penetration-testing-project-using-metasploit
Initialized & connected PostgreSQL to Metasploit. Reconnoitered 10.1.16.0/24 with Nmap and imported results. Enumerated hosts/services using SYN, SMB…
 huynambka/cve-2026-26114-poc
Proof-of-concept exploit for CVE-2026-26114, a remote code execution vulnerability in Microsoft SharePoint, with a Python PoC and Metasploit module…
 epsilonpointori/ikev2-poc
IKEv2, ikeext.dll, CVE-2026-33824, double free, heap grooming, ROP, SKF fragmentation, Windows exploit, anti-debug, obfuscation, API hooking,…
 qi4l/jyso
Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…
 danimrtzp/cve-2026-31431-revshell
Weaponized Python exploit for CVE-2026-31431, chaining Linux kernel privilege escalation to a daemonized root reverse shell with full PTY, patching…
 devianntsec/cve-2025-55182
Master's thesis research on CVE-2025-55182 (React2Shell). Modular exploitation framework with 6 attack scenarios (RCE, exfiltration, defacement),…
 kaleth4/cve-2026-4747-
Remote kernel exploit for FreeBSD CVE-2026-4747, leveraging a stack buffer overflow in kgssapi.ko to achieve RCE with a reverse shell. Includes…
 vig9610/exploiting-samba-on-metasploitable-2
Utilize metasploit from a Kali Linux machine to exploit a well-known samba vulnerability (CVE-2007-2447). This is done in order to infiltrate a…
 sadisticnight/poc-cve-2025-62222
Proof-of-concept demonstrating remote code execution via prompt injection in GitHub Copilot Chat, using a crafted Python file to trigger a…
 nulltrace1336/samba-exploit-cve-2007-2447
Step-by-step guide to exploiting Samba 3.0.20 (CVE-2007-2447) using Metasploit, including Nmap scanning, payload setup, and reverse shell execution.
 hklabcr/cve-2011-2523
Manual and automated exploitation walkthrough for vsftpd 2.3.4 backdoor (CVE-2011-2523) with custom reverse shell payload and Metasploit integration…