

CVE-2026-74586
 tarpeg007/cve-2026-74586
Unprivileged proof-of-concept for CVE-2026-74586, a Linux kernel SCTP ASCONF use-after-free. Provides a raw-packet trigger, reliability metrics, and…
binary-exploitationexploitationexploit-frameworks+1
1
tarpeg007/cve-2026-74586Unprivileged proof-of-concept for CVE-2026-74586, a Linux kernel SCTP ASCONF use-after-free. Provides a raw-packet trigger, reliability metrics, and…
 pubglite55/oppo-ghostlock
OPPO Find N2 GhostLock (CVE-2026-43499) exploit adaptation
 joinchang/ghostlock-oneplus
GhostLock (CVE-2026-43499) kernel exploit for Android devices with locked bootloader
 0b0111100/2009
Collection of Linux kernel exploits targeting CVE-2009-1185, CVE-2009-1337, CVE-2009-2692, CVE-2009-2698, and CVE-2009-3547, providing…
 0b0111100/2008
Linux kernel exploit implementations targeting CVE-2008-0600, CVE-2008-0900, and CVE-2008-4210, providing proof-of-concept code for privilege…
 0b0111100/2006
Linux kernel privilege escalation exploits targeting CVE-2006-2451 and CVE-2006-3626, providing proof-of-concept code for local privilege escalation…
 0b0111100/2005
Linux kernel exploit implementations targeting CVE-2005-0736 and CVE-2005-1263, providing proof-of-concept code for privilege escalation on…
 0b0111100/2004
Linux kernel privilege escalation exploits targeting CVE-2004-0077 and CVE-2004-1235, including caps_to_root technique for gaining root access.
 dorlow/hazel-cve-2026-43499
Firmware-specific temporary root exploit for Toshiba/Amazon Fire TV (hazel) using CVE-2026-43499. Implements ARM32 futex-PI UAF, kernel address leak,…
 oopnv70-lab/ghostlock-aak-apk
GhostLock AAK Launcher - CVE-2026-43499 Linux kernel rtmutex stack UAF local privilege escalation trigger (GPLv3)
 franklinf25/cve-2026-31431
Analyzes CVE-2026-31431, a Linux kernel AF_ALG AEAD vulnerability, providing a safe detector, in-lab LPE exploit, and QEMU-based A/B kernel lab for…
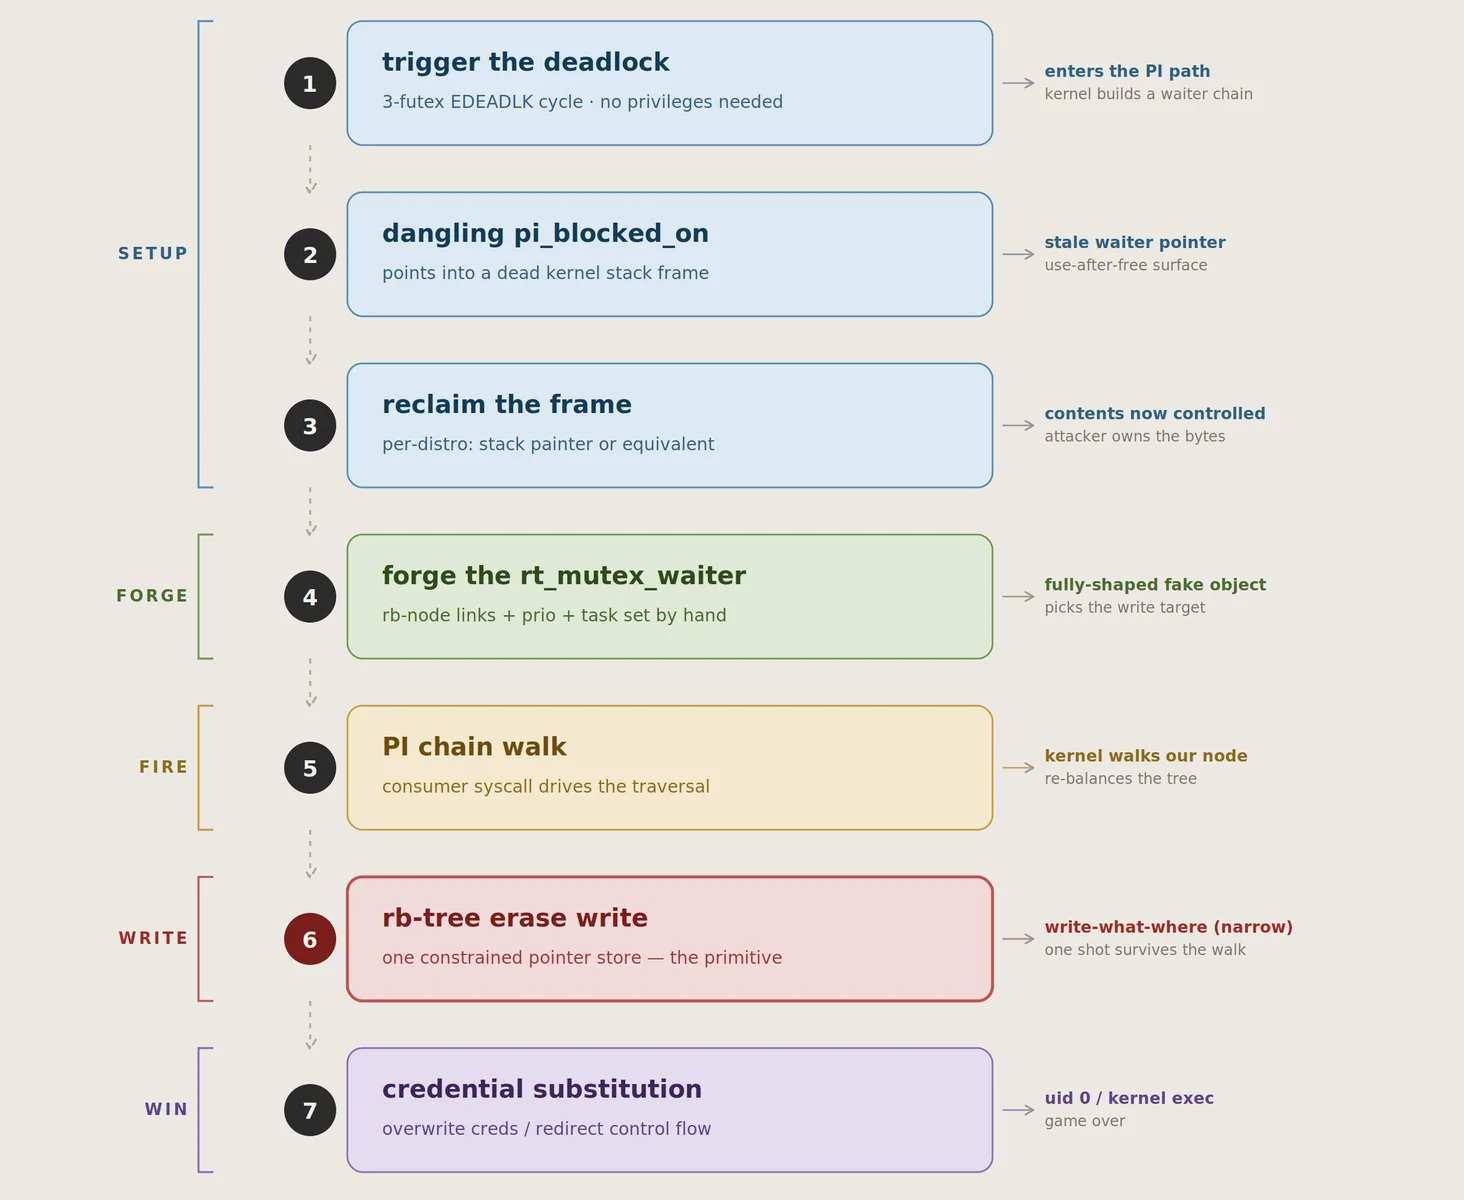 lkeld/cve-2026-43499-poc
Weaponized proof-of-concept for CVE-2026-43499 (GhostLock), a Linux kernel rtmutex bug enabling local privilege escalation. Includes per-distribution…
 xiaobailovesstirring/ghostlock-k419-adapter
GhostLock (CVE-2026-43499) adapter for 4.19.152-perf+ Android kernel
 lanleft/cve-2023-1281
Proof-of-concept exploit for CVE-2023-1281, a use-after-free vulnerability in the Linux kernel traffic control index filter (tcindex), demonstrating…
 aramosf/cve-2026-64468
Unprivileged proof-of-concept and x86_64 local privilege escalation for a Linux kernel Binder use-after-free (CVE-2026-64468), with KASAN lab and…
 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.
 soralis0912/cve-2026-43499-aristotle
Local privilege escalation exploit for Xiaomi XIG04 (Android 12) via CVE-2026-43499 kernel use-after-free. Data-only direct-root technique with MTE…
 whatswrongandwhy/cve-2017-16995
Standalone exploit for CVE-2017-16995, a Linux kernel local privilege escalation vulnerability, providing a ready-to-use proof-of-concept for…