
ghostlock-aak-apk
 oopnv70-lab/ghostlock-aak-apk
GhostLock AAK Launcher - CVE-2026-43499 Linux kernel rtmutex stack UAF local privilege escalation trigger (GPLv3)
android-securitybinary-exploitationexploitation+5
7
oopnv70-lab/ghostlock-aak-apkGhostLock AAK Launcher - CVE-2026-43499 Linux kernel rtmutex stack UAF local privilege escalation trigger (GPLv3)
 0b0111100/2008
Linux kernel exploit implementations targeting CVE-2008-0600, CVE-2008-0900, and CVE-2008-4210, providing proof-of-concept code for privilege…
 0b0111100/2006
Linux kernel privilege escalation exploits targeting CVE-2006-2451 and CVE-2006-3626, providing proof-of-concept code for local privilege escalation…
 lkeld/cve-2026-43499-poc
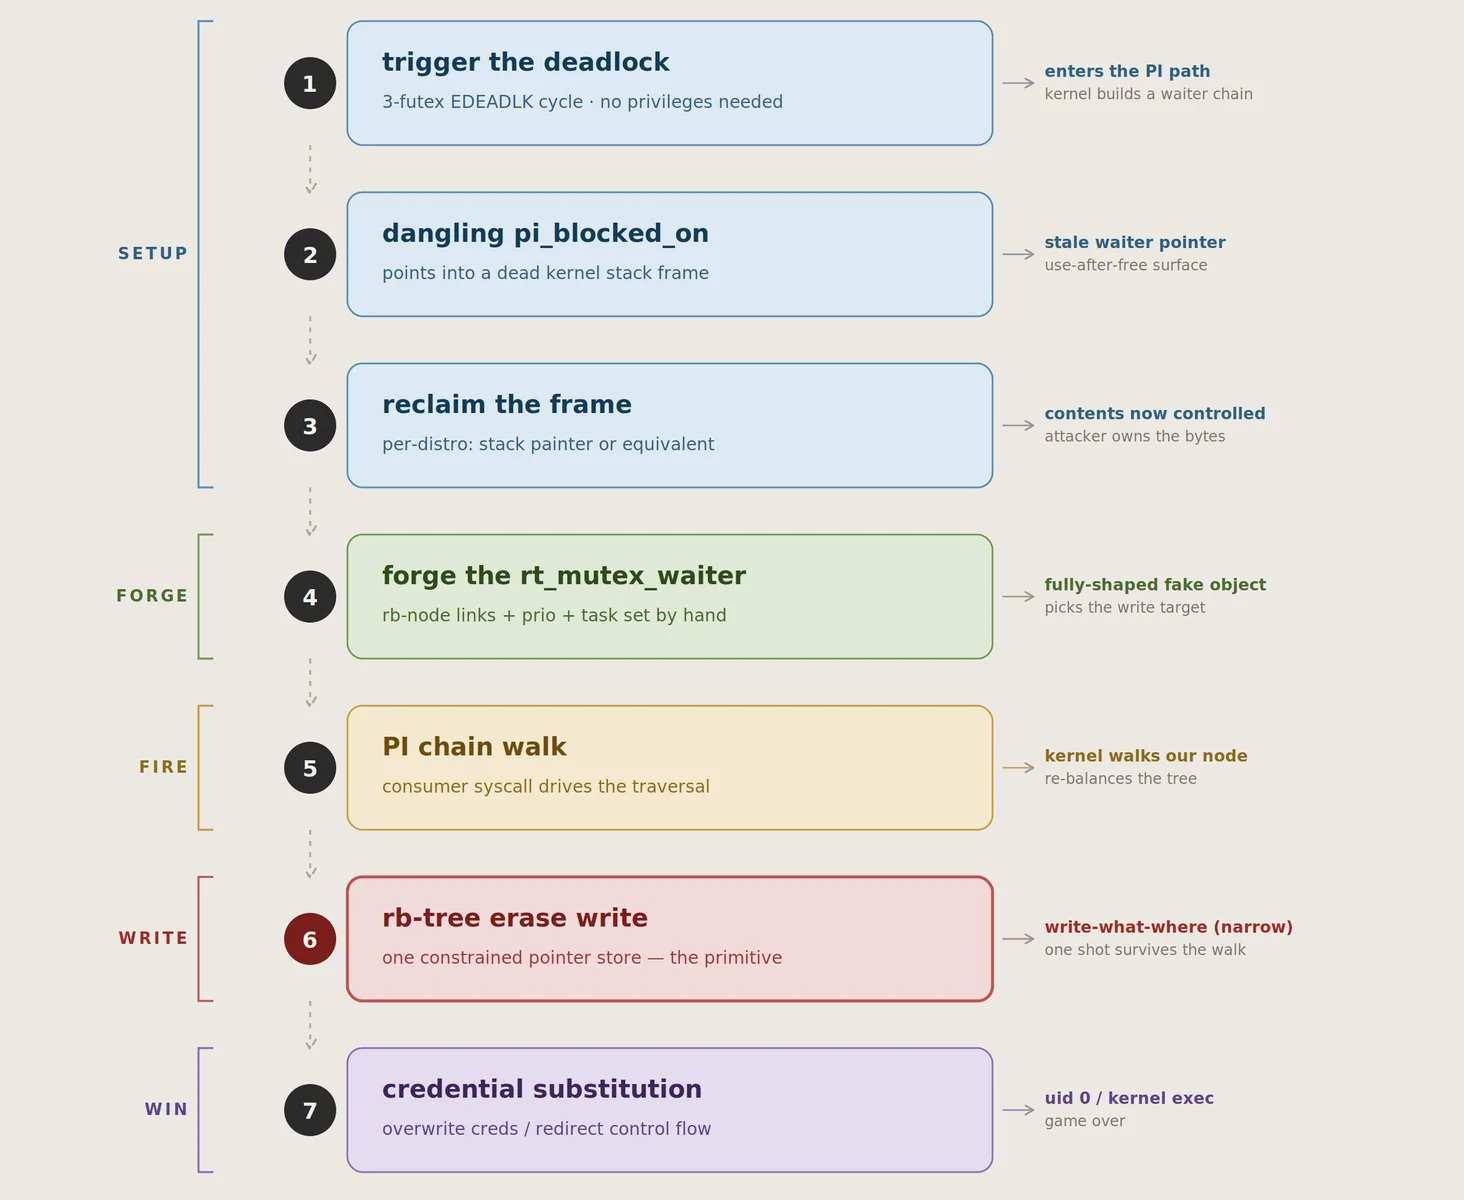
Weaponized proof-of-concept for CVE-2026-43499 (GhostLock), a Linux kernel rtmutex bug enabling local privilege escalation. Includes per-distribution…
 r3dw4n48m3d/cve-2021-3493-exploit
C-based local privilege escalation exploit for CVE-2021-3493, targeting OverlayFS in Linux kernels prior to 5.11. Provides compilation and usage…
 aramosf/cve-2026-64468
Unprivileged proof-of-concept and x86_64 local privilege escalation for a Linux kernel Binder use-after-free (CVE-2026-64468), with KASAN lab and…
 soralis0912/cve-2026-43499-aristotle
Local privilege escalation exploit for Xiaomi XIG04 (Android 12) via CVE-2026-43499 kernel use-after-free. Data-only direct-root technique with MTE…
 whatswrongandwhy/cve-2017-16995
Standalone exploit for CVE-2017-16995, a Linux kernel local privilege escalation vulnerability, providing a ready-to-use proof-of-concept for…
 adityasingh108/cve-2026-31431-metasploit-exploit
Automated Metasploit post-exploitation module for CVE-2026-31431 ("Copy Fail"). Weaponizes a deterministic logic flaw in the Linux kernel AF_ALG…
 smarttfoxx/copyfail
CVE-2026-31431 (Copy Fail) PoC - Linux kernel page cache corruption via authencesn AF_ALG + splice()
 p401a-ops/copy-fail
Detects and exploits CVE-2026-31431 (Copy Fail) local privilege escalation on Astra Linux, with Python 3.7+ compatibility and one-liner deployment.
 polyakovavv/copyfail
C-based local privilege escalation exploit for CVE-2026-31431, a Linux kernel vulnerability in the AF_ALG crypto interface, providing root access via…
 dgrobinson0/copyfile_cve-2026-31431
Local privilege escalation exploit for CVE-2026-31431, corrupting setuid binaries in page cache via AF_ALG and splice to gain root shell.
 cleozi/copy_grail
Elegant C++ exploit for CVE-2026-31431 (Copy Fail) using AF_ALG authenticated encryption + splice(2) to overwrite setuid binary memory
 ryan2929/cve-2026-43284-
Local privilege escalation exploit for Linux kernel CVE-2026-43284 (Dirty Flag), providing root access on vulnerable systems.
 hori0729/cve-2026-31431-verificador-exploit
Local privilege escalation exploit for Linux kernel CVE-2026-31431, exploiting AF_ALG and splice() to modify page cache and gain root shell.
 guiimoraes/cve-2026-31431
Python implementation of a Linux kernel local privilege escalation exploit for CVE-2026-31431, leveraging xfrm ESP-in-UDP MSG_SPLICE_PAGES no-COW to…
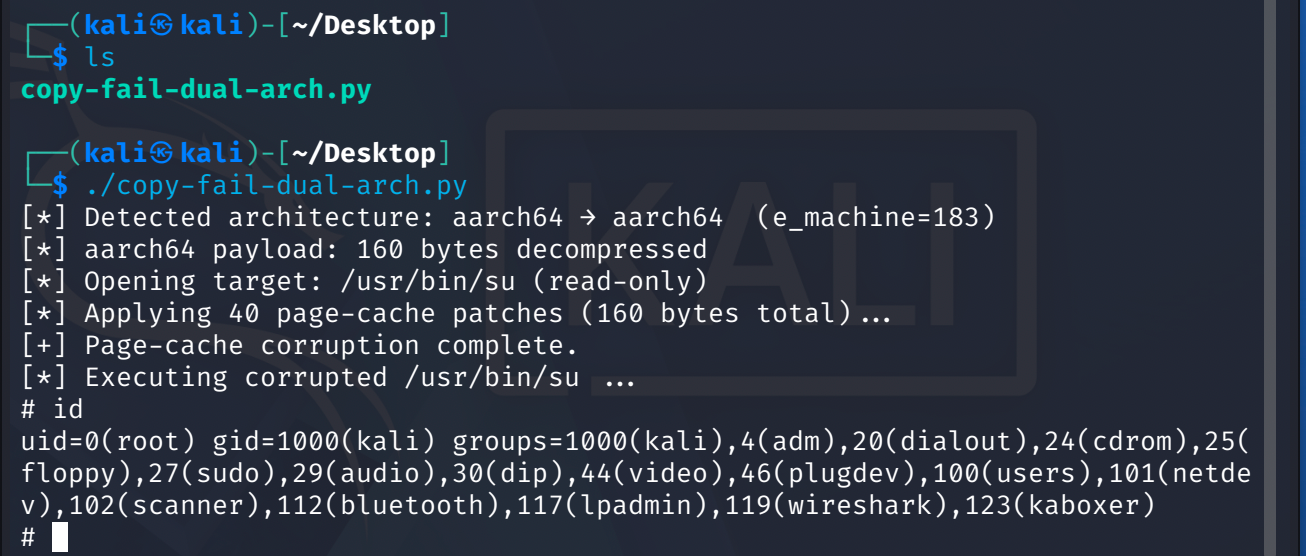 0xer0/cve-2026-31431-copy-fail-add-arm64
Python exploit for CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG and splice() to write to page cache, gaining root on arm64…