

discover
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
api-security-testingcloud-securitycontainer-security+9
3.9k
leebaird/discoverCustom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 zeze-zeze/ioctlance
A tool that is used to hunt vulnerabilities in x64 WDM drivers
 dannyendortest/ollama-consumer
Demo consumer for ollama v0.5.0 (vulnerable range for CVE-2024-12886) — endorctl scan target
 frkngksl/shoggoth
Polymorphic encryptor that transforms shellcode, PE, and COFF files into obfuscated, position-independent payloads with RC4 and random block cipher…
 dr4x-c0d3r/sudo-chroot
Sudo Vulnerability Local PrivEsc (CVE-2025-32463) POC with Python
 darmado/atomic-red-team-c2
ARTi-C2 is a post-exploitation framework used to execute Atomic Red Team test cases with rapid payload deployment and execution capabilities via…
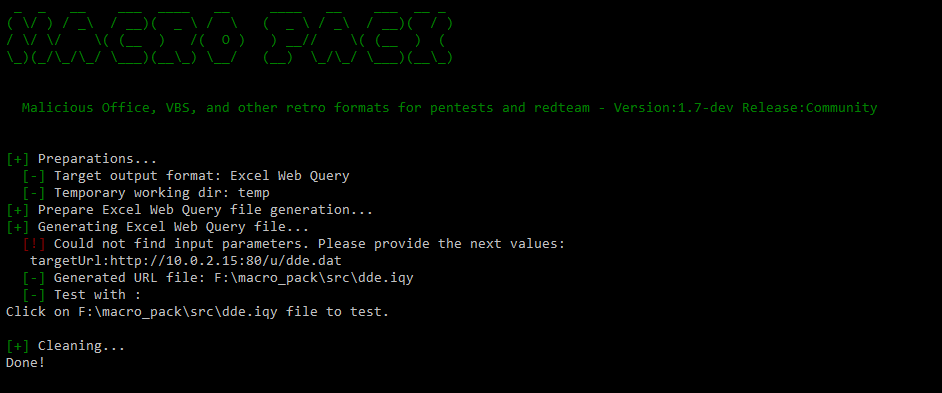 sevagas/macro_pack
macro_pack is a tool by @EmericNasi used to automatize obfuscation and generation of Office documents, VB scripts, shortcuts, and other formats for…
 catsploit/catsploit
Automated penetration testing tool using Cyber Attack Techniques Scoring (CATS) to select and execute optimal attack scenarios via Metasploit, Nmap,…
 coolman6942o/-exploit-cve-2023-36025
Windows SmartScreen Security Feature Bypass Vulnerability
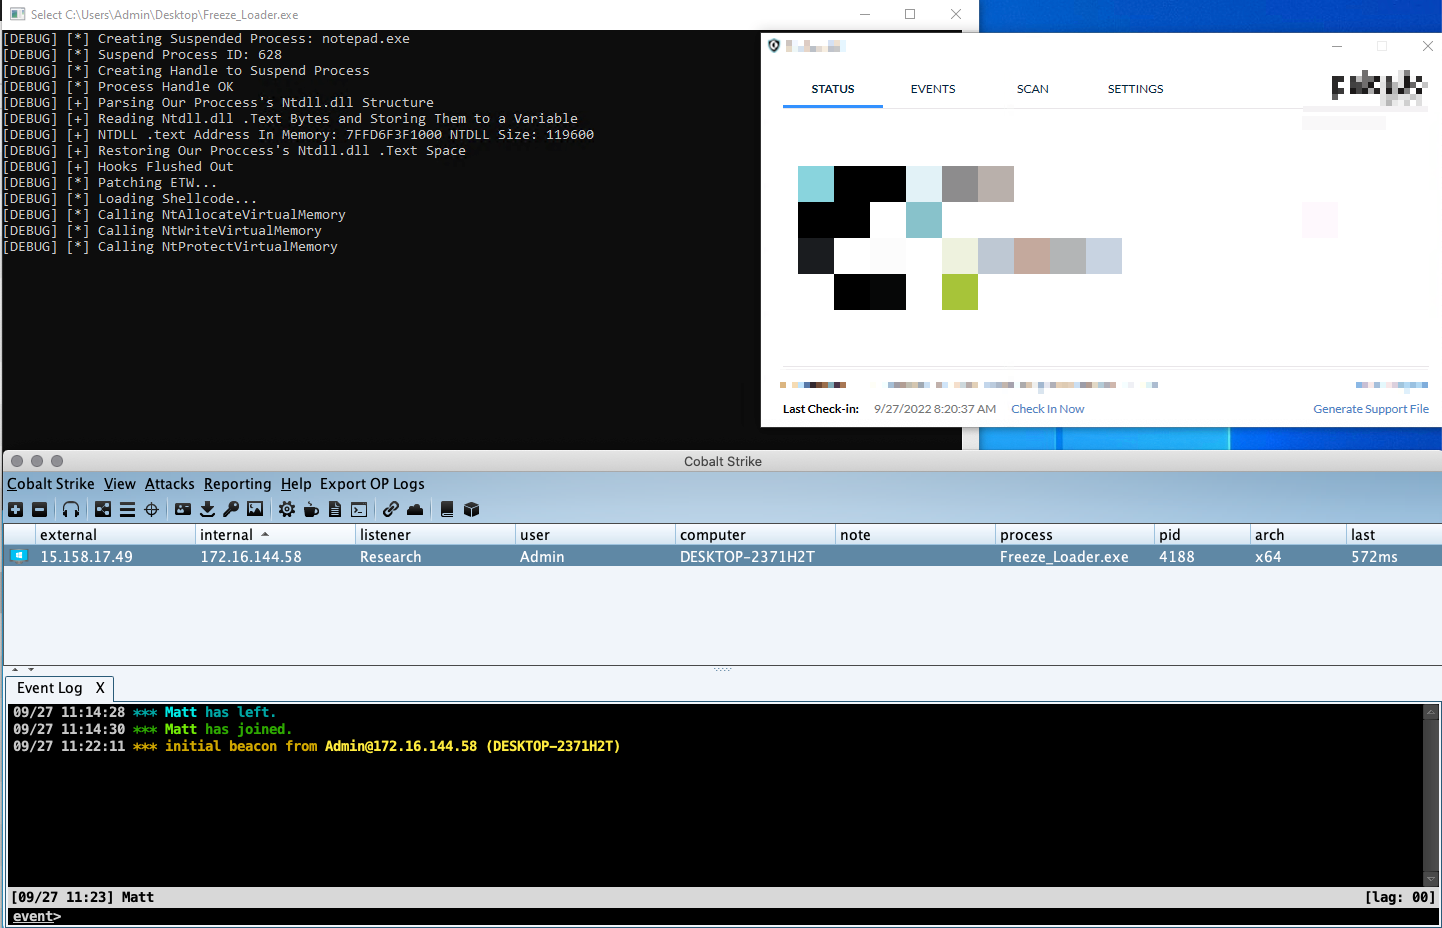 optiv/freeze
Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods
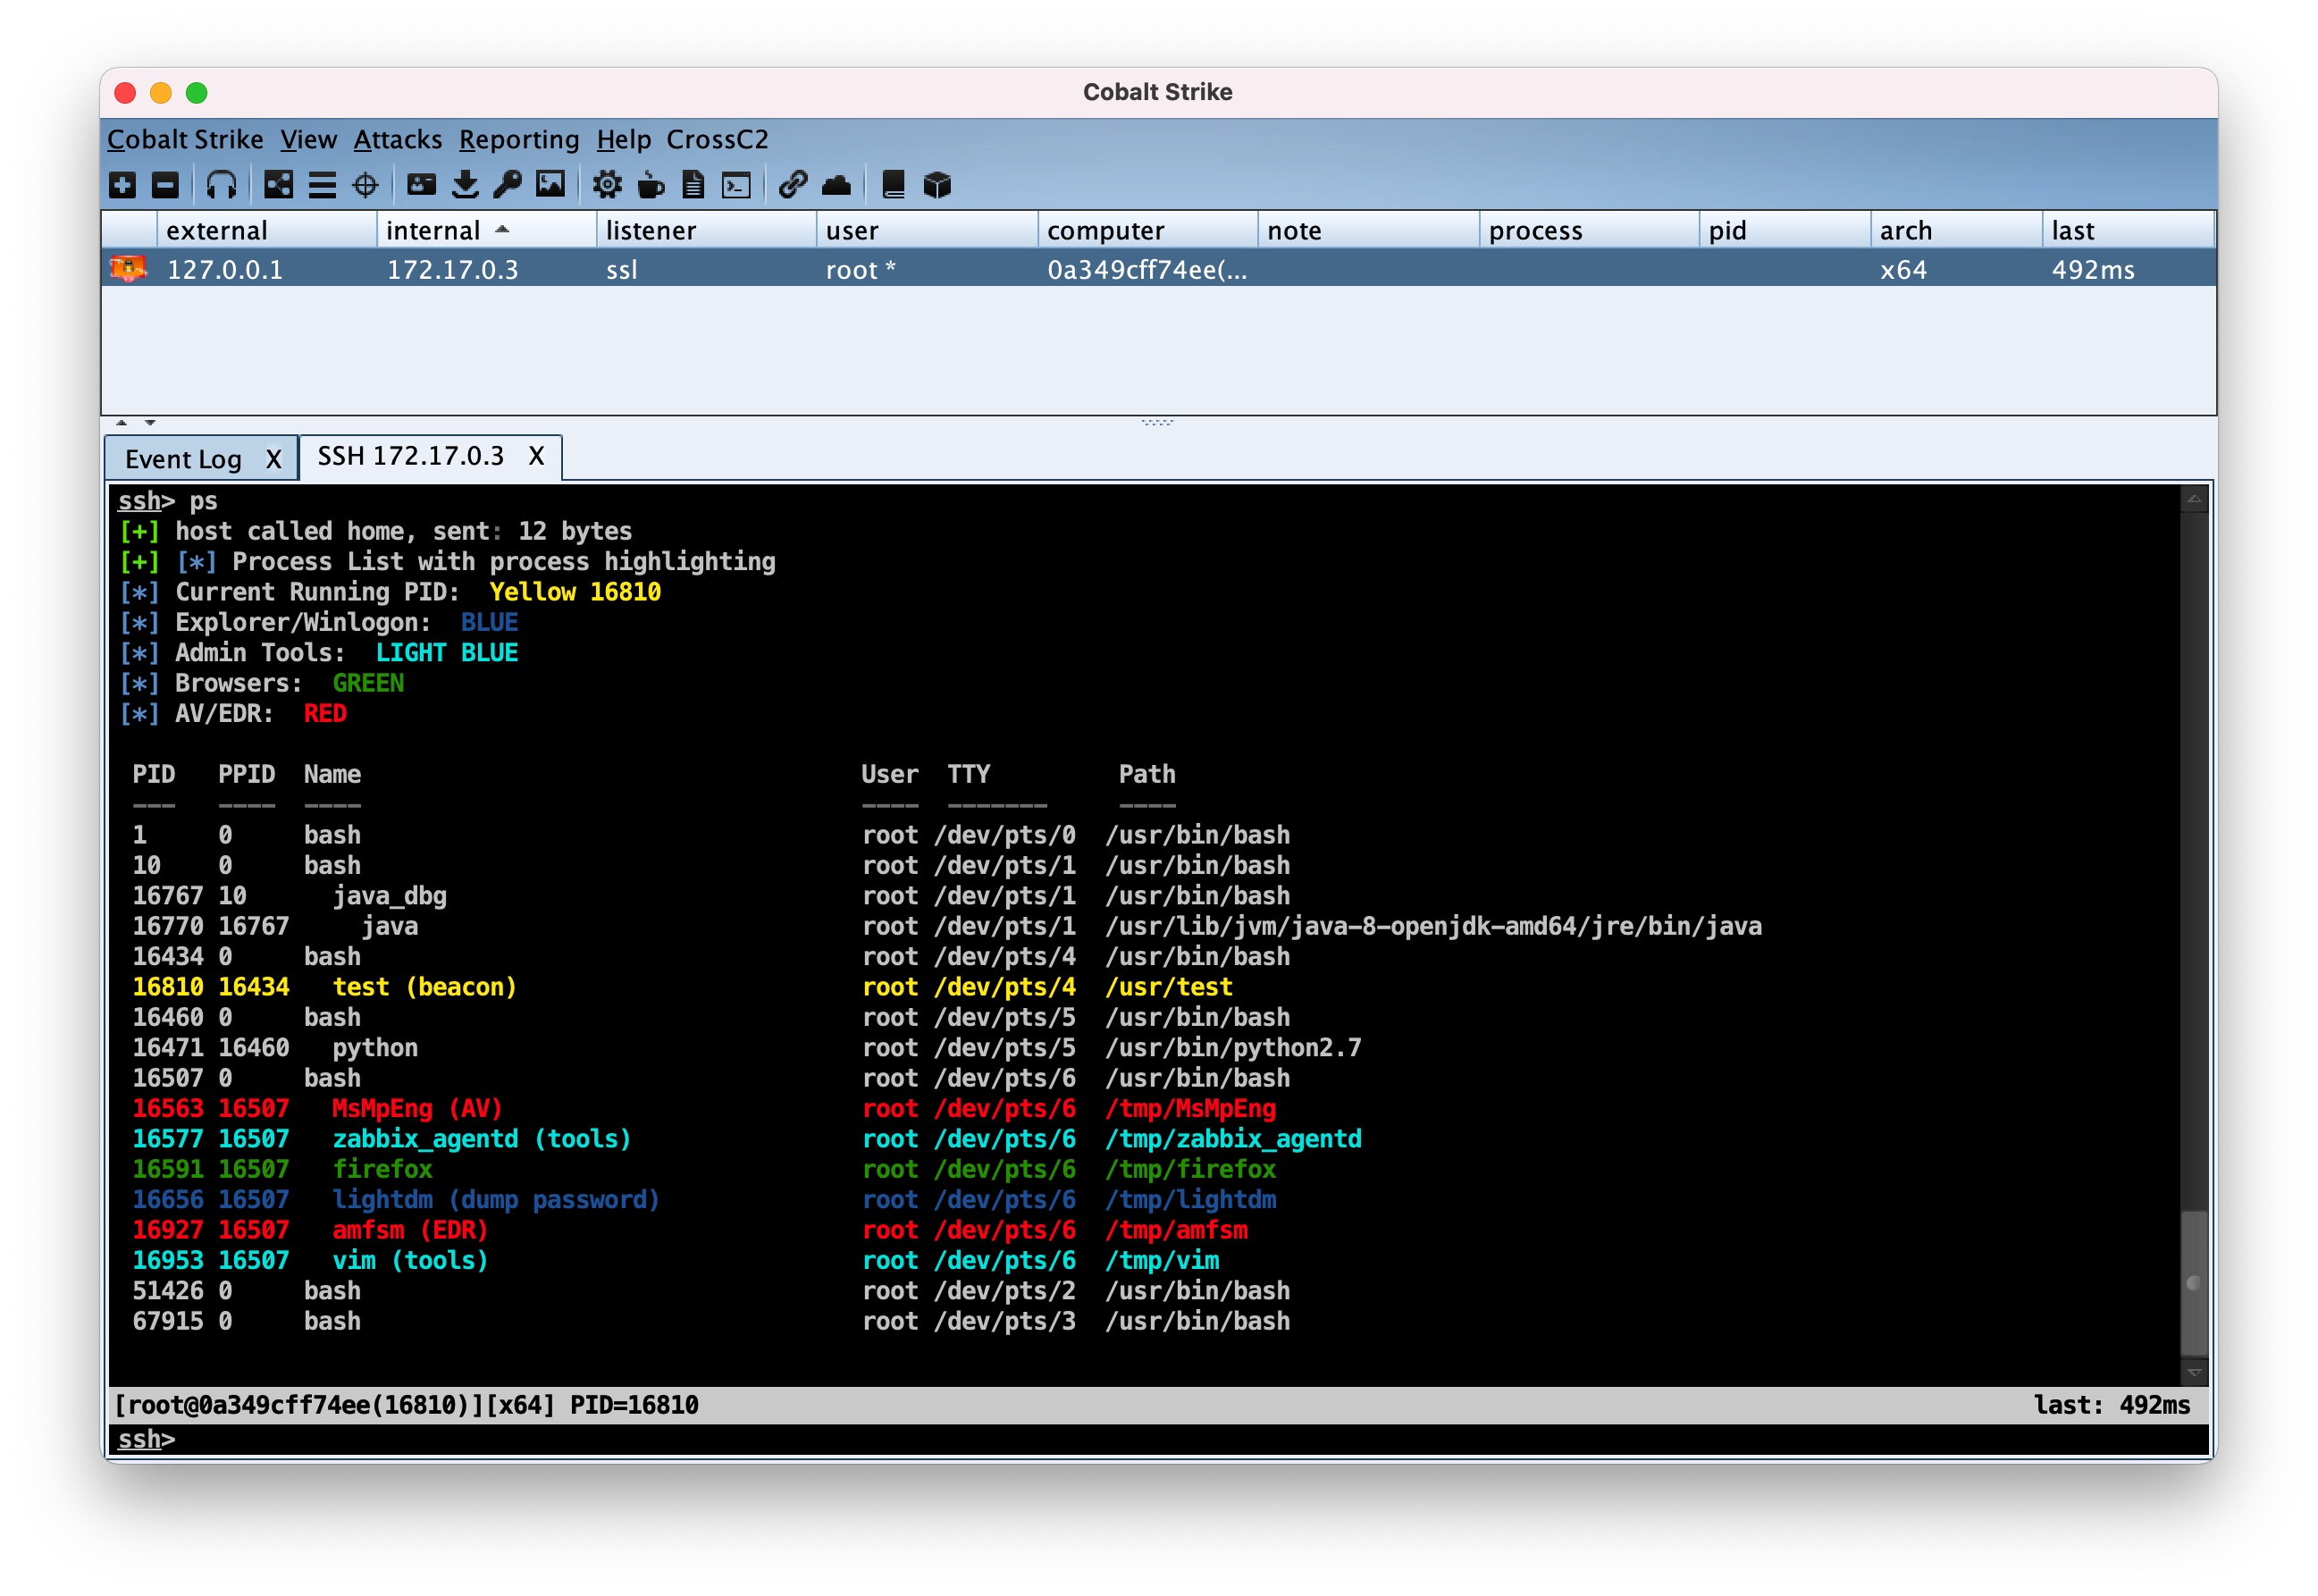 crossc2/crossc2kit
CrossC2 developed based on the Cobalt Strike framework can be used for other cross-platform system control. CrossC2Kit provides some interfaces for…
 ireshchaminda1/android-privilege-escalation-remote-access-vulnerability-cve-2015-1805
AndroRAT is a capability that can be used to inject a root exploit as a silent installation to perform a malicious task on the device. This AndroRAT…
 cckuailong/pocsploit
a lightweight, flexible and novel open source poc verification framework
 aaaguirrep/offensive-docker
Offensive Docker is an image with the more used offensive tools to create an environment easily and quickly to launch assessment to the targets.
 yakumwamba/poc-cve-2021-4034
Proof-of-concept exploit for CVE-2021-4034 (PwnKit), a local privilege escalation in polkit's pkexec, verified on Debian 10 and CentOS 7.
 kirill89/cve-2021-4034
Dockerized exploit for Polkit privilege escalation (CVE-2021-4034) that grants root access via pkexec, with a simple script to run and verify.
 luckythandel/cve-2021-4034
This is a POC for the vulnerability found in polkit's pkexec binary which is used to run programs as another users.