awesome-hacker-search-engines

A curated list of awesome search engines useful during Penetration testing, Vulnerability assessments, Red/Blue Team operations, Bug Bounty and more

A curated list of awesome search engines useful during Penetration testing, Vulnerability assessments, Red/Blue Team operations, Bug Bounty and more

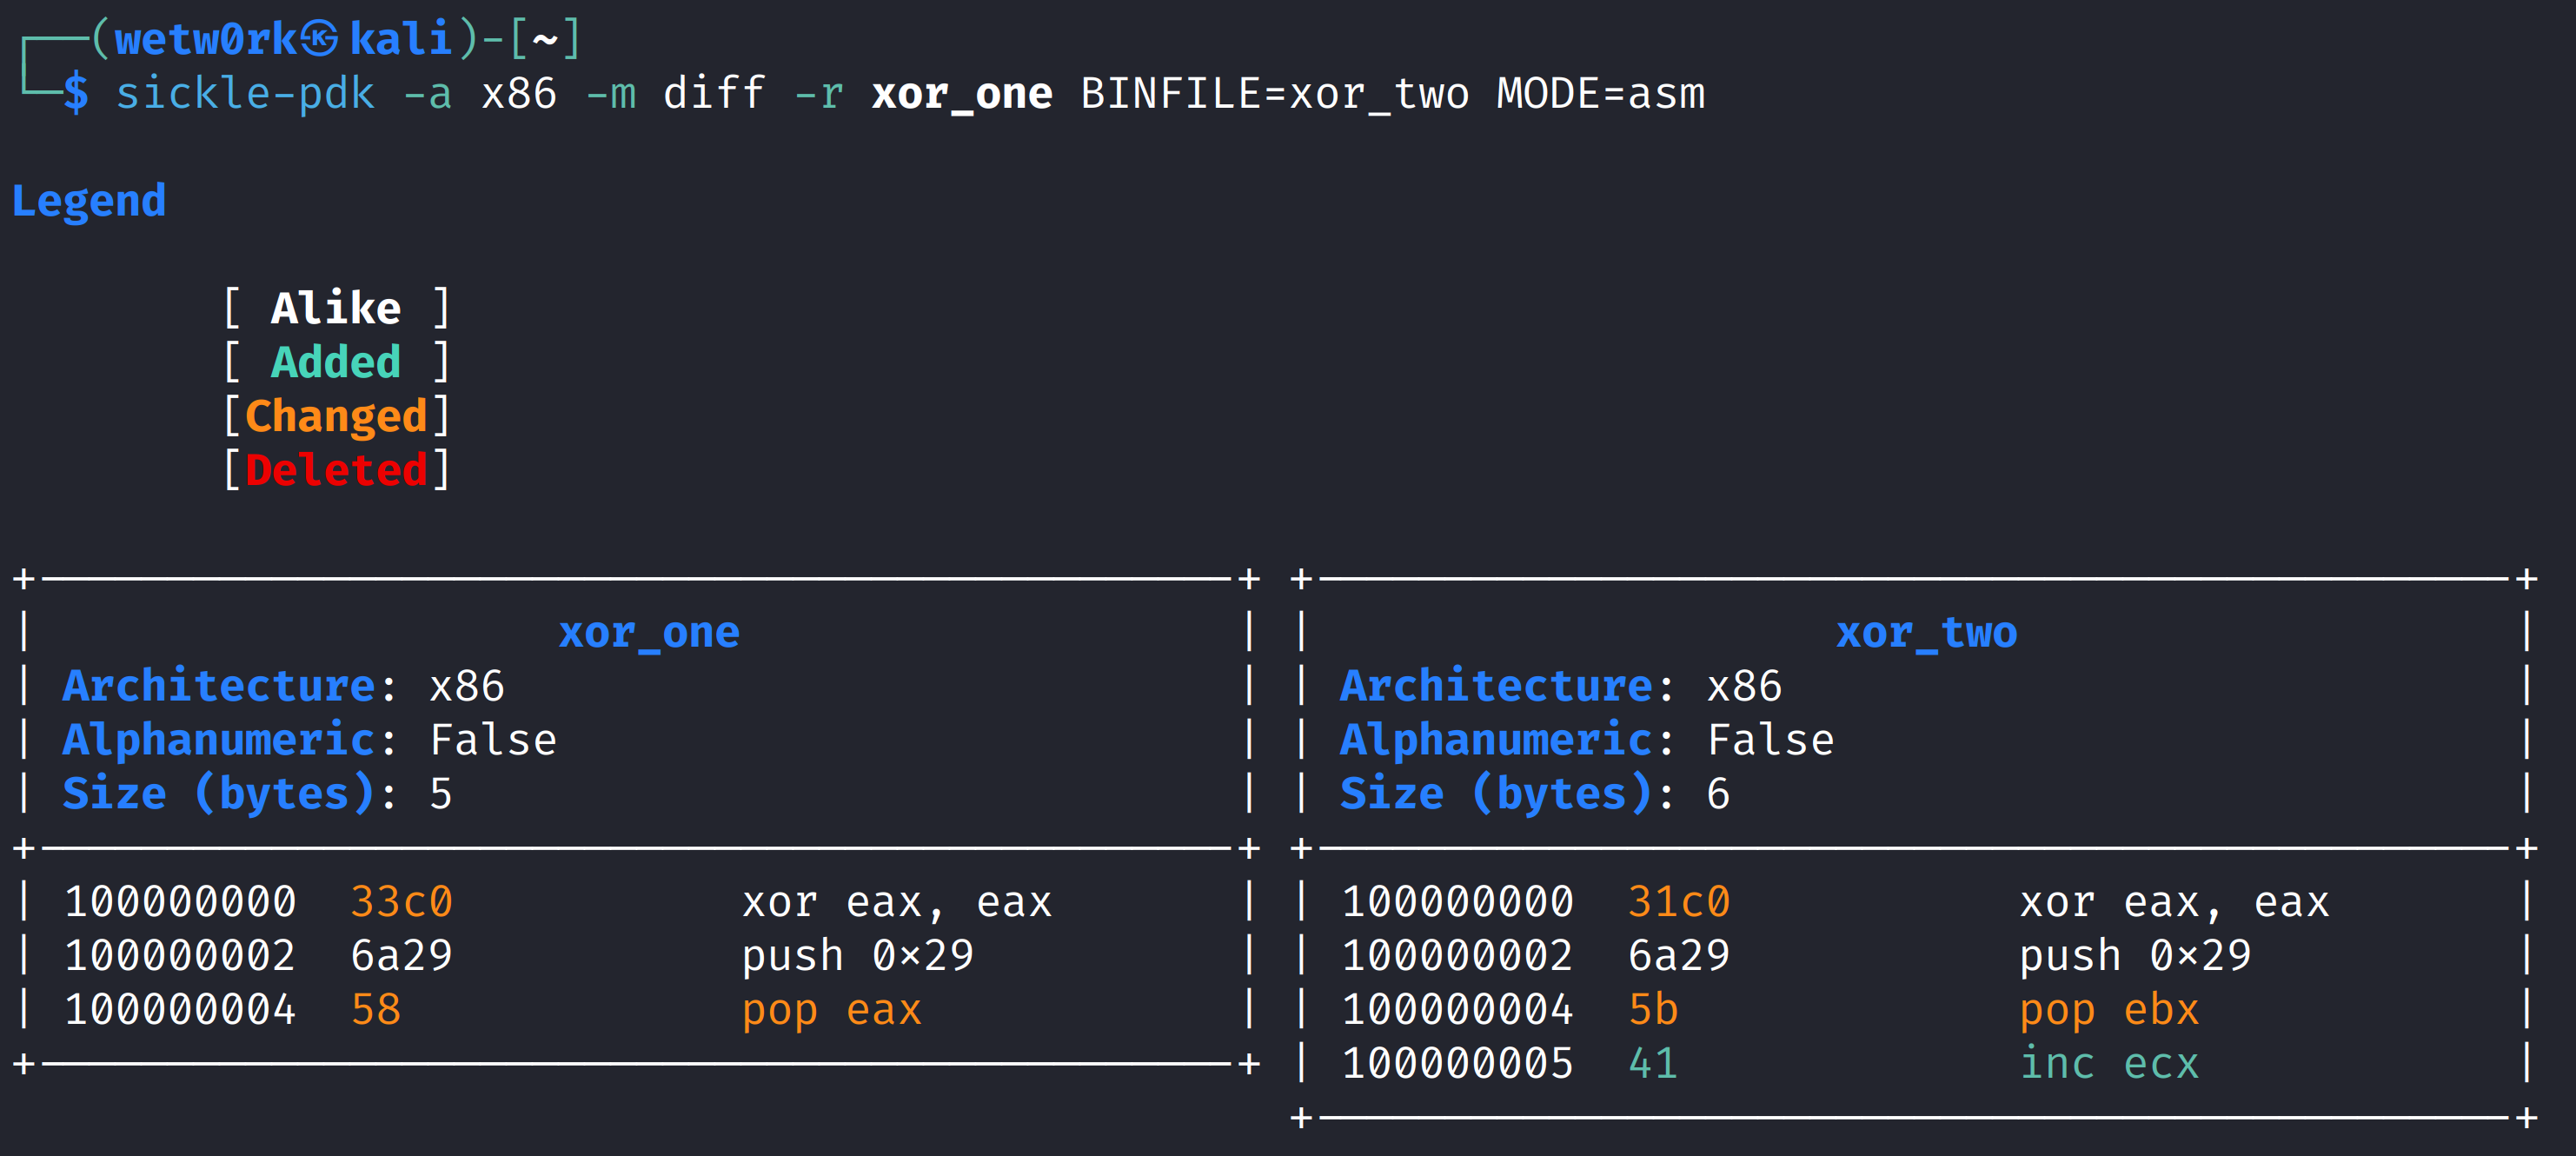
Sickle - Payload Development Kit

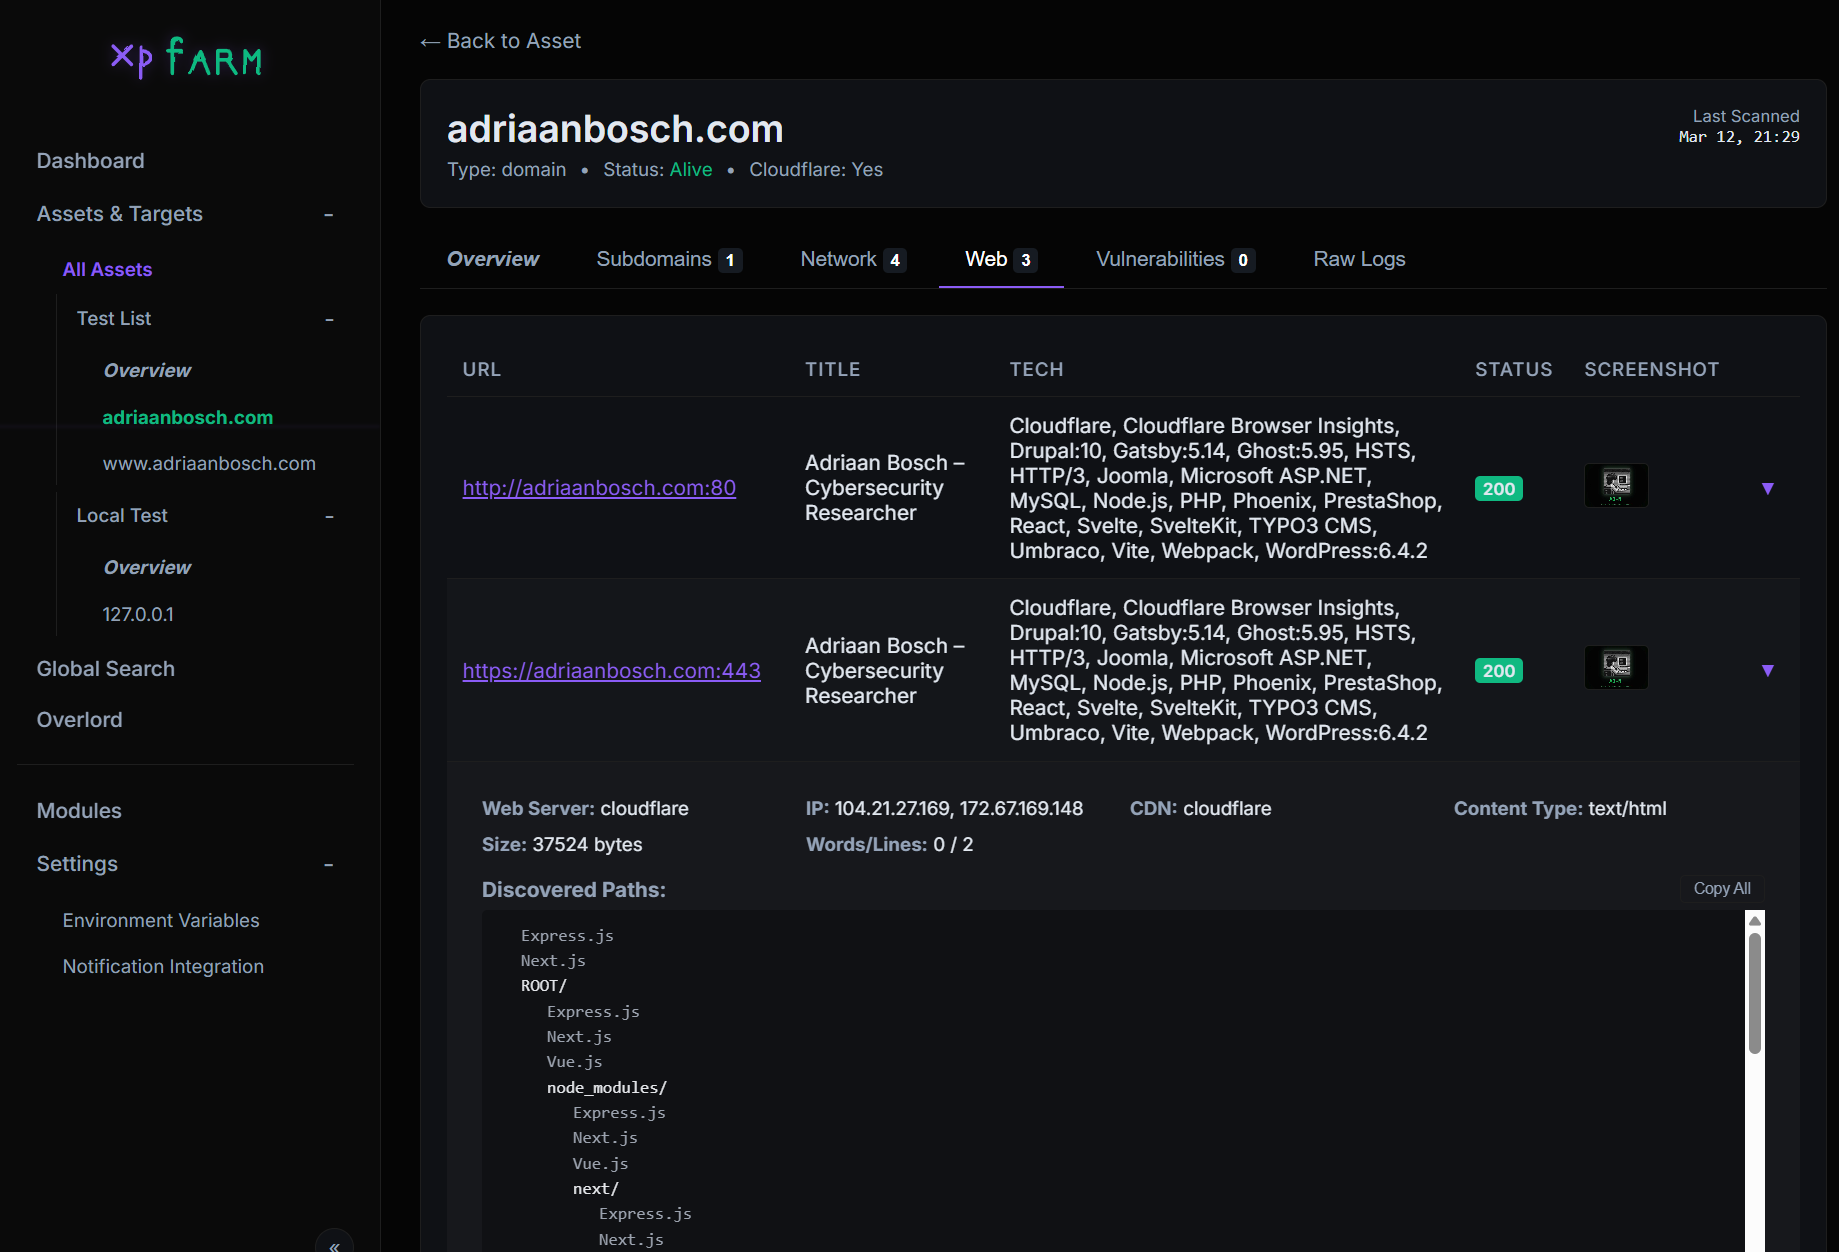
Automated bug bounty & recon framework — wraps Subfinder, Naabu, Httpx, Nuclei, Nmap, CVEMap, Gowitness, Katana & more behind a unified web UI

R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…

Wi-Fi Framework for creating proof-of-concepts, automated experiments, test suites, fuzzers, and more.

Proof of concept for VMware vCenter CVE-2024-37081, modified to enhance usability for security testing and validation of the vulnerability.


app turn nil publics and privates into blanks 3 months ago config Use bundler/setup for more graceful bundler related failures 11 days ago data…

Cobalt Strike extension for post-exploitation persistence using SharpStay .NET assembly. Provides GUI-driven persistence via Registry keys, Scheduled…

A personal tool in GO for my usual first enumeration steps on a target

CVE-2019-0708-Msf-验证

Automated network protocol scanner and exploiter leveraging Metasploit modules for rapid penetration testing across large networks, supporting SMB,…

CLI wrapper for MSFvenom that streamlines payload creation with profile management, automated listener generation, and organized output for…