
Zero-Logon-Exploit
 sq00ky/zero-logon-exploit
Python script exploiting Zerologon (CVE-2020-1472) to perform Netlogon authentication bypass and reset domain controller password to null.
exploitationexploit-frameworkspayload-development+2
38
sq00ky/zero-logon-exploitPython script exploiting Zerologon (CVE-2020-1472) to perform Netlogon authentication bypass and reset domain controller password to null.
 ozergoker/cve-2026-31431-copy-fail
Exploit for CVE-2026-31431: a 732-byte Python script that exploits a straight-line logic flaw to gain root on all Linux distributions since 2017.
 astounds/copy-fail-cve-2026-31431
Local privilege escalation exploit for CVE-2026-31431, a Linux kernel AF_ALG + splice page-cache overwrite. Includes PoC, BPFtrace detection script,…
 recofu/cve-2026-31431-copy-fail
Local privilege escalation exploit for CVE-2026-31431 in the Linux kernel crypto subsystem, providing root access and container breakout with a…
 m4xsec/cve-2026-31431-rce-exploit
Local privilege escalation exploit for CVE-2026-31431, a Linux kernel AF_ALG logic flaw allowing unprivileged users to write 4 bytes into page cache…
 exploiteoom/cve-2026-31431
Exploit for CVE-2026-31431 that escalates privileges by altering user ID, with a verification script and mitigation instructions for the algif_aead…
 painoob/copy-fail-exploit-cve-2026-31431
Most Linux LPEs need a race window or a kernel-specific offset. Copy Fail is a straight-line logic flaw, it needs neither. The same 732-byte Python…
 nisec-eric/cve-2026-31431
Linux kernel local privilege escalation exploit for CVE-2026-31431, providing a reliable single-shot PoC with multiple language implementations,…
 mebeim/cve-2021-4034
Proof-of-concept exploit for CVE-2021-4034, a local privilege escalation in polkit's pkexec, demonstrating exploitation with simple C helpers and a…
 f4t1h21/cve-2021-3560-polkit-dbus
f4T1H's PoC script for CVE-2021-3560 Polkit D-Bus Privilege Escalation
 thejoyofhacking/berdav-cve-2021-4034
Exploit for CVE-2021-4034 (PwnKit) that provides a root shell via polkit pkexec. Includes a dry-run mode to test vulnerability and a one-liner script…
 neonwhiterabbit/cve-2021-4034
Bash script exploiting CVE-2021-4034 (Pwnkit) for local privilege escalation on vulnerable Linux systems. Copy-paste execution for quick testing.
 kirill89/cve-2021-4034
Dockerized exploit for Polkit privilege escalation (CVE-2021-4034) that grants root access via pkexec, with a simple script to run and verify.
 isw-9/copy-fail-cve-2026-31431-aarch64
Python exploit for CVE-2026-31431 targeting aarch64, verified on Ubuntu 25.10. Executes the provided script to trigger the vulnerability.
 jiangban046-spec/cve-2026-31431-exploit_py2_py3
Python2/3 compatible exploit script for CVE-2026-31431, enabling privilege escalation on vulnerable systems.
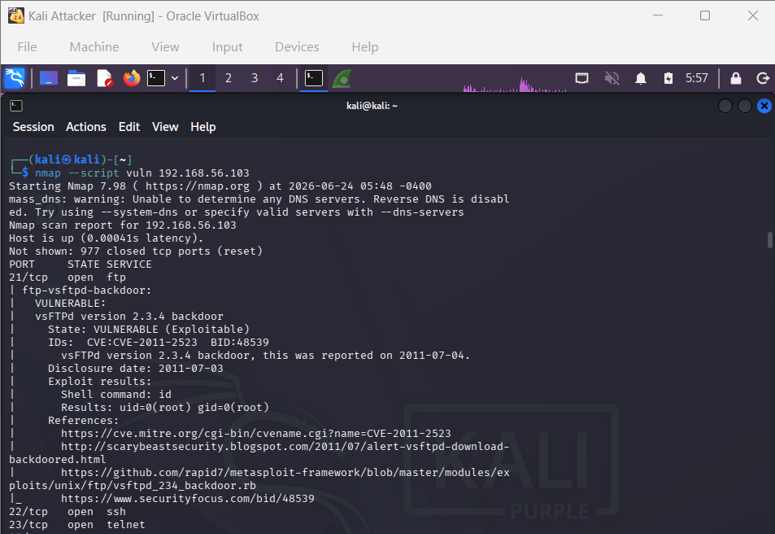 sonalisarkar-2003/ftp-vsftpd-cve-2011-2523-vapt-report
VAPT report for vsFTPd 2.3.4 backdoor CVE-2011-2523, covering Nmap vulnerability scanning, Metasploit exploitation, post-exploitation root access,…
 bluscreenofjeff/malleable-c2-randomizer
A script to randomize Cobalt Strike Malleable C2 profiles and reduce the chances of flagging signature-based detection controls
 qax-a-team/cobaltstrike-toolset
Aggressor Script, Kits, Malleable C2 Profiles, External C2 and so on