initial-access-community

Go-based exploits for unauthenticated network vulnerabilities in routers, VPNs, appliances, and IoT, bundled with PCAPs, Suricata/Snort/YARA/Sigma…

Go-based exploits for unauthenticated network vulnerabilities in routers, VPNs, appliances, and IoT, bundled with PCAPs, Suricata/Snort/YARA/Sigma…

A listener profile for the Mythic C2 framework that utilizes AI vendors file API's

The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…

Android complete exploit chain that enables privilege escalation from a local untrusted app to root/kernel, combination of CVE-2026-49881 and…

From patch to RCE: hand-built exploit for CVE-2010-4221 (ProFTPD TELNET IAC stack overflow), with the full failure-driven journey documented

Kernel root exploit (CVE-2026-43499) for some Amazon devices

Firmware-specific temporary root exploit for Toshiba/Amazon Fire TV (hazel) using CVE-2026-43499. Implements ARM32 futex-PI UAF, kernel address leak,…

Analyzes CVE-2026-31431, a Linux kernel AF_ALG AEAD vulnerability, providing a safe detector, in-lab LPE exploit, and QEMU-based A/B kernel lab for…

Search public CVE proof-of-concept exploits from GitHub, Nuclei, ExploitDB, Metasploit and Vulhub, with CVSS, EPSS and CISA KEV context.

The FortiGate SSL-VPN pot of gold. CVE-2024-21762 and CVE-2023-27997. 79 working exploit clients. 53 hardware SKUs. 55 FortiOS builds.

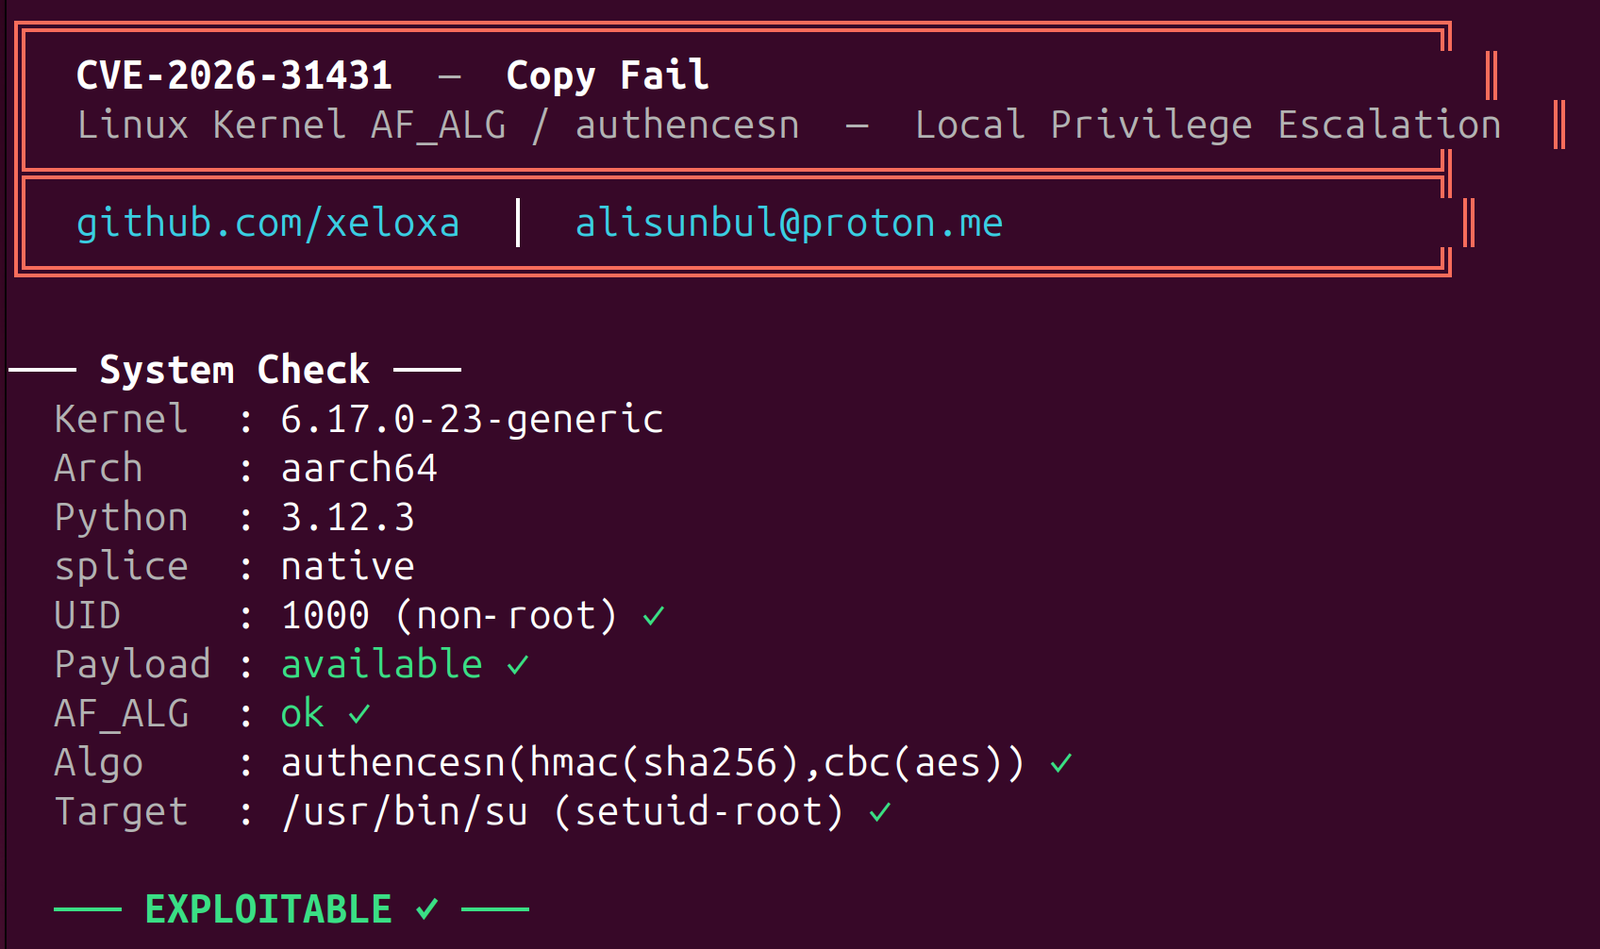
Copy Fail (CVE-2026-31431) LPE exploit. A clean, multi-arch Python reimplementation targeting the Linux kernel AF_ALG page cache vulnerability.

CVE research and exploits to help gaining roots for Pixel devices

Sudo Vulnerability Local PrivEsc (CVE-2025-32463) POC with Python

Local privilege escalation exploit for CVE-2026-3888 targeting snap-confine and systemd-tmpfiles on Ubuntu, providing SUID and capabilities variants…

Static Go proof-of-concept for CVE-2026-31431, leveraging Linux AF_ALG and splice(2) to trigger the vulnerability. Provides prebuilt binaries for…

Proof of Concept for CVE-2021-4034 (with experimental traceless exploitation)

Exploit for CVE-2021-4034 (PwnKit) that leverages a race condition in pkexec to escalate privileges to root on Linux systems.

Firefox content-to-parent IPDL privilege escalation (N-day, bug 2054416): forged PDocumentChannel with RemoteTypeOverride -> privilegedabout process…